pfsense-api-enroll-json-ssh
 abraxas/pfsense-api-enroll-json-ssh
pfSense Plus MIM API toolkit b4acd7ca - High - Remote - Privilege leftover - example-add-devices.py JSON into SSH
code-analysiscommand-and-controlexploitation+6
abraxas/pfsense-api-enroll-json-sshpfSense Plus MIM API toolkit b4acd7ca - High - Remote - Privilege leftover - example-add-devices.py JSON into SSH
 abraxas/gitea-user-keys-idor
Proof-of-concept and lab for a Gitea IDOR (CWE-639) in GET /api/v1/user/keys/{id}, letting an authenticated read:user token enumerate other users'…
 abraxas/sqlite-rsync-ssh
SQLite 3.53.4 sqlite3_rsync - High - Remote - RCE - SSH filename command injection
 abraxas/forgejo-keys-idor
Forgejo 16.0.5 - High - Remote - IDOR - GET /api/v1/user/keys/{id} returns other users SSH and deploy keys
 faizanali8232/cve-exploit-research-development
A professional Python tool designed for educational penetration testing, demonstrating SSH vulnerabilities (CVE-2008-0166 / CVE-2008-1657) with…
 damnkrishna/cve-2025-32433-lab
A Flaw in SSH protocol message handling, a malicious actor could gain unauthorized access to affected systems and execute arbitrary commands without…
 adfortunato/metasploitable3-pentest-writeup
Home-lab penetration test report of Metasploitable3 covering Nmap recon, Drupalgeddon RCE, SQL injection, SSH credential reuse, sudo privilege…
 liam-worsley/cve-2025-32433-poc-analysis
This is an analysis for CVE-2025-32433 (Erlang OTP SSH Vulnerability). I did not write any of the code, I only wrote comments describing what the…
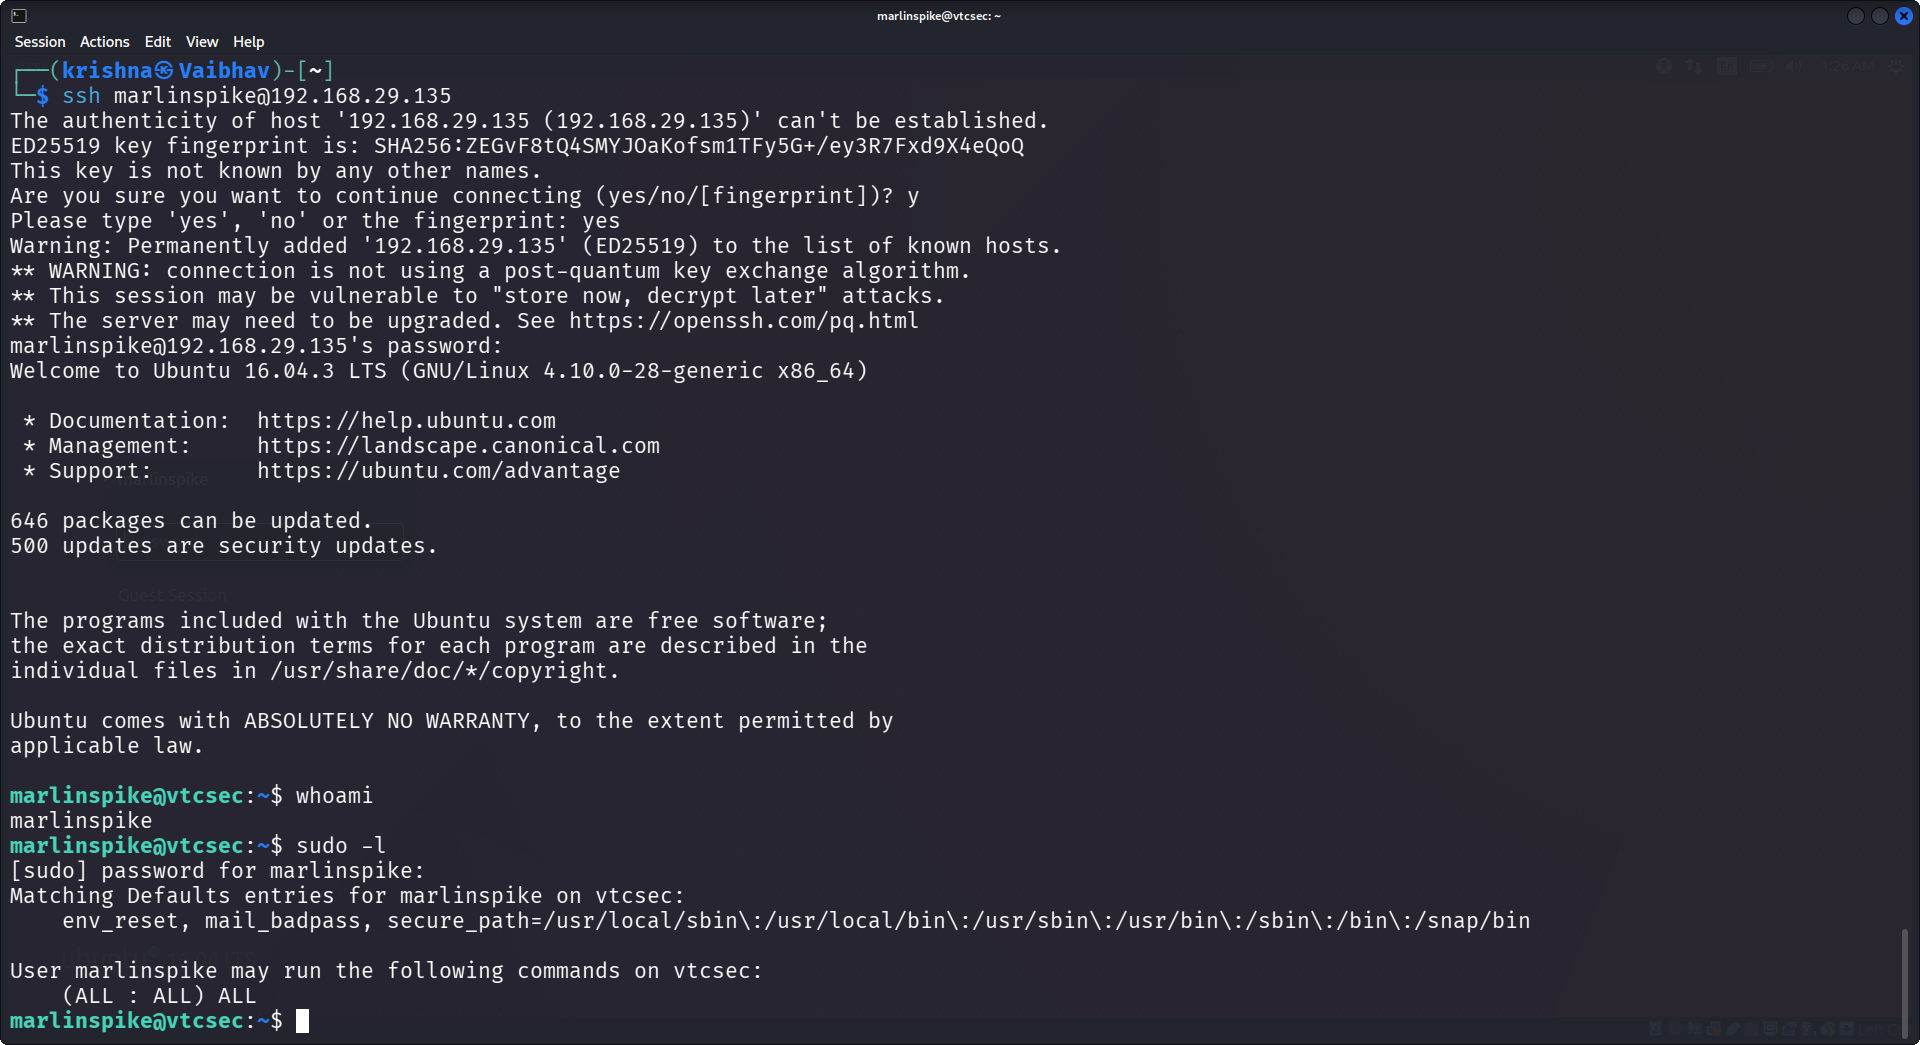 vaibhavkrishna12004/ubuntu-privesc-lab
Full penetration testing workflow: credential brute force, SSH access and privilege escalation (CVE-2021-4034)
 pallangyo98/trickster-htb
This report details exploiting Trickster via an XSS in PrestaShop (CVE-2024-34716) to gain www-data access, extracting database credentials for SSH…
 mauricelambert/labautomationcve-2021-43798
This script implements a lab automation where I exploit CVE-2021-43798 to steal user secrets and then gain privileges on a Linux system.
 zakariamaaraki/dirty-cow-cve-2016-5195-
Exploit the dirtycow vulnerability to login as root
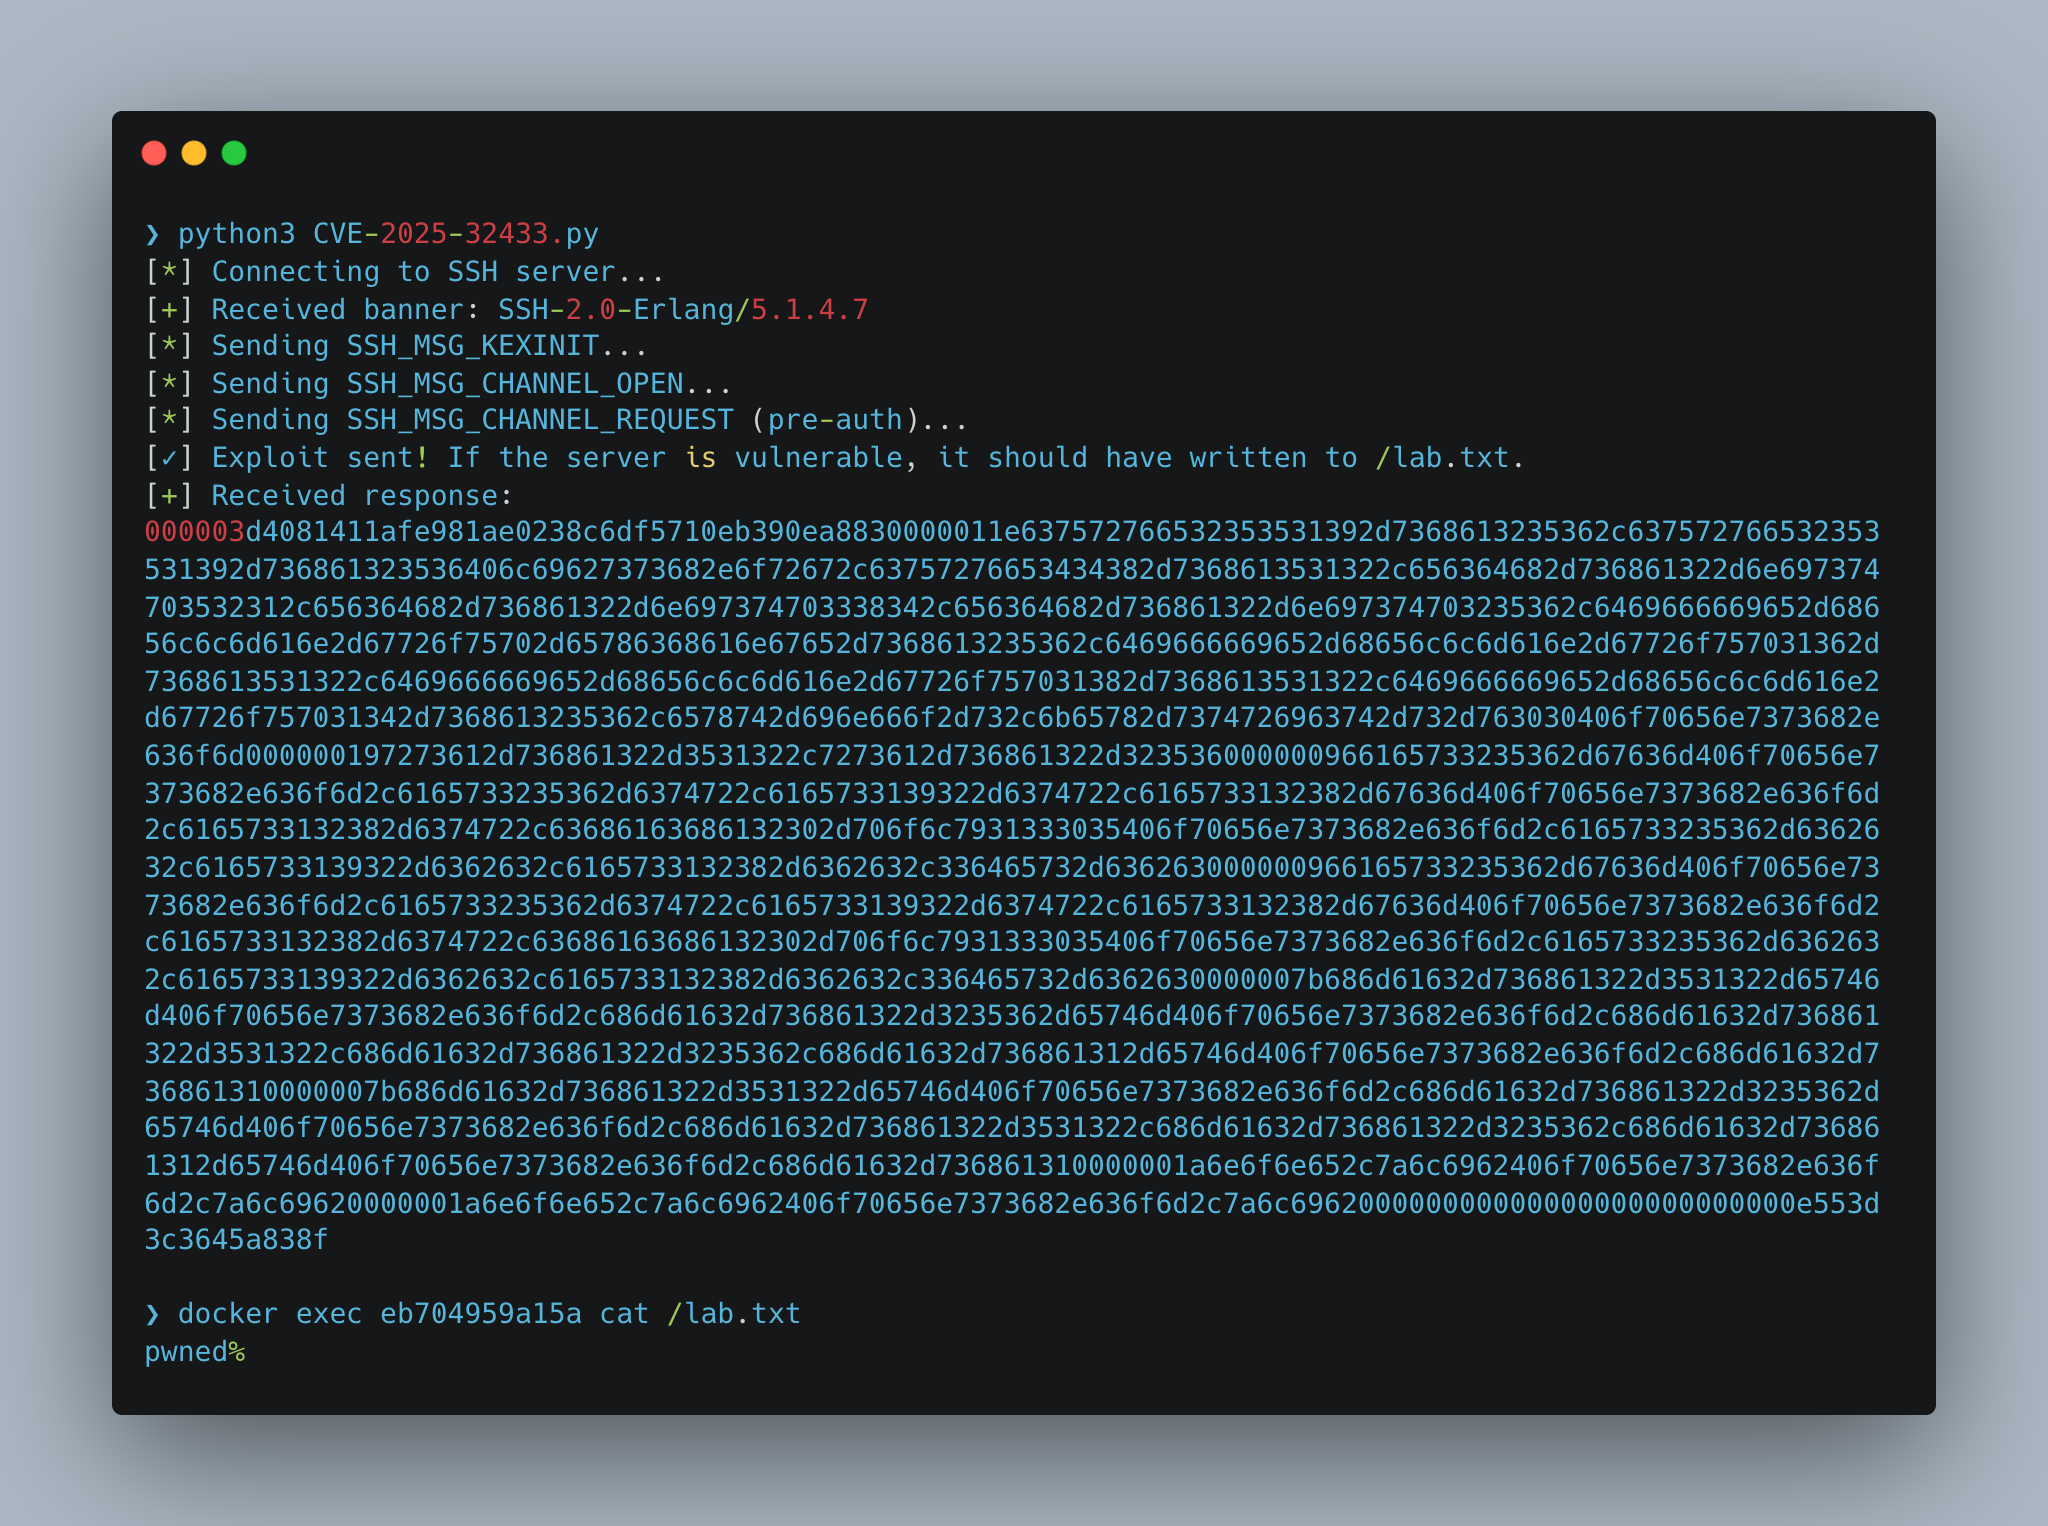 yonathanpy/cve-2025-32433.py
CVE-2025-32433 PoC – SSH Protocol Python-based PoC for controlled lab testing of SSH message handling, channel operations, and pre-auth interactions.…
 sarjanpatel22/siem-threat-detection-lab
Blue-team SIEM lab: Wazuh 4.7.5 detecting 7 simulated attacks (SSH brute force, Slowloris DoS / CVE-2007-6750, web attacks) with real-time MITRE…
 mboatella25/metasploitable-pentest-lab
Pentest completo sobre Metasploitable: recon con nmap, explotación con Metasploit (CVE-2007-2447), extracción y cracking de credenciales,…
 jerry-zhuang/cve-2017-1000117
Proof-of-concept exploit for CVE-2017-1000117 (Git clone command injection) targeting SSH, designed for vulnerability testing and educational lab…
 siling2017/cve-2017-1000117
Proof-of-concept exploit for CVE-2017-1000117 (Git SSH command injection) that writes command output to a web-accessible file. Part of VulApps…