
soc-home-lab
 szzxli/soc-home-lab
Hands-on SOC lab: AWS mini-SOC with CloudTrail/GuardDuty, a Python CloudTrail IOC analyzer, phishing header forensics, ELF binary triage, and agent…
binary-analysiscloud-securitydigital-forensics+8
6
szzxli/soc-home-labHands-on SOC lab: AWS mini-SOC with CloudTrail/GuardDuty, a Python CloudTrail IOC analyzer, phishing header forensics, ELF binary triage, and agent…
 vighnesh91/severitas
Authorized social-engineering simulation framework with an isolated loopback lab, synthetic audience generation, pre-flight authorization checks, and…
 shauryarathore357-hub/thm-moniker-link-cve-2024-21413-writeup
TryHackMe room walkthrough of CVE-2024-21413, covering the Outlook Moniker Link Protected View bypass, NTLM hash leaking, and credential capture with…
 0xblackash/cve-2026-76461
Research repository for CVE-2026-76461, a critical SQL injection in Cisco Secure Email Gateway leading to root RCE, with detection rules, mitigation…
 arcanum-sec/wraith
Browser-hooking framework for authorized red teams and educators. Hooks browsers via XSS, provides interactive post-exploitation control, blind-XSS…
 praneethnaidu1910-cmd/cve-2023-23397-purple-team
Purple team project exploiting CVE-2023-23397 Outlook NTLM leak with phishing delivery, plus Sigma/Wazuh detections mapped to MITRE ATT&CK for the…
 abhayclasher/cve-2026-33331
Local lab reproducing stored XSS in oRPC's OpenAPI docs generation (CVE-2026-33331), with vulnerable and patched versions for comparison and a…
 ransomleak/training-security-awareness
Open-source interactive security awareness training library with 130+ SCORM exercises covering phishing, vishing, BEC, MFA fatigue, and OWASP AI/LLM…
 yfelipecruvinel/tryhackme-moniker-link
Documentation of my hands-on lab Moniker Link (CVE-2024-21413) completed on TryHackMe.
 doctoreww/evilfonttool
A font-based deception tool for red teaming, security research, and whatever else.
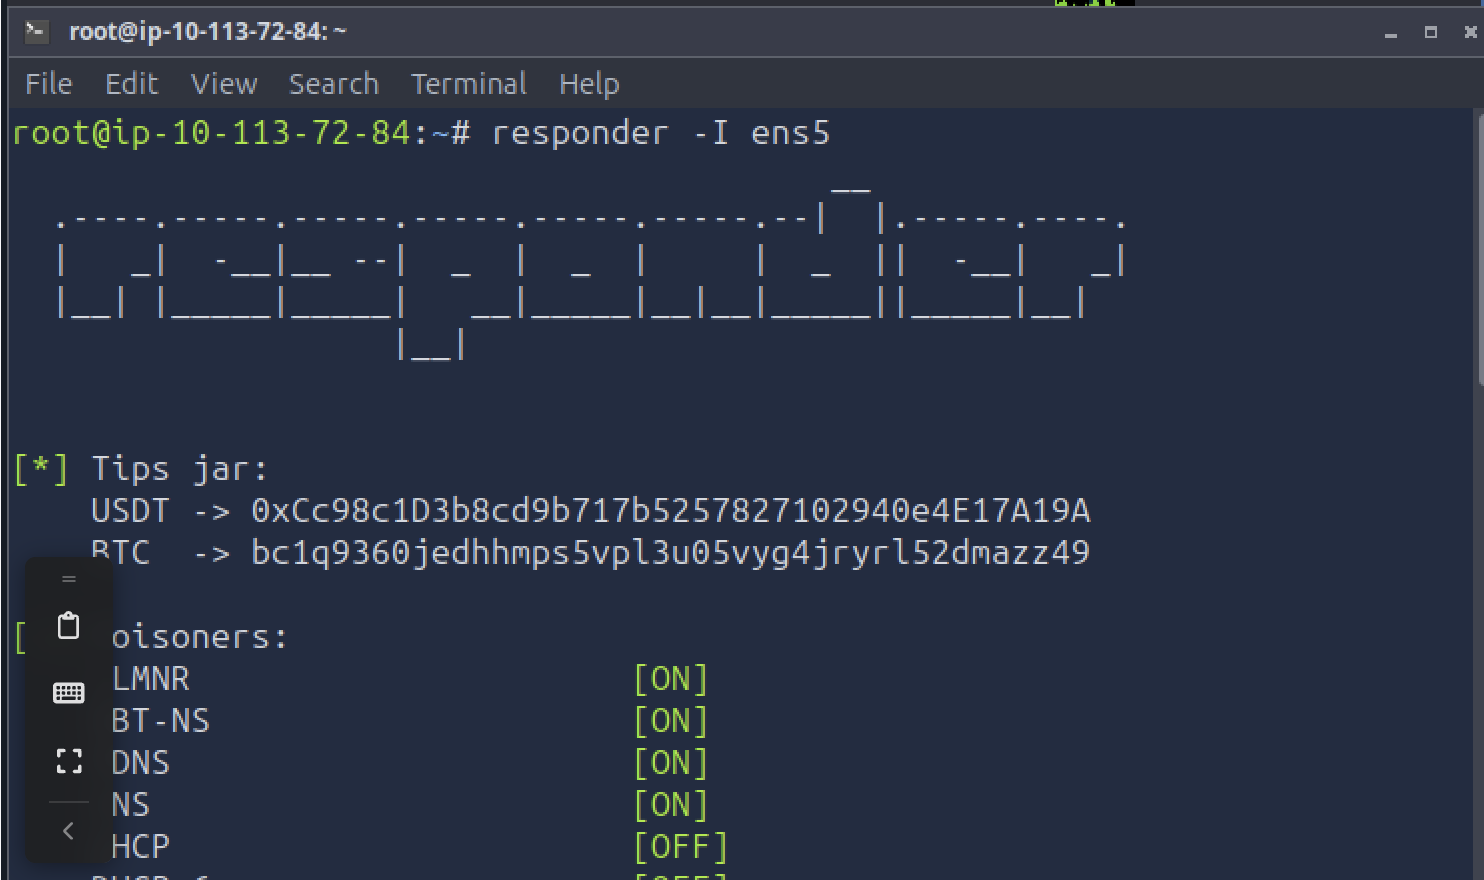 omarmahmoud1024/tryhackme-monikerlink-writeup
TryHackMe Moniker Link (CVE-2024-21413) walkthrough: Outlook Protected View bypass leading to NTLMv2 hash capture via a crafted moniker link.
 h4cknain/cve-2024-21413-microsoft-outlook-moniker-link-vulnerability
Lab write-up analyzing CVE-2024-21413 Outlook Moniker Link exploitation, NetNTLMv2 credential leakage via SMB, detection with YARA/Wireshark, and…
 cappricio-securities/camjacking-templates
camjacking templates
 boredchilada/clickfix-simulator-2025
A lightweight, self-hosted simulation tool for "ClickFix" (ClearFake) social engineering training. Safely simulates clipboard-injection attacks with…
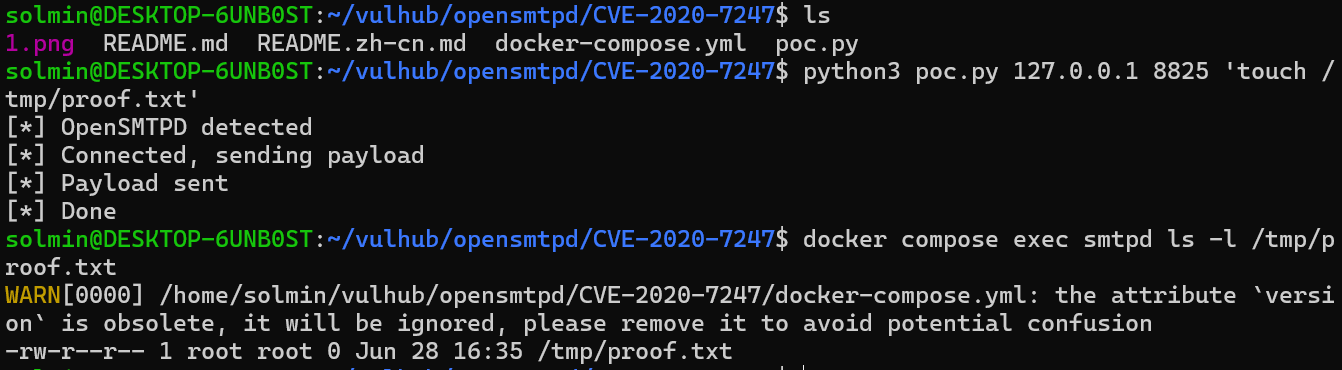 solmin111/opensmtpd-cve-2020-7247-
Docker-based lab demonstrating CVE-2020-7247 remote code execution in OpenSMTPD 6.6.1p1 with a Python PoC for educational security testing.
 pedro-lucas-melo/estudo-de-caso-cve-2024-21413
Um estudo de caso do CVE-2024-21413. Usado como parâmetro a sala do TryHackMe Moniker Link (CVE-2024-21413). Feito edições com claude code no exploit.
 razureink/cve-2024-43451-ntlm_hash_disclosure_reproduction
CVE Reproduction: cve-2024-43451-ntlm_hash_disclosure_reproduction