
CVE-2026-43284---DirtyFrag-Analysis-THM-
 revyhub/cve-2026-43284---dirtyfrag-analysis-thm-
TryHackMe Dirty Frag (CVE-2026-43284) — Linux LPE writeup
ctfeducationexploitation+3
1
revyhub/cve-2026-43284---dirtyfrag-analysis-thm-TryHackMe Dirty Frag (CVE-2026-43284) — Linux LPE writeup
 h1n4mx0z/research-cve-2016-5195
Detailed technical analysis and proof-of-concept exploit for CVE-2016-5195 (Dirty COW), a Linux kernel privilege-escalation vulnerability using a…
 reconinfosec/web-traffic-generator
A quick and dirty HTTP/S "organic" traffic generator.
 kasunpriyashan/y2s1-project-linux-exploitaion-using-cve-2016-5195-vulnerability
Educational Linux privilege escalation exploit targeting CVE-2016-5195 (Dirty COW) to demonstrate kernel vulnerability exploitation and root access…
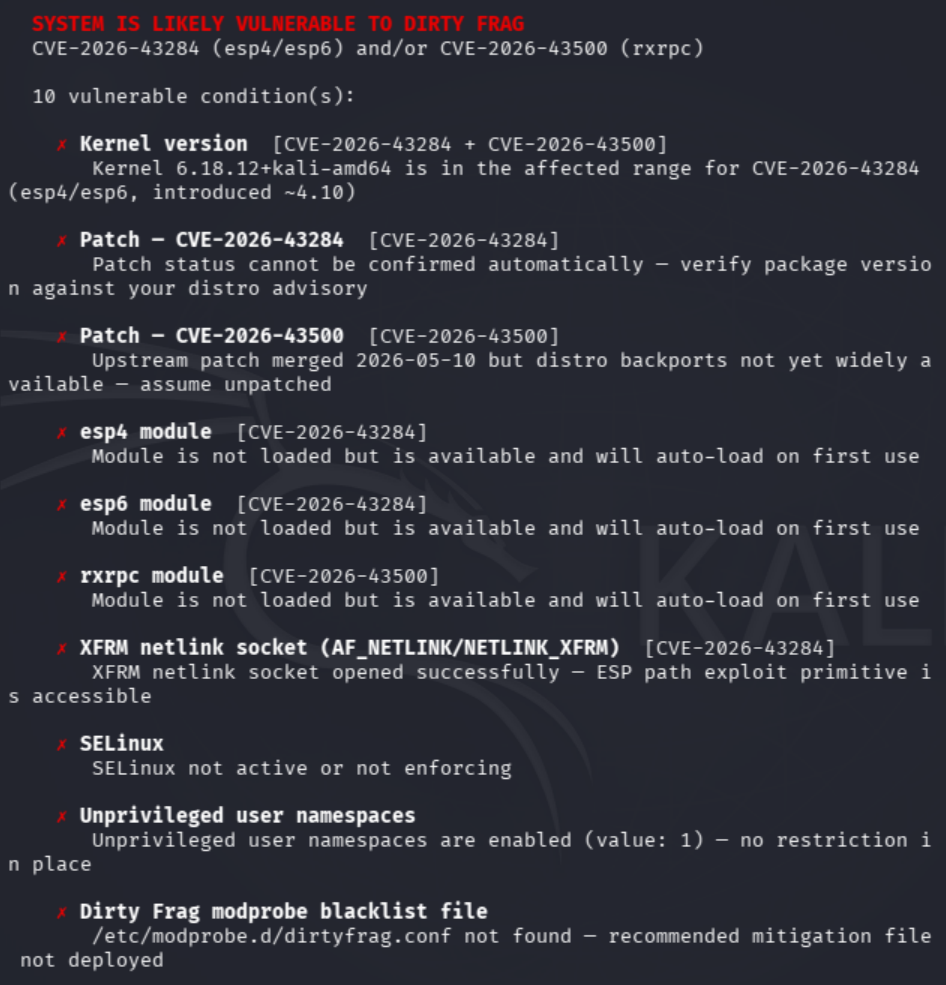 dylanclaudio/reporte-de-escalada-de-privilegios-local-dirty-frag
Se realizó una evaluación de vulnerabilidades sobre una máquina virtual con Kali Linux utilizando un script detector para la vulnerabilidad Dirty…
 zsolt-halo/log4j-log4shell-cve-2021-44228-spring-boot-test-service
Dockerized Spring Boot service intentionally vulnerable to Log4Shell (CVE-2021-44228) for testing detection tools, payloads, and exploit capabilities…
 sakilahamed/linux-kernel-exploit-lab
More specific : Dirty COW (CVE-2016-5195)
 gonzabot/kernel-exploit-dirtycow
Lab — Privilege Escalation via Dirty Cow CVE-2016-5195 | 4Geeks Academy
 cristinapravata/dirtycaw-projet
Escala de privilegios con CVE-2010-5195
 karazajac/dirtyfail
Detector + PoC for Linux page-cache write vulnerabilities: Copy Fail (CVE-2026-31431) and Dirty Frag (CVE-2026-43284/43500). Authorized security…
 mohammadamin382/dirtycow-lab
Educational PoC for Dirty COW (CVE-2016-5195) with logging, ptrace fallback, and binary payload support.
 zakariamaaraki/dirty-cow-cve-2016-5195-
Exploit the dirtycow vulnerability to login as root
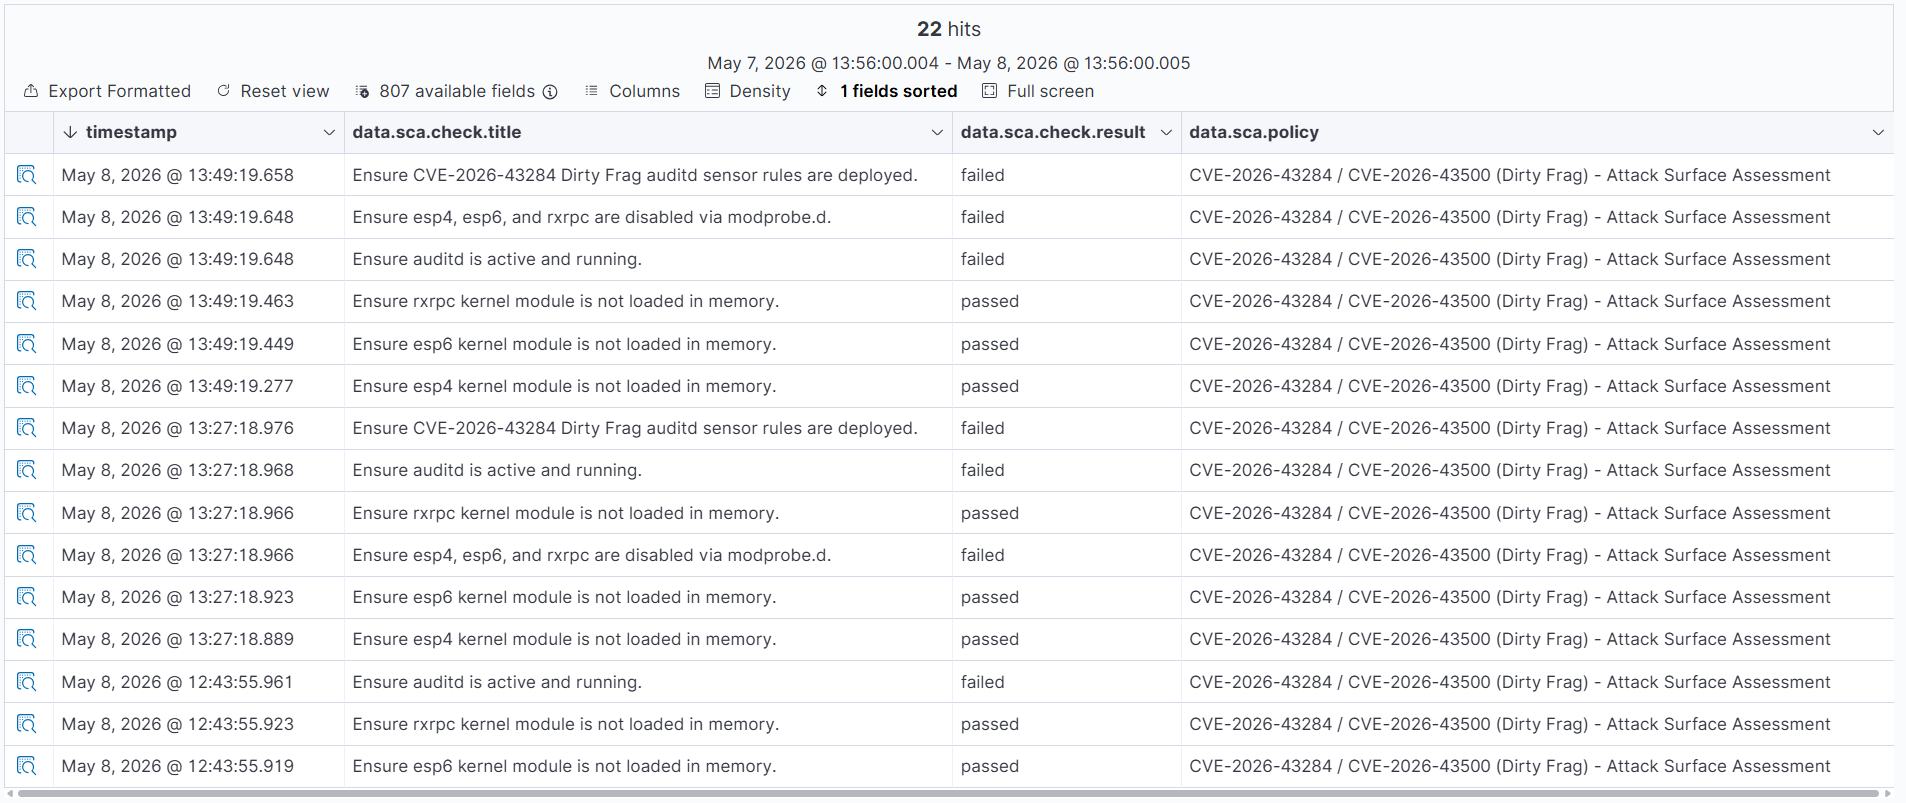 mym0us3r/dirty-frag-detection-with-wazuh-4.14.4
Wazuh 4.14.4 detection rules for CVE-2026-43284 / CVE-2026-43500 (Dirty Frag) - Linux Local Privilege Escalation via page cache write
 mrchucu1/cve-2022-0847-docker
Docker exploit
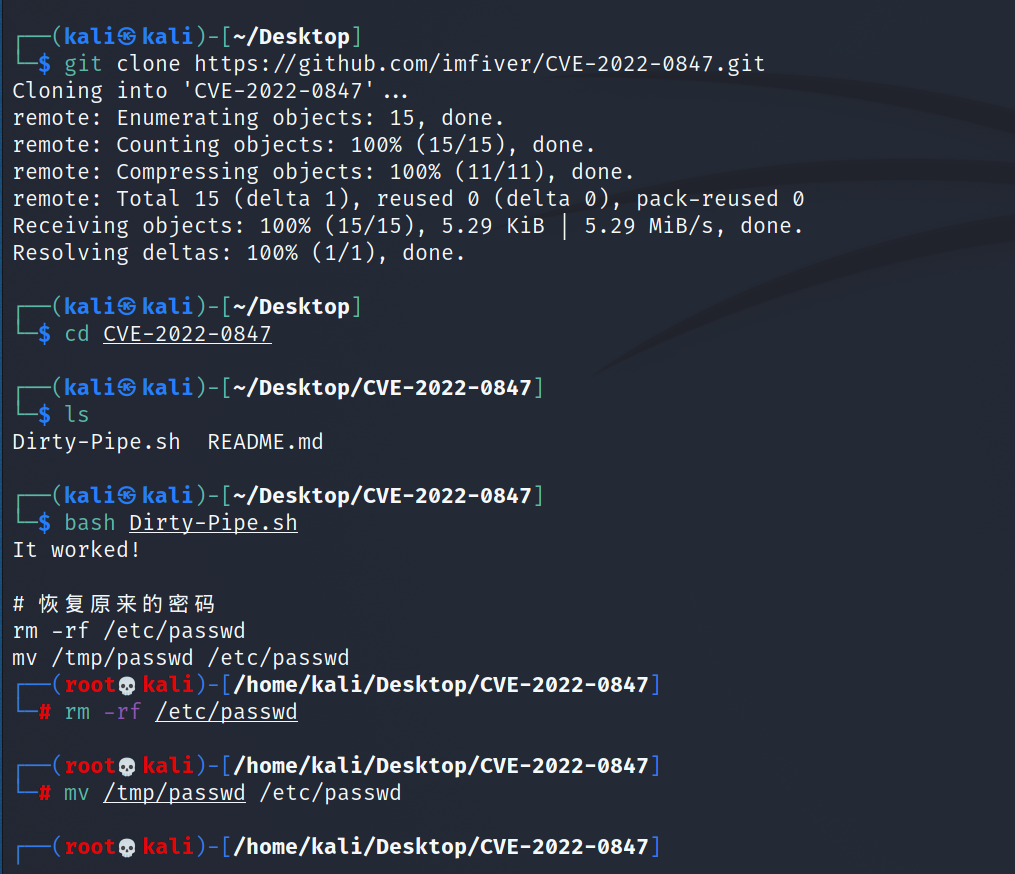 puckiestyle/cve-2022-0847
Proof-of-concept exploit for CVE-2022-0847 (Dirty Pipe) targeting Linux kernel versions 5.8–5.15. Provides reproduction environment setup and…
 justinye377/ctf-cve-2022-0847
CTF challenge deploying CVE-2022-0847 (Dirty Pipe) exploit to overwrite read-only files. Includes setup scripts, hints, and verification for kernel…
 marioalejos-cs/dirtycow-lab
Explotación vulnerabilidad Dirty COW (CVE-2016-5195) en Ubuntu 16.04.1.
 tulhan/commons-text-goat
An intentionally vulnerable webapp to get your hands dirty with CVE-2022-42889.