

secbox
 yv1ing/secbox
Conducting cybersecurity testing using the pi agent in a pre-built sandbox environment.
binary-exploitationctfdebuggers+9
yv1ing/secboxConducting cybersecurity testing using the pi agent in a pre-built sandbox environment.
 abraxas/n8n-function-vm2
Proof-of-concept and lab for an n8n 2.42.0 sandbox escape: hidden Function/FunctionItem nodes execute JS in the main process, giving authenticated…
 abraxas/cve-2026-19445-sni-uaf
Proof-of-concept lab for CVE-2026-19445, a CPython ssl SNI SSLContext use-after-free where a remote TLS client frees the server's dispatch context…
 jazho76/house_of_apple_2
Interactive GDB walkthrough of the House of Apple 2 FSOP technique on glibc 2.43, with a reproducible sandbox covering vtable bypass, stack pivoting,…
 top-celestial-company-ltd/dros-vep-lite
Open-source, 100% reproducible AI Agent Runtime Security Benchmark & Sandbox Environment (RFC-010 Draft Protocol).
 fuzzingbrain/fuzzingbrain-bench
A benchmark for LLM-driven bug discovery: 77 challenges across 43 open-source projects (C/C++/Java).
 gavz/cve-2026-21509-poc
Educational PoC generating a harmless DOCX with dummy OLE artifacts to test EDR/AV visibility, ASR rules, and sandbox analysis for CVE-2026-21509.…
 trailofbits/not-slithering-anywhere
The Python Version of our Not Go-ing Anywhere Vulnerable Application
 0x0allenace/windows-malware-behavioral-analysis
Behavioral Malware Analysis of a Simulated Multi-Stage Windows Malware Sample using FLARE-VM and REMnux. Evidence-driven DFIR investigation with IOC…
 phanhoangkhang/react2shell
Isolated Docker lab and static scanner for CVE-2025-55182, with vulnerable/patched Next.js builds and PoC validation of RSC Flight deserialization.
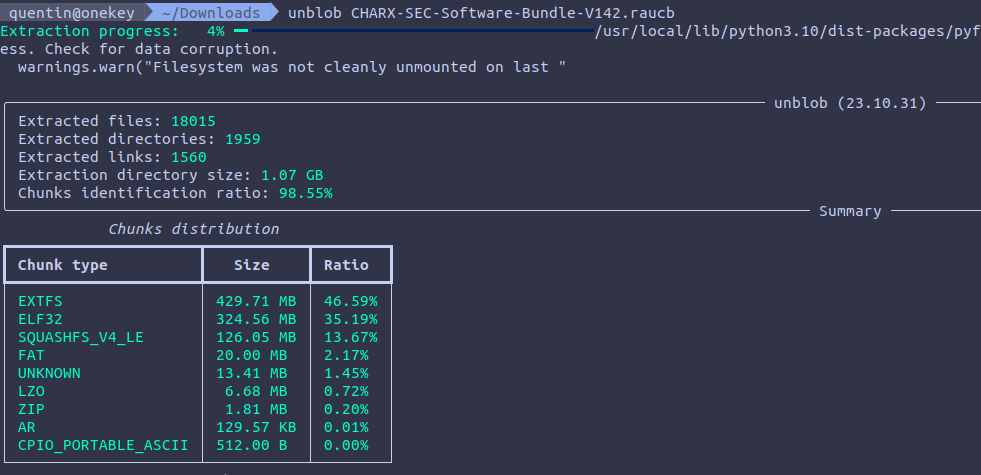 onekey-sec/firmware-workshop
In this workshop session, we will extract firmware from an EV charger, dig into the firmware, and eventually emulate it so we can interact with the…
 dinosn/fastjson-jsontype-rce-lab
Docker labs + defensive scanner for fastjson remote-class-load RCE. fastjson 1.2.66-1.2.83: @JSONType resource probe (CVE-2026-16723). fastjson2…
 sastraadiwiguna-purpleeliteteaming/holistic-deconstruction-of-cve-2019-5736-
This repository provides a high-fidelity technical deconstruction and production-ready exploitation suite for CVE-2019-5736. It demonstrates how a…
 f2u0a0d3/cve-2026-42945-nginx-rift-poc
PoC for CVE-2026-42945 (nginx Rift) — heap buffer overflow in ngx_http_rewrite_module. Includes detect/probe/exploit modes, dual-fixture Docker lab,…
 horkimhab/cve-2026-39813
CVE-2026-39813 - Fortinet Sandbox - Draft
 horkimhab/cve-2026-39808
CVE-2026-39808 - Fortinet Sandbox - Draft
 lat-06/cve-2026-34197
Proof-of-concept exploit for CVE-2026-34197, demonstrating authenticated remote code execution in Apache ActiveMQ via Jolokia JMX-HTTP bridge and…
 fkshield/cve-2025-5548
End-to-end exploitation lab for CVE-2025-5548 (FreeFloat FTP Server stack buffer overflow). Includes static analysis with IDA/Ghidra, binary fuzzing,…