

jellyfin-svg-gzip
 abraxas/jellyfin-svg-gzip
Jellyfin Server 12.2 - High - Remote - SSRF - gzip data:image/png leftover of GHSA-cf3c still fetches http and file
exploitationinformation-gatheringlabs-practice+3
abraxas/jellyfin-svg-gzipJellyfin Server 12.2 - High - Remote - SSRF - gzip data:image/png leftover of GHSA-cf3c still fetches http and file
 abraxas/pfsense-https-host-redirect
pfSense CE 2.9.0-DEVELOPMENT - Medium - Remote - Open redirect - HTTP 301 $http_host
 abraxas/gitea-git-redir-ssrf
Proof-of-concept and lab for an authenticated SSRF in Gitea's repo migrate endpoint, where git follows HTTP redirects into loopback git HTTP and…
 abraxas/moodle-grades-gradeitems
Moodle 5.2.3 - High - Remote - IDOR - core_grades_get_gradeitems lists hidden grade items
 b4sith-sec/gu3ssweak
Deliberately vulnerable Android app for mobile security research and bug bounty practice - OWASP Mobile Top 10
 devcop95/bugbounty-lab101
A complete bug bounty workspace for HackerOne researchers. Includes scope enforcement, automated recon/vuln pipeline (400+ tools), report templates,…
 1833ravikumar-max/cve-2021-41773-apache-path-traversal-lab
Docker-based cybersecurity lab for studying and reproducing CVE-2021-41773 in an isolated environment.
 sarthak4126/web-app-pentesting
Web application penetration testing lab — vulnerable Flask app, automated scanner, and professional pentest report. Covers OWASP Top 10, SQLi, XSS,…
 learnerxuan/cve-2026-29057-poc
Docker-based lab reproducing CVE-2026-29057 Next.js request smuggling, comparing vulnerable 15.5.12 against patched 15.5.13 with a raw chunked HTTP…
 mohammadalimehri/cve-2021-44790-lab
Dockerized Apache mod_lua lab with a Python PoC reproducing the CVE-2021-44790 multipart boundary buffer overflow for local defensive testing and…
 isaca0315/cve-2026-65013-bola-idor
Reproducible BOLA/IDOR PoC against Onlook's tRPC API (CVE-2026-65013), with a 12-step exploit chain, vulnerable and patched Docker targets, and…
 vanivamshi/cve-2013-2028-exploit
Docker-based lab and Python exploit for CVE-2013-2028, an Nginx 1.3.9 chunked-parser integer overflow, covering canary recovery, mprotect, and…
 dinosn/cve-2026-75650-magento-validation-lab
Docker lab reproducing the complete CVE-2026-75650 StyleSmuggler unauthenticated HTTP RCE and validating Adobe VULN-39341.
 joaovicdev/exploit-cve-2026-42559
Docker lab + Python PoC for CVE-2026-42559 - DNS rebinding via unvalidated Host header in the rmcp (Rust MCP SDK) Streamable HTTP server transport
 j3ssie/dynast-bench
A DAST benchmark of intentionally-vulnerable apps with ground-truth answer keys for scoring scanners
 pizz33/spring-cloud-function-spel
Reproduction environment and proof-of-concept for Spring Cloud Function SpEL injection leading to remote code execution, with a runnable Java 11 demo…
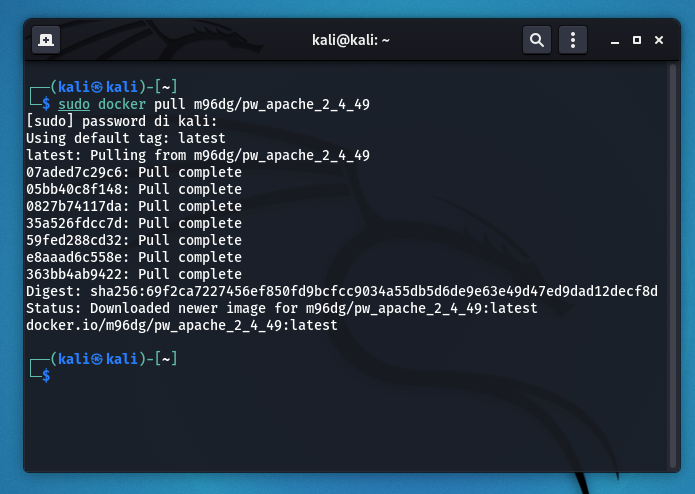 m96dg/cve-2021-41773-exercise
Hands-on lab to exploit Apache 2.4.49 path traversal (CVE-2021-41773) using Docker, Nmap scanning, and curl to retrieve a flag.
 dinosn/gitlab-cve-2026-19478-lab
Reproducible A/B lab + safe PoC for GitLab CVE-2026-19478 / CVE-2026-19650 (GraphQL @gl_introduced)