
cve-2026-105221-gist-tls
 abraxas/cve-2026-105221-gist-tls
CVE-2026-105221 - gist RubyGem - High - MITM - GitHub OAuth token theft
cryptographyexploitationlabs-practice+4
abraxas/cve-2026-105221-gist-tlsCVE-2026-105221 - gist RubyGem - High - MITM - GitHub OAuth token theft
 owasp/owasp-ctf-in-a-box
Self-hosted OWASP CTF kit: one box, one free GitHub org, no cloud dependencies
 boreas37/cve-2026-56705
PoC exploit for Adminer < 5.4.3 unauthenticated RCE via MSSQL PDO DSN injection, including Docker lab and negative test.
 abhayclasher/cve-2026-39866
Proof-of-concept lab demonstrating command injection in GitHub Actions workflow dispatch (CVE-2026-39866). Runs vulnerable and patched versions…
 batosay1337lab/cve-2026-31900-lab
CVE-2026-31900 Vulnerable Lab - psf/black GitHub Action RCE
 anggatechi/mass-scanner-cve-2026-3891
Python-based mass scanner for validating a specific WordPress AJAX behavior in authorized environments, supporting URL normalization, endpoint…
 hardik05/damn_vulnerable_c_program
An example C program which contains vulnerable code for common types of vulnerabilities. It can be used to show fuzzing concepts.
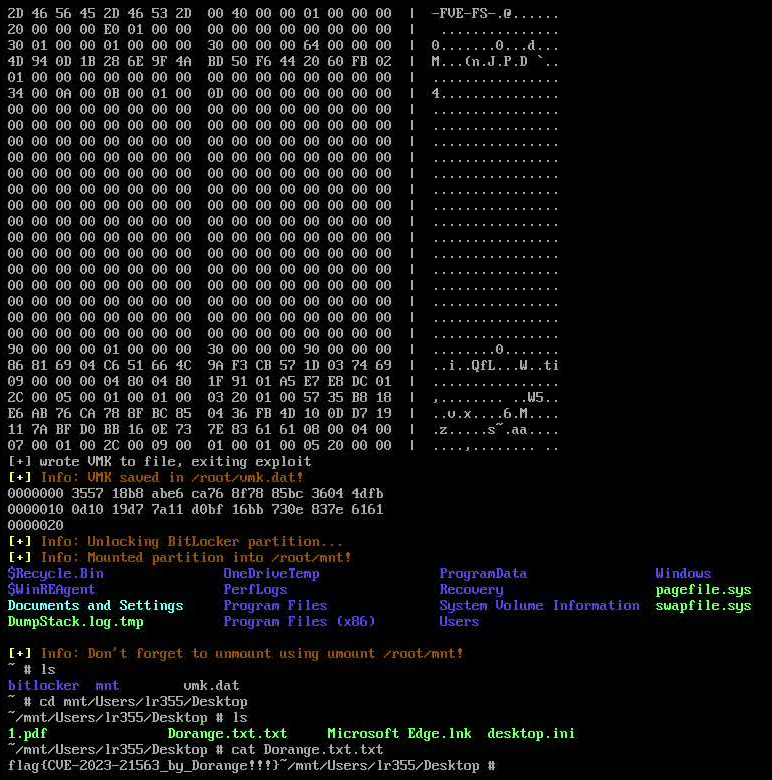 lr2006-robot/bitpixie
Cracking BitLocker encryption based on CVE-2023-21563 vulnerability
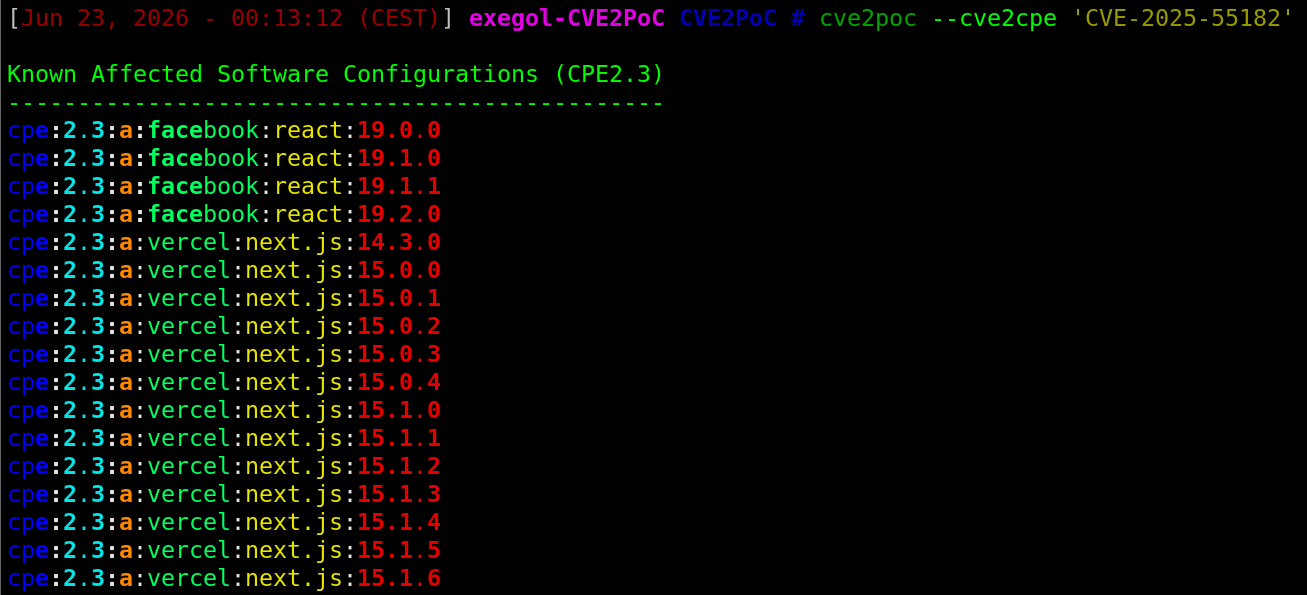 0liverflow/cve2poc
CVE2PoC is a tool that helps penetration testers, bug hunters, and security researchers quickly find public exploits or PoCs related to a CVE ID
 zkaaanon/proyectofinalso
Estudio del bug CVE-2026-31431
 natsuki-engr/live-server-evil-crawler
Live Server VSCode Vulnerability (CVE-2025-65717) Demo
 owasp/owasp-scs
OWASP Smart Contract Security (SCS) Project
 noah4puppy/cve-2024-21262
THREE different reproduction, WORKDIR, EXEC & RUNC.
 mallutrojan/cve-2023-30212-lab
GitHub repository with Dockerfile and files to create a vulnerable environment for CVE-2023-30212, enabling exploration of the exploitability of this…
 a-poc/blueteam-tools
Tools and Techniques for Blue Team / Incident Response
 ibondarenko1/azure-sentinel-detection-engineering
9 MITRE ATT&CK-mapped KQL detections on a live Microsoft Sentinel + Defender XDR environment (control-plane, endpoint, identity), with a PR-gated…
 enochgitgamefied/nextjs-cve-2025-29927
Intentionally vulnerable Next.js application demonstrating CVE-2025-29927 authentication bypass via middleware WAF evasion. Designed for security…