
CVE-2026-20896
 yym8538/cve-2026-20896
Proof-of-concept lab and Python/cURL scripts demonstrating CVE-2026-20896, an authentication bypass in official Gitea Docker images via the…
authenticationcontainer-securityexploitation+5
1
yym8538/cve-2026-20896Proof-of-concept lab and Python/cURL scripts demonstrating CVE-2026-20896, an authentication bypass in official Gitea Docker images via the…
 kaill-jlq/mmskillrisk
Benchmark and evaluation harness testing whether LLM agents resist malicious instructions hidden in multimodal skill images, with 108 cases across…
 dinosn/cve-2026-23989-opencloud-lab
Reproduction lab (A/B Docker) for CVE-2026-23989 — OpenCloud / ownCloud Infinite Scale public-link scope-validation bypass in Reva
 ctf-o-matic/capture-the-flag
Helper scripts to remaster Linux Live CD images for the purpose of creating ready to use security wargames with pre-installed vulnerabilities to…
 meganekos/secure-by-default-rce-demo
Secure-by-default demo lab showing how container hardening (distroless images, non-root, read-only filesystem, runtime-injected secrets) can…
 vettrivel007/cve-2024-1086
Proof-of-concept local privilege escalation exploit for CVE-2024-1086 targeting Linux kernels v5.14–v6.6. Achieves root shell with 99.4% success rate…
 hydragyrum/cve-2021-41773-playground
Some docker images to play with CVE-2021-41773 and CVE-2021-42013
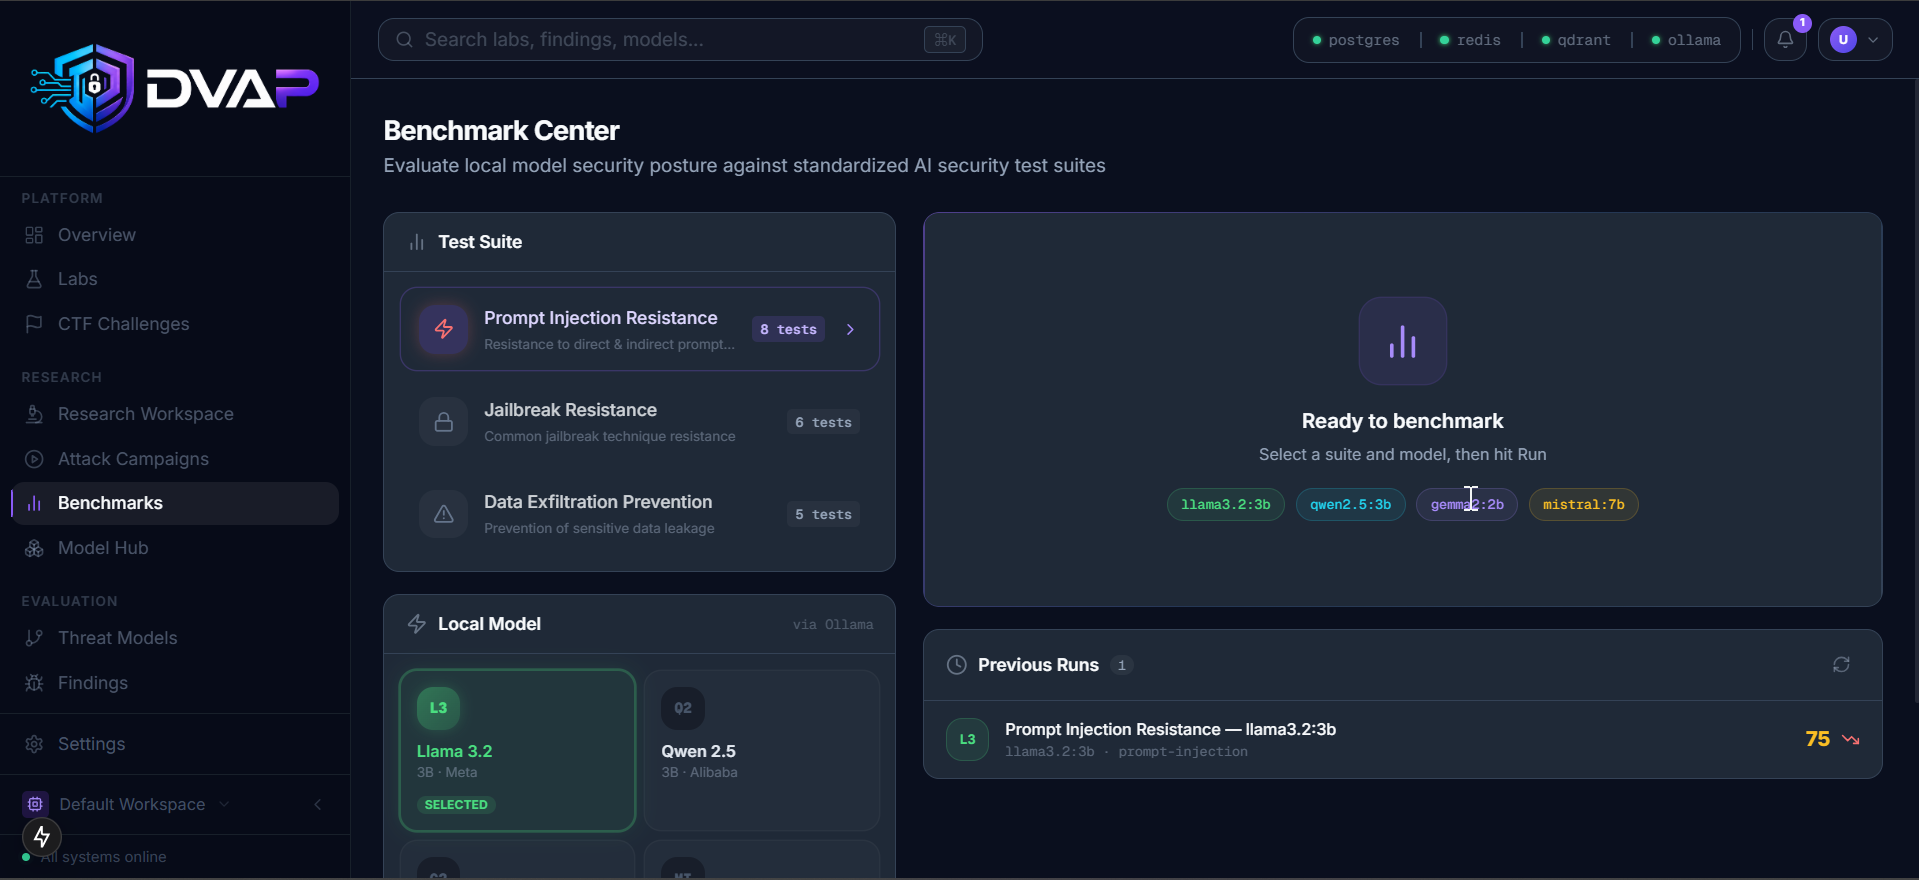 sonuoffsec/dvap
An OWASP-aligned intentionally vulnerable platform for learning and testing AI, LLM, RAG, MCP, and Agentic AI security.
 hkcfs/pil-cve-2017-8291
CVE-2017-8291 CTF with docker and examples
 developerfred/cve-2019-14206-poc
Proof-of-concept exploit for CVE-2019-14206, demonstrating arbitrary file deletion in the Adaptive Images WordPress plugin. Includes Docker lab,…
 battleofthebots/dejavu
Challenge based on CVE-2021-22204 where users send a malicious file to a web application to gain RCE
 ankur-katiyar/log4j-docker
Docker images and k8s YAMLs for Log4j Vulnerability POC (Log4j (CVE-2021-44228 RCE Vulnerability)
 edgecases-purplehax/cve-images
Intentionally-vulnerable nginx 1.30.0 CVE lab images (CVE-2026-40701/42934/42945/42946) for isolated security research. Lab use only.
 blueteamsteve/cve-2021-41773
Vulnerable docker images for CVE-2021-41773

 rode0day/fuzzer-testing
Docker images for testing fuzzers on the Rode0day corpora