Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
87 results
pfsense-timezone-phpini preview

pfsense-timezone-phpini

GitHubabraxas/pfsense-timezone-phpini

pfSense CE 2.9.0-DEVELOPMENT - High - Remote - RCE - timezone php.ini prepend
exploitationlabs-practicepayload-development+4
14 days ago
CVE-2026-48356 preview

CVE-2026-48356

GitHubabraxas/cve-2026-48356

Proof-of-concept and lab pack for CVE-2026-48356, an unauthenticated unrestricted file upload in Magento Open Source guest-cart REST custom options.
exploitationlabs-practicepayload-generation+5
17h 4m ago
CVE-2026-75650 preview

CVE-2026-75650

GitHubabraxas/cve-2026-75650

Disclosure pack and lab reproduction script for CVE-2026-75650, an unauthenticated SSTI RCE in Magento Open Source GraphQL email templates.
exploitationlabs-practicepayload-development+5
17h 4m ago
CVE-2026-87902 preview

CVE-2026-87902

GitHubcrowsec-edtech/cve-2026-87902

Python PoC exploiting CVE-2026-87902, an unauthenticated path traversal in WordPress locate_template() leading to LFI and PEAR-based RCE, with safe…
exploitationlabs-practicepayload-development+5
31 month ago
Comment2Shell preview

Comment2Shell

GitHubdeathshotxd/comment2shell

Zero-click pre-auth WordPress CVE-2026-93485 exploit chain: stored XSS in wpautop() escalates to admin-session plugin upload and a self-deleting…
exploitationlabs-practicepayload-development+7
6423 days ago
PixelSmash preview

PixelSmash

GitHubse1ims/pixelsmash

Proof-of-concept and lab harness for CVE-2026-8461, an out-of-bounds write in FFmpeg's MagicYUV decoder, with payload generator and Qt demo player.
binary-exploitationeducationexploitation+6
1 month ago
CVE-2026-29057-POC preview

CVE-2026-29057-POC

GitHublearnerxuan/cve-2026-29057-poc

Docker-based lab reproducing CVE-2026-29057 Next.js request smuggling, comparing vulnerable 15.5.12 against patched 15.5.13 with a raw chunked HTTP…
educationexploitationlabs-practice+5
1 month ago
CVE-2026-90817 preview

CVE-2026-90817

GitHubexdev994/cve-2026-90817

Python PoC for CVE-2026-90817, an unauthenticated REDCap RCE via survey passthrough routing and file-path injection, with a Docker lab and…
exploitationlabs-practicepayload-development+5
1 month ago
JFrog_CVE-2026-65615-ByGLM preview

JFrog_CVE-2026-65615-ByGLM

GitHubbl0odz/jfrog_cve-2026-65615-byglm

JFrog Artifactory 预认证全链 RCE 复现项目(CVE-2026-42018 / CVE-2026-65616 / CVE-2026-65615):完整攻击链报告、7.146.7 Docker 复现交付物(EXP / 部署 / 基线验证 / payload 样本 / 恢复工具)
educationexploitationlabs-practice+7
1 month ago
tomcat-cve-2025-24813-lab preview

tomcat-cve-2025-24813-lab

GitHubmega-starmie/tomcat-cve-2025-24813-lab

Local reproduction lab for Apache Tomcat CVE-2025-24813, documenting exploitation conditions and AI-assisted verification of the vulnerability.

educationexploitationlabs-practice+4
1 month ago
Spring4Shell-POC preview

Spring4Shell-POC

GitHublunasec-io/spring4shell-poc

This is a dockerized application that is vulnerable to the Spring4Shell vulnerability (CVE-2022-22965).
exploitationlabs-practicepayload-development+4
1064 years ago
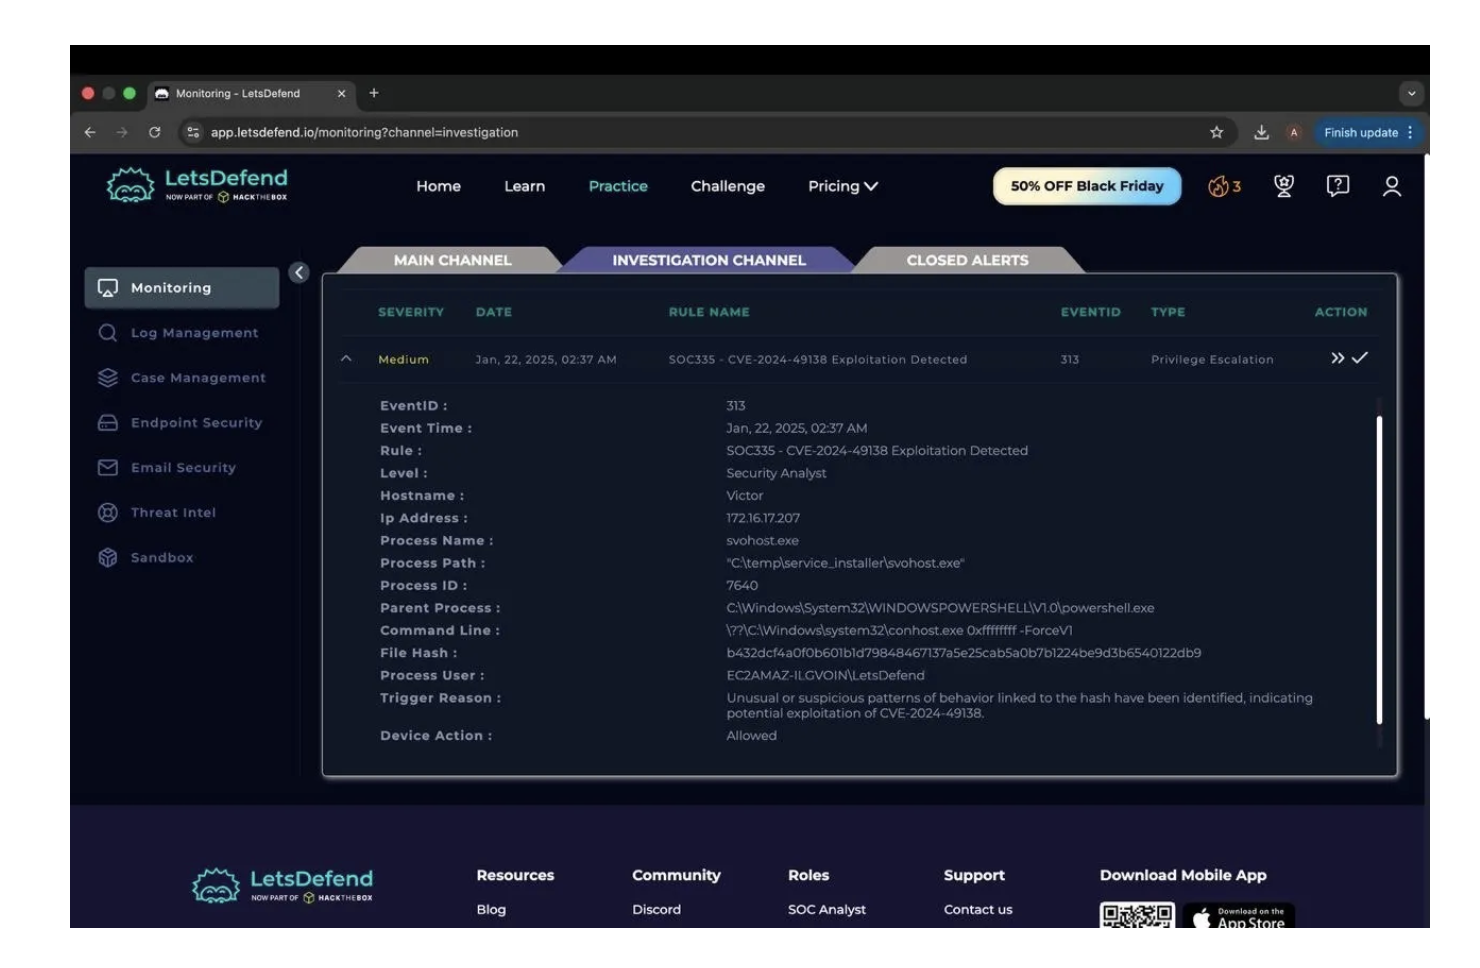
CVE-2024-49138-SOC-Investigation preview

CVE-2024-49138-SOC-Investigation

GitHubadisasoc/cve-2024-49138-soc-investigation

SOC investigation of CVE-2024-49138 exploitation involving brute-force activity, PowerShell execution, malicious payload analysis, privilege…
digital-forensicseducationincident-response+4
1 month ago
CVE-2026-24061-PoC-Telnetd preview

CVE-2026-24061-PoC-Telnetd

GitHubandroidteacher/cve-2026-24061-poc-telnetd

Proof-of-concept exploit for CVE-2026-24061, an unauthenticated remote root privilege escalation in inetutils-telnetd via USER environment variable…
binary-exploitationeducationexploitation+3
9 months ago
CVE-2025-1094-Lab-Setup preview

CVE-2025-1094-Lab-Setup

GitHubpinkarmor/cve-2025-1094-lab-setup

Hands-on lab to exploit CVE-2025-1094, a PostgreSQL psql SQL injection leading to RCE via COPY TO PROGRAM, with Docker setup and reverse shell…
educationexploitationlabs-practice+3
1 year ago
CVE-2026-34197 preview

CVE-2026-34197

GitHubkondordevsecuritycorp/cve-2026-34197

Exploit for Apache ActiveMQ RCE via Jolokia API (CVE-2026-34197) with command output capture, mass scanning, and auto-exploitation.
exploitationlabs-practicepayload-generation+4
26 months ago
CVE-2026-34197 preview

CVE-2026-34197

GitHubdevsecurityspro/cve-2026-34197

Proof-of-concept exploit for CVE-2026-34197, an RCE in Apache ActiveMQ via the Jolokia API. Includes a Python exploit, payload template, and Docker…
educationexploitationlabs-practice+4
46 months ago
CVE-2025-55182 preview

CVE-2025-55182

GitHubmr-destroyer/cve-2025-55182

Exploit for CVE-2025-55182 enabling remote code execution via prototype pollution in Next.js React Server Components, with command execution and…

exploitationlabs-practicepayload-development+4
2 months ago
Burp-Suite-Certified-Practitioner-Exam-Study preview

Burp-Suite-Certified-Practitioner-Exam-Study

GitHubbotesjuan/burp-suite-certified-practitioner-exam-study

Practical study notes and walkthroughs for PortSwigger Academy labs, covering web vulnerabilities, payloads, enumeration, and BSCP exam strategies.

curated-resourceseducationinformation-gathering+7
1.5k2 months ago
Previous12345Next