

Spring4Shell-POC
 lunasec-io/spring4shell-poc
This is a dockerized application that is vulnerable to the Spring4Shell vulnerability (CVE-2022-22965).
exploitationlabs-practicepayload-development+4
106
lunasec-io/spring4shell-pocThis is a dockerized application that is vulnerable to the Spring4Shell vulnerability (CVE-2022-22965).
 r4ch1d0/cve-2018-14667_lab_poc
Demonstration of the expression language (EL) injection vulnerability CVE-2018-14667 using the photoalbum lab under Jboss application server
 makarov05bm/wsgoat
The vulnerable application that will teach you how to hack WebSockets
 paulvkitor/log4shellwithlog4j2_13_3
Springboot web application accepts a name get parameter and logs its value to log4j2. Vulnerable to CVE-2021-44228.
 webgoat/webgoat
Deliberately vulnerable web application with interactive lessons and challenges for learning web application security and penetration testing…
 commando-x/vuln-bank
Intentionally vulnerable banking platform for practicing web application, API, and AI/LLM security testing, secure code review, and DevSecOps…
 ransomleak/training-application-security
Interactive secure coding training with hands-on SCORM exercises covering OWASP Top 10 web and API vulnerabilities, Git/secrets exposure, and…
 cy-clon3/awesome-ios-security
A curated list of awesome iOS application security resources.
 prateek147/dvia-v2
Damn Vulnerable iOS App (DVIA) is an iOS application that is damn vulnerable. Its main goal is to provide a platform to mobile security…
 tandasat/hypervisor-101-in-rust
The materials of "Hypervisor 101 in Rust", a one-day long course, to quickly learn hardware-assisted virtualization technology and its application…
 george0papasotiriou/cve-2026-11119-padding-oracle-attack-on-cbc-mode-encryption
Demonstrates a padding oracle attack against AES-CBC encryption using a vulnerable Flask decrypt endpoint and a Python exploit script to decrypt…
 nccgroup/vulnerabledotnethttpremoting
Example Vulnerable .NET HTTP Remoting
 bishopfox/vulnerablegwtapp
An intentionally-vulnerable GWT-based web application to test tooling and techniques
 mobetasec/cve-2024-1813-poc
PoC exploit for CVE-2024-1813: PHP object injection in Simple Job Board WordPress plugin, achieving unauthenticated RCE via gadget chain. Includes…
 lite-os15/lab-001-gitea-cve-2026-20896-
Educational lab for exploiting Gitea CVE-2026-20896, focusing on web application vulnerability analysis and penetration testing.
 theronielanddaronpodcastshow/svja
The Super Vulnerable Java Application (SVJA), as demonstrated in the Roniel and DaRon Podcast Show, is an Apache Struts application designed to…
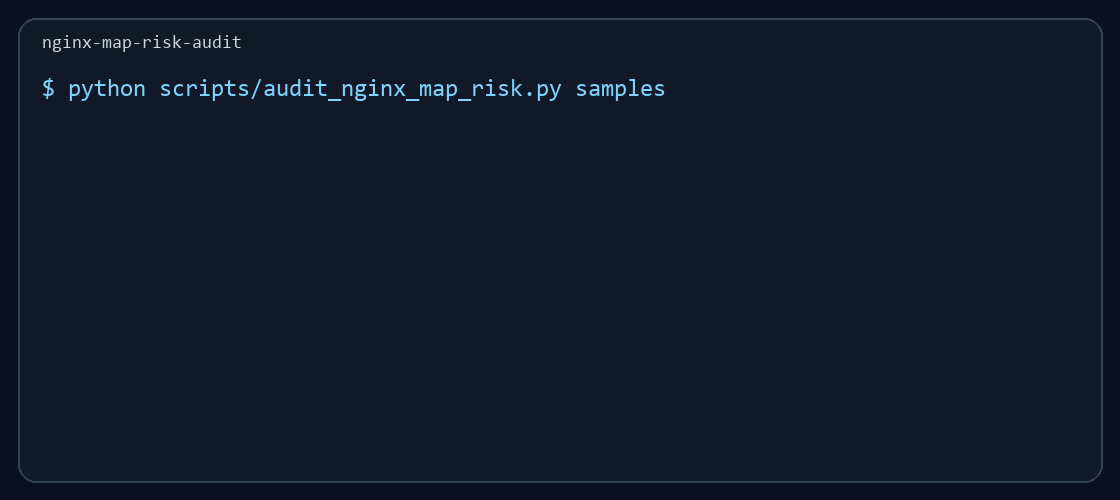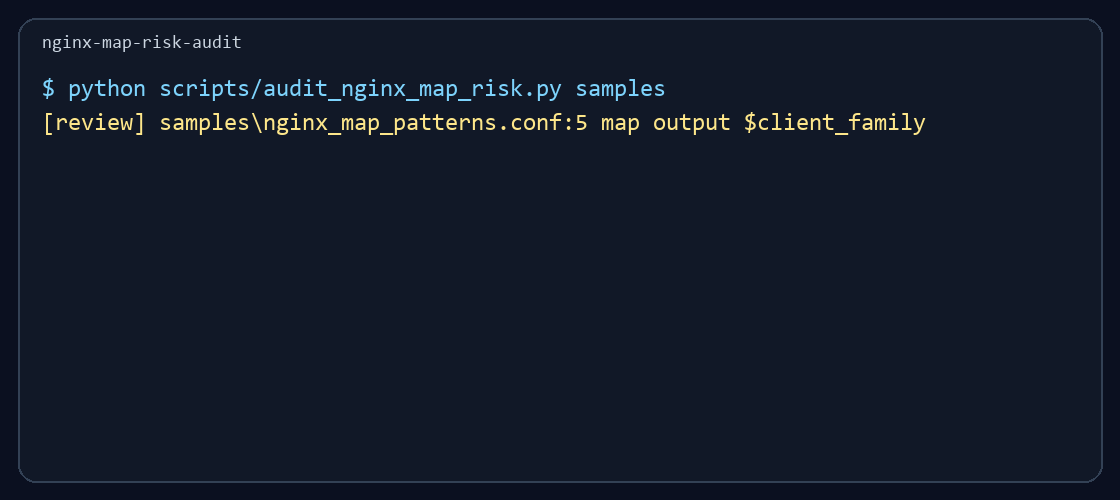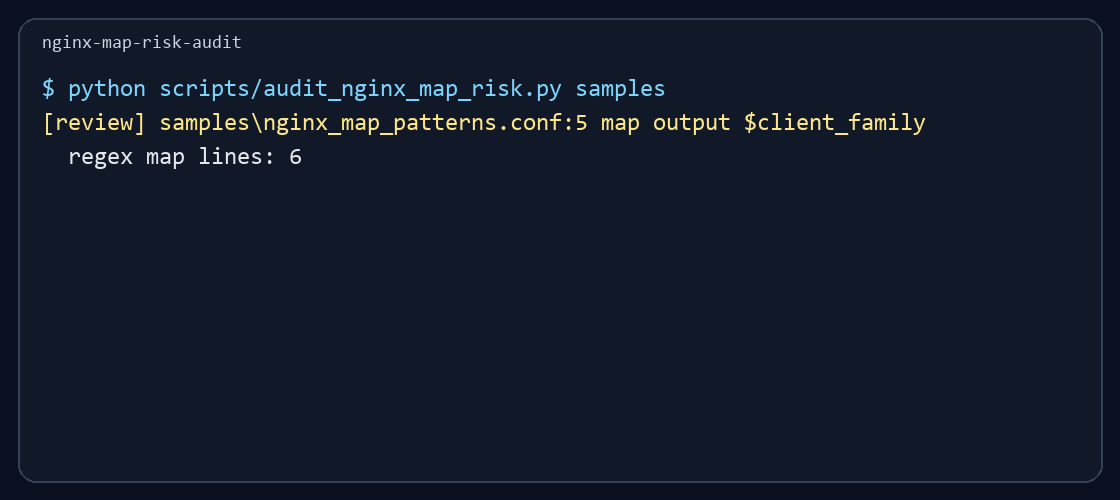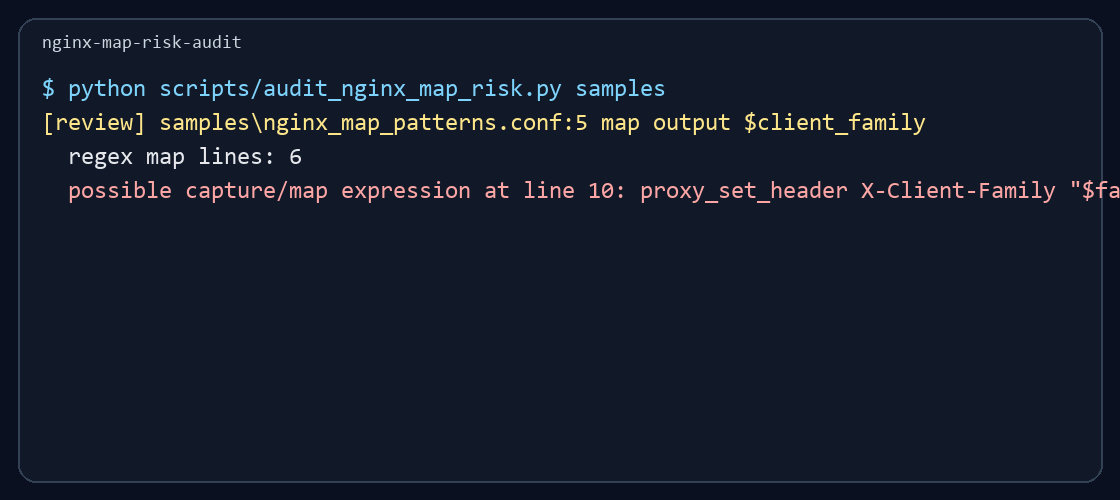 srkyn/nginx-map-risk-audit
Defensive NGINX CVE-2026-42533 map regex risk audit with config scanner, Splunk/Defender notes, and lab evidence.
 owasp/dvsa
a Damn Vulnerable Serverless Application