
not-slithering-anywhere
 trailofbits/not-slithering-anywhere
The Python Version of our Not Go-ing Anywhere Vulnerable Application
dynamic-analysis-sandboxingeducationlabs-practice+3
11
trailofbits/not-slithering-anywhereThe Python Version of our Not Go-ing Anywhere Vulnerable Application
 yonliud/cve-2026-76904
One-Day POC | GeoServer Unauthenticated SQL injection to complete RCE
 trailofbits/not-going-anywhere
Intentionally vulnerable Golang programs exposing web, gRPC, and database/sql flaws for security training, vulnerability discovery, and remediation…
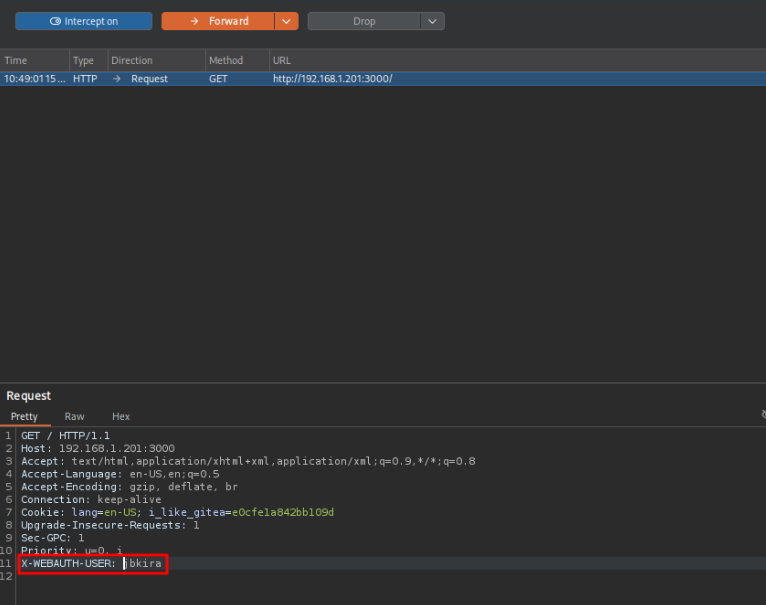 judgedbykira/cve-2026-20896-gitea-authentication-bypass
An explanation and PoC to exploit CVE-2026-20896 Authentication Bypass Vulnerability on Gitea. Being able to steal session tokens for valid users in…
 joaovicdev/exploit-cve-2026-40901
Automated exploit for DataEase: 4-vulnerability chain (auth bypass, JDBC blocklist bypass, SQL injection, Java deserialization) achieving…
 owasp/nodegoat
The OWASP NodeGoat project provides an environment to learn how OWASP Top 10 security risks apply to web applications developed using Node.js and how…
 uname1able/cve-2025-21333
Proof-of-concept exploit for CVE-2025-21333, a heap-based buffer overflow in Hyper-V's vkrnlintvsp.sys leading to local privilege escalation via I/O…
 sischkg/cve-2018-5740
Proof-of-concept exploit for CVE-2018-5740, a denial-of-service vulnerability in BIND DNS server triggered by a crafted DNAME query, with…
 sirbuvladste/bind-9-cache-poisoning-poc---cve-2025-40778
Proof of Concept for CVE-2025-40778: BIND 9 DNS Cache Poisoning via unsolicited Additional Section records.
 axelcurmi/log4shell-docker-lab
Log4Shell (CVE-2021-44228) docker lab
 zeyad-azima/cve-2022-1388
F5 BIG-IP iControl REST vulnerability RCE exploit with Java including a testing LAB
 ikarolaborda/cve2026-42926
Controlled NGINX HTTP/2 frame injection lab for CVE-2026-42926 patch validation and defensive research
 cedric-martz/ethernalblue_report
This is a security assessment report regarding the EthernalBlue vulnerability (CVE-2017-0143).
 alexsvobo/nhi-zero-trust-bypass
Demonstrates a real-world zero-trust bypass by exploiting BIND CVE-2025-40775 to disrupt DNS, break secret rotation, and expose static credentials in…
 acceis/exploit-cve-2023-38490
Kirby < 3.9.6 XML External Entity exploit
 ricterz/pie-stack-clash-cve-2017-1000253
Demo-ing CVE-2017-1000253 in a container
 ahmedmansour93/event-id-217-rule-name-soc254-apache-ofbiz-auth-bypass-and-code-injection-0day-cve-2023-51467-
🚨 Just completed an incident report on Event ID 217: Apache OFBiz Auth Bypass and Code Injection 0-Day (CVE-2023-51467). This critical vulnerability…
 a0xnirudh/kurukshetra
Kurukshetra - A framework for teaching secure coding by means of interactive problem solving.