
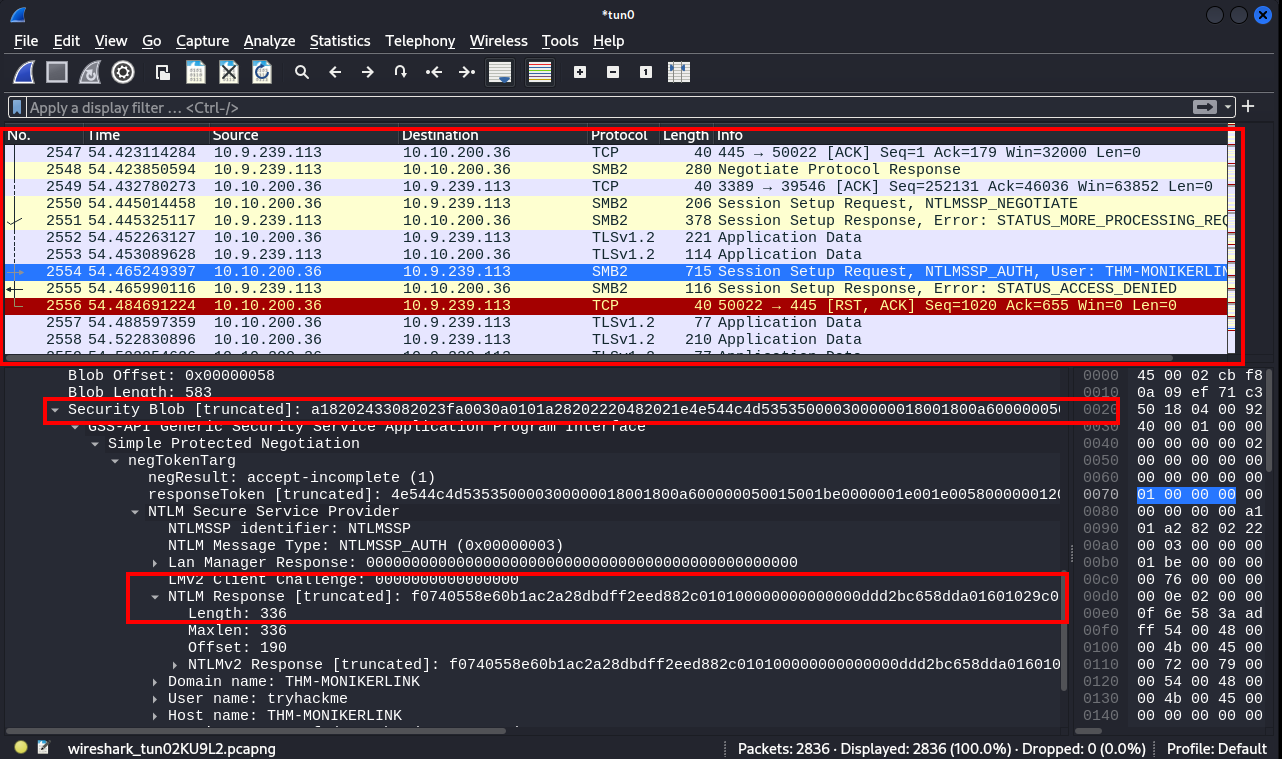
tryhackme-moniker-link
 yfelipecruvinel/tryhackme-moniker-link
Documentation of my hands-on lab Moniker Link (CVE-2024-21413) completed on TryHackMe.
educationemail-securityexploitation+3
yfelipecruvinel/tryhackme-moniker-linkDocumentation of my hands-on lab Moniker Link (CVE-2024-21413) completed on TryHackMe.
 mrintern/thm_steelmountain_cve-2014-6287
a python3 version of the exploit written for CVE-2014-6287. Useful for completing the "Steel Mountain" room on TryHackMe.com without the use of…
 shauryarathore357-hub/thm-moniker-link-cve-2024-21413-writeup
TryHackMe room walkthrough of CVE-2024-21413, covering the Outlook Moniker Link Protected View bypass, NTLM hash leaking, and credential capture with…
 cliffe/breakescape
Mountable Rails engine providing 24+ cybersecurity escape room scenarios with randomized passwords, JIT-compiled NPC dialogue, and RESTful API for…
 lavanya2085/solar-exploiting-log4j
This repository provides a detailed walkthrough of the *Solar Exploiting Log4j room* on TryHackMe, focusing on exploiting the critical Log4Shell…
 musa-xvi/active-directory-badsuccessor
A TryHackme room covering the CVE-2025-53779 exploitation using windows
 johnwickakash12/cve-2021-41773
Detailed writeup of CVE-2021-41773 Apache path traversal and RCE exploitation, with step-by-step commands and root cause analysis from a TryHackMe…
 adityabhatt3010/room-walkthrough-billing
A detailed walkthrough of Billing room exploiting CVE-2023-30258 and escalating via fail2ban misconfig
 revyhub/cve-2026-43284---dirtyfrag-analysis-thm-
TryHackMe Dirty Frag (CVE-2026-43284) — Linux LPE writeup
 j4ck3lsyn-gen2/n8n-cve-2025-68613-tryhackme
The minor methodology for room: https://tryhackme.com/room/n8ncve202568613
 0xtas/cve-2012-2982
Exploits CVE-2012-2982 in Webmin with a Rust PoC that delivers a configurable TCP reverse shell and optional Netcat listener.
 asg-castle/cve-2021-4034
Security documentation and lab companion for the polkit pkexec local privilege escalation, with a TryHackMe room for hands-on exploitation practice.
 cpyre/cve-2012-2982
Practice POC scripting in Tryhackme’s intro poc scripting room (For Linux)