Burp-Suite-Certified-Practitioner-Exam-Study

Practical study notes and walkthroughs for PortSwigger Academy labs, covering web vulnerabilities, payloads, enumeration, and BSCP exam strategies.

Practical study notes and walkthroughs for PortSwigger Academy labs, covering web vulnerabilities, payloads, enumeration, and BSCP exam strategies.

Comprehensive Java vulnerability lab with vulnerable and fixed code, attack scenarios, source/sink audit notes, and secure coding guidance for…

Atomic web vulnerability labs. One OWASP flaw per app — minimal Flask + Docker, intentionally broken for hands-on study with Burp Suite.

PoC and test server

CVE proof-of-concept labs, exploit scripts, and detection/prevention rules (Nginx, Apache, Snort, YARA) for high-severity CVEs. Authorized security…

CVE-2021-44228 Vulnerability Reproduction Environment CVE-2021-44228 漏洞复现环境

Proof-of-concept exploit for CVE-2020-13925, a command injection vulnerability in Apache Kylin's diagnostic API, allowing remote code execution via…

In-depth technical analysis and proof-of-concept for CVE-2017-9822, an insecure deserialization vulnerability in DotNetNuke leading to remote code…

PHP CVE-2026-109618/109619 — self-contained unauthenticated RCE on stock PHP 8.5.11 (in-band PS(id)→cookie memory disclosure + UAF chain), full…

CVE-2025-26794: Blind SQL injection in Exim 4.98 (SQLite DBM)- exploit writeup

Hands-on exploit lab for CVE-2024-28000 — unauthenticated privilege escalation in LiteSpeed Cache (WordPress plugin, <=6.3.0.1). Spins up a…

Educational Docker-based lab demonstrating the Heartbleed bug (CVE-2014-0160) with hacker, victim, and server containers for hands-on exploitation…

PoC for CVE-2026-87902 — unauthenticated path traversal in WordPress page-template resolution (local PHP inclusion, conditional RCE) with a pinned…

Step-by-step lab environment for exploiting CVE-2019-0232, a Tomcat CGI command injection vulnerability, with setup instructions and payload examples.

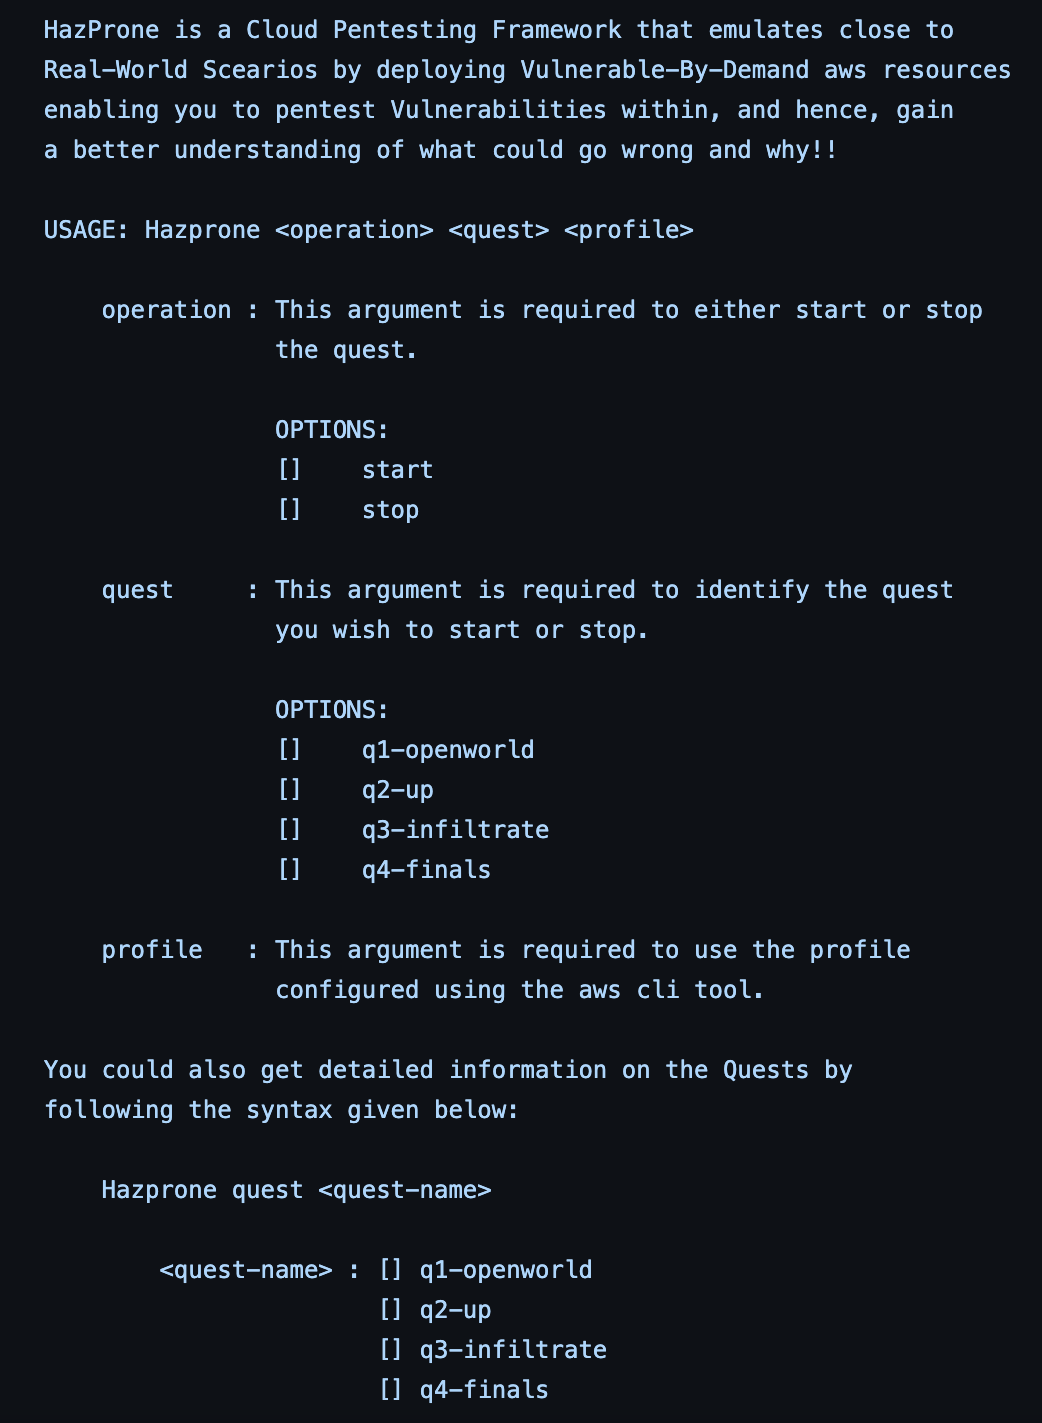
Cloud pentesting framework deploying vulnerable-by-demand AWS resources with quest-based scenarios to teach practical penetration testing and…

Demonstrates exploitation of CVE-2024-4577, a PHP CGI RCE on Windows, including attack steps, reverse shell deployment, and ransomware simulation…

Exploit a 2021 Kernel vulnerability in Ubuntu to become root almost instantly!

LazyWeb is a demonstration web application designed to showcase common server-side application vulnerabilities. Each vulnerability is categorized…