
CVE-2026-5718-Lab
 rootdirective-sec/cve-2026-5718-lab
Local Docker lab demonstrating CVE-2026-5718 arbitrary file upload in a WordPress plugin, with vulnerable and patched services for side-by-side…
ctfeducationexploitation+3
1
rootdirective-sec/cve-2026-5718-labLocal Docker lab demonstrating CVE-2026-5718 arbitrary file upload in a WordPress plugin, with vulnerable and patched services for side-by-side…
 bahartanir/wp2shell-scanner
CVE-2026-63030 / CVE-2026-60137 - WordPress pre-auth RCE scanner
 codeb0ssx/ultimate-wp2shell
wp2shell — Pre-authentication RCE in WordPress Core (CVE-2026-60137 + CVE-2026-63030). Chains an SQL injection in author__not_in with batch-route…
 dinosn/cve-2026-87902-wordpress-lfi-lab
Reproduction lab + URL-list scanner + PoC for CVE-2026-87902 / GHSA-7hp8-65ch-5whp — WordPress get_page_template() unauthenticated LFI to conditional…
 dinosn/givewp-cve-2026-82222-rce-lab
Authorized Docker lab and clean PoC for validating CVE-2026-82222 RCE in GiveWP 4.16.5.1 and the 4.16.7.2 fix.
 shawnng078-ops/cve-2024-28000-exploit-lab
Hands-on reproduction of CVE-2024-28000 in LiteSpeed Cache using an isolated WordPress lab. Includes reconnaissance, vulnerable hash recovery,…
 joaovicdev/exploit-cve-2026-63030
Docker-based vulnerable WordPress lab with Python exploit demonstrating pre-auth route confusion and SQL injection chain (CVE-2026-63030 +…
 ivanbg2004/odh-bricksbuilder-cve-2024-25600-thm
OD&H's scanner for CVE-2024-25600 vulnerability in the Bricks Builder WordPress plugin. For use in Try Hack Me (THM) environments.
 hassham1/cve-2026-87902
WordPress Core <= 7.1.1 unauthenticated LFI to RCE - validation lab, PoC, nuclei template (GHSA-7hp8-65ch-5whp)
 joaovicdev/exploit-cve-2026-87902
Lab vulnerável (Docker) + PoC Python para a CVE-2026-87902 — path traversal não autenticado no WordPress Core (page-template -> LFI -> RCE…
 vulpecuna/cve-2026-87902
Python PoC for CVE-2026-87902, an unauthenticated WordPress path traversal RCE via get_page_template(), with version fingerprinting, theme checks,…
 abraxas/cve-2026-19952
Proof-of-concept and disclosure pack for CVE-2026-19952, an unauthenticated arbitrary file deletion in the WordPress Frontend Admin plugin, with lab…
 abraxas/cve-2026-81294
Proof-of-concept and lab reproduction for CVE-2026-81294, an unauthenticated privilege escalation in the WordPress Authorizer plugin via unverified…
 thecyberfairy/cve-lfi-lab
A hands on lab investigating CVE-2025-39507 from a Tier 1 SOC analyst perspective. Includes log review in Microsoft Sentinel, IP analysis, real world…
 griisemine/cve-2026-87902-detection
Detection toolkit and reproducible lab for CVE-2026-87902, an unauthenticated WordPress path traversal. Includes remote checker, IoC analyzer, Sigma…
 deathshotxd/comment2shell
Zero-click pre-auth WordPress CVE-2026-93485 exploit chain: stored XSS in wpautop() escalates to admin-session plugin upload and a self-deleting…
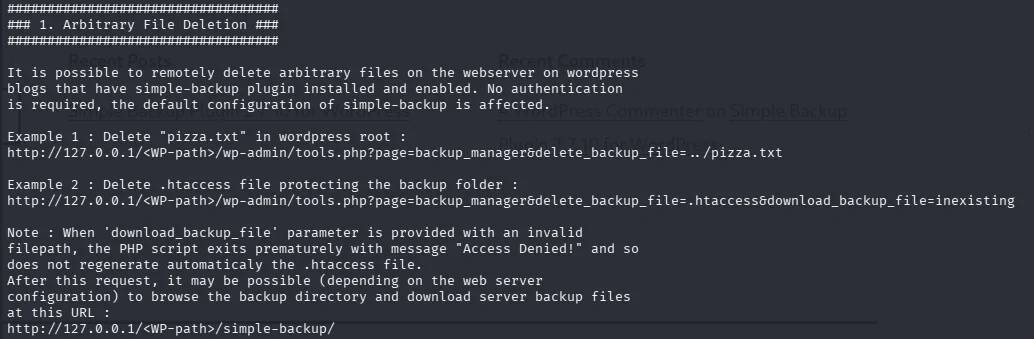 capivara-research/wordpress-path-traversal-cve-2019-11447
Detailed penetration test report demonstrating unauthenticated path traversal (CVE-2019-11447) in WordPress Simple Backup plugin, including…