
awesome-osint-arsenal
 rawfilejson/awesome-osint-arsenal
OSINT & recon toolkit // 100+ tools, one-command installer, SOCMINT, GEOINT, network recon, dark web, forensics & more.
ctfcurated-resourcesdigital-forensics+8
3.2k
rawfilejson/awesome-osint-arsenalOSINT & recon toolkit // 100+ tools, one-command installer, SOCMINT, GEOINT, network recon, dark web, forensics & more.
 hamed233/cybersecurity-mastery-roadmap
A comprehensive, step-by-step guide to mastering cybersecurity from beginner to expert level with curated resources, tools, and career guidance
 juice-shop/juice-shop
Intentionally vulnerable web application covering OWASP Top 10 vulnerabilities for security training, CTF competitions, and penetration testing…
 doretox/atomicvulns
Atomic web vulnerability labs. One OWASP flaw per app — minimal Flask + Docker, intentionally broken for hands-on study with Burp Suite.
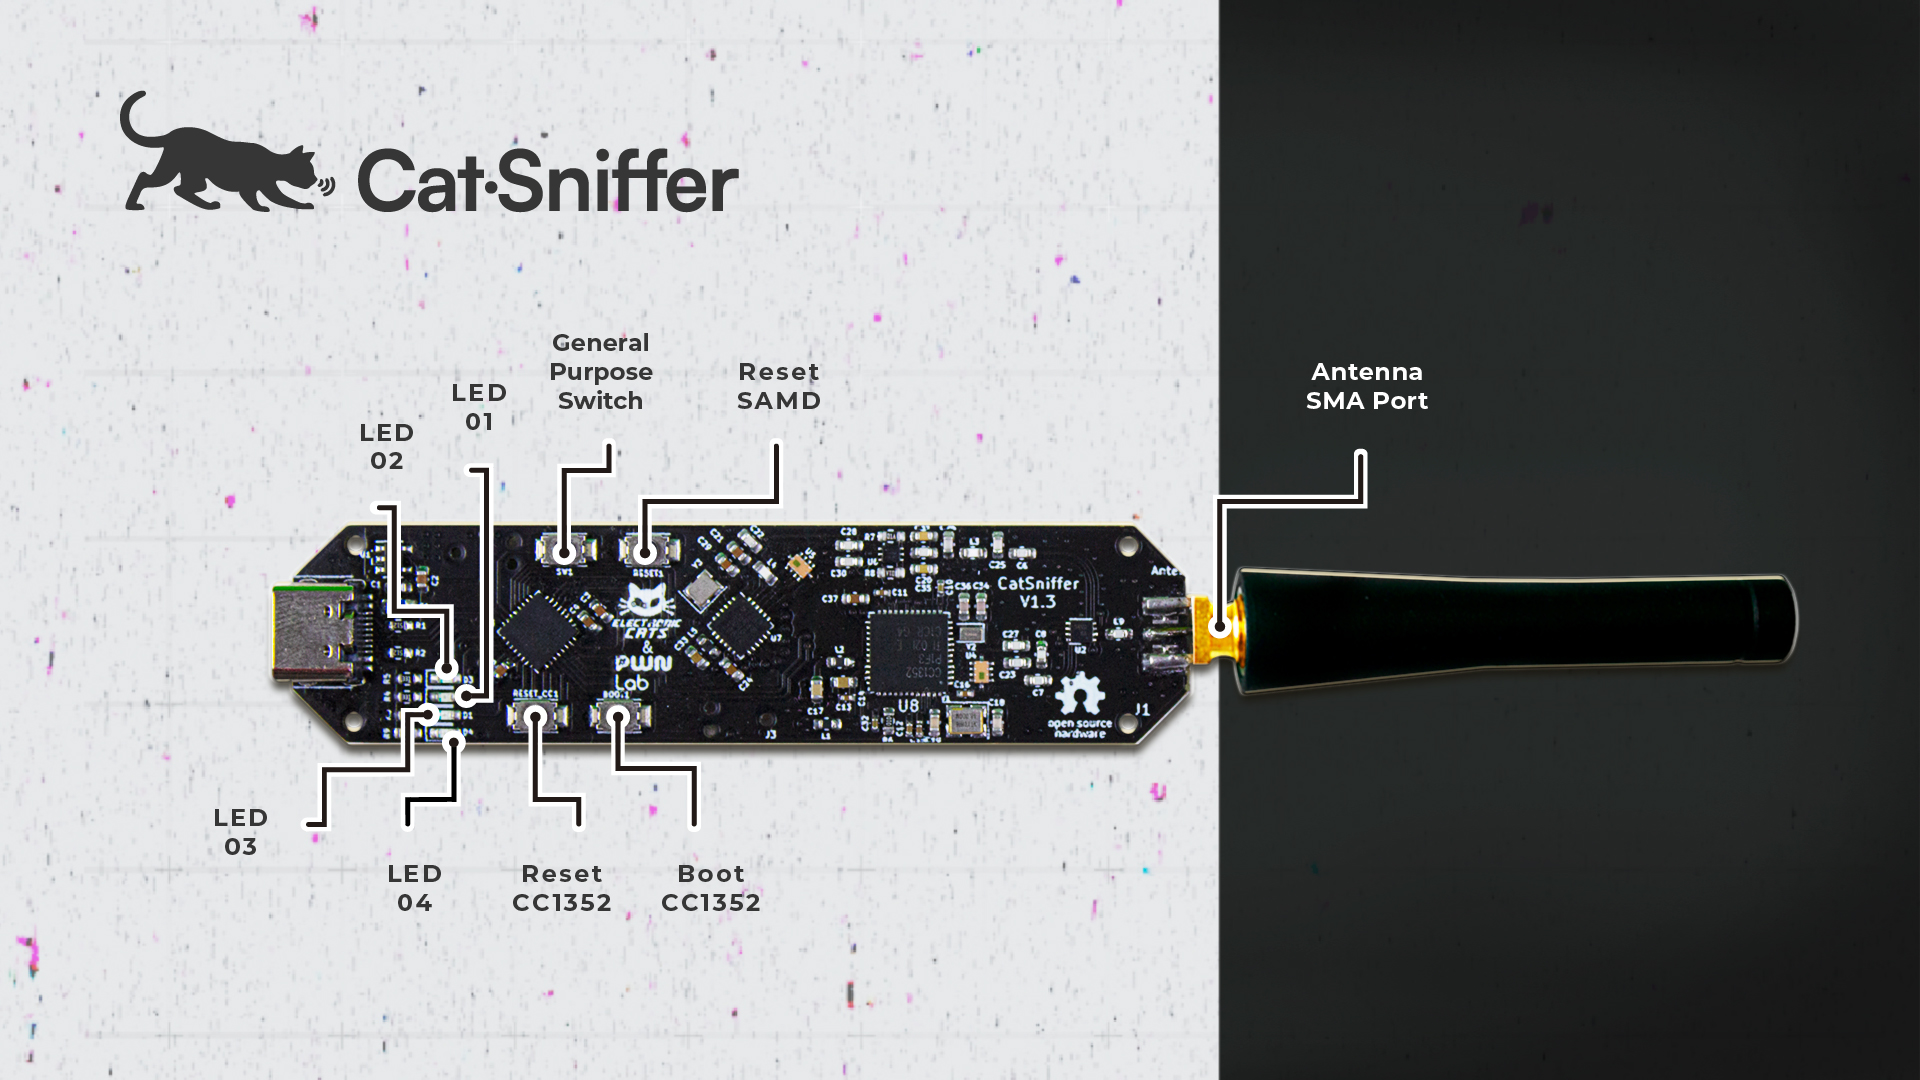 electroniccats/catsniffer
CatSniffer is an original multiprotocol and multiband board for sniffing, communicating, and attacking IoT (Internet of Things) devices using the…
 raminfp/redis_exploit
CVE-2025-49844 (RediShell)
 mbrandner-group/juiceshopgl
Intentionally vulnerable web application for security training, CTF competitions, and testing security tools. Covers OWASP Top Ten vulnerabilities…
 jtmh37/apache-tomcat-cve-2025-24813-lab
ICT279 Vulnerability Detection and Mitigation Project using CVE-2025-24813 in an Internet Banking Environment
 lastvocher/redis-cve-2025-49844
Educational lab environment with a proof-of-concept exploit for CVE-2025-49844 (RediShell), a critical use-after-free in Redis Lua interpreter,…
 rushikesh-a-bhujbal/cve-2010-2075
UnrealIRCd 3.2.8.1 backdoor exploit — reverse shell via AB; trigger, built from scratch in Python using raw sockets. No Metasploit.
 pedrorichil/cve-2025-49844
Educational lab environment demonstrating CVE-2025-49844 (RediShell) in Redis. Includes Docker setup, exploit PoC script, and security…
 l-iberty/cve-2012-1889
Educational exploit demo for CVE-2012-1889 with heap spray technique, providing a practical walkthrough of binary exploitation targeting Internet…