Purple-Team-Automation

Automated adversary emulation (Caldera) against an AD lab to validate Sigma detection coverage and map results to MITRE ATT&CK.

Automated adversary emulation (Caldera) against an AD lab to validate Sigma detection coverage and map results to MITRE ATT&CK.

CVE-2026-109618/109619 — 5 RCE chains + detection rules (Suricata, Sigma, ModSecurity). PHP session.upload_progress pre-auth exploit research.

A comprehensive guide to adversarial testing and security evaluation of AI systems, helping organizations identify vulnerabilities before attackers…

OSINT tool researched and designed to hunt down IG handles

Deliberately vulnerable web application with interactive lessons and challenges for learning web application security and penetration testing…

A complete bug bounty workspace for HackerOne researchers. Includes scope enforcement, automated recon/vuln pipeline (400+ tools), report templates,…

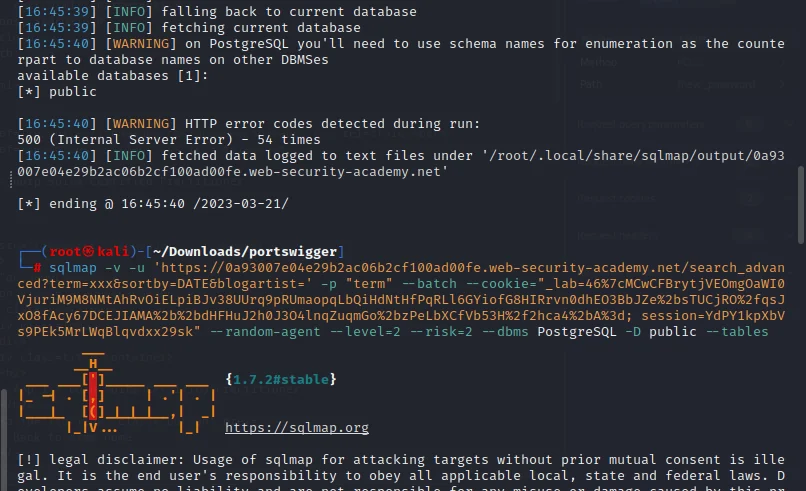
Practical study notes and walkthroughs for PortSwigger Academy labs, covering web vulnerabilities, payloads, enumeration, and BSCP exam strategies.

OSINT & recon toolkit // 100+ tools, one-command installer, SOCMINT, GEOINT, network recon, dark web, forensics & more.

A collection of inspiring lists, manuals, cheatsheets, blogs, hacks, one-liners, cli/web tools and more.

CTF Cheat Sheet + Writeups / Files for some of the Security CTFs that I've done

Curated collection of cybersecurity resources, labs, and training materials covering ethical hacking, penetration testing, exploit development,…

Kali Linux advanced setup

Hello, aspiring hackers! 🕵️♂️ Here’s a list of 500+ Free TryHackMe rooms to kickstart your cybersecurity journey. These rooms are absolutely free,…

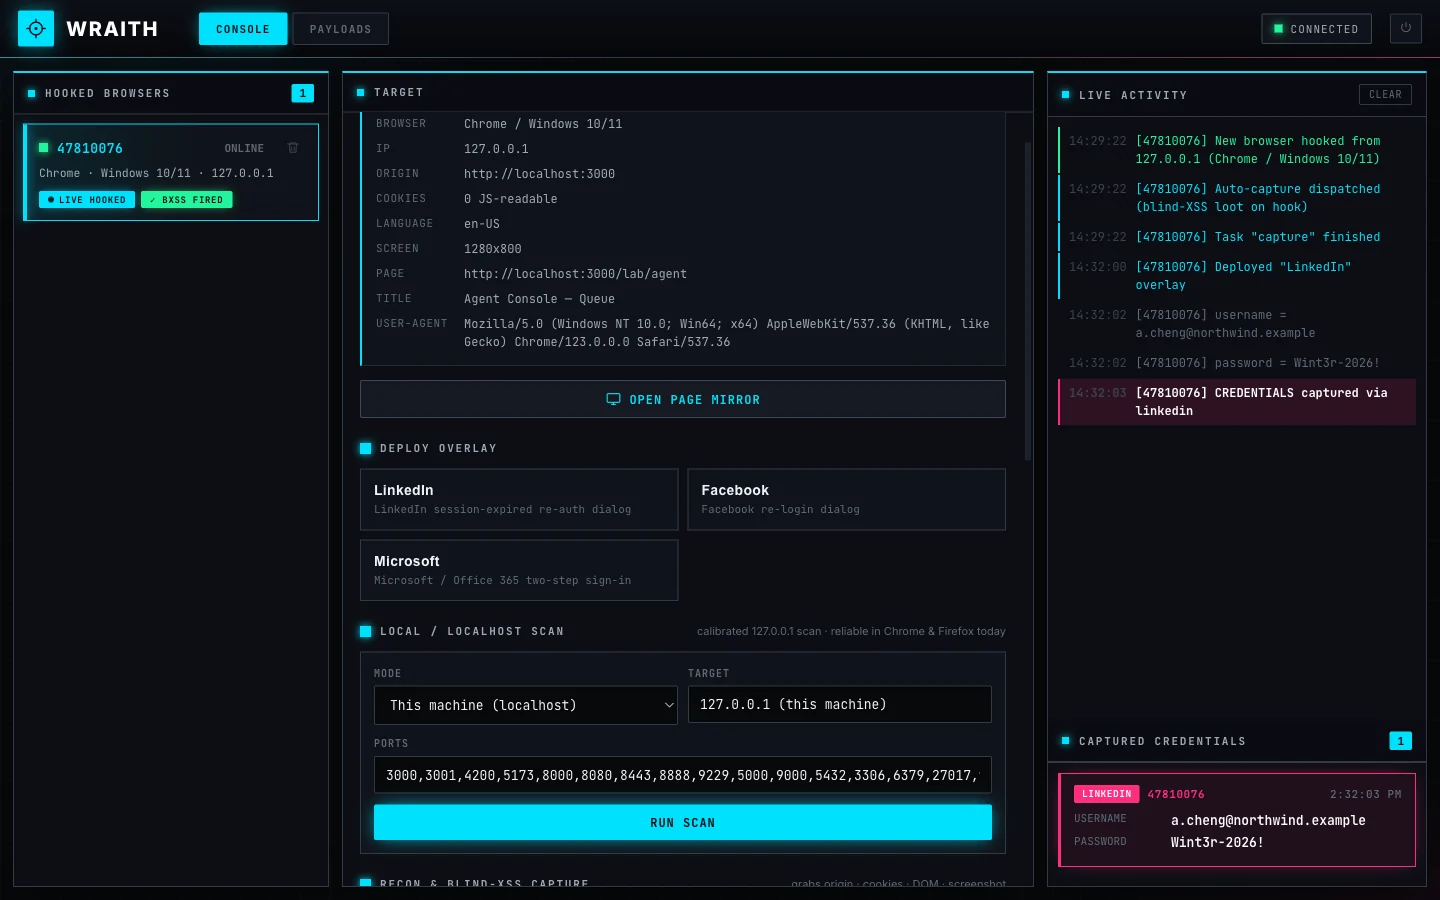
Browser-hooking framework for authorized red teams and educators. Hooks browsers via XSS, provides interactive post-exploitation control, blind-XSS…

🐶 A curated list of Web Security materials and resources.

A curated list of Web3 Security materials and resources for Pentesters and Bug Hunters.

Standalone autonomous AI pentest agent with a plan→act→judge loop, generic skills, destructive-action gate, and swappable LLM providers, plus a…

Self-hosted OWASP CTF kit: one box, one free GitHub org, no cloud dependencies