
SUDO_KILLER
 th3xace/sudo_killer
A tool designed to exploit a privilege escalation vulnerability in the sudo program on Unix-like systems. It takes advantage of a specific…
ctfeducationexploitation+5
2.5k
th3xace/sudo_killerA tool designed to exploit a privilege escalation vulnerability in the sudo program on Unix-like systems. It takes advantage of a specific…
 adfortunato/metasploitable3-pentest-writeup
Home-lab penetration test report of Metasploitable3 covering Nmap recon, Drupalgeddon RCE, SQL injection, SSH credential reuse, sudo privilege…
 shams-ul-mehmood/cve-2021-3156-project
Educational lab environment for CVE-2021-3156 (Baron Samedit) with a Dockerized vulnerable sudo target, exploit scaffold, canary test, root-cause…
 ic3-512/linux-root-kit
End-to-end simulation of a Python dependency confusion attack, sudo privilege escalation (CVE-2025-32463), and rootkit-based persistence - with full…
 kranti08/cve-2021-3156-baron-samedit
Exploitation and mitigation analysis of CVE-2021-3156 heap-based buffer overflow in sudo
 theleopard65/cve-2021-3156-baron-samedit
A simple Docker lab and Exploit setup for CVE-2021-3156 - "Baron Samedit".
 abraxas/cve-2026-96512
Disclosure pack and PoC for CVE-2026-96512, a sudo NOTBEFORE/NOTAFTER TZ time-window bypass enabling local privilege escalation, with lab…
 lemonadern/poc-cve-2019-14287
Docker-based PoC demonstrating CVE-2019-14287 sudo privilege escalation via Runas user restriction bypass, with step-by-step reproduction…
 yonathanpy/cve-2025-32462-cve-2025-32463-poc-lab
Container-based lab with proof-of-concept exploits for two critical sudo vulnerabilities: host validation bypass (CVE-2025-32462) and NSS library…
 ricardomaia/cve-2025-32463
Provides a containerized environment and signed Nuclei template to safely test CVE-2025-32463, a sudo privilege escalation vulnerability, with…
 daryllundy/cve-2025-32463
Detection framework for CVE-2025-32463 sudo privilege escalation vulnerability. Provides real-time monitoring, forensic analysis, and SIEM…
 painoob/cve-2025-32463
Proof-of-concept exploit for CVE-2025-32463, a local privilege escalation vulnerability in sudo allowing chroot jail escape via specific sudoers…
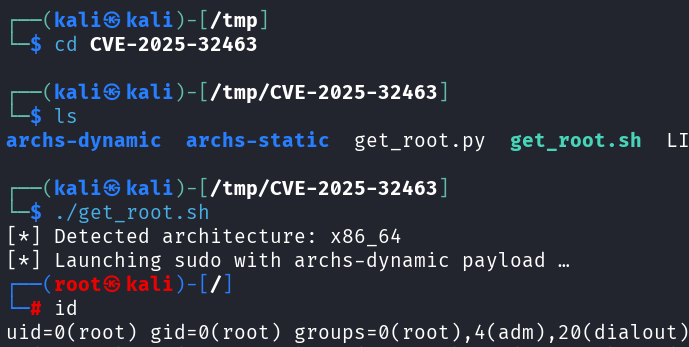 mohamedkarrab/cve-2025-32463
Privilege escalation to root using sudo chroot, NO NEED for gcc installed.
 adityabhatt3010/room-walkthrough-billing
A detailed walkthrough of Billing room exploiting CVE-2023-30258 and escalating via fail2ban misconfig
 chenaotian/cve-2021-3156
CVE-2021-3156 POC and Docker and Analysis write up
 ijbaig/cve-2021-3156
CVE-2021-3156 (Baron Samedit) Report and Research
 cybersentinelx1/cve-2025-32462-exploit
PoC exploit for CVE-2025-32462, a sudo privilege escalation via hostname spoofing. Demonstrates bypassing hostname-based restrictions to gain root…
 cves-labs/cve-2026-21877
Dockerized vulnerable lab environment with a Python-based network monitor and dedicated exploit script, enabling hands-on exploitation, privilege…