
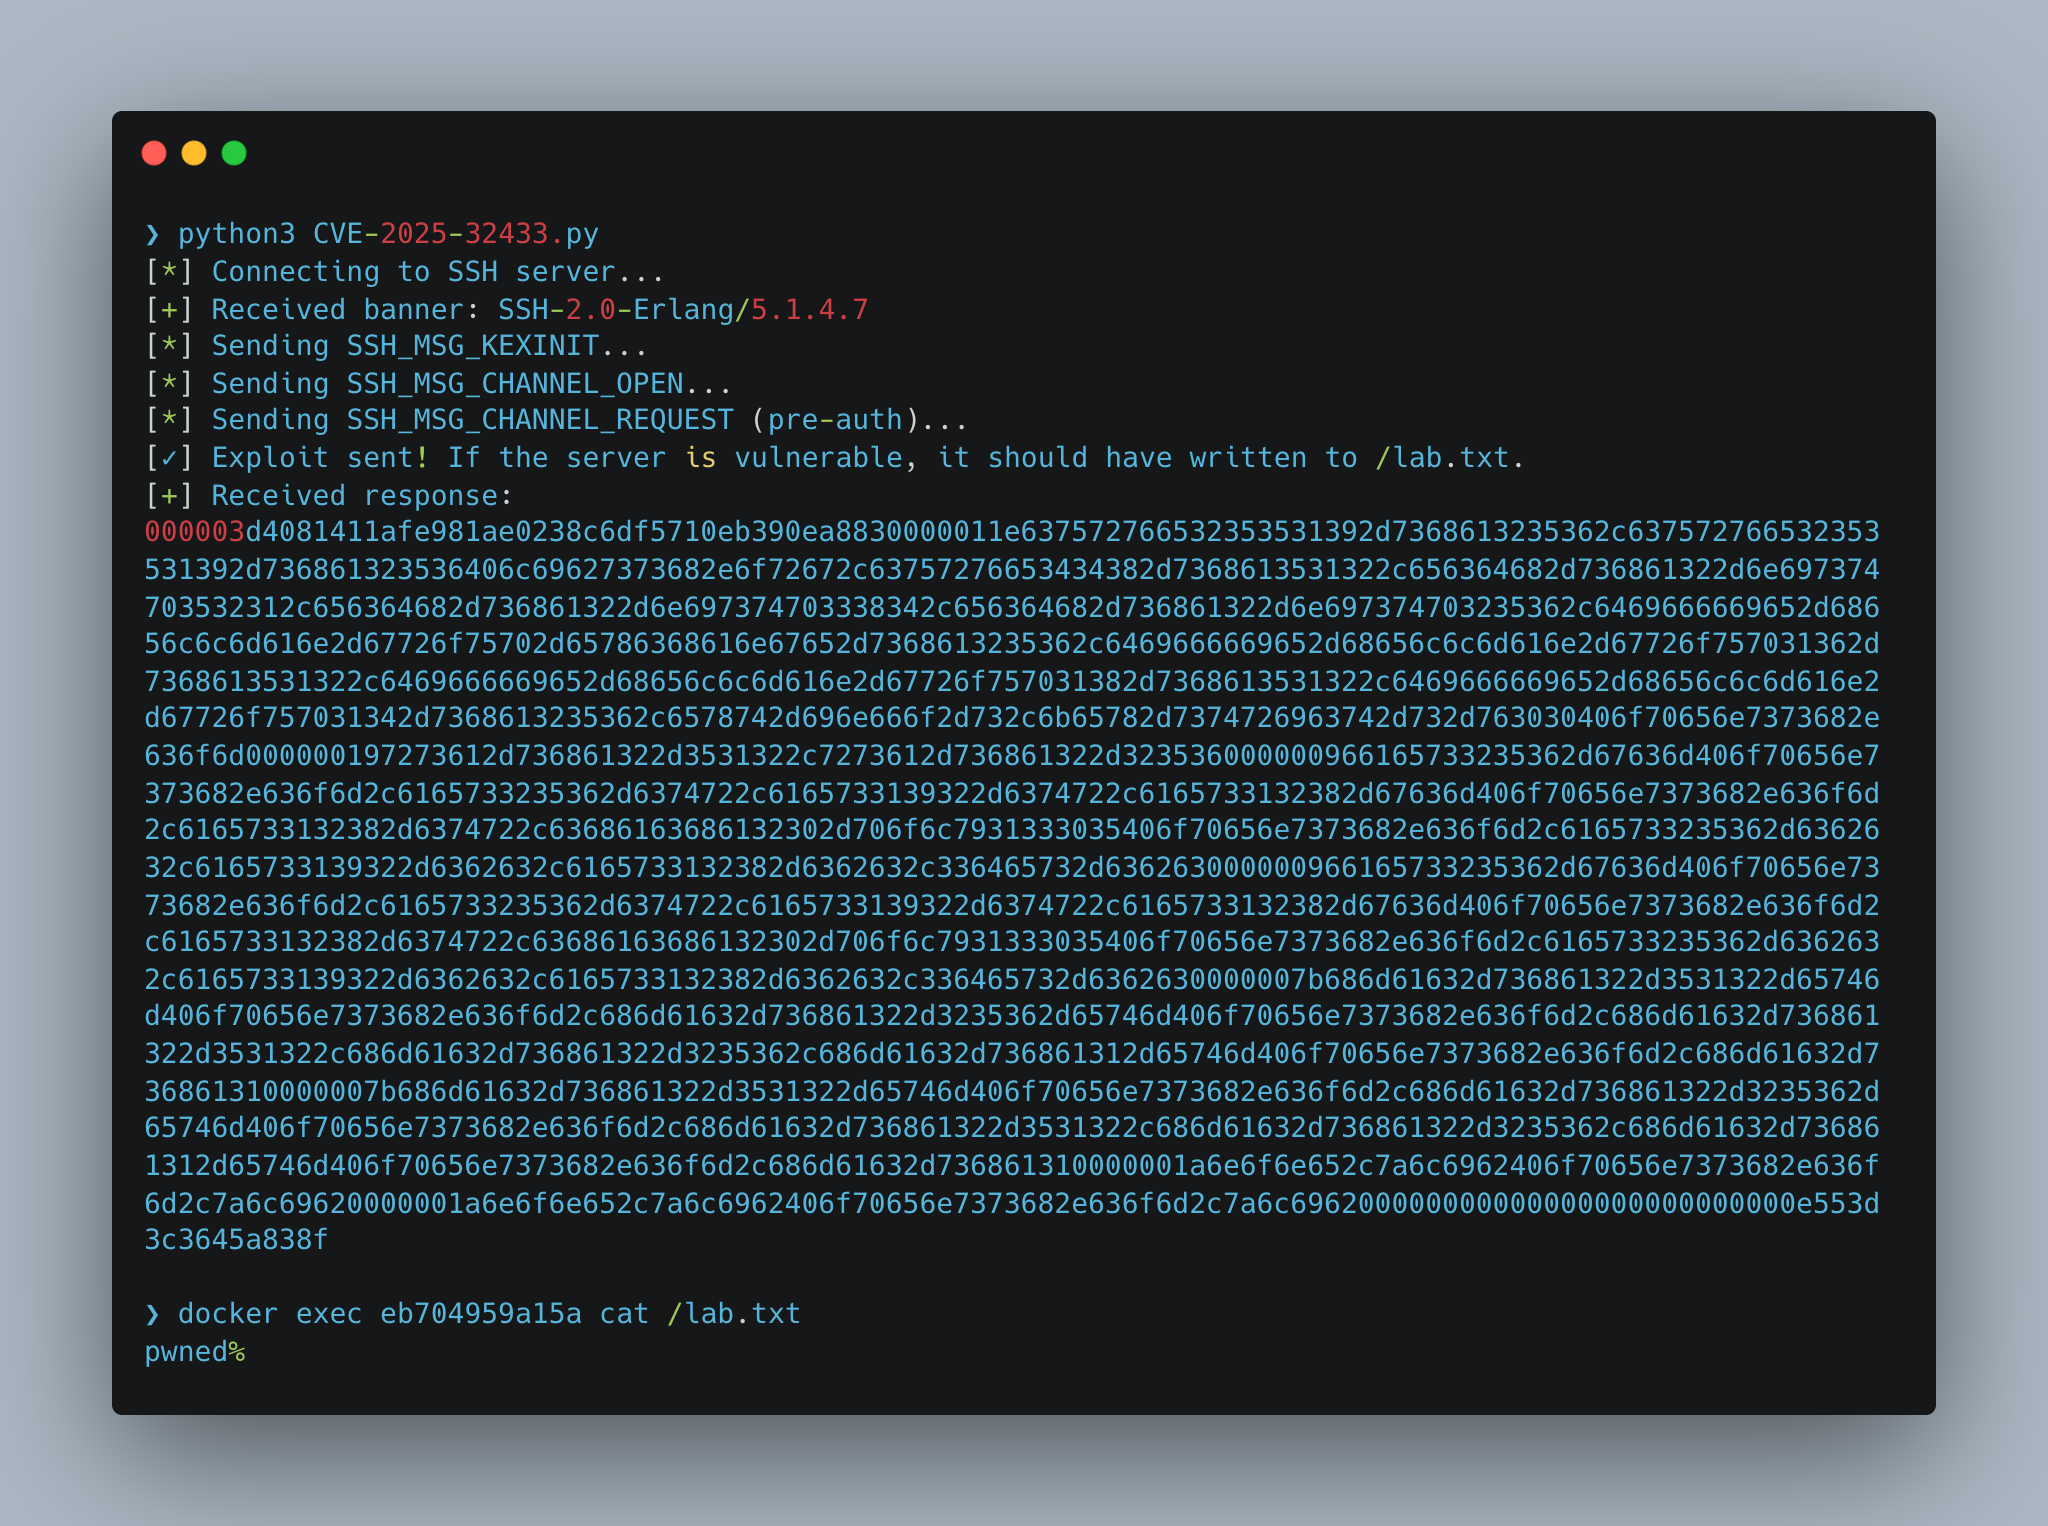
CVE-2025-32433.py
 yonathanpy/cve-2025-32433.py
CVE-2025-32433 PoC – SSH Protocol Python-based PoC for controlled lab testing of SSH message handling, channel operations, and pre-auth interactions.…
educationexploitationlabs-practice+3
3
yonathanpy/cve-2025-32433.pyCVE-2025-32433 PoC – SSH Protocol Python-based PoC for controlled lab testing of SSH message handling, channel operations, and pre-auth interactions.…
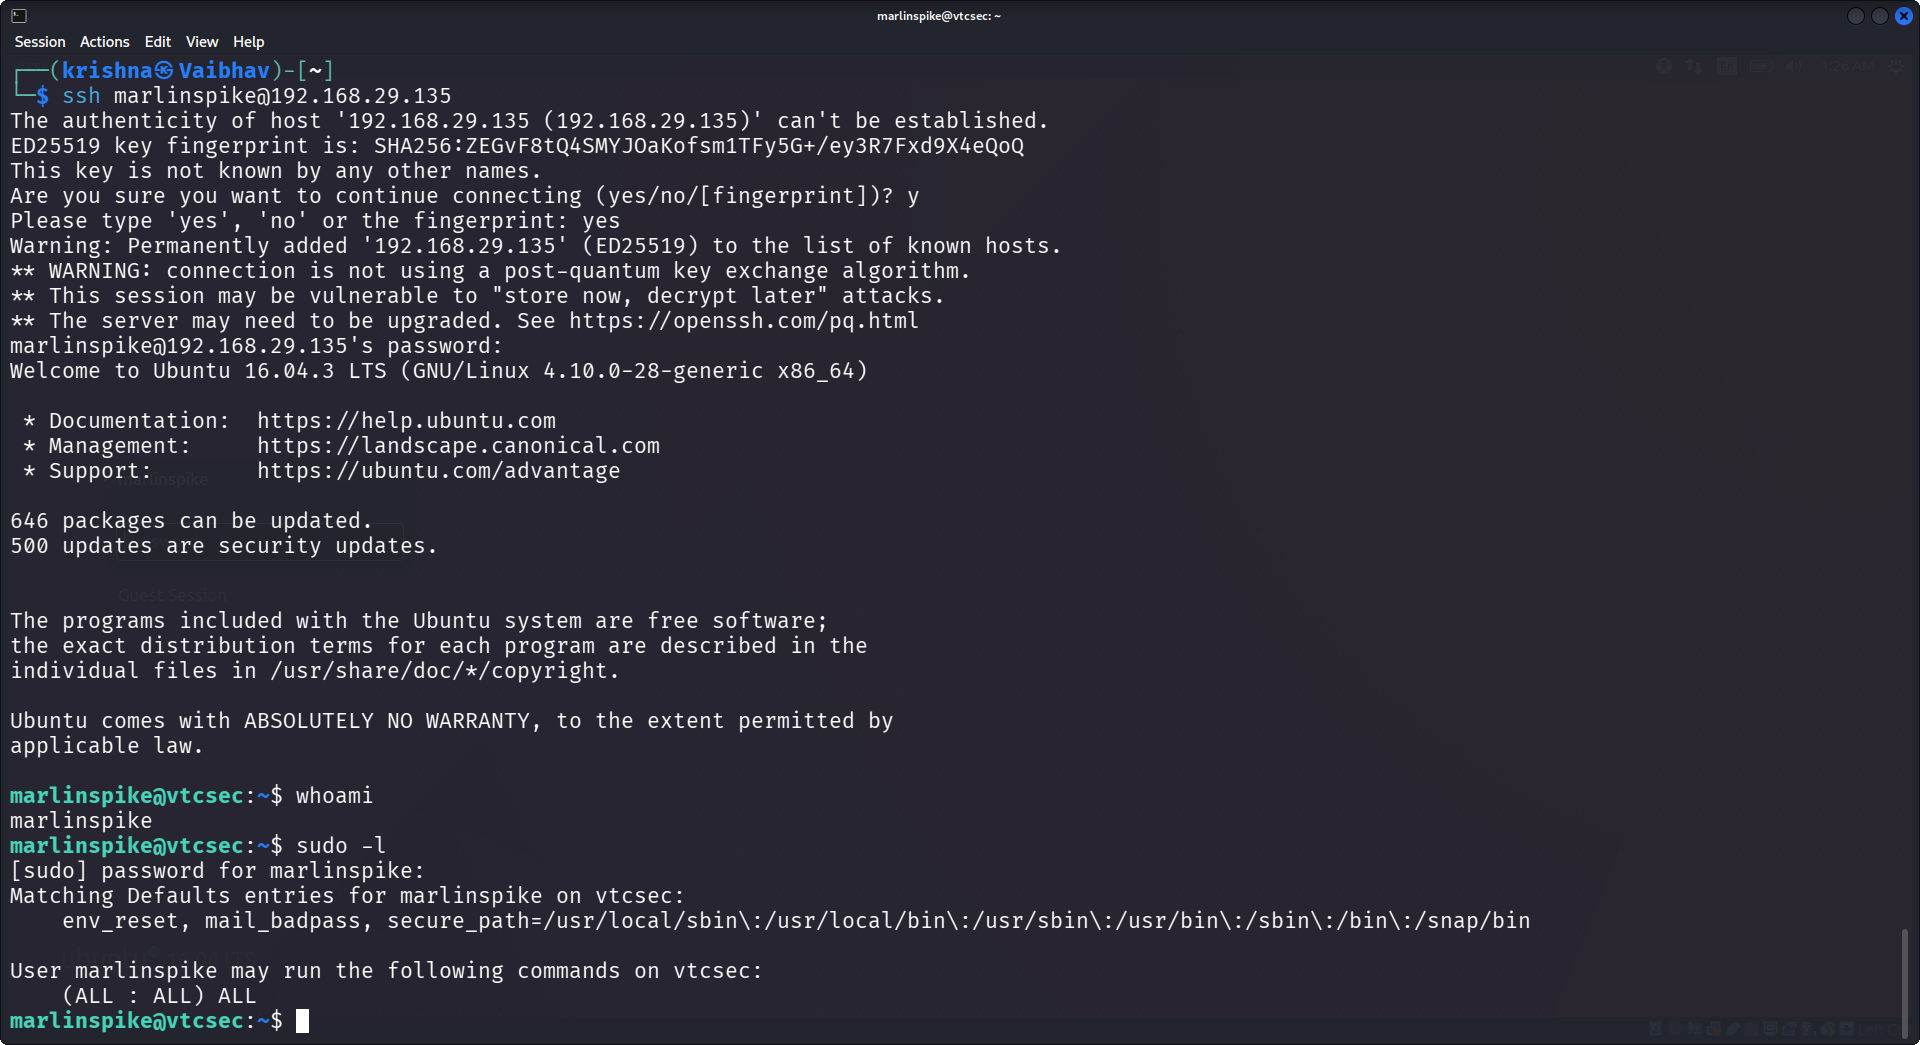 vaibhavkrishna12004/ubuntu-privesc-lab
Full penetration testing workflow: credential brute force, SSH access and privilege escalation (CVE-2021-4034)
 liam-worsley/cve-2025-32433-poc-analysis
This is an analysis for CVE-2025-32433 (Erlang OTP SSH Vulnerability). I did not write any of the code, I only wrote comments describing what the…
 go-lanz/persistnux
Bash-based Linux persistence detection tool for DFIR investigations. Scans 15+ persistence mechanisms (systemd, cron, kernel modules, SSH,…
 dampedcoast/exploiting-a-vulnerability-using-reverse-shell
This project simulates a real-world attack-and-defend scenario across two virtual machines. You will exploit a critical pre-authentication RCE…
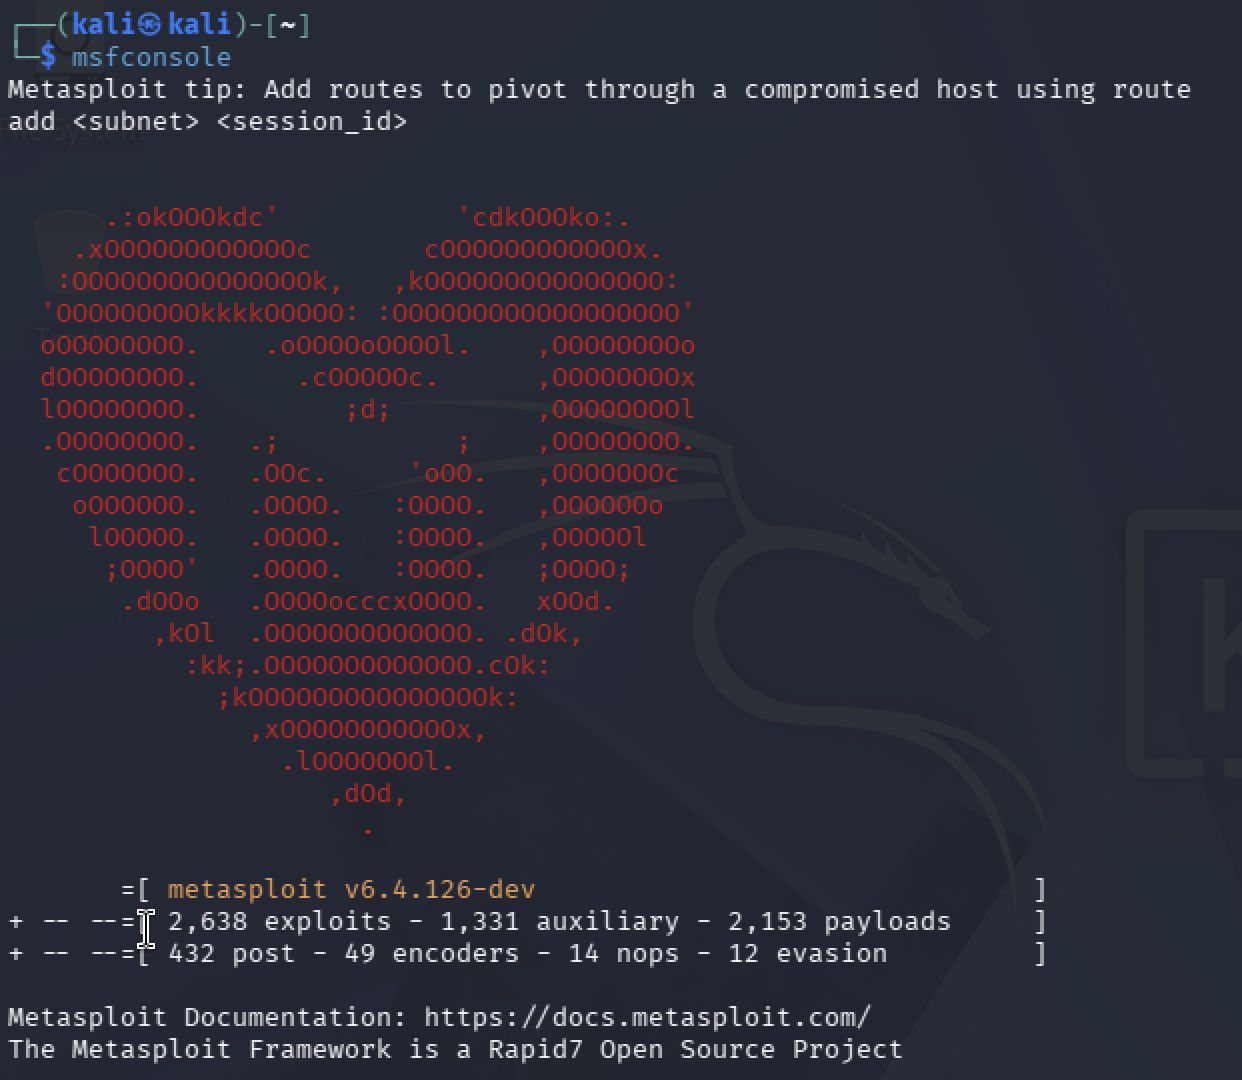 mboatella25/metasploitable-pentest-lab
Pentest completo sobre Metasploitable: recon con nmap, explotación con Metasploit (CVE-2007-2447), extracción y cracking de credenciales,…
 v0idw1re/htb-pterodactyl-writeup
HackTheBox — Pterodactyl (Medium/Linux) walkthrough. CVE-2025-49132 LFI → pearcmd RCE → bcrypt crack → SSH. Privesc via CVE-2025-6018 (PAM…
 zakariamaaraki/dirty-cow-cve-2016-5195-
Exploit the dirtycow vulnerability to login as root
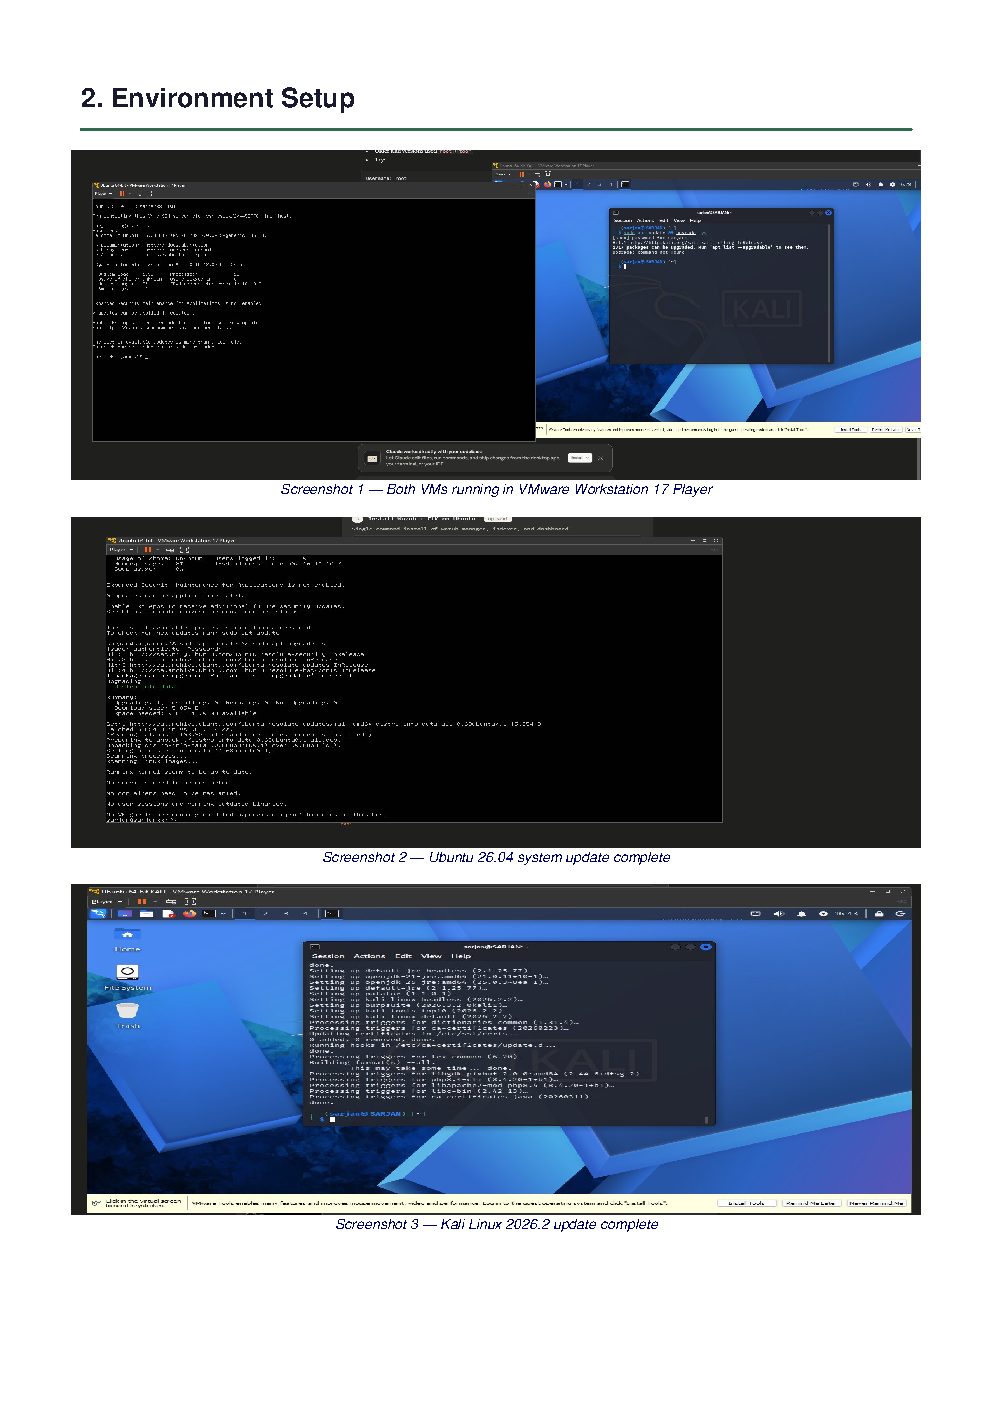 sarjanpatel22/siem-threat-detection-lab
Blue-team SIEM lab: Wazuh 4.7.5 detecting 7 simulated attacks (SSH brute force, Slowloris DoS / CVE-2007-6750, web attacks) with real-time MITRE…
 ayham-megdadi/zero-day-legacy
A vulnerable Boot-to-Root CTF lab machine simulating a hospital environment. Features a realistic 17-step attack chain including SQL Injection, XSS,…
 adfortunato/metasploitable3-pentest-writeup
Home-lab penetration test report of Metasploitable3 covering Nmap recon, Drupalgeddon RCE, SQL injection, SSH credential reuse, sudo privilege…
 anonymking/cve-2017-1000117
CVE-2017-1000117漏洞复现(PoC+Exp)
 pallangyo98/trickster-htb
This report details exploiting Trickster via an XSS in PrestaShop (CVE-2024-34716) to gain www-data access, extracting database credentials for SSH…
 jerry-zhuang/cve-2017-1000117
Proof-of-concept exploit for CVE-2017-1000117 (Git clone command injection) targeting SSH, designed for vulnerability testing and educational lab…
 kikechans/-ssh-enum-cve-2018-15473
🛡️ SSH User Enumeration (CVE-2018-15473). Python 3, multihilo y calibración anti-falsos positivos. 🧵
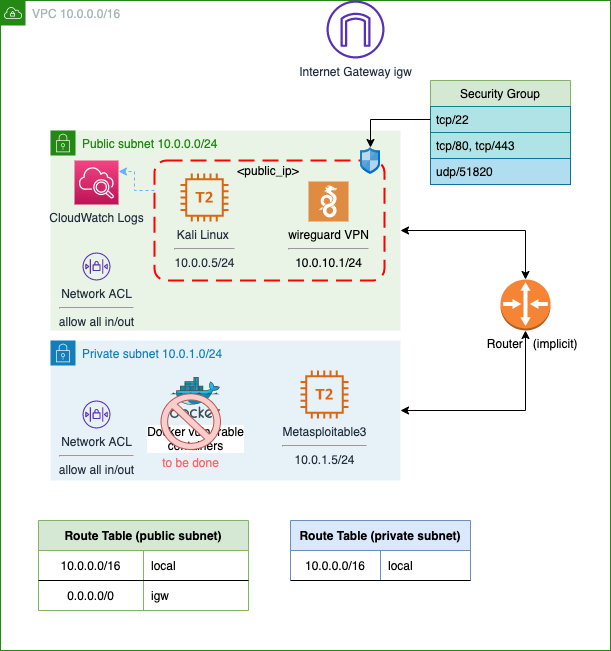 juanjosanz/aws-pentesting-lab
Pentesting lab with a Kali Linux instance accessible via ssh & wireguard VPN and with vulnerable instances in a private subnet
 mauricelambert/labautomationcve-2021-43798
This script implements a lab automation where I exploit CVE-2021-43798 to steal user secrets and then gain privileges on a Linux system.