
EXPLOIT-CVE-2026-42559
 joaovicdev/exploit-cve-2026-42559
Docker lab + Python PoC for CVE-2026-42559 - DNS rebinding via unvalidated Host header in the rmcp (Rust MCP SDK) Streamable HTTP server transport
educationexploitationlabs-practice+2
joaovicdev/exploit-cve-2026-42559Docker lab + Python PoC for CVE-2026-42559 - DNS rebinding via unvalidated Host header in the rmcp (Rust MCP SDK) Streamable HTTP server transport
 sischkg/cve-2018-5740
Proof-of-concept exploit for CVE-2018-5740, a denial-of-service vulnerability in BIND DNS server triggered by a crafted DNAME query, with…
 dicanio/cve-2021-44228-docker-example
Docker-based demonstration of CVE-2021-44228 (Log4Shell) exploitation, featuring a vulnerable Java server, malicious LDAP server, and data…
 june-in-exile/cve-2021-26700
Educational RCE exploit for CVE-2021-26700 in VS Code npm extension, demonstrating DNS tunneling to a Caldera C2 server via malicious package.json…
 abraxas/cve-2026-15583
Proof-of-concept client and Docker lab reproducing CVE-2026-15583, an unauthenticated confused-deputy SSRF in Grafana MCP Server that leaks…
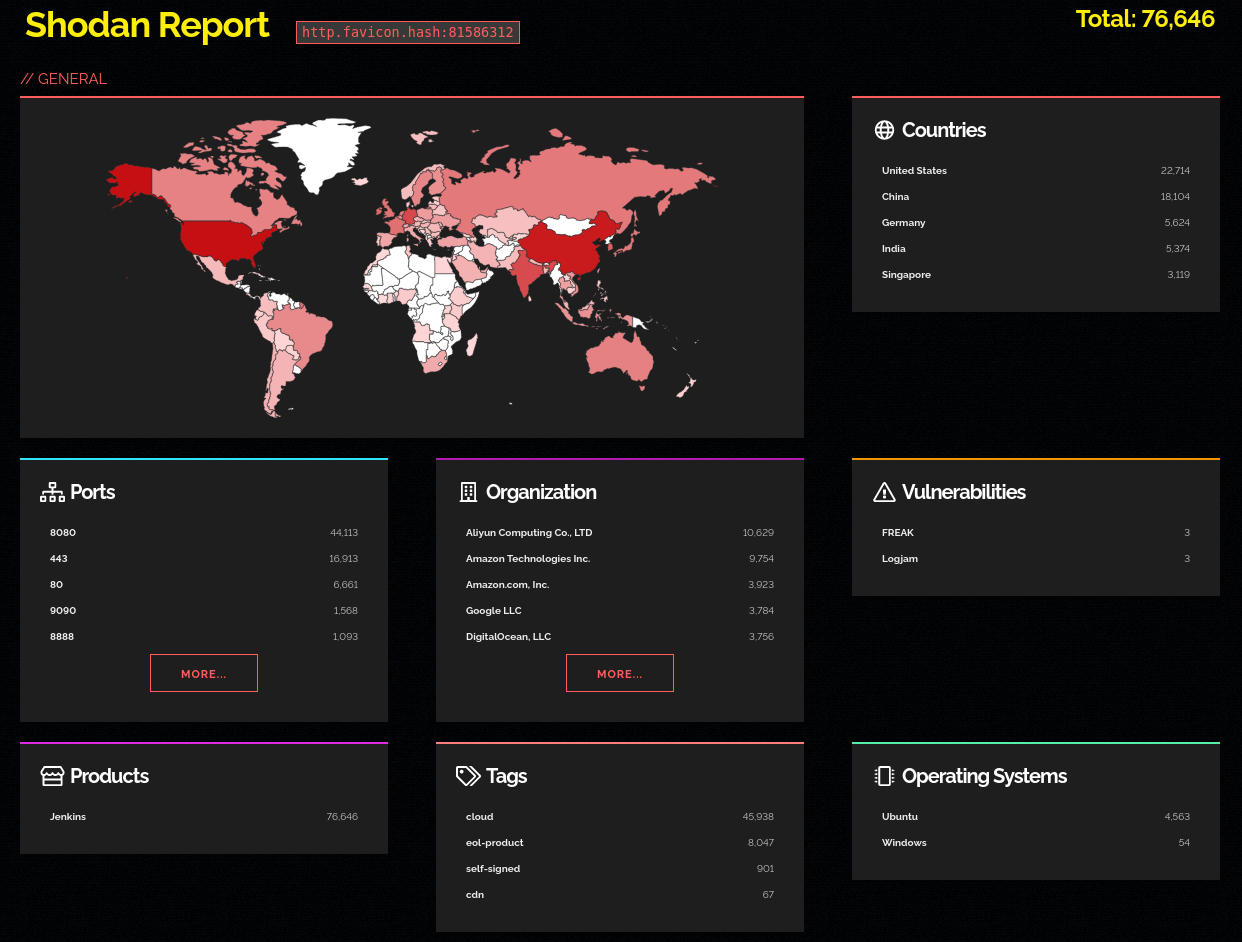 yoryio/cve-2024-23897
Scanner for CVE-2024-23897 - Jenkins
 abraxas/mysql-mysqldump-tab-path
MySQL Community Server 26.7.0 - High - mysqldump --tab path leftover - client file write
 abraxas/jellyfin-svg-gzip
Jellyfin Server 12.2 - High - Remote - SSRF - gzip data:image/png leftover of GHSA-cf3c still fetches http and file
 abraxas/jellyfin-playlist-itemids
Jellyfin Server 12.2 - High - Remote - IDOR - public playlist ItemIds leftover of GHSA-9x85 then unauth stream
 abraxas/jellyfin-suggestions-idor
Jellyfin Server 12.2 - High - Remote - IDOR - GET /Items/Suggestions omit-userId dumps hidden library Path and IDs
 abraxas/openmeetings-wb-fileid-idor
Apache OpenMeetings 9.1.0 - High - Remote - IDOR - WHITEBOARD fileId plant then room file resource serves bytes
 abraxas/ats-jsonrpc-unrestricted
Apache Traffic Server 10.2.0 - High - Local - Privilege leftover - JSON-RPC unix socket unrestricted mode 0777
 abraxas/ats-magick-unsigned
Apache Traffic Server 10.2.0 - High - Remote - File write - unsigned magick convert writes as nobody