
metarget
 metarget/metarget
Metarget is a framework providing automatic constructions of vulnerable infrastructures.
cloud-securitycontainer-securityeducation+4
1.4k
metarget/metargetMetarget is a framework providing automatic constructions of vulnerable infrastructures.
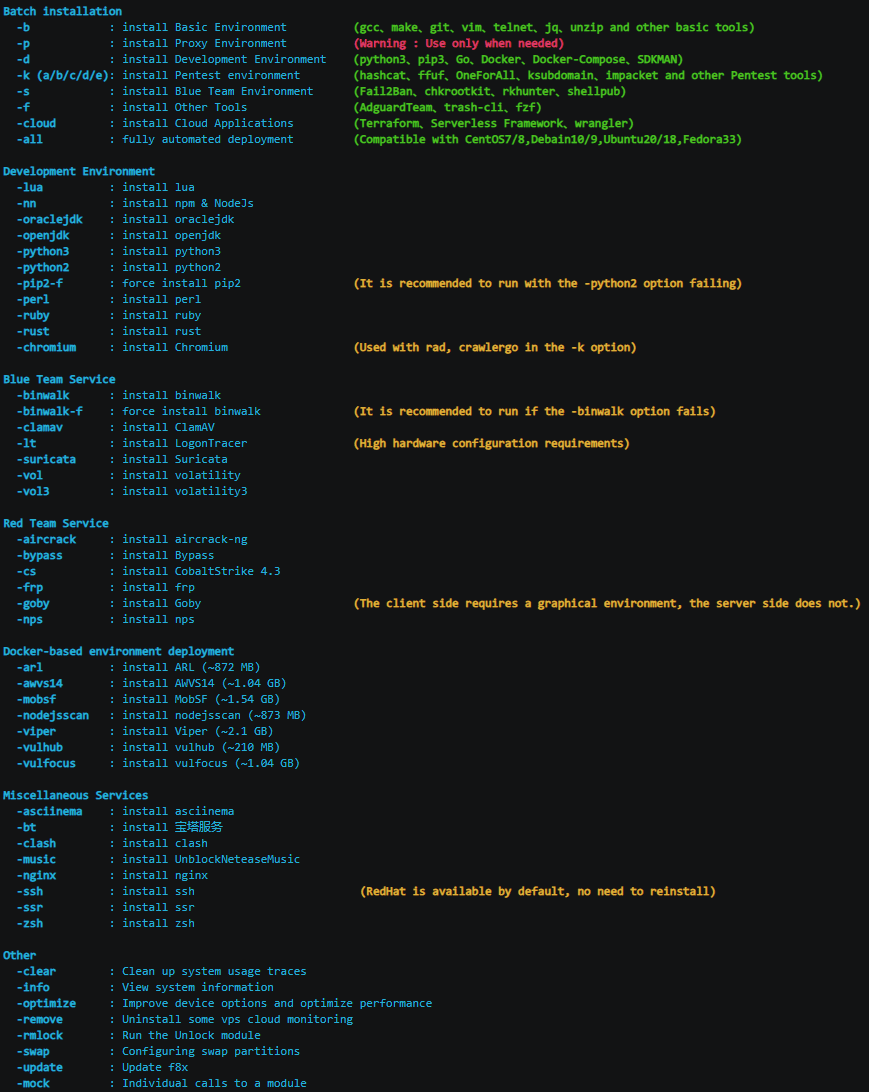 ffffffff0x/f8x
红/蓝队环境自动化部署工具 | Red/Blue team environment automation deployment tool
 xxdndxx/ctf-tracker
Offline-first dashboard for tracking CTF machines and labs, with attack lifecycle management, dynamic reverse shell builder, and embedded writeup…
 wattocyber/oscp-notes-2026
OSCP notes vault + exam cockpit dashboard: merged technique notes, variable-filled command decks, machines, creds, and runbook for exam day. MIT.
 daniyal48/ghostlock-vagrant-box
An isolated Vagrant testbed designed to simulate a complete attack chain: Initial access via the Nginx heap buffer overflow (CVE-2026-42533) followed…
 bishopfox/iam-vulnerable
Use Terraform to create your own vulnerable by design AWS IAM privilege escalation playground.
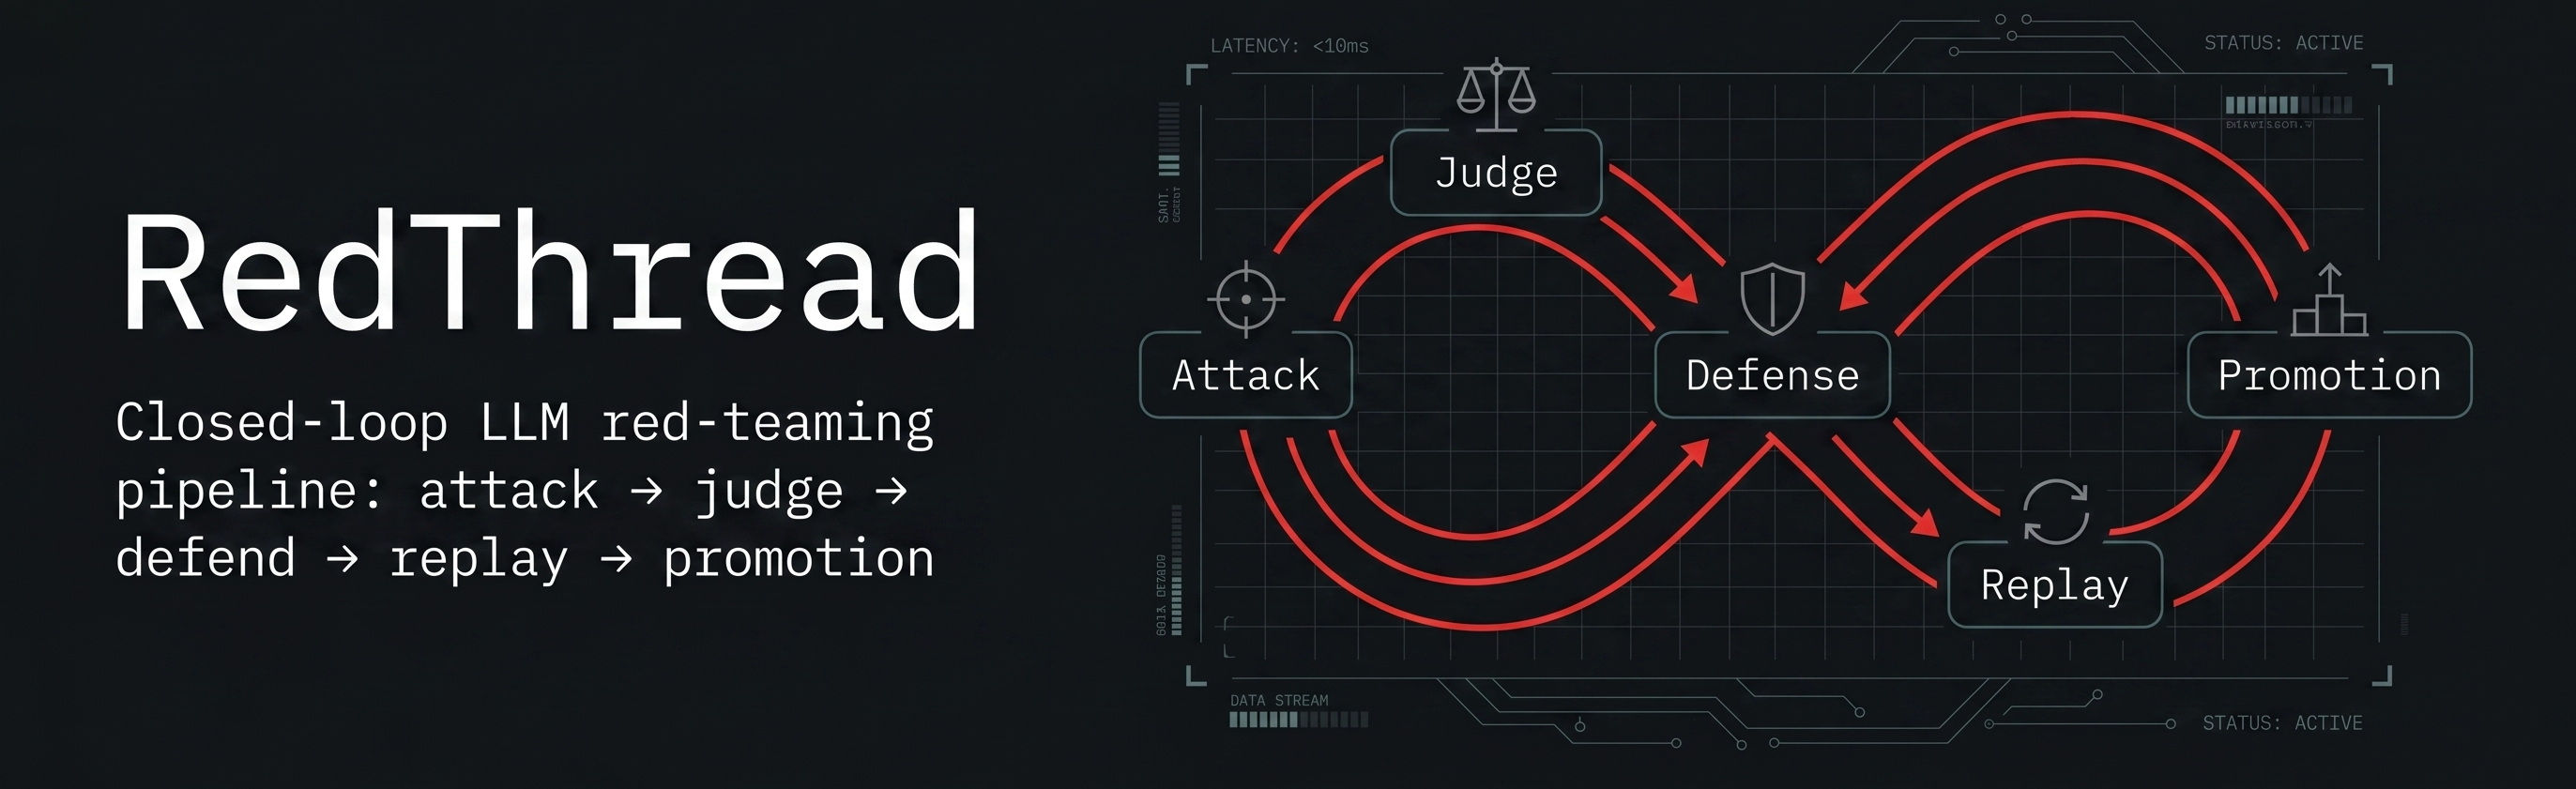 matheusht/redthread
An autonomous red-teaming engine for LLMs. RedThread manages the full security lifecycle: generating adversarial attacks, executing precision…
 chenaotian/cve-2022-0847
Proof-of-concept exploit and detailed analysis of CVE-2022-0847 (Dirty Pipe) Linux kernel privilege escalation vulnerability, including Docker…
 zer0sumgam3/cve-2026-66066-poc
PoC for CVE-2026-66066 in Ruby on Rails
 theporgs/exegol
Fully featured and community-driven hacking environment
 alihzsec/cve-2024-28000
Hands-on exploit lab for CVE-2024-28000 — unauthenticated privilege escalation in LiteSpeed Cache (WordPress plugin, <=6.3.0.1). Spins up a…
 th3xace/sudo_killer
A tool designed to exploit a privilege escalation vulnerability in the sudo program on Unix-like systems. It takes advantage of a specific…
 nccgroup/vulnerabledotnethttpremoting
Example Vulnerable .NET HTTP Remoting
 nweks/bluekeep-metasploit-lab-project
Exploiting Bluekeep (CVE-2019-0708) on windows 7 using metasploit (Esucational lab)
 maldev-academy/dumpbrowsersecrets
Extracts browser-stored data such as refresh tokens, cookies, saved credentials, credit cards, autofill entries, browsing history, and bookmarks from…
 pithase/asm-copyfail
CVE-2026-31431 (Copy Fail) — Análisis y desarrollo en Ensamblador x86-64 | Analysis and development in x86-64 Assembly
 shivam-bathla/cve-2026-24061-setup
Docker setup for CVE-2026-24061
 rayferrufino/make-and-break
Built a custom Virtual Machine, running Ubuntu 18.04.1 and Webmin 1.810. Using CVE-2019-15107 to exploit a backdoor in the Linux machine