
CTFs
 adamkadaban/ctfs
CTF Cheat Sheet + Writeups / Files for some of the Security CTFs that I've done
binary-exploitationcryptographyctf+9
adamkadaban/ctfsCTF Cheat Sheet + Writeups / Files for some of the Security CTFs that I've done
 rufflabs/ludus_crushftp_cve-2025-31161_sim
Ansible role that simulates a realistic CrushFTP CVE-2025-31161 exploitation scenario with rotating sensitive data files and automated defender…
 frankwxu/digital-forensics-lab
Free hands-on digital forensics labs for students and faculty
 binarygolf/bggp
Annual small file competition repository with binary golf challenges across themes like polyglots, crashes, self-replication, and downloads,…
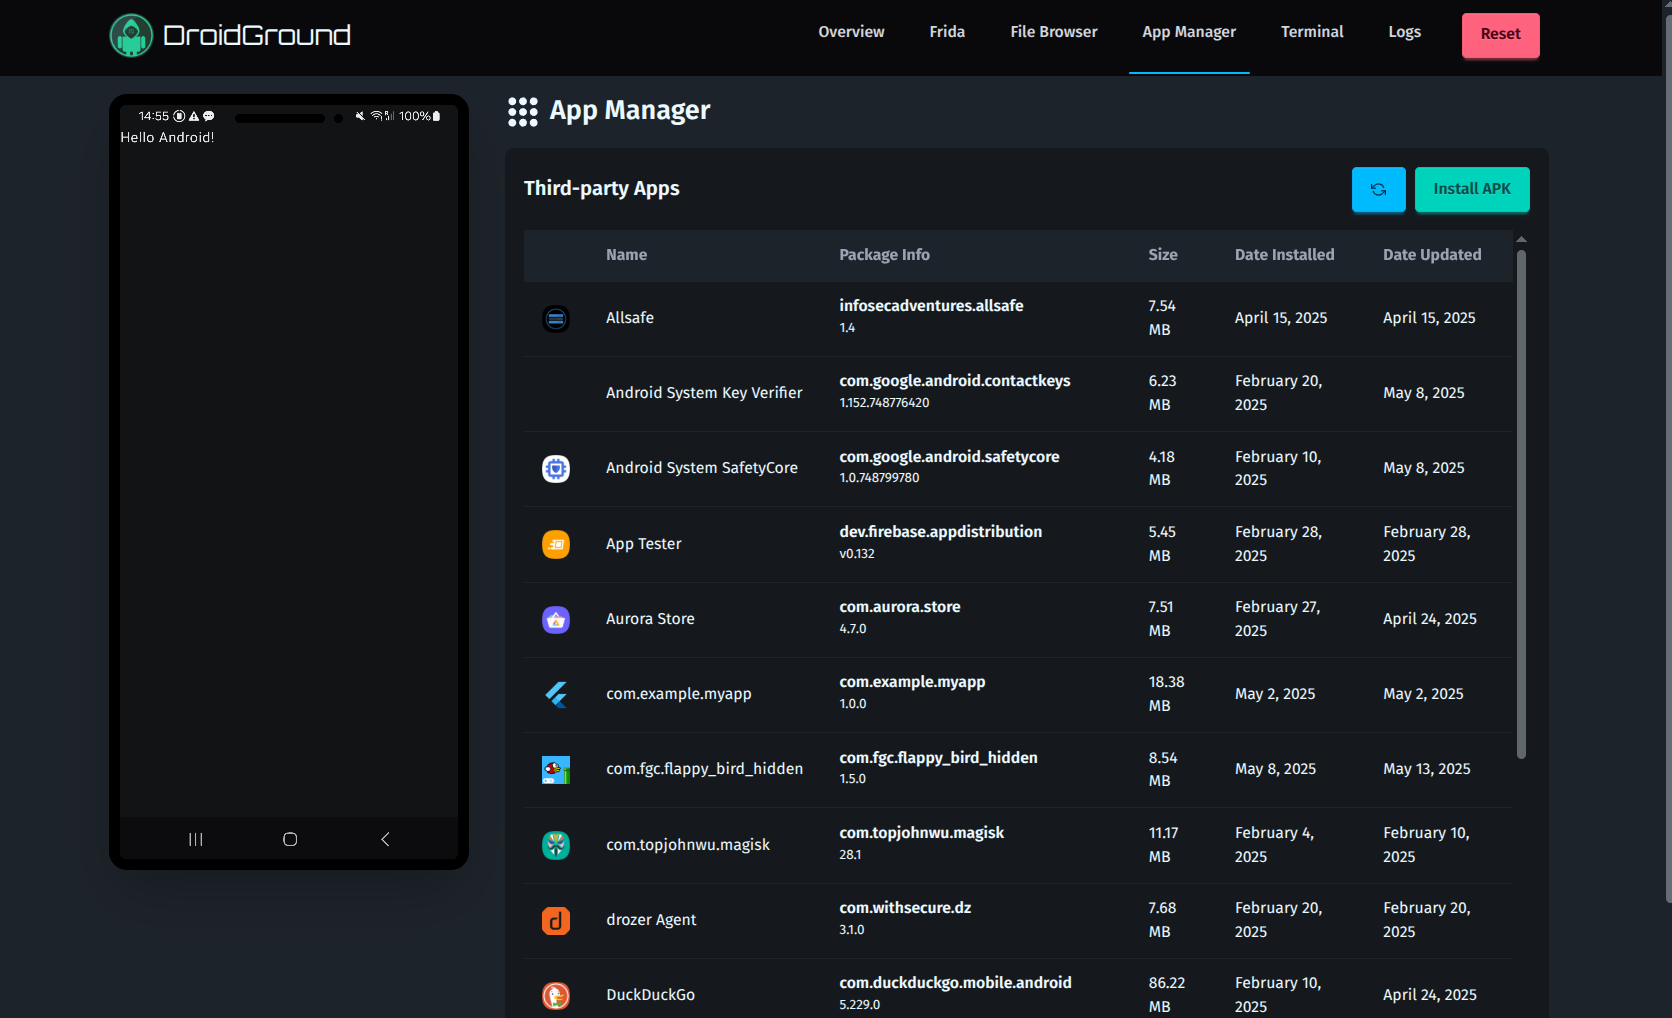 secforce/droidground
A flexible playground for Android CTF challenges.
 solivaquaant/cve-2026-85706
Proof-of-concept and reproduction lab for CVE-2026-85706, an unauthenticated path-traversal file read in GitLab CE/EE repository commits and files…
 mattijsmoens/intentshield
Pre-execution intent verification for AI agents. Audits what your AI is about to do, not what it says. Zero dependencies, deterministic, hash-sealed.

 cyberharsh/shellbash-cve-2014-6271
Docker-based lab environment for exploiting Shellshock (CVE-2014-6271) via CGI scripts, demonstrating remote command injection through crafted HTTP…
 jstrosch/malware-samples
Malware samples, analysis exercises and other interesting resources.
 d3vzer0/reternal-quickstart
Repo containing docker-compose files and setup scripts without having to clone the individual reternal components
 owasp/vulnerable-container-hub
VULCONHUB provides access to files to build your own hands-on vulnerable container image to learn and practice security
 nu11secur1ty/vulnerable-pdf
Educational PDF files demonstrating client-side exploitation techniques, including calculator execution and directory browsing, for security testing…
 mo200909/office-malware-forensics-lab-remnux-static-analysis
Static analysis of 2 malicious Office documents on REMnux using oletools; identified CVE-2017-11882 and obfuscated macros.
 zjuicsr/deeptrap
Security benchmark for evaluating OpenClaw agents against adversarial execution contexts including poisoned files, injected skills, misleading tool…