
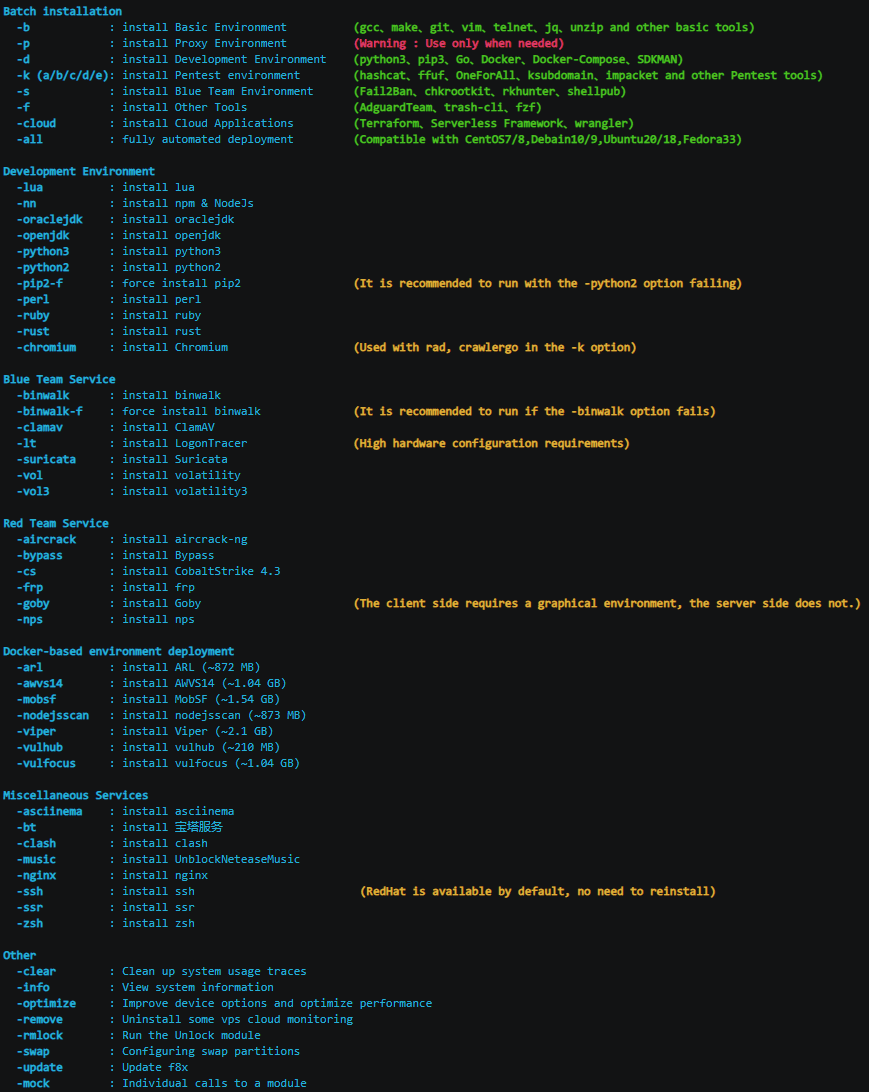
f8x
 ffffffff0x/f8x
红/蓝队环境自动化部署工具 | Red/Blue team environment automation deployment tool
cloud-securityctfdevsecops+7
ffffffff0x/f8x红/蓝队环境自动化部署工具 | Red/Blue team environment automation deployment tool
 hekadan/cve-2019-7609
Docker-based lab environment and exploit for CVE-2019-7609 (Kibana Timelion RCE) with reverse shell payload and patch analysis.
 ahmetramazank/cve-2024-4577
Demonstrates exploitation of CVE-2024-4577, a PHP CGI RCE on Windows, including attack steps, reverse shell deployment, and ransomware simulation…
 eurogig/jankybank
Simple Java Front and Back end with bad log4j version featuring CVE-2021-44228
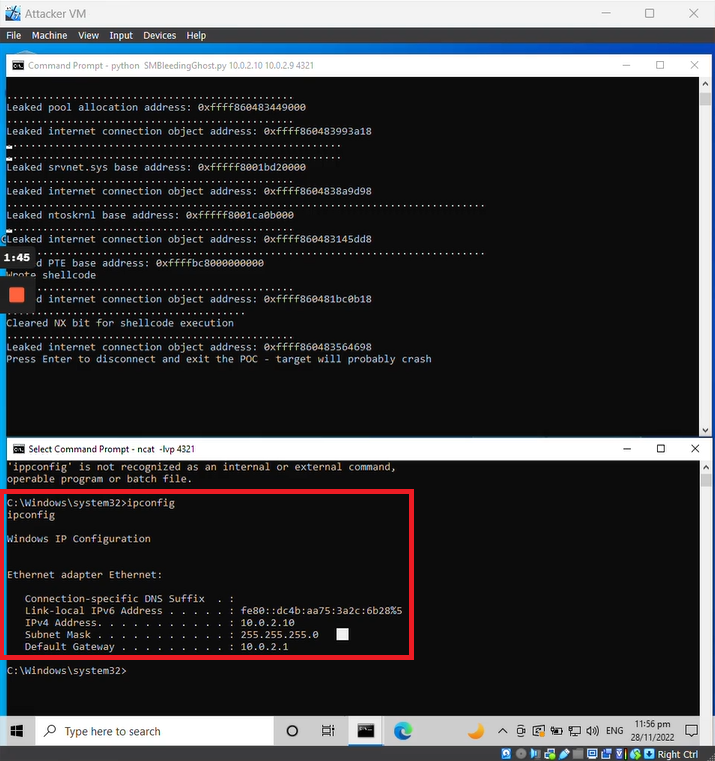 tdevworks/cve-2020-0796-smbghost-exploit-demo
Educational proof-of-concept exploit for CVE-2020-0796 (SMBGhost) demonstrating pre-auth RCE on Windows SMBv3. Includes step-by-step lab setup,…
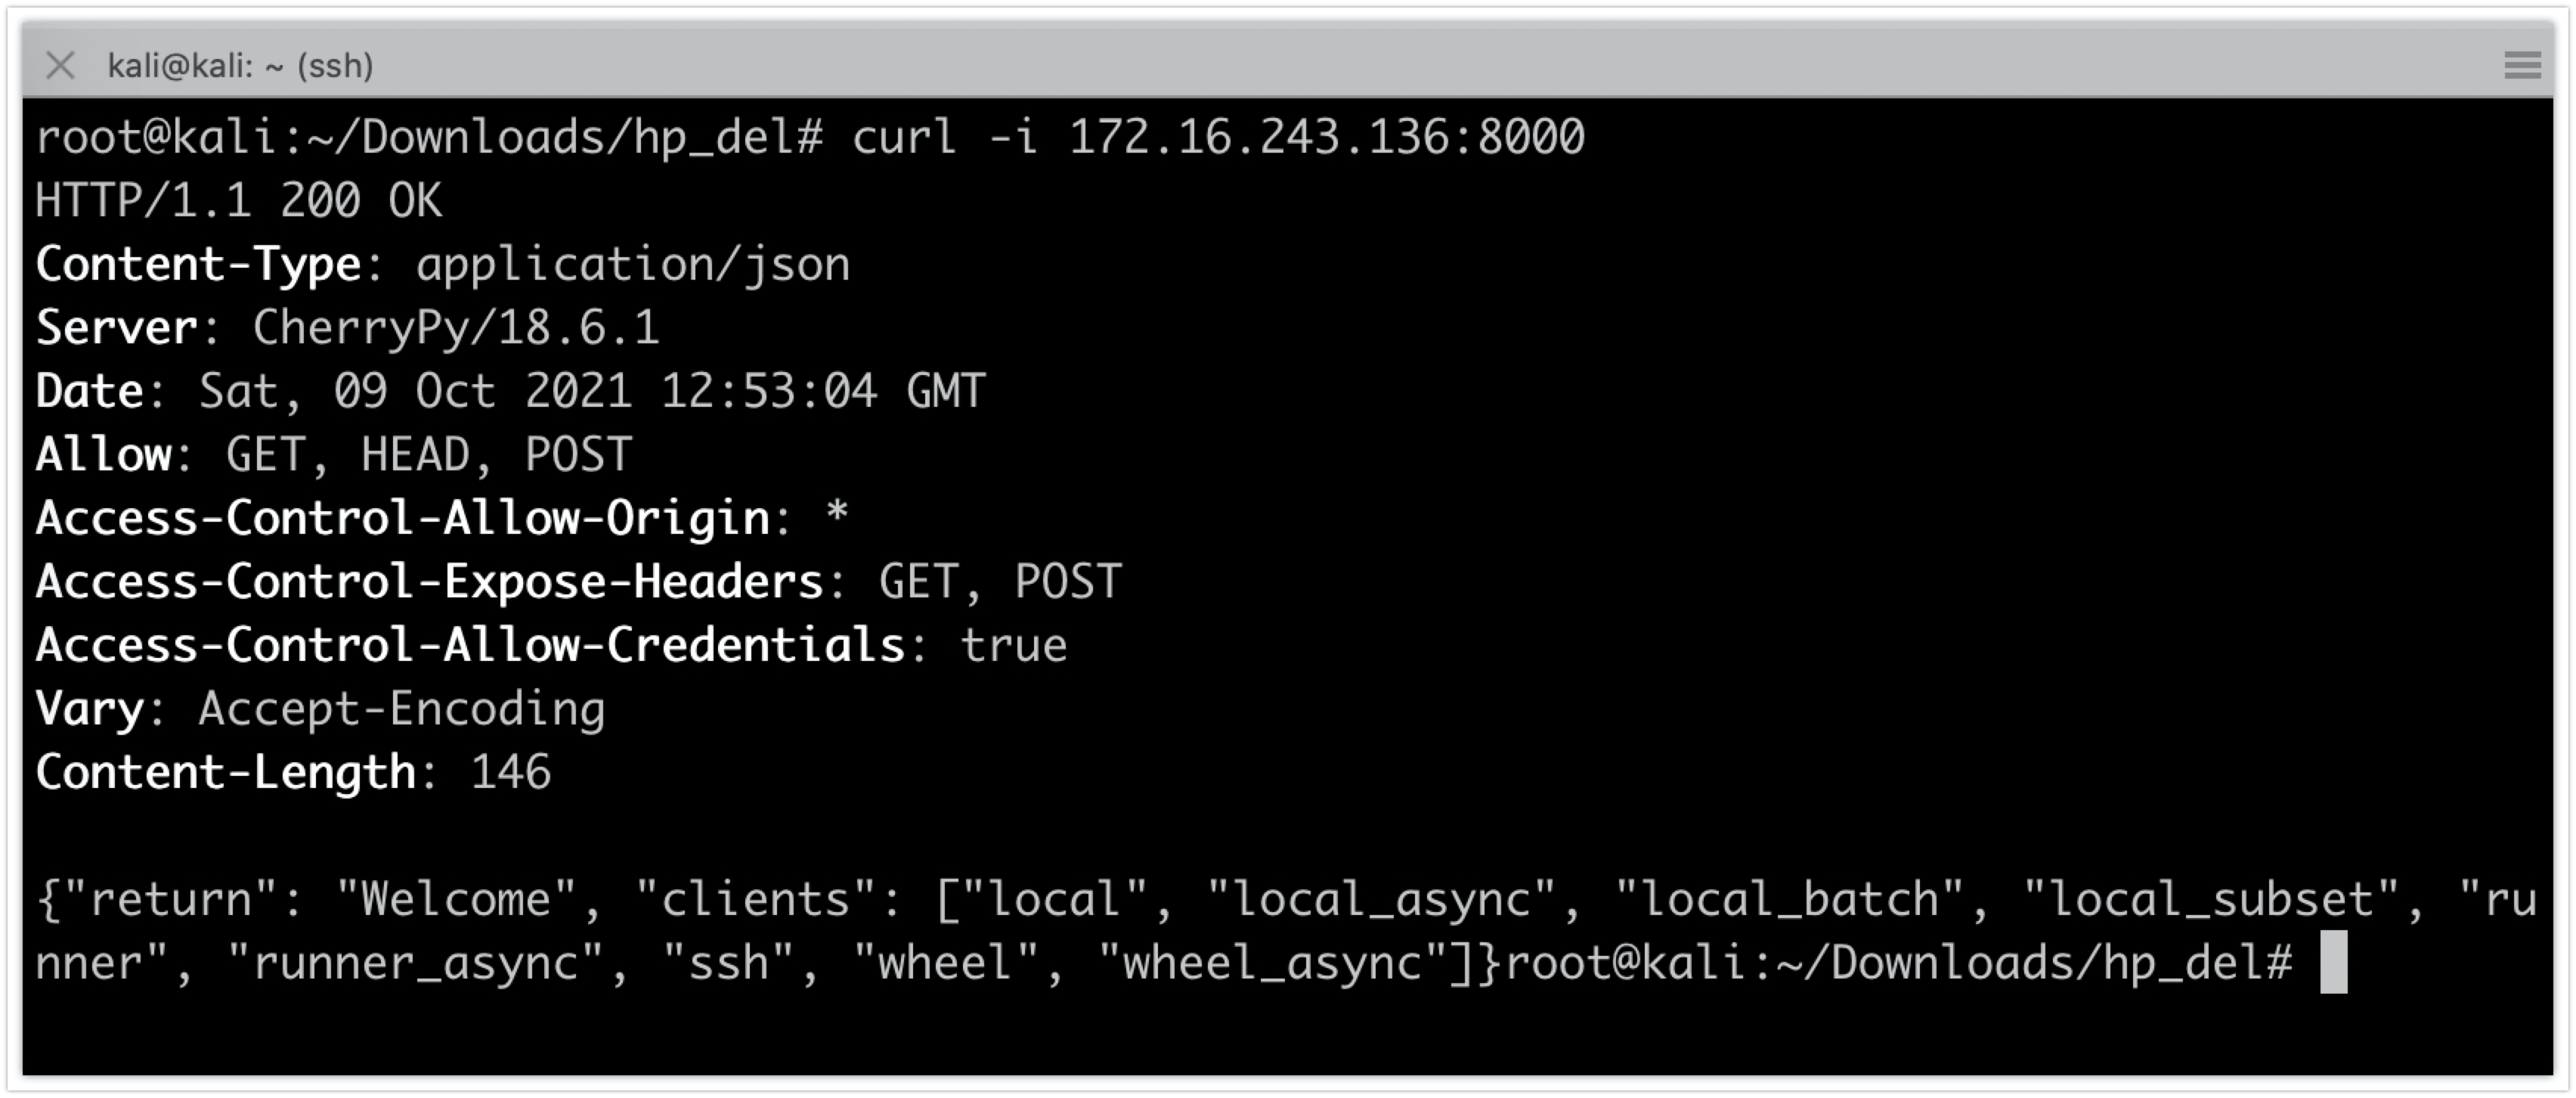 zomy22/cve-2020-16846-saltstack-salt-api
Docker-based lab environment for exploiting CVE-2020-16846, a shell injection vulnerability in SaltStack Salt API, with step-by-step exploitation…
 vig9610/exploiting-samba-on-metasploitable-2
Utilize metasploit from a Kali Linux machine to exploit a well-known samba vulnerability (CVE-2007-2447). This is done in order to infiltrate a…
 mattijsmoens/intentshield
Pre-execution intent verification for AI agents. Audits what your AI is about to do, not what it says. Zero dependencies, deterministic, hash-sealed.
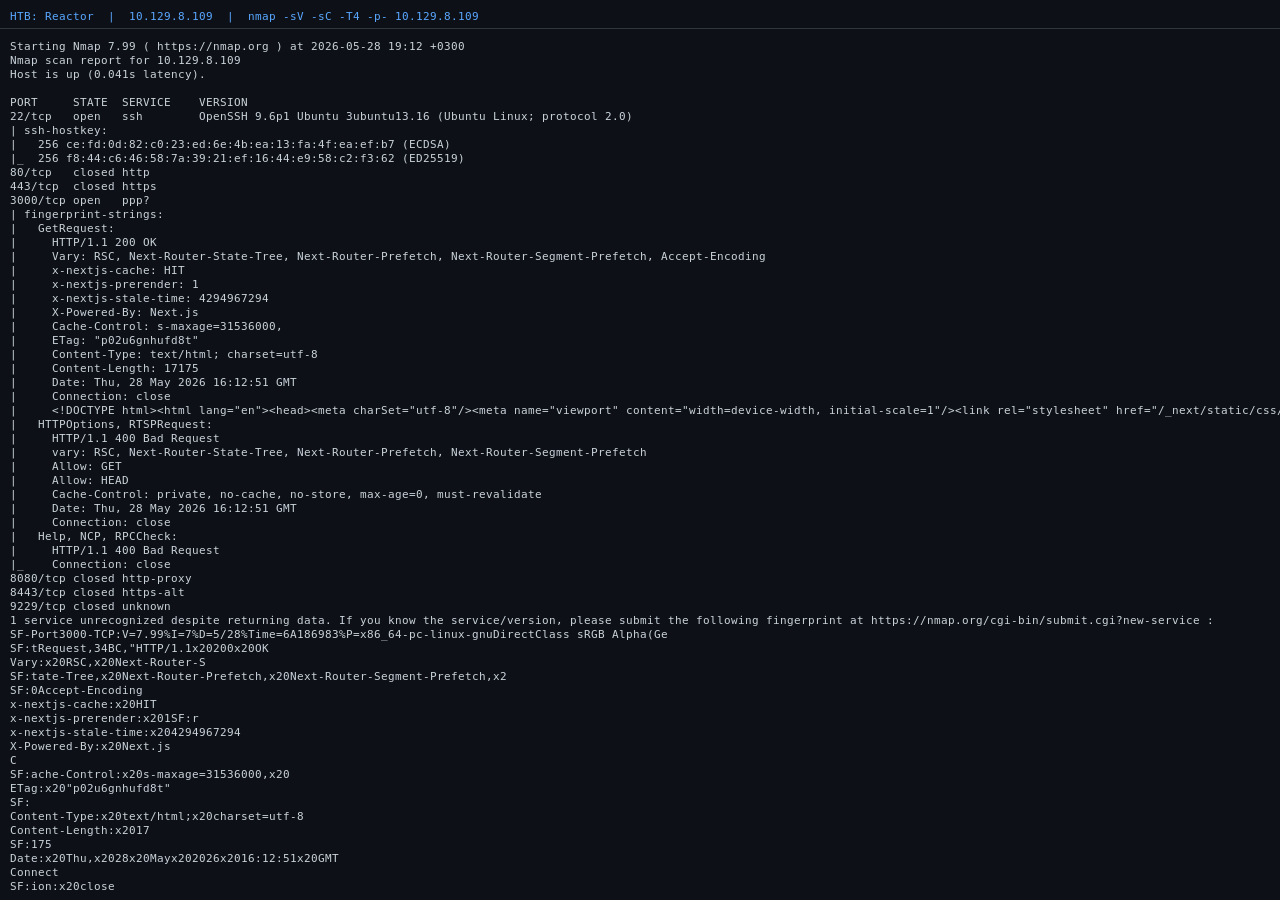 sonnycroco/htb-reactor-linux-machine-walkthrough
Full walkthrough of HTB's Reactor machine — exploit CVE-2025-55182 to gain a shell, then get root via an exposed Node.js debugger. Step-by-step with…
 giangdurian/cve-2026-63030-cve-2026-60137
Pre-auth RCE exploit for WordPress (CVE-2026-63030 + CVE-2026-60137) chaining route confusion and SQL injection into full shell access. Includes…
 r3fr4kt/devvortex
HackTheBox Devvortex walkthrough covering subdomain fuzzing, Joomla API enumeration, template-based web shell, bcrypt hash cracking, and Apport-CLI…
 muhammad-ali007/log4j_cve-2021-44228
Hands-on lab exercise for exploiting Log4Shell (CVE-2021-44228) with JNDI injection, LDAP referral servers, and reverse shell payloads. Includes…
 rahul-securify/react2shell-cve-2025-55182
Proof-of-concept exploit for CVE-2025-55182 demonstrating remote code execution in Next.js via prototype pollution. Includes a pre-configured…
 sastraadiwiguna-purpleeliteteaming/holistic-deconstruction-of-cve-2019-5736-
This repository provides a high-fidelity technical deconstruction and production-ready exploitation suite for CVE-2019-5736. It demonstrates how a…
 shivshantp/cve-2025-24813
Apache Tomcat PUT JSP RCE - CVE-2025-24813 - Exploit & PoC
 fkshield/cve-2025-5548
End-to-end exploitation lab for CVE-2025-5548 (FreeFloat FTP Server stack buffer overflow). Includes static analysis with IDA/Ghidra, binary fuzzing,…
 mrk336/cve-2021-3456
A practical chain that starts with an innocuous PDF file and ends up in a reverse shell on an AWS EC2 instance
 opsxcq/exploit-cve-2014-6271
Shellshock exploit + vulnerable environment