
TIWAP
 tombstoneghost/tiwap
Deliberately vulnerable Flask web application with 22 security flaws across 3 difficulty levels for hands-on penetration testing and web security…
educationlabs-practicepenetration-testing+2
178
tombstoneghost/tiwapDeliberately vulnerable Flask web application with 22 security flaws across 3 difficulty levels for hands-on penetration testing and web security…
 rosesecurity/red-teaming-ttps
Useful Techniques, Tactics, and Procedures for red teamers and defenders, alike!
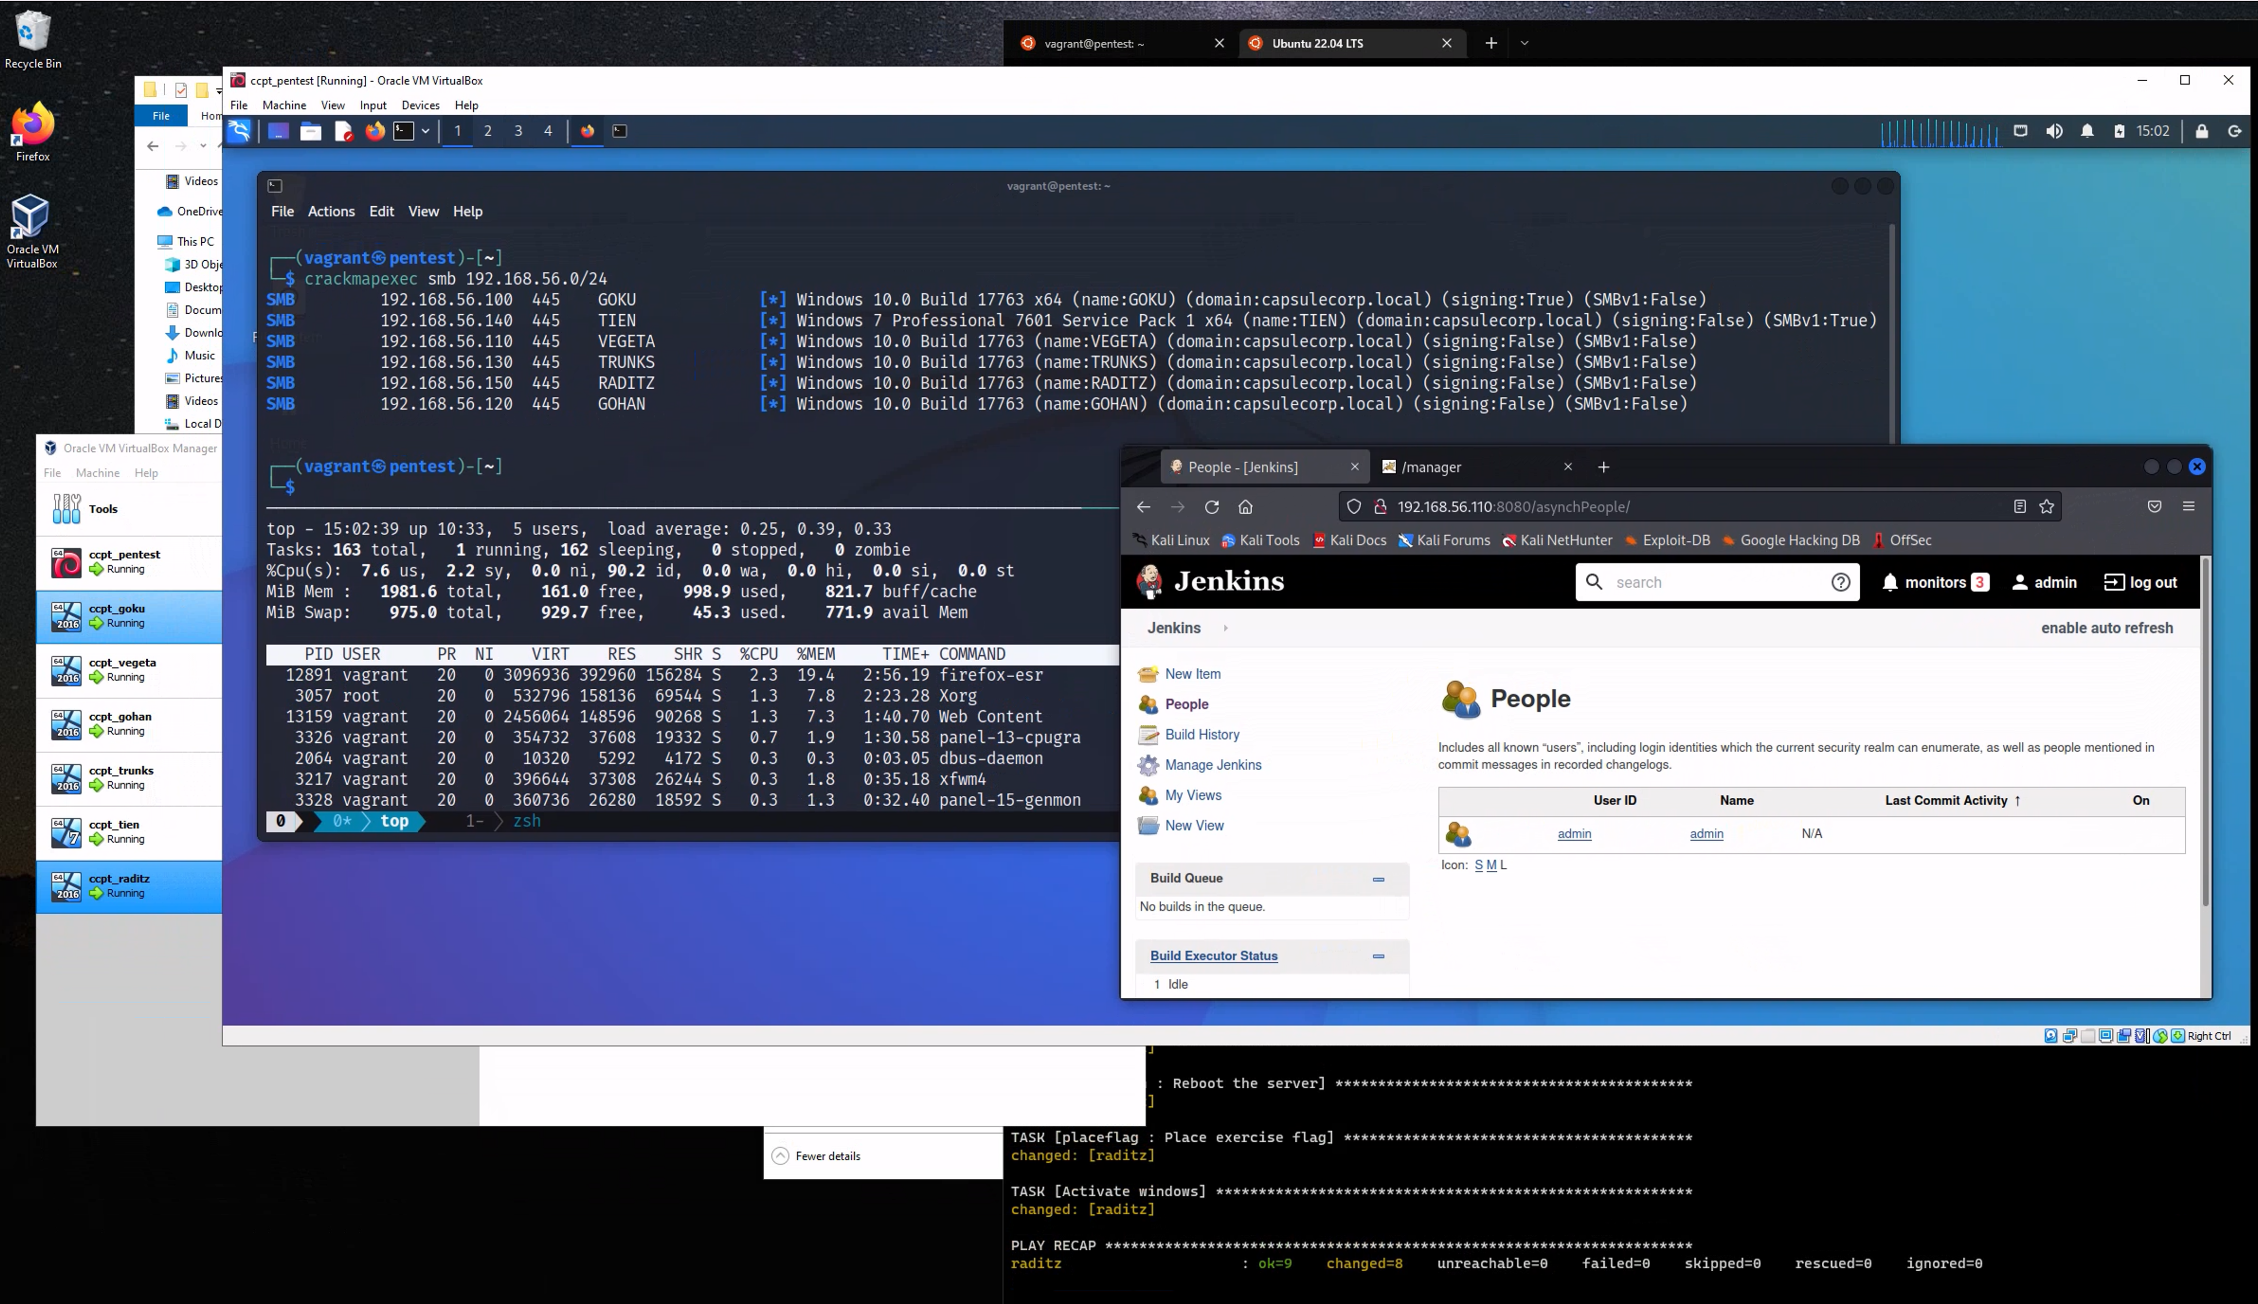 r3dy/capsulecorp-pentest
Vagrant VirtualBox environment for conducting an internal network penetration test
 webpwnized/mutillidae
OWASP Mutillidae II is a free, open-source, deliberately vulnerable web application providing a target for web-security training. This is an…
 priyanshu-rawa/cybersecurity-handbook
Open-source cybersecurity knowledge base with 400+ notes, labs, and cheat sheets covering offense, defense, cryptography, cloud, and forensics.
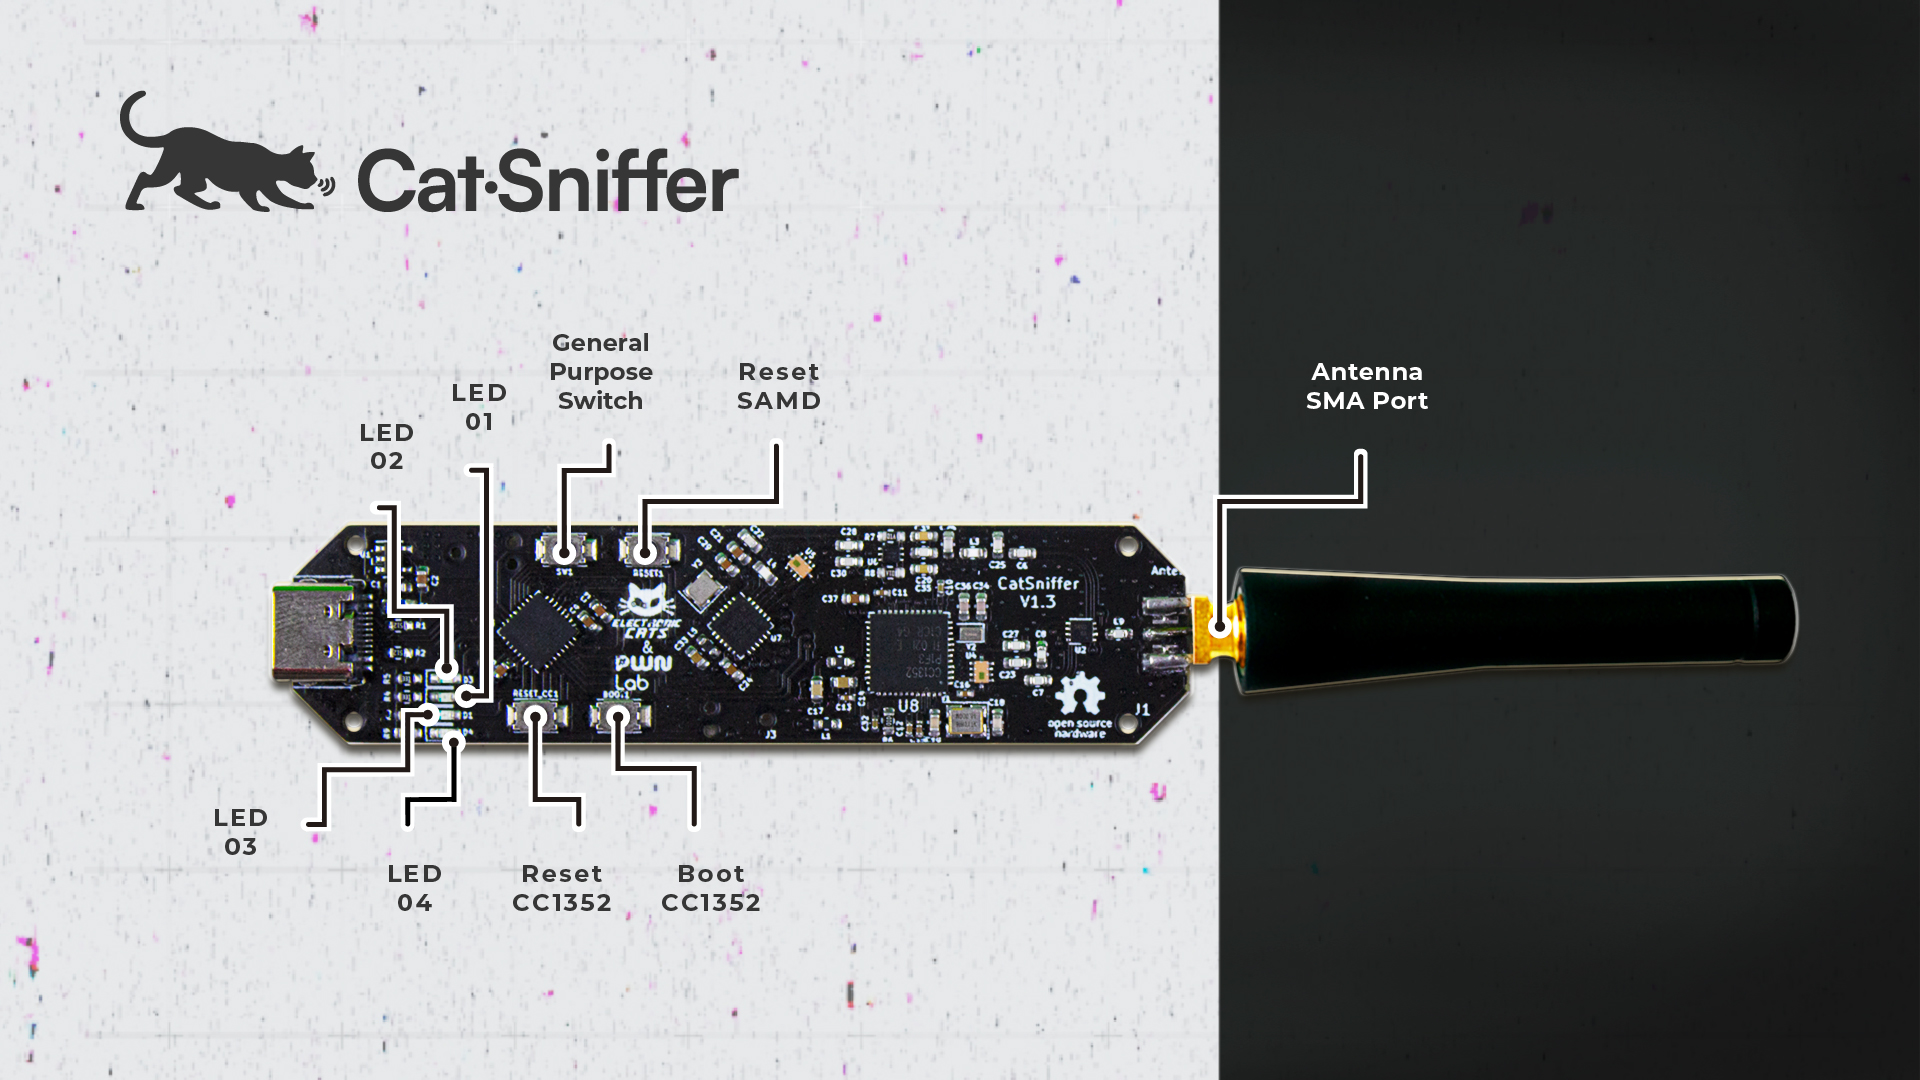 electroniccats/catsniffer
CatSniffer is an original multiprotocol and multiband board for sniffing, communicating, and attacking IoT (Internet of Things) devices using the…
 chryzsh/darthsidious
Building an Active Directory domain and hacking it
 toxy4ny/redteam-ai-benchmark
Red Team AI Benchmark: Evaluating LLMs for authorized offensive-security tasks. Red Team AI Benchmark is a CLI model-evaluation benchmark. It…
 d1se0/cve-2024-21413-vulnerabilidad-outlook-lab
Educational lab demonstrating CVE-2024-21413 Outlook vulnerability exploitation with Python email exploit tool and Responder for NTLM credential…