Burp-Suite-Certified-Practitioner-Exam-Study

Practical study notes and walkthroughs for PortSwigger Academy labs, covering web vulnerabilities, payloads, enumeration, and BSCP exam strategies.

Practical study notes and walkthroughs for PortSwigger Academy labs, covering web vulnerabilities, payloads, enumeration, and BSCP exam strategies.

Curated collection of cybersecurity resources, labs, and training materials covering ethical hacking, penetration testing, exploit development,…

System Vulnerability Checklist & Network Security Hardening project featuring reconnaissance, vsFTPd backdoor analysis (CVE-2011-2523), and active…

Step-by-step SOC analyst walkthrough for investigating and remediating CVE-2024-3400 (PAN-OS command injection). Covers detection, log analysis,…

An isolated Vagrant testbed designed to simulate a complete attack chain: Initial access via the Nginx heap buffer overflow (CVE-2026-42533) followed…

A tool designed to exploit a privilege escalation vulnerability in the sudo program on Unix-like systems. It takes advantage of a specific…

Educational Docker-based lab demonstrating the Heartbleed bug (CVE-2014-0160) with hacker, victim, and server containers for hands-on exploitation…

Cloud pentesting framework deploying vulnerable-by-demand AWS resources with quest-based scenarios to teach practical penetration testing and…

OWASP Mutillidae II is a free, open-source, deliberately vulnerable web application providing a target for web-security training. This is an…

Docker exploit

Utilize metasploit from a Kali Linux machine to exploit a well-known samba vulnerability (CVE-2007-2447). This is done in order to infiltrate a…

Exploit basado en vulnerabilidades criticas Bluetooth (CVE-2023-45866, CVE-2024-21306)

Reproduces CVE-2025-0108 path confusion vulnerability in Nginx/Apache stacks. Includes a vulnerable PoC and a patched implementation demonstrating…

Comprehensive Penetration Testing report and exploit chain for Metasploitable 2 focusing on CVE-2011-2523.

Security research tool for PaperCut CVE-2026-81578 & CVE-2026-82078

Checkov PoC: arbitrary code execution through auto-loaded configuration and unsigned external Python checks.

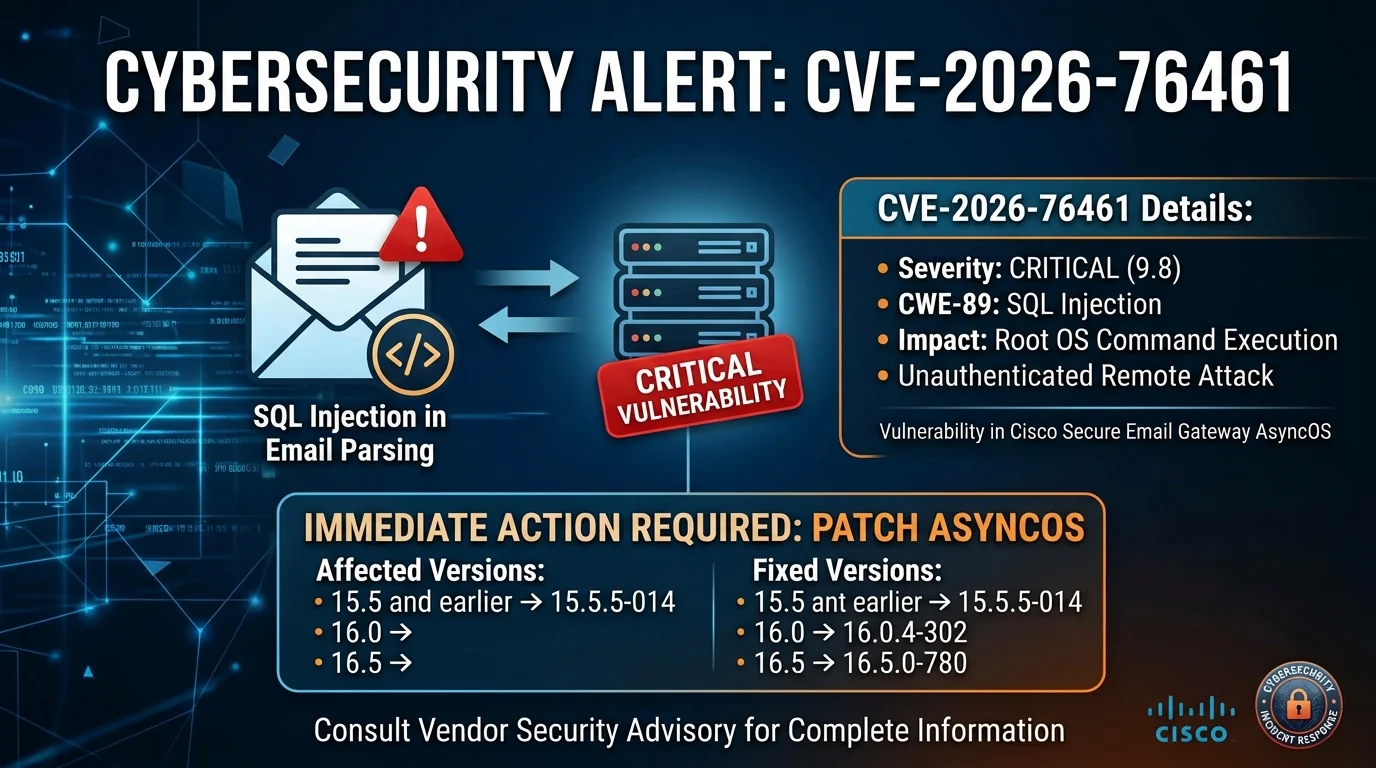
Research repository for CVE-2026-76461, a critical SQL injection in Cisco Secure Email Gateway leading to root RCE, with detection rules, mitigation…

Some labs looking at the xz backdoor vulnerability (CVE-2024-3094)