
cve-2026-8697
 itzmetanjim/cve-2026-8697
Detailed CVE-2026-8697 writeup with POC exploit for a login rate-limit bypass on TP-Link Archer C64 routers via a debug SSH service, enabling…
educationexploitationhardware-iot-security+7
1
itzmetanjim/cve-2026-8697Detailed CVE-2026-8697 writeup with POC exploit for a login rate-limit bypass on TP-Link Archer C64 routers via a debug SSH service, enabling…
 ultramangaia/xiaomi_mi_wifi_r3g_vulnerability_poc
A login bypass(CVE-2019-18371) and a command injection vulnerability(CVE-2019-18370) in Xiaomi Router R3G up to version 2.28.23.
 xewdy444/netgrave
A tool for retrieving login credentials from Netwave IP cameras using a memory dump vulnerability (CVE-2018-17240)
 xw77cve/cve-2019-7642
Proof-of-concept exploit for CVE-2019-7642 demonstrating unauthenticated access to DNS query logs and login history on vulnerable D-Link routers via…
 haingn/lohongcam-cve-2021-33044
Python exploit for Dahua device authentication bypass (CVE-2021-33044). Sends crafted malicious data packets to bypass login and gain unauthorized…
 kienquoc102/cve-2018-9995-2
Python exploit for CVE-2018-9995 targeting DVR/NVR devices with login bypass, supporting reconnaissance via Shodan and Zoomeye dorks.
 mesutozsoycom/cve-2018-9995
exploit camera with vuln cve-2018-9995 ( Novo, CeNova, QSee, Pulnix, XVR 5 in 1 (title: "XVR Login"), Securus, - Security. Never Compromise !! - …
 0xf3d0rq/cve-2017-7921
CVE-2017-7921 is a critical vulnerability (CVSS score: 9.8) affecting multiple Hikvision IP camera and DVR models, first disclosed in 2017. It stems…
 kirubel-cve/cve-2025-65427
Proof-of-concept exploit for CVE-2025-65427: missing rate limiting on Dbit N300 T1 Pro router login API enabling brute-force attacks and…
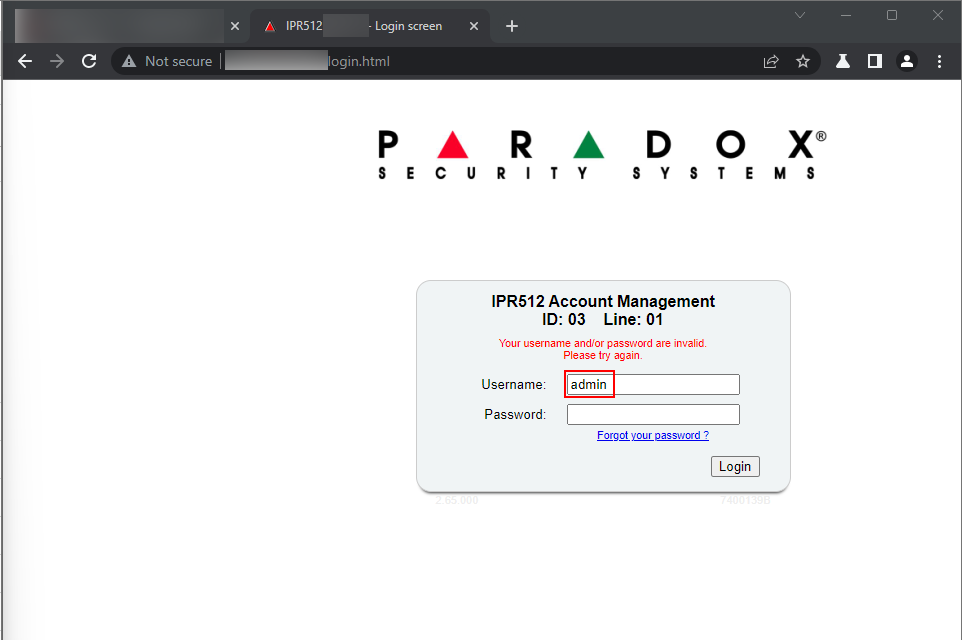 darknesschieftain/injection-vulnerability-in-paradox-security-systems-ipr512-cve-2023-24709-poc
In Paradox Security System IPR512 Web console login form page, attacker can input JavaScript string, such as "</script>" that will overwrite…
 c0nyy/iot_vuln
Proof-of-concept exploits for IoT device vulnerabilities, including TOTOLINK login bypass CVEs, with detailed technical analysis and reproduction…
 miguelhamal/cve-2019-19393
Proof-of-concept for stored XSS vulnerability in Rittal CMC PU III web management interface, enabling persistent client-side script injection before…
 ajaymt6/ultramangaia
A login bypass(CVE-2019-18371) and a command injection vulnerability(CVE-2019-18370) in Xiaomi Router R3G up to versi…
 spy0x7/cve-2021-33044
Dahua IPC/VTH/VTO devices auth bypass exploit
 baza-nato/cve-2021-33044
Exploit for Dahua IPC/VTH/VTO devices that bypasses identity authentication by sending crafted malicious packets, allowing unauthorized access.
 nrtlox/cve-2025-63587
CVE-2025-63587
 rosembergpro/cve-2024-48644
Reolink Duo 2 WiFi v1.0.280 - Account Enumeration Vulnerability
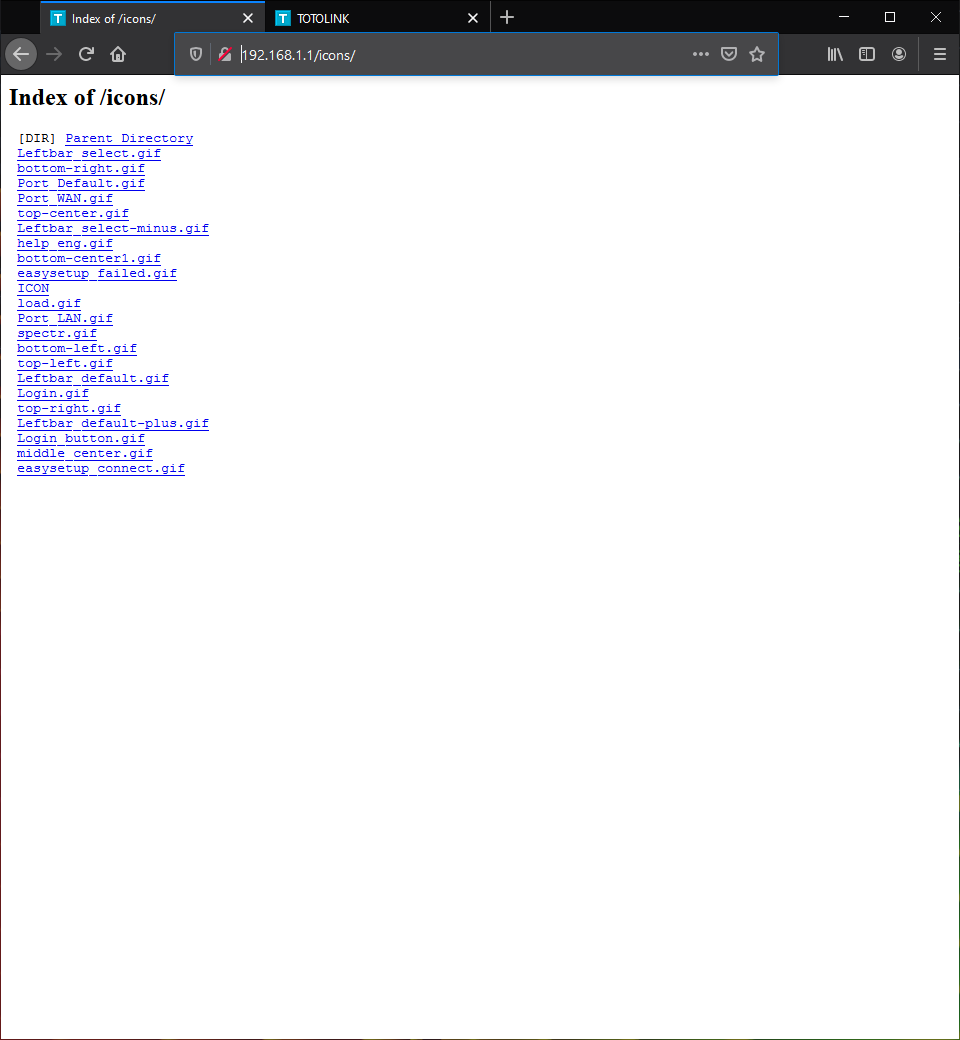 swzhouu/cve-2020-27368
TOTOLINK-A702R-V1.0.0-B20161227.1023 Directory Indexing Vulnerability