
CVE-2019-13361
 lodi-g/cve-2019-13361
Smanos W100 1.0.0 devices have Insecure Permissions, exploitable by an attacker on the same Wi-Fi network.
exploitationiot-securitypenetration-testing+2
lodi-g/cve-2019-13361Smanos W100 1.0.0 devices have Insecure Permissions, exploitable by an attacker on the same Wi-Fi network.
 kirubel-cve/cve-2025-65427
Proof-of-concept exploit for CVE-2025-65427: missing rate limiting on Dbit N300 T1 Pro router login API enabling brute-force attacks and…
 my0723/cnvd-2022-27366__cve-2023-37621
Exploit for CVE-2023-37621 targeting unauthorized access in Fronius Datalogger Web 2.0.5-4, allowing attackers to retrieve sensitive device…
 mk-ultra-project-monarch/cve-2017-7921-writeup-2026
Vulnerability research write-up on CVE-2017-7921 — a critical unauthenticated auth bypass in Hikvision IP cameras/DVRs/NVRs, covering root cause,…
 remenis/cve-2025-63667
Vatilon-based IP camera firmwares issue Session-Id tokens without verifying credentials, allowing attackers to obtain sessions and retrieve plaintext…
 bytereaper77/cve-2025-7795
Proof-of-concept exploit for a buffer overflow vulnerability in Tenda routers. Sends crafted unauthenticated POST requests to trigger a crash and…
 poxsky/cve-2026-38577
Proof-of-concept demonstrating hardcoded root credentials (admin/system) in Tenda HG21 XPON modem firmware, enabling unauthorized root access via…
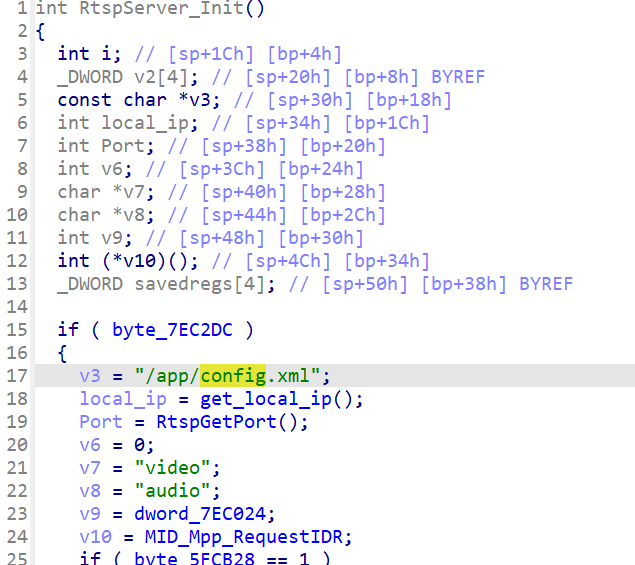 namaek2/cve-2025-70962
CVE-2025-70962 PoC
 danish1162/cve-2026-2035703-x300
Tozed ZLT X300 5G CPE — Remote Root Code Execution via SDR Rogue Base Station (CVE-2026-2035703, CWE-78, CVSS 9.8) — Coordinated Disclosure
 snyi001/cve-2026-79551-tenda
Tenda Technology Co., Ltd NVR_4H: CH3 v2.1.V27.5.58.6 was discovered to contain a hardcoded cryptographic key.