
-CVE-2017-0785-BlueBorne-PoC
 alfa100001/-cve-2017-0785-blueborne-poc
CVE-2017-0785 BlueBorne PoC
bluetooth-securityexploitationinformation-gathering+4
40
alfa100001/-cve-2017-0785-blueborne-pocCVE-2017-0785 BlueBorne PoC
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
 wh00hw/pyflipper
Flipper Zero Python CLI Wrapper
 cisc0-gif/kitt
Python-Based Pentesting Framework
 flipperdevices/flipperzero-firmware
Flipper Zero firmware source code
 secdev/scapy
Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
 rfidresearchgroup/proxmark3
Hardware tool for RFID analysis, emulation, and penetration testing. Supports 125kHz, 13.56MHz protocols (MIFARE, iClass, ISO14443/15693) with key…
 earlephilhower/arduino-pico
Raspberry Pi Pico Arduino core, for all RP2040 and RP2350 boards
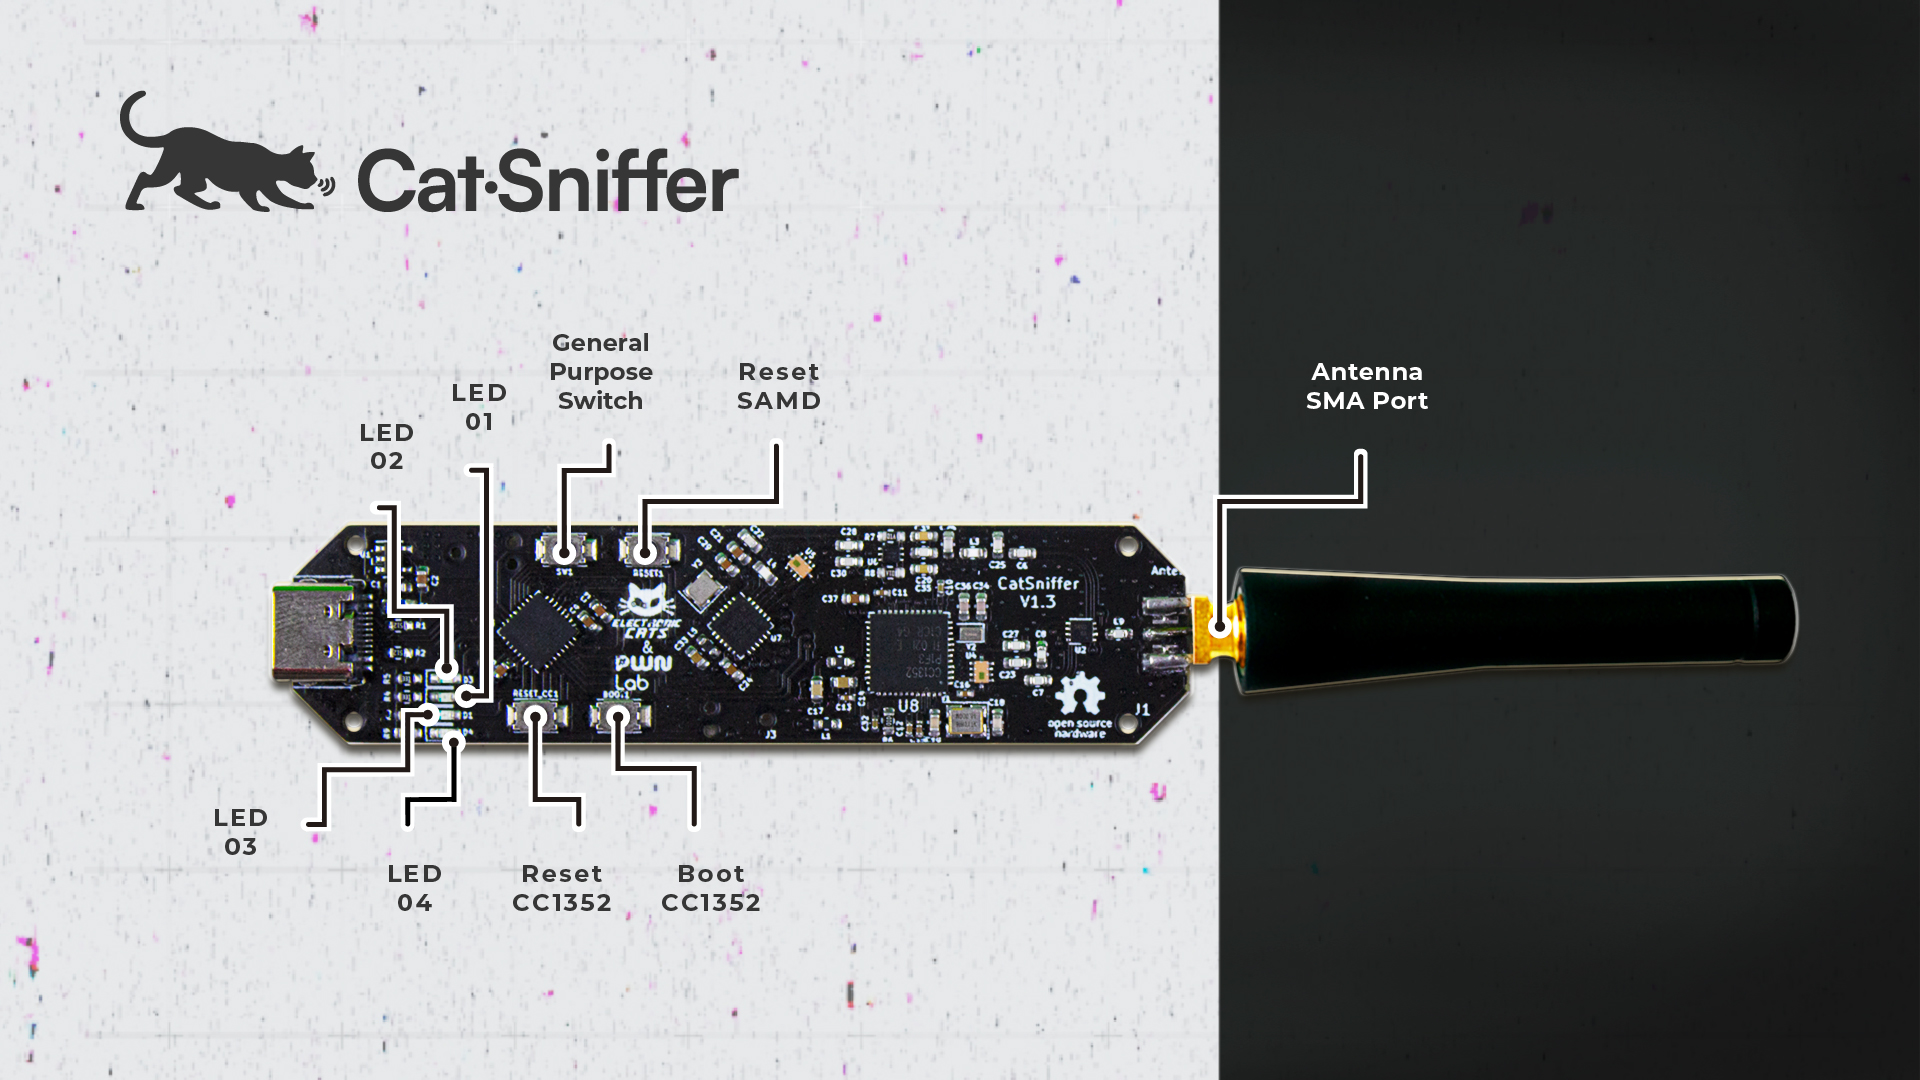 electroniccats/catsniffer
CatSniffer is an original multiprotocol and multiband board for sniffing, communicating, and attacking IoT (Internet of Things) devices using the…
 furrtek/precir
Open-source hardware and software toolkit for reverse-engineering and communicating with infrared-based electronic shelf labels. Includes custom…
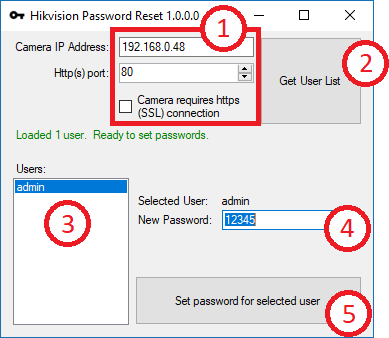 bp2008/hikpasswordhelper
A tool which exploits a backdoor in Hikvision camera firmwares circa 2014-2016 to help the owner change a forgotten password.
 botlabsdev/cve-2020-11881
CVE-2020-11881: unauthenticated remote DoS for MikroTik SMB service.
 zzz66686/cve-2017-14262
Exploit for CVE-2017-14262 targeting Samsung NVR devices: extracts admin MD5 password hash via unauthenticated CGI request and logs in with the hash…
 interceptsuite/interceptsuite
MITM proxy for TCP/TLS/DTLS/UDP traffic, with STARTTLS, IoT, Thick Client and more.
 azhariramadhan/cve-2025-45512
Proof-of-concept exploit suite for U-Boot bootloader vulnerabilities, including insecure update mechanisms, hardcoded credentials, debugging…
 gigachadusers/cve-2026-20169
Windows-native IoT vulnerability scanner that discovers exposed management interfaces, tests default credentials, and validates network segmentation…
 spiritualmachines/buds-audit
No-dongle, no-root Bluetooth security assessment tool for wireless earbuds affected by the Airoha SDK vulnerability chain (CVE-2025-20700/20701/20702)