
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
242 results
CVE-2026-19586 preview

CVE-2026-19586

GitHubmattgsys/cve-2026-19586

Python PoC exploiting CVE-2026-19586, an unauthenticated command injection in TP-Link Omada SSL VPN that executes arbitrary commands as root via…
command-and-controlcryptographyembedded-systems-security+6
2
1 month ago
GL.iNet-Multiple-Vulnerabilities preview

GL.iNet-Multiple-Vulnerabilities

GitHubcyberaz0r/gl.inet-multiple-vulnerabilities

Exploits for GL.iNet CVE-2023-46454, CVE-2023-46455 and CVE-2023-46456
embedded-systems-securityexploitationhardware-security+3
32 years ago
sricam-gsoap2.8-dos-exploit preview

sricam-gsoap2.8-dos-exploit

GitHubbitfu/sricam-gsoap2.8-dos-exploit

Sricam gSOAP2.8 DoS exploit PoC
embedded-systems-securityexploitationiot-security+3
37 years ago
CVE-2024-22894 preview

CVE-2024-22894

GitHubjaarden/cve-2024-22894

Proof-of-concept exploit for CVE-2024-22894, demonstrating 3DES-encrypted root password extraction from Alpha Innotec/Novelan heatpump firmware,…
cryptographyembedded-systems-securityexploitation+6
32 years ago
CVE-2026-94095 preview

CVE-2026-94095

GitHubhackspeak/cve-2026-94095

PoC for CVE-2026-94095, a traceroute command injection in Netcore NBR200V2 firmware via ubus JSON-RPC, enabling root RCE for authorized testing.
embedded-systems-securityexploitationhardware-iot-security+5
17 days ago
CVE-2024-48705 preview

CVE-2024-48705

GitHubl41kaa/cve-2024-48705

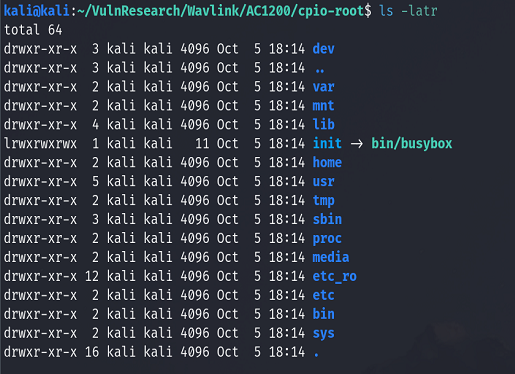
Wavlink AC1200 with firmware versions M32A3_V1410_230602 and M32A3_V1410_240222 are vulnerable to a post-authentication command injection while…

binary-analysiscommand-and-controlembedded-systems-security+7
21 year ago
CVE-2022-24693 preview

CVE-2022-24693

GitHublukejenkins/cve-2022-24693

Documentation and reproduction steps for CVE-2022-24693: hardcoded credentials in Baicells Nova436Q and Neutrino 430 firmware, enabling remote SSH…
embedded-systems-securityexploitationfirmware-analysis+6
31 year ago
nec_aterm_tools preview

nec_aterm_tools

GitHubinfobyte/nec_aterm_tools

Extracts hardware random keys from NEC Aterm router firmware images and QR codes to generate valid passwords for gaining shell access.

embedded-systems-securityexploitationfirmware-analysis+4
34 years ago
CVE-2020-35575-TP-LINK-TL-WR841ND-password-disclosure preview

CVE-2020-35575-TP-LINK-TL-WR841ND-password-disclosure

GitHubdylvie/cve-2020-35575-tp-link-tl-wr841nd-password-disclosure

Weaponized exploit script for CVE-2020-35575, a password-disclosure vulnerability in TP-Link router web interfaces, granting remote administrative…
embedded-systems-securityexploitationiot-security+3
31 year ago
CVE-2026-22017-Firmware-Update-via-BLE-Without-Authentication preview

CVE-2026-22017-Firmware-Update-via-BLE-Without-Authentication

GitHubgeorge0papasotiriou/cve-2026-22017-firmware-update-via-ble-without-authentication

Simulated BLE peripheral exposing an unauthenticated GATT firmware-update characteristic; demonstrates critical CVE-2026-22017 device-takeover…
bluetooth-securityembedded-systems-securityexploitation+4
1 month ago
accfly preview

accfly

GitHubtezeb/accfly

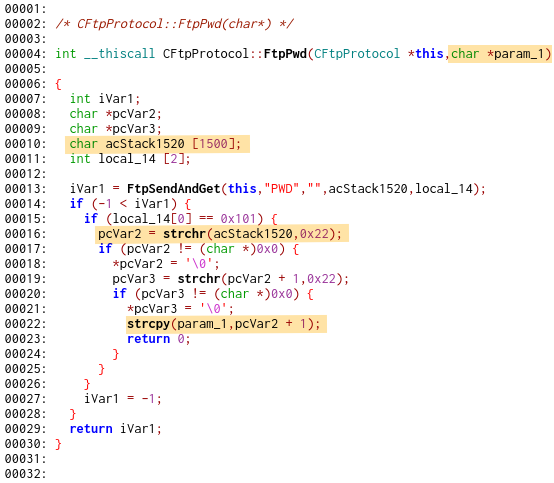
Disclosure of Accfly camera vulnerabilities: CVE-2020-25782, CVE-2020-25783, CVE-2020-25784, CVE-2020-25785.
binary-exploitationembedded-systems-securityexploitation+6
35 years ago
Poc-CVE-2024-57040 preview

Poc-CVE-2024-57040

GitHubabsholi7ly/poc-cve-2024-57040

CVE-2024-57040 is a security vulnerability found in certain TP-Link TL-WR845N router models. Specifically, it involves a "hardcoded" password for the…
embedded-systems-securityexploitationhardware-iot-security+3
21 year ago
CVE-2026-21006-Zigbee-Light-Link-Factory-Reset-Exploit preview

CVE-2026-21006-Zigbee-Light-Link-Factory-Reset-Exploit

GitHubgeorge0papasotiriou/cve-2026-21006-zigbee-light-link-factory-reset-exploit

Simulated Zigbee Light Link (ZLL) factory reset exploit for CVE-2026-21006, demonstrating unauthenticated TouchLink command injection that wipes…
embedded-systems-securityexploitationhardware-iot-security+3
1 month ago
WiFi-SpiderWeb preview

WiFi-SpiderWeb

GitHubbadrrx/wifi-spiderweb

An active cyber defense & honeypot system for OpenWrt routers running from a USB drive.
defensive-toolsembedded-systems-securityhardware-security+7
34 months ago
tapo-c260-rce preview

tapo-c260-rce

GitHubl0lsec/tapo-c260-rce

PoC exploit chain for TP-Link Tapo C260 camera — CVE-2026-0651/0652/0653. Research by @spaceraccoon.
command-and-controlembedded-systems-securityexploitation+7
26 months ago
CVE-2023-40459 preview

CVE-2023-40459

GitHubmajidmc2/cve-2023-40459

PoC of CVE-2023-40459 (DoS on ACEmanager)

embedded-systems-securityexploitationiot-security+2
42 years ago
CVE-2026-8023 preview

CVE-2026-8023

GitHubret2c/cve-2026-8023

PoC for CVE-2026-8023: Improper Limitation of a Pathname to a Restricted Directory ('Path Traversal')
embedded-systems-securityexploitationiot-security+3
3 months ago
CVE-2026-8888-Printer-Firmware-Unsigned-Update-via-HTTP preview

CVE-2026-8888-Printer-Firmware-Unsigned-Update-via-HTTP

GitHubgeorge0papasotiriou/cve-2026-8888-printer-firmware-unsigned-update-via-http

Demonstrates CVE-2026-8888, an unsigned printer firmware update over HTTP, including a malicious update server and vulnerable printer emulator for…

embedded-systems-securityexploitationfirmware-analysis+4
1 month ago
Previous1…678…14Next