
gxdlmsdirector-cve
 seqred-s-a/gxdlmsdirector-cve
CVE-2020-8809 and CVE-2020-8810
educationexploitationiot-security+3
16 years ago
seqred-s-a/gxdlmsdirector-cveCVE-2020-8809 and CVE-2020-8810
 mk-ultra-project-monarch/cve-2017-7921-writeup-2026
Vulnerability research write-up on CVE-2017-7921 — a critical unauthenticated auth bypass in Hikvision IP cameras/DVRs/NVRs, covering root cause,…
 my0723/cnvd-2022-27366__cve-2023-37621
Exploit for CVE-2023-37621 targeting unauthorized access in Fronius Datalogger Web 2.0.5-4, allowing attackers to retrieve sensitive device…
 michaeladamgroberman/cve-2026-32662
CVE-2026-32662: Active Debug Code in Production — Gardyn Home Kit (ICSA-26-055-03)
 pointedsec/cve-2024-57725
This repository documents an unauthenticated GPON manipulation vulnerability discovered in certain Arcadyan routers.
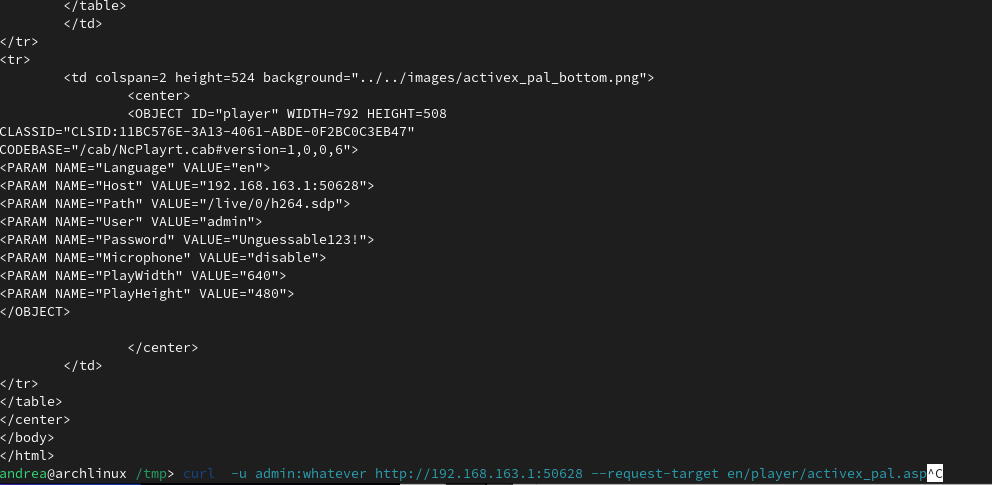 n0n4m3x41/cve-2025-1738
0day discover CVE-2025-1738
 fzbacon/cve-2019-18370_xiaomi_mi_wifi_rce_analysis
 mirellesilvajs/iot-vuln-lab-cve-2017-17761
Simulação educacional de exploração de falha em dispositivos IoT com base no CVE-2017-17761

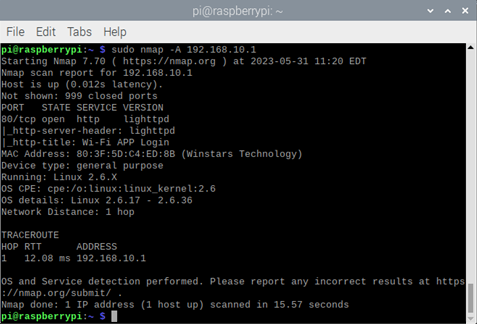 scorpion-security-labs/cve-2020-12124
Proof-of-concept exploit for CVE-2020-12124 targeting Wavlink AC1200 router, demonstrating unauthenticated command injection and stack buffer…
 c0nyy/iot_vuln
Proof-of-concept exploits for IoT device vulnerabilities, including TOTOLINK login bypass CVEs, with detailed technical analysis and reproduction…
 lequockhanh2k/tool_camera_exploit_netwave_cve-2018-6479
Exploit tool for CVE-2018-6479, a denial-of-service vulnerability in Netwave IP cameras. Targets IoT devices to trigger temporary service disruption…
 hamza0x/cve-2023-37073
Telnet default credentials can lead to information disclosure and denial-of-service (DoS) attacks.
 cr0n1c/dlink_shell_poc
Dlink 615/815 shell PoC
 prisect/hichipreset
Hicip IP admin password reset script using CVE-2020-9529. This is made for educational purposes only of course.
 4onurdemir/tcl-androidtv-root-attempts
Documents reverse engineering of a TCL Android TV factory layer: 56 kHz IR protocol, tclfactoryos daemon, kernel IR driver, and evidence that…