

proxmark3
 rfidresearchgroup/proxmark3
Hardware tool for RFID analysis, emulation, and penetration testing. Supports 125kHz, 13.56MHz protocols (MIFARE, iClass, ISO14443/15693) with key…
bluetooth-securitycryptographyembedded-systems-security+11
6.2k
rfidresearchgroup/proxmark3Hardware tool for RFID analysis, emulation, and penetration testing. Supports 125kHz, 13.56MHz protocols (MIFARE, iClass, ISO14443/15693) with key…
 secdev/scapy
Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
 earlephilhower/arduino-pico
Raspberry Pi Pico Arduino core, for all RP2040 and RP2350 boards
 mrhenrike/embedxpl-forge
Embedded Device Security Assessment Framework — 700 modules, 350 CVEs, 55 vendors, APT Group Engine. Covers routers, IP cameras, GPON ONTs, ISP CPEs,…
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
 flipperdevices/flipperzero-firmware
Flipper Zero firmware source code
 karaaslanlabs/kl-security-key
Experimental RP2040 FIDO2/WebAuthn authenticator with packed attestation and documented Windows/Entra interoperability
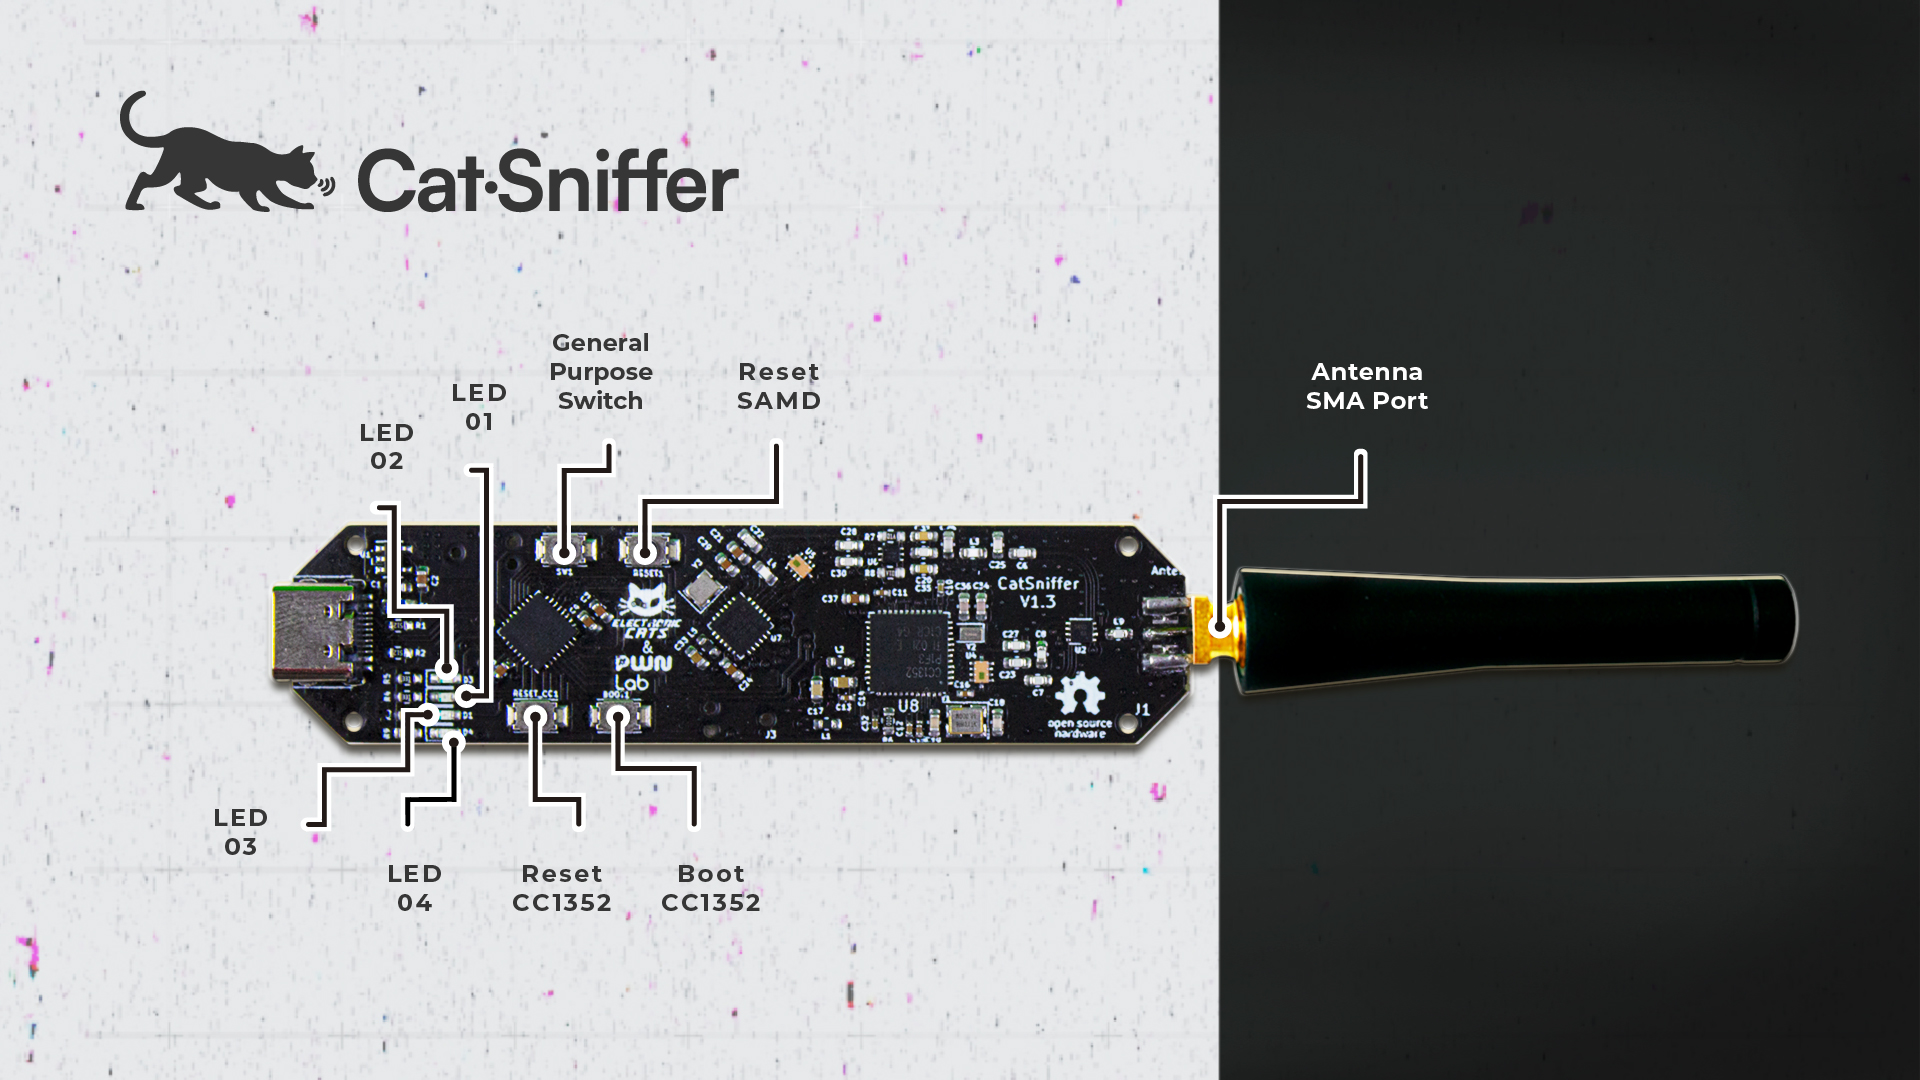 electroniccats/catsniffer
CatSniffer is an original multiprotocol and multiband board for sniffing, communicating, and attacking IoT (Internet of Things) devices using the…
 cisagov/untitledgoosetool
Untitled Goose Tool is a robust and flexible hunt and incident response tool that adds novel authentication and data gathering methods in order to…
 foxio-llc/ja4
JA4+ is a suite of network fingerprinting standards
 y0oshi/project-deep-focus
Asynchronous network reconnaissance engine for large-scale service discovery and fingerprinting. Identifies unsecured services (RTSP cameras, VNC,…
 nocoderrandom/sunsetscan
Local-network security auditing with EOL, CVE, device identity, and HTML reports
 codykociemba/nolongerevil-thermostat
Breathe fresh life into your bricked Nest, now with 100% less evil!
 cappricio-securities/cappriciosec-university
A Hacker's E-learning App for Tamil People
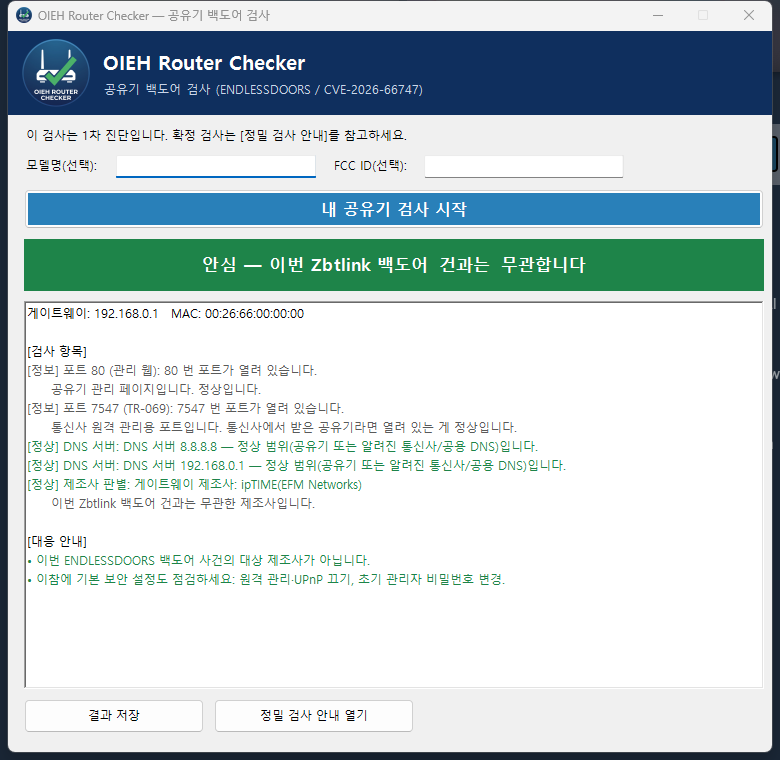 oiehnow/oieh-router-checker
내 공유기가 Zbtlink ENDLESSDOORS 백도어(CVE-2026-66747) 대상인지 클릭 한 번으로 검사하는 Windows 프로그램
 wyl-cmd/cve-2017-7921-research-toolkit
用于借助FOFA快速测试海康威视的CVE-2017-7921漏洞,并且给出登陆账号和密码,并输出json文件。
 msdmehdipour/meshtastic-cve-2025-52464-poc
Software-only proof of concept for CVE-2025-52464 in Meshtastic Direct Messages
 gigachadusers/cve-2026-20169
Windows-native IoT vulnerability scanner that discovers exposed management interfaces, tests default credentials, and validates network segmentation…