
zoneminder
 zoneminder/zoneminder
ZoneMinder is a free, open source Closed-circuit television software application developed for Linux which supports IP, USB and Analog cameras.
anomaly-detectiondefensive-toolshardware-security+3
5.9k
zoneminder/zoneminderZoneMinder is a free, open source Closed-circuit television software application developed for Linux which supports IP, USB and Analog cameras.
 zephyrproject-rtos/zephyr
Primary Git Repository for the Zephyr Project. Zephyr is a new generation, scalable, optimized, secure RTOS for multiple hardware architectures.
 yozarseef95/cve-2023-31594
IC Realtime ICIP-P2012T 2.420 is vulnerable to Incorrect Access Control
 roxanne_ardary/ai-and-the-automobile
Curated collection of open specifications for AI-integrated vehicle systems, covering autonomy, perception, navigation, energy management, safety,…
 nrtlox/cve-2025-63587
CVE-2025-63587
 steampunk424/cve-2025-36911-wisper_pair_target_finder
This is not an exploit for CVE-2025-36911!!! This is a detector for finding potentially vulnerable devices! Only use on your own devices! I am not…
 hivesecurity/pso-printer-security-offensive
Offensive security tool for printer pentesting
 hanianis/cve-2025-63353
A vulnerability in fiberhome GPON ONU HG6145F1 RP4423 allows the device's factory default Wi-Fi password (WPA/WPA2 pre-shared key) to be predicted…
 kh4sh3i/cve-2025-34152
Go-based PoC exploit for unauthenticated remote code execution on Shenzhen Aitemi M300 Wi-Fi repeaters. Includes a scanner and does not reboot the…
 d-raco/cve-2024-31964
Proof-of-concept exploit for CVE-2024-31964, a temporary authentication bypass in Mitel 6900w Series SIP phones allowing unauthenticated POST…
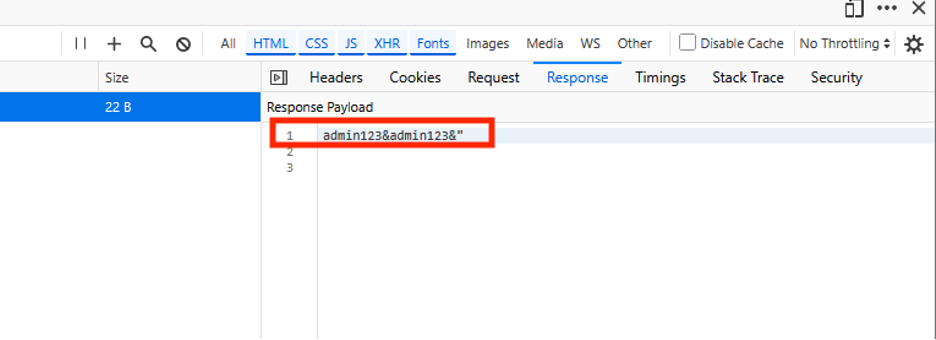 weedl/cve-2025-45620
Disclosure of client-side authentication bypass in AVer camera web interface exposing unencrypted credentials via network traffic monitoring.
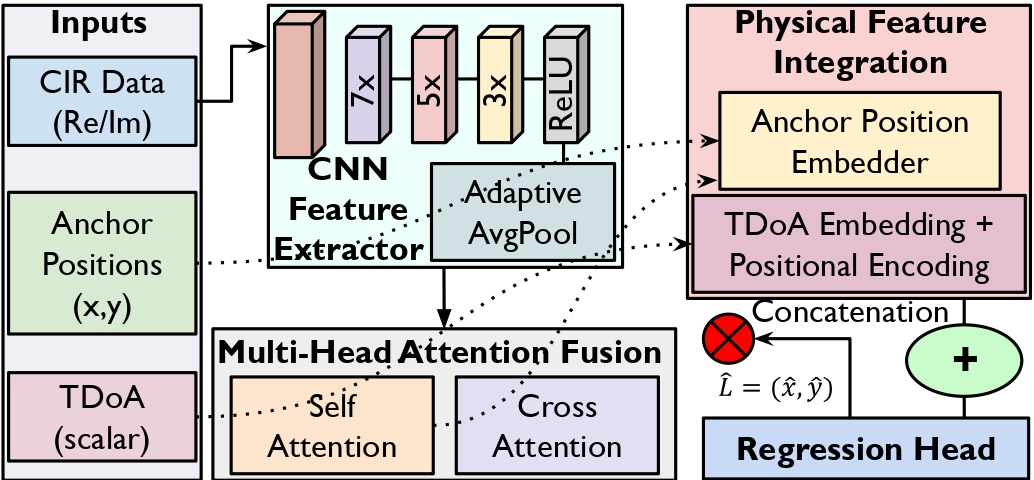 sec5gloc/sec5gloc
Adversary-resilient deep learning architecture for secure 5G indoor localization, combining CNN and multi-head attention to defend against signal…
 thottysploity/cve-2024-53375
TP-Link Archer AXE75 Authenticated Command Injection
 redfox-security/digisol-dg-gr1321-s-password-storage-in-plaintext-cve-2024-4232
Proof-of-concept demonstrating plaintext password storage vulnerability in Digisol DG-GR1321 routers, enabling credential exposure and unauthorized…
 bahaabdelwahed/st
IoT protocol threat detection tool that scans devices for vulnerabilities, searches CVEs/PoCs, analyzes firmware, and monitors MQTT/UPnP traffic to…
 yozarseef95/cve-2023-31595
IC Realtime ICIP-P2012T is vulnerable to Incorrect Access Control via an open port
 robertguetzkow/cve-2021-37740
PoC for DoS vulnerability CVE-2021-37740 in firmware v3.0.3 of SCN-IP100.03 and SCN-IP000.03 by MDT. The bug has been fixed in firmware v3.0.4.
 pussycat0x/cve-2021-40859
Auerswald VoIP System Secret Backdoors -PoC