
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
32 results
CVE-2026-76070 preview

CVE-2026-76070

GitHubozcanpng/cve-2026-76070

Original research and PoC for a pre-auth Base64-decoded password stack buffer overflow in Netis NC63 login.cgi
binary-exploitationembedded-systems-securityexploitation+4
1
1 month ago
esp_wifi_repeater preview

esp_wifi_repeater

GitHubmartin-ger/esp_wifi_repeater

A full functional WiFi NAT Router (and now also a WiFi Repeater)
dns-analysisembedded-systems-securityhardware-iot-security+5
5.3k4 months ago
cve-2026-8697 preview

cve-2026-8697

GitHubitzmetanjim/cve-2026-8697

Detailed CVE-2026-8697 writeup with POC exploit for a login rate-limit bypass on TP-Link Archer C64 routers via a debug SSH service, enabling…
educationexploitationhardware-iot-security+7
15 months ago
cve-2026-34474-zte-h298a-h108n-sensitive-data-exposure preview

cve-2026-34474-zte-h298a-h108n-sensitive-data-exposure

GitHubminanagehsalalma/cve-2026-34474-zte-h298a-h108n-sensitive-data-exposure

CVE-2026-34474: unauthenticated ETHCheat=1 requests leak the admin password and Wi-Fi PSK from ZTE H298A/H108N routers.
exploitationinformation-gatheringiot-security+3
15 months ago
CVE-2026-36438 preview

CVE-2026-36438

GitHubkensh1k/cve-2026-36438

Documentation of CVE-2026-36438: a vulnerability in Intelbras VIP 1230 B/D G4 devices allowing remote attackers to obtain administrator account…
authenticationembedded-systems-securityinformation-gathering+3
5 months ago
CVE-2022-25012 preview

CVE-2022-25012

GitHubxk3nf4/cve-2022-25012

Argus Surveillance DVR v4.0 employs weak password encryption.
encryption-decryption-toolsexploitationiot-security+2
29 months ago
CVE-2025-63353 preview

CVE-2025-63353

GitHubhanianis/cve-2025-63353

A vulnerability in fiberhome GPON ONU HG6145F1 RP4423 allows the device's factory default Wi-Fi password (WPA/WPA2 pre-shared key) to be predicted…
exploitationhardware-securityiot-security+3
1111 months ago
CVE-2022-37932 preview

CVE-2022-37932

GitHubtim-hoekstra/cve-2022-37932

Proof-of-concept exploit for an authentication bypass in HP 1920 Series switches, allowing unauthenticated admin password change via crafted HTTP…
educationexploitationiot-security+3
21 year ago
Poc-CVE-2024-57040 preview

Poc-CVE-2024-57040

GitHubabsholi7ly/poc-cve-2024-57040

CVE-2024-57040 is a security vulnerability found in certain TP-Link TL-WR845N router models. Specifically, it involves a "hardcoded" password for the…
embedded-systems-securityexploitationhardware-iot-security+3
21 year ago
hichipreset preview
Archived

hichipreset

GitHubprisect/hichipreset

Hicip IP admin password reset script using CVE-2020-9529. This is made for educational purposes only of course.
educationexploitationiot-security+2
1 year ago
CVE-2024-48705 preview

CVE-2024-48705

GitHubl41kaa/cve-2024-48705

Wavlink AC1200 with firmware versions M32A3_V1410_230602 and M32A3_V1410_240222 are vulnerable to a post-authentication command injection while…
binary-analysiscommand-and-controlembedded-systems-security+7
21 year ago
CVE-2020-35575-TP-LINK-TL-WR841ND-password-disclosure preview

CVE-2020-35575-TP-LINK-TL-WR841ND-password-disclosure

GitHubdylvie/cve-2020-35575-tp-link-tl-wr841nd-password-disclosure

Weaponized exploit script for CVE-2020-35575, a password-disclosure vulnerability in TP-Link router web interfaces, granting remote administrative…
embedded-systems-securityexploitationiot-security+3
32 years ago
RomBuster preview

RomBuster

GitHubentysec/rombuster

RomBuster is a router exploitation tool that allows to disclosure network router admin password.
exploitationinformation-gatheringiot-security+1
5662 years ago
CamOver preview

CamOver

GitHubentysec/camover

CamOver is a camera exploitation tool that allows to disclosure network camera admin password.
exploitationinformation-gatheringiot-security+1
6052 years ago
nepstech-xpon-router-CVE-2024-40119 preview

nepstech-xpon-router-CVE-2024-40119

GitHubbaroi-ai/nepstech-xpon-router-cve-2024-40119

Cross-Site Request Forgery (CSRF) vulnerability in the password change function, which allows remote attackers to change the admin password without…
exploitationiot-securitypenetration-testing+3
12 years ago
Digisol-DG--GR1321-s-Password-Storage-in-Plaintext--CVE-2024-4232 preview

Digisol-DG--GR1321-s-Password-Storage-in-Plaintext--CVE-2024-4232

GitHubredfox-security/digisol-dg--gr1321-s-password-storage-in-plaintext--cve-2024-4232

Proof-of-concept exploit for CVE-2024-4232 targeting plaintext password storage in Digisol DG-GR1321 routers. Demonstrates extraction of credentials…
exploitationiot-securitymisconfiguration+3
2 years ago
CVE-2024-22853 preview

CVE-2024-22853

GitHubfallenskill1/cve-2024-22853

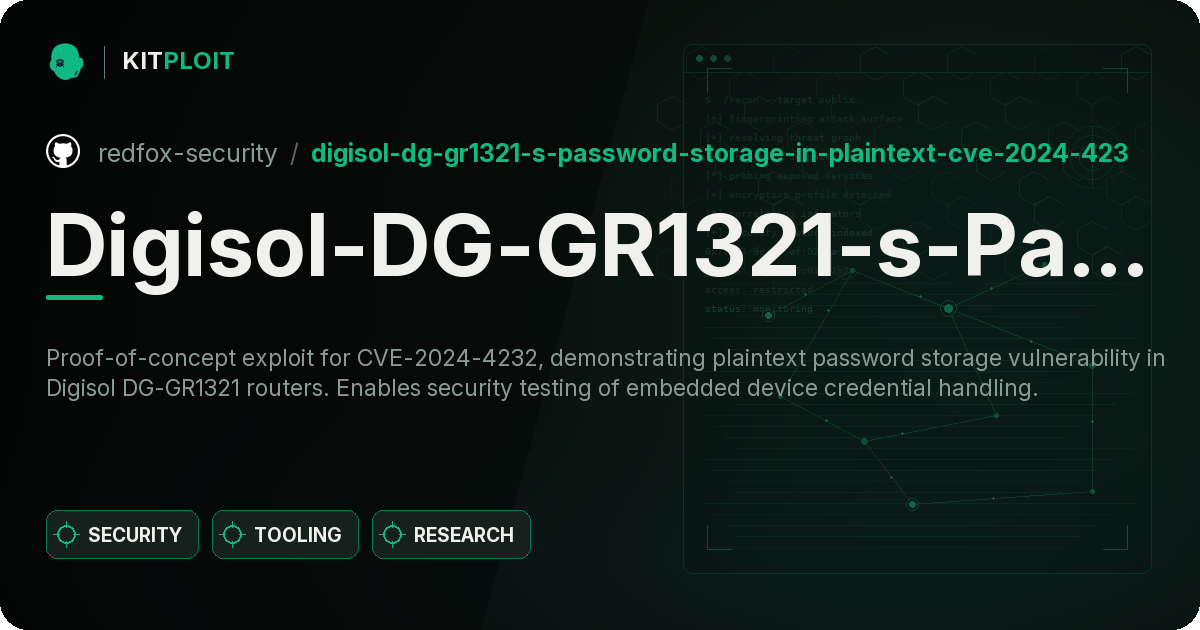
D-LINK Go-RT-AC750 GORTAC750_A1_FW_v101b03 has a hardcoded password for the Alphanetworks account, which allows remote attackers to obtain root…
embedded-systems-securityexploitationfirmware-analysis+5
2 years ago
Digisol-DG-GR1321-s-Password-Storage-in-Plaintext-CVE-2024-4232 preview

Digisol-DG-GR1321-s-Password-Storage-in-Plaintext-CVE-2024-4232

GitHubredfox-security/digisol-dg-gr1321-s-password-storage-in-plaintext-cve-2024-4232

Proof-of-concept demonstrating plaintext password storage vulnerability in Digisol DG-GR1321 routers, enabling credential exposure and unauthorized…

hardware-securityiot-securitymisconfiguration+3
2 years ago
Previous12Next