Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
32 results
metasploit-framework preview

metasploit-framework

GitHubrapid7/metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

command-and-controldatabase-securitydata-exfiltration+20
39.1k
7h 55m ago
ziti preview

ziti

GitHubopenziti/ziti

Zero-trust networking platform that makes services invisible with cryptographic identity, policy-based access, and end-to-end encryption. Replaces…

api-securityauthentication-authorizationcloud-security+7
4.4k2 days ago
MeshCore preview

MeshCore

GitHubmeshcore-dev/meshcore

A new lightweight, hybrid routing mesh protocol for packet radios

command-and-controldata-exfiltrationeducation+8
3.7k7 days ago
bettercap preview

bettercap

GitHubbettercap/bettercap

The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.

bluetooth-securitydata-exfiltrationfingerprint-spoofing+16
20.0k1 month ago
go-without-bounds-cve-2026-67822-stack-overflow-in-tenda-w6-s-wifissidset preview

go-without-bounds-cve-2026-67822-stack-overflow-in-tenda-w6-s-wifissidset

GitHubhunt-benito/go-without-bounds-cve-2026-67822-stack-overflow-in-tenda-w6-s-wifissidset

PoC for CVE-2026-67822 stack overflow in Tenda W6-S /goform/wifiSSIDset: DoS reproducer, QEMU MIPS shim, and conceptual RCE payload skeleton.

binary-exploitationdynamic-analysis-sandboxingembedded-systems-security+6
1 month ago
CVE-2026-22017-Firmware-Update-via-BLE-Without-Authentication preview

CVE-2026-22017-Firmware-Update-via-BLE-Without-Authentication

GitHubgeorge0papasotiriou/cve-2026-22017-firmware-update-via-ble-without-authentication

Simulated BLE peripheral exposing an unauthenticated GATT firmware-update characteristic; demonstrates critical CVE-2026-22017 device-takeover…

bluetooth-securityembedded-systems-securityexploitation+4
1 month ago
CVE-2026-8888-Printer-Firmware-Unsigned-Update-via-HTTP preview

CVE-2026-8888-Printer-Firmware-Unsigned-Update-via-HTTP

GitHubgeorge0papasotiriou/cve-2026-8888-printer-firmware-unsigned-update-via-http

Demonstrates CVE-2026-8888, an unsigned printer firmware update over HTTP, including a malicious update server and vulnerable printer emulator for…

embedded-systems-securityexploitationfirmware-analysis+4
1 month ago
DahuaLoginBypass preview

DahuaLoginBypass

GitHubbp2008/dahualoginbypass

Chrome extension that uses vulnerabilities CVE-2021-33044 and CVE-2021-33045 to log in to Dahua cameras without authentication.

authentication-authorizationexploitationiot-security+3
1982 months ago
NanoMQ-Memory-Leak-Research preview

NanoMQ-Memory-Leak-Research

GitHubmoxie25/nanomq-memory-leak-research

Public advisory and technical analysis for CVE-2026-36590, a NanoMQ v0.24.9 denial-of-service vulnerability.

dynamic-analysis-sandboxingexploitationiot-security+4
2 months ago
CVE-2026-32646 preview

CVE-2026-32646

GitHubmichaeladamgroberman/cve-2026-32646

CVE-2026-32646: Missing Authentication on Admin Device Endpoint — Gardyn Home Kit (ICSA-26-055-03)

api-securityauthenticationcloud-security+6
3 months ago
CVE-2025-10681 preview

CVE-2025-10681

GitHubmichaeladamgroberman/cve-2025-10681

CVE-2025-10681: Hardcoded Azure Blob Storage Account Key — Gardyn Home Kit (ICSA-26-055-03)

cloud-securitydata-exfiltrationembedded-systems-security+8
3 months ago
BlueSpy preview

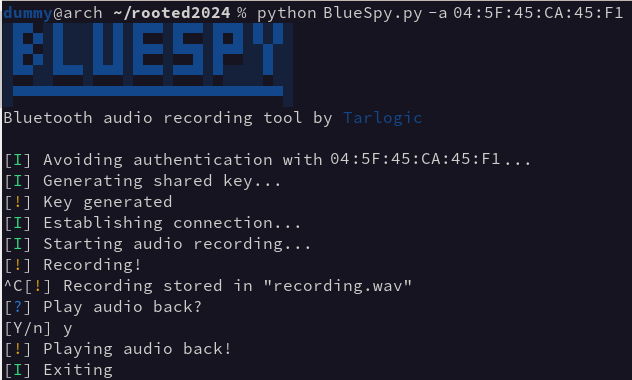
BlueSpy

GitHubtarlogicsecurity/bluespy

PoC to record audio from a Bluetooth device

bluetooth-securityexploitationhardware-iot-security+3
1.6k5 months ago
duckLogger preview

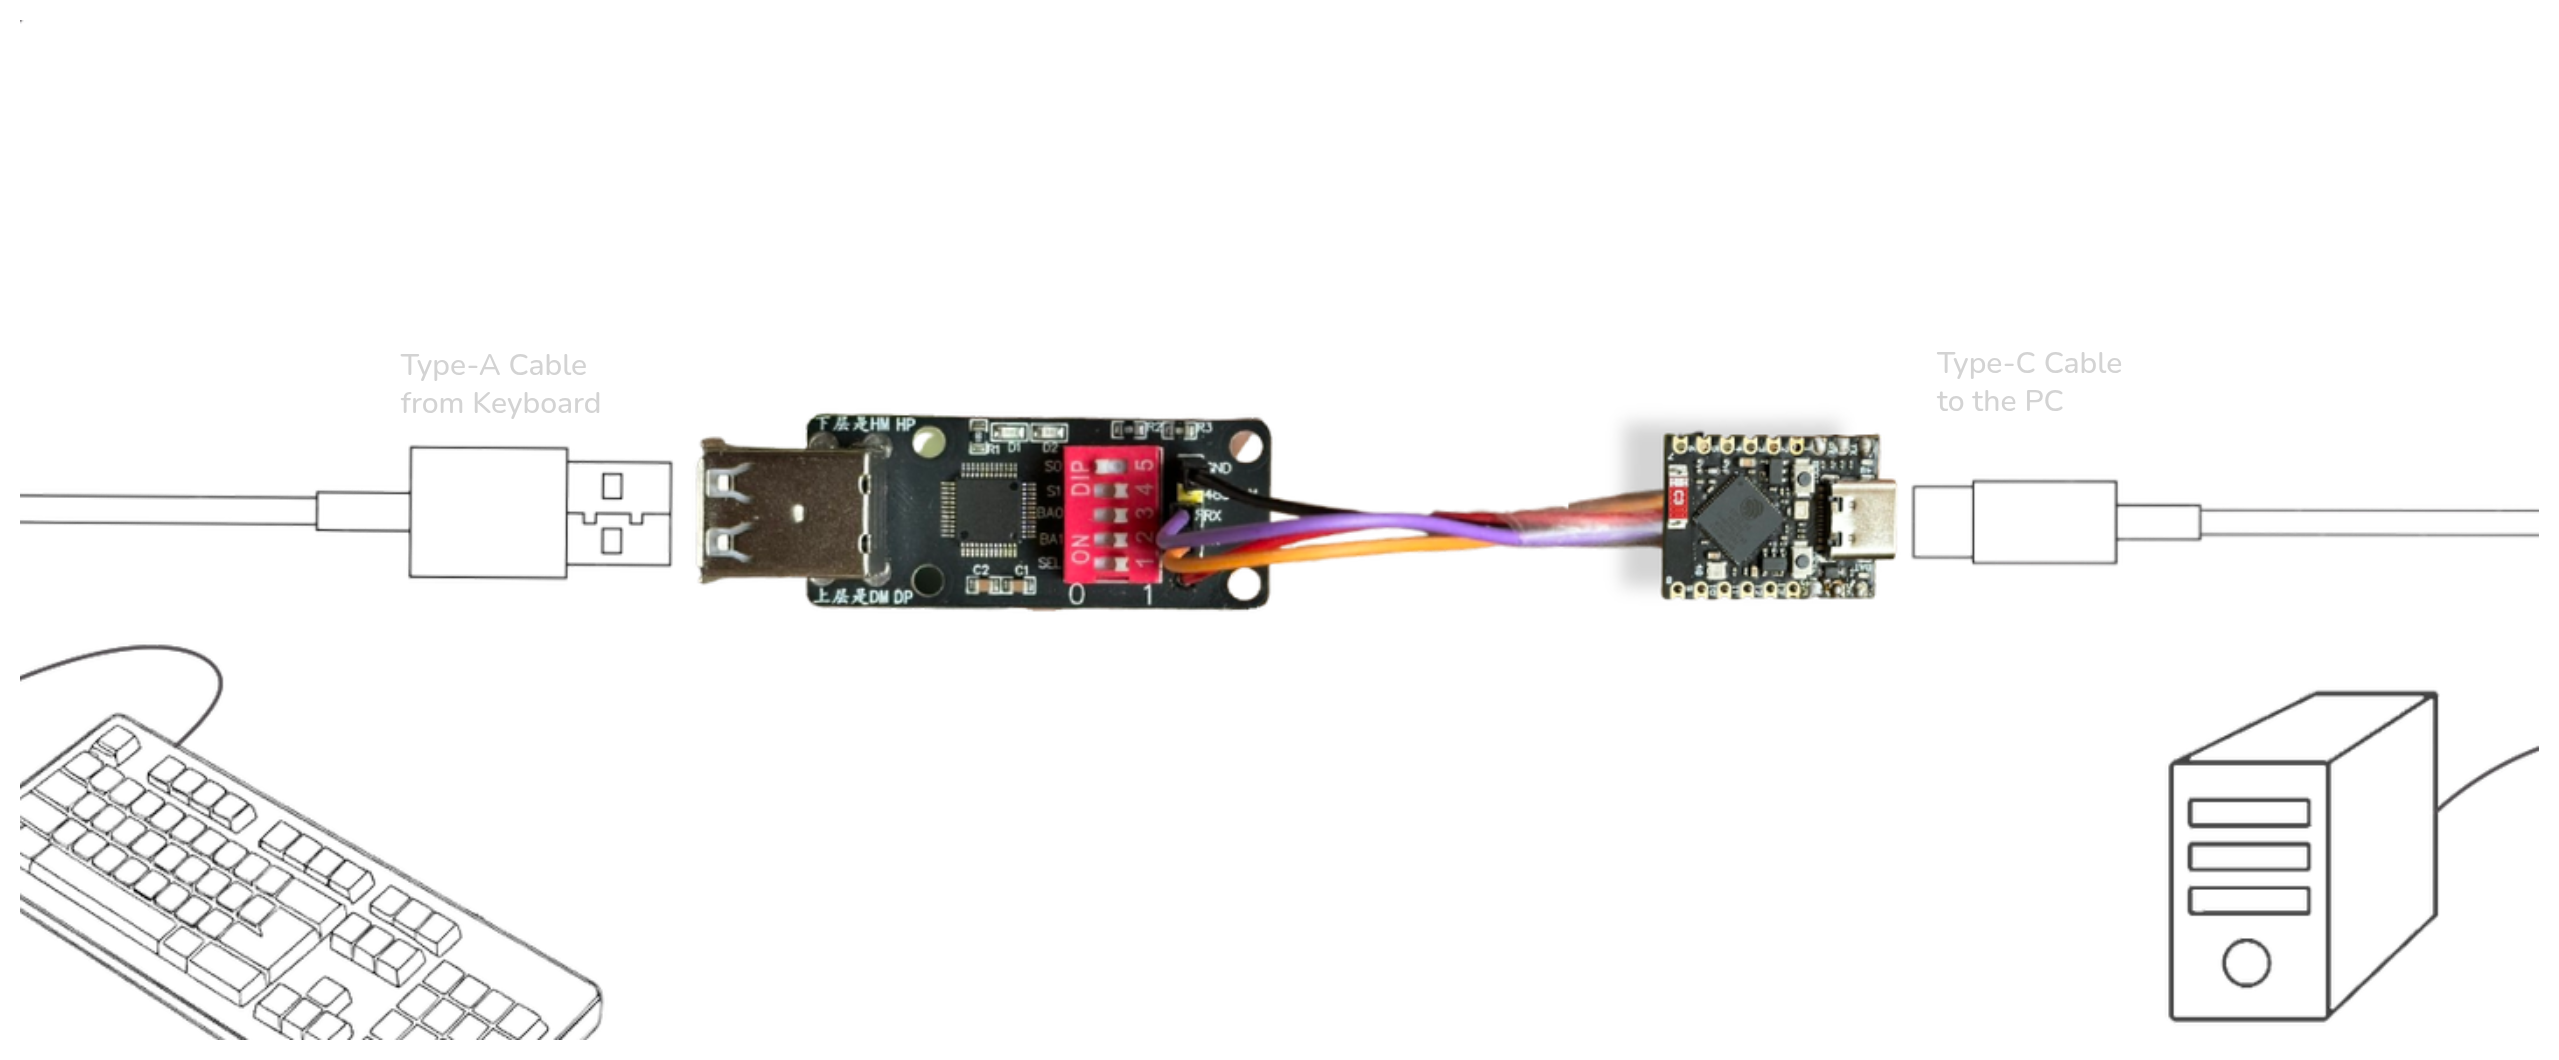
duckLogger

GitHubitsmmdoha/ducklogger

A ESP32-S3–based usb keylogger with wifi, easy DIY-able with widely available hardware.

command-and-controldata-exfiltrationembedded-systems-security+8
915 months ago
DAHUA_AUTH-BYPASS-CVE-2021-33044 preview

DAHUA_AUTH-BYPASS-CVE-2021-33044

GitHubeagle-nett/dahua_auth-bypass-cve-2021-33044

PoC exploit for Dahua authentication bypass (CVE-2021-33044). Scans subnets, tests multiple CVEs, and dumps device configs via crafted cookies…

authentication-authorizationeducationexploitation+4
15 months ago
CVE-2025-69821-Beat-XP-Vega-Smartwatch-Security-Assessment preview

CVE-2025-69821-Beat-XP-Vega-Smartwatch-Security-Assessment

GitHubcipherx1802/cve-2025-69821-beat-xp-vega-smartwatch-security-assessment

A security assessment of the Beat XP VEGA Smartwatch (Firmware RB303ATV006229) focused on Bluetooth Low Energy (BLE) connectivity revealed a design…

bluetooth-securityembedded-systems-securityexploitation+6
5 months ago
CVE-2025-13834-A-Bluetooth-RFCOMM-Out-of-Bounds-Read-Vulnerability-in-Modern-Wireless-Devices preview

CVE-2025-13834-A-Bluetooth-RFCOMM-Out-of-Bounds-Read-Vulnerability-in-Modern-Wireless-Devices

GitHubsastraadiwiguna-purpleeliteteaming/cve-2025-13834-a-bluetooth-rfcomm-out-of-bounds-read-vulnerability-in-modern-wireless-devices

CVE-2025-13834 Technical Summary Vulnerability Type: Memory Disclosure / Out-of-Bounds (OOB) Read (CWE-125). CVSS Score: 7.5–8.1 (High/Critical). …

binary-exploitationbluetooth-securityexploitation+8
18 months ago
CVE-2025-67160 preview

CVE-2025-67160

GitHubremenis/cve-2025-67160

Vatilon-based IP cameras expose internal web directories without authentication, leading to information disclosure.

exploitationinformation-gatheringiot-security+3
8 months ago
CVE-2018-12633-TPLink-Auth-Bypass preview

CVE-2018-12633-TPLink-Auth-Bypass

GitHubwiliam227user/cve-2018-12633-tplink-auth-bypass

A technical case study and exploitation analysis of the Authentication Bypass vulnerability in TP-Link TL-WR840N firmware (CVE-2018-12633).

data-exfiltrationeducationembedded-systems-security+8
8 months ago
Previous12Next