
CVE-2024-54887-PoC
 gumbraise/cve-2024-54887-poc
TypeScript PoC for CVE-2024-54887 (TP-Link TL-WR940N authenticated RCE)
exploitationhardware-iot-securityiot-security+4
gumbraise/cve-2024-54887-pocTypeScript PoC for CVE-2024-54887 (TP-Link TL-WR940N authenticated RCE)
 istaarkk/cve-2025-65817
Here is the CVE-2025-65817
 h4ckusaur/cve-2024-57366
Remote code execution exploit for CVE-2024-57366 targeting WAVLINK routers via MAC address validation bypass and command injection, with automatic…
 edwins907/-cve-2024-45352
Technical report about a critical vulnerability in Xiaomi (CVE-2024-45352)
 d-raco/cve-2024-31964
Proof-of-concept exploit for CVE-2024-31964, a temporary authentication bypass in Mitel 6900w Series SIP phones allowing unauthenticated POST…
 c0nyy/iot_vuln
Proof-of-concept exploits for IoT device vulnerabilities, including TOTOLINK login bypass CVEs, with detailed technical analysis and reproduction…
 aliask/dinkleberry
Patch your D-Link device affected by CVE-2024-3272
 absholi7ly/poc-cve-2024-57040
CVE-2024-57040 is a security vulnerability found in certain TP-Link TL-WR845N router models. Specifically, it involves a "hardcoded" password for the…
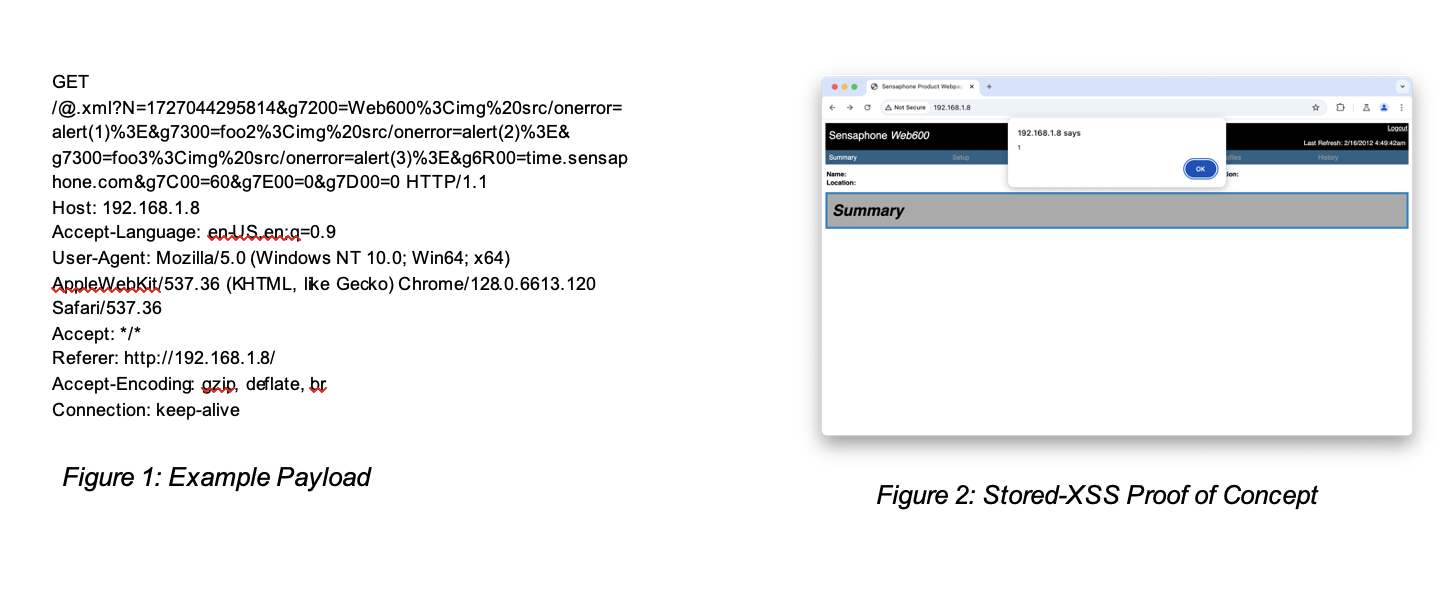 tcbutler320/cve-2024-55040-sensaphone-xss
Public disclose of several stored XSS vulnerabilities in the Sensaphone WEB600 (CVE-2024-55040)
 dylvie/cve-2024-9570_d-link-dir-619l-bof
Remote buffer overflow exploit for D-Link DIR-619L router (CVE-2024-9570) targeting the formEasySetTimezone function for penetration testing and…
 fj016/cve-2024-41992-poc
PoC for the CVE-2024-41992 (RCE on devices running WiFi-TestSuite-DUT)
 xen0bit/fwbt
Proof of Concept code for interaction with Firewalla via Bluetooth Low-Energy and exploitation of CVE-2024-40892 / CVE-2024-40893
 baroi-ai/cve-2024-42658
CVE-2024-42658 An issue in wishnet Nepstech Wifi Router NTPL-XPON1GFEVN v1.0 allows a remote attacker to obtain sensitive information via the cookies…
 revoltsecurities/cve-2024-7339
An Vulnerability detection and Exploitation tool for CVE-2024-7339
 baroi-ai/nepstech-xpon-router-cve-2024-40119
Cross-Site Request Forgery (CSRF) vulnerability in the password change function, which allows remote attackers to change the admin password without…
 wanlichangchengwanlichang/cve-2024-29972
Exploit script for CVE-2024-29972 Zyxel NAS backdoor account, combining with CVE-2024-29973 for unauthorized root access via NsaRescueAngel.
 oiivr/turvan6rkus-cve-2024-3273
Turvanõrkuse CVE 2024 3273 analüüs: D-Link seadmete käsusüst