
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
86 results
CVE-2026-90847 preview

CVE-2026-90847

GitHubshlln/cve-2026-90847

Proof-of-concept for CVE-2026-90847, an authenticated RCE in iux_set.cgi via malicious .cfg tar upload that writes commands into crontab for…
embedded-systems-securityexploitationiot-security+5
2 days ago
cve-2026-19900-PoC preview

cve-2026-19900-PoC

GitHubon3sk-0x1/cve-2026-19900-poc

Proof-of-concept exploit for CVE-2026-19900, an authentication bypass and remote code execution vulnerability in LB-LINK X-PRO routers, allowing…
authenticationexploitationiot-security+3
21 days ago
CVE-2026-82592 preview

CVE-2026-82592

GitHubhackspeak/cve-2026-82592

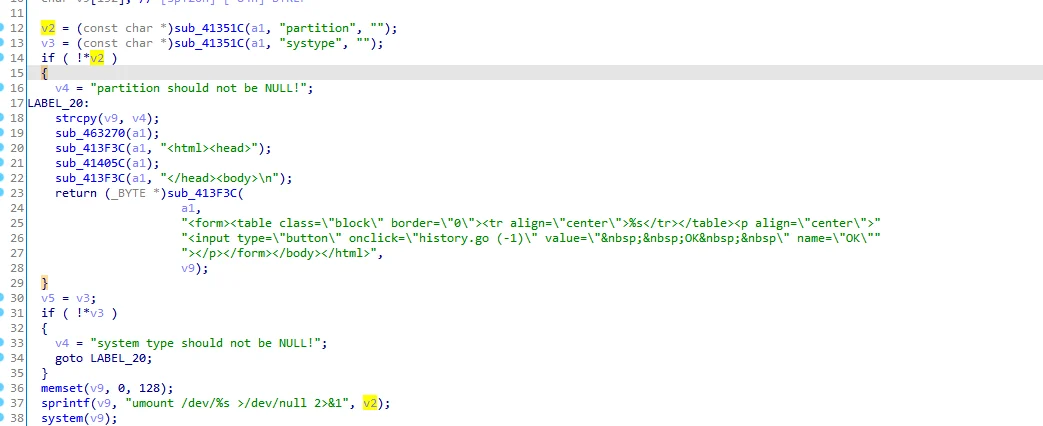
Proof-of-concept exploit for D-Link DIR-825M stack buffer overflow and command injection in /boafrm/formDiskFormat, enabling remote code execution as…
binary-exploitationexploitationhardware-iot-security+4
224 days ago
CVE-2026-2035703-x300 preview

CVE-2026-2035703-x300

GitHubdanish1162/cve-2026-2035703-x300

Tozed ZLT X300 5G CPE — Remote Root Code Execution via SDR Rogue Base Station (CVE-2026-2035703, CWE-78, CVSS 9.8) — Coordinated Disclosure
binary-analysiseducationexploitation+4
27 days ago
CVE-2026-32662 preview

CVE-2026-32662

GitHubxf-secops/cve-2026-32662

Advisory detailing active debug code in production Gardyn Home Kit cloud API, exposing development endpoints and embedded credentials, with…
cloud-securityconfiguration-auditingiot-security+3
5 months ago
RFIDIOt preview

RFIDIOt

GitHubadamlaurie/rfidiot

Python library and tools for exploring RFID/NFC tags and readers: read, write, clone, and analyze supported ACG serial hardware for research and…
embedded-systems-securityhardware-hackinghardware-iot-security+4
1.1k11 days ago
flipperzero-firmware preview

flipperzero-firmware

GitHubflipperdevices/flipperzero-firmware

Flipper Zero firmware source code
bluetooth-securityembedded-systems-securityhardware-hacking+6
16.6k21 days ago
sonos preview

sonos

GitHubblasty/sonos

Exploit and tooling for Amlogic-based Sonos devices: dumps OTP/eFUSE via an EL3 exploit, extracts LUKS decryption keys, and fetches/decrypts OTA…
embedded-systems-securityencryption-decryption-toolsexploitation+5
643 years ago
dlink preview

dlink

GitHubnetsecfish/dlink

Proof-of-concept exploit and analysis for command injection and hardcoded backdoor credentials in D-Link NAS devices, enabling unauthenticated remote…
authenticationexploitationiot-security+3
992 years ago
CVE-2026-23005-Matter-Commissioning-Code-Brute-Force-Without-Rate-Limit preview

CVE-2026-23005-Matter-Commissioning-Code-Brute-Force-Without-Rate-Limit

GitHubgeorge0papasotiriou/cve-2026-23005-matter-commissioning-code-brute-force-without-rate-limit

Simulates a Matter commissioning code brute-force attack (CVE-2026-23005) using Python to demonstrate missing rate limiting and lockout on 8-digit…
embedded-systems-securityexploitationiot-security+2
1 month ago
CVE-2026-2222-MQTT-Broker-CONNECT-Packet-Heap-Overflow preview

CVE-2026-2222-MQTT-Broker-CONNECT-Packet-Heap-Overflow

GitHubgeorge0papasotiriou/cve-2026-2222-mqtt-broker-connect-packet-heap-overflow

Demonstrates CVE-2026-2222 heap overflow in MQTT CONNECT packet handling with a simulated vulnerable broker and proof-of-concept exploit code for…
binary-exploitationeducationexploitation+2
1 month ago
CVE-2026-6789-Stack-Buffer-Overflow-in-Embedded-TLS-Certificate-Parser preview

CVE-2026-6789-Stack-Buffer-Overflow-in-Embedded-TLS-Certificate-Parser

GitHubgeorge0papasotiriou/cve-2026-6789-stack-buffer-overflow-in-embedded-tls-certificate-parser

Stack buffer overflow PoC in an embedded TLS certificate parser using a crafted X.509 SAN extension for remote code execution on IoT and industrial…
binary-exploitationeducationembedded-systems-security+3
1 month ago
CVE-2026-1122-IoT-Firmware-Update-Signature-Bypass-via-Low-Order-Point-Injection preview

CVE-2026-1122-IoT-Firmware-Update-Signature-Bypass-via-Low-Order-Point-Injection

GitHubgeorge0papasotiriou/cve-2026-1122-iot-firmware-update-signature-bypass-via-low-order-point-injection

Demonstrates CVE-2026-1122 Ed25519 signature bypass via low-order point injection, forging malicious IoT firmware updates with Python and C verifier…
cryptographyembedded-systems-securityexploitation+4
1 month ago
shining-mask preview

shining-mask

GitHubbishopfox/shining-mask

BLE-based tool that automatically discovers and exploits Shining LED Masks by uploading a custom image without user interaction, proving security…
bluetooth-securityeducationembedded-systems-security+5
1211 months ago
system_bt_AOSP10_r33_CVE-2021-0431 preview

system_bt_AOSP10_r33_CVE-2021-0431

GitHubnanopathi/system_bt_aosp10_r33_cve-2021-0431

Android Bluetooth stack (Fluoride) source code for AOSP 10 r33, specifically related to CVE-2021-0431 Bluetooth vulnerability research and…
bluetooth-securityembedded-systems-securityexploitation+4
4 years ago
sricam-gsoap2.8-dos-exploit preview

sricam-gsoap2.8-dos-exploit

GitHubbitfu/sricam-gsoap2.8-dos-exploit

Sricam gSOAP2.8 DoS exploit PoC
embedded-systems-securityexploitationiot-security+3
37 years ago
CVE-2026-53921 preview

CVE-2026-53921

GitHub0xblackash/cve-2026-53921

CVE-2026-53921

educationiot-securitypapers-research+1
21 month ago
CP-PLUS-EZ-P21-CVE-2026-65893-65894 preview

CP-PLUS-EZ-P21-CVE-2026-65893-65894

GitHubcybervinner/cp-plus-ez-p21-cve-2026-65893-65894

Documents CP PLUS EZ-P21 IP camera CVEs: arbitrary code execution via debug feature and improper authentication of HTTP endpoints, with responsible…

authenticationeducationembedded-systems-security+5
1 month ago
Previous12345Next