
Terrminus-CVE-2026-2406
 ridpath/terrminus-cve-2026-2406
AsyncIO Scanner & Exploitation Framework for CVE-2026-24061 (Telnet NEW_ENVIRON Auth Bypass). Features high-concurrency discovery, passive…
exploitationinformation-gatheringiot-security+8
2
ridpath/terrminus-cve-2026-2406AsyncIO Scanner & Exploitation Framework for CVE-2026-24061 (Telnet NEW_ENVIRON Auth Bypass). Features high-concurrency discovery, passive…
 whad-team/whad-client
Protocol client and CLI framework for interacting with wireless hacking devices, enabling security researchers to explore, test, and automate…
 pr0v3rbs/firmae
Towards Large-Scale Emulation of IoT Firmware for Dynamic Analysis
 jarrettgohxz/cve-research
A repository that contains all the working PoC I have crafted for known CVEs, and details on any ongoing research I am currently doing (mostly Iot…
 wilfred-wulbou/hg532d-rce-exploit
A Remote Code Execution (RCE) exploit for Huawei HG532d based on CVE-2017-17215 vulnerability. Modded from original PoC code from exploit-db.com
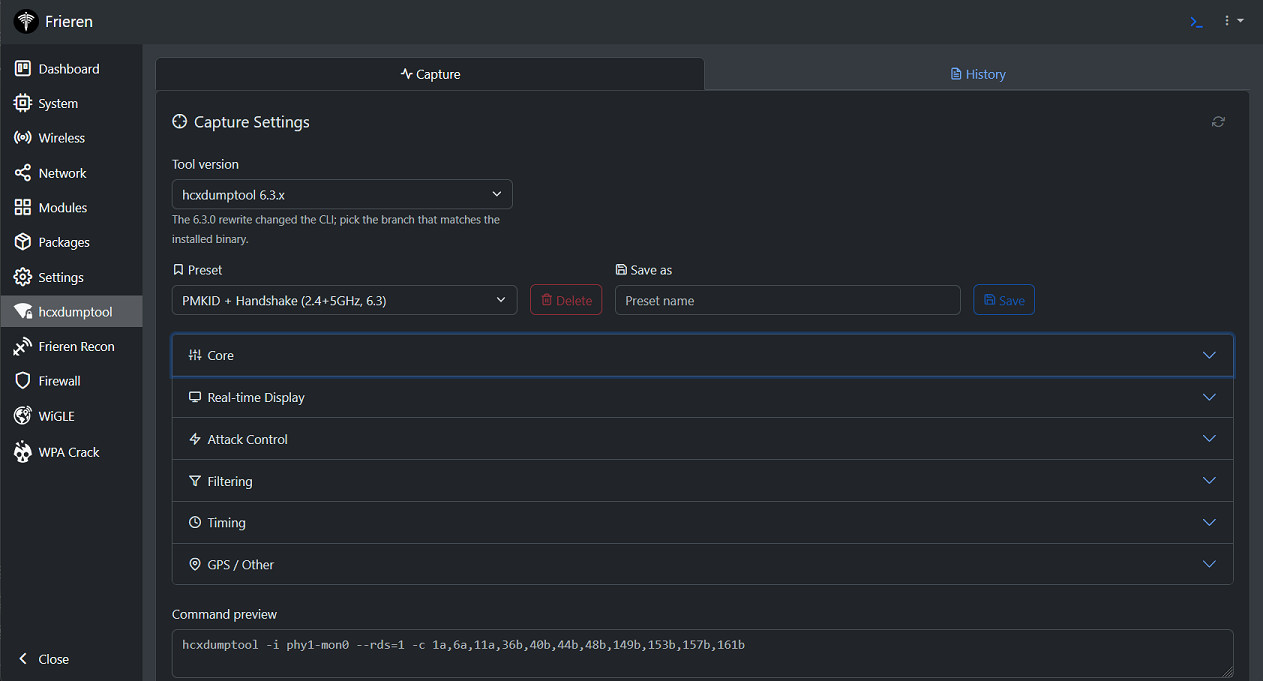 xchwarze/frieren
Frieren is a micro-framework designed for use in routers and Single Board Computers (SBCs). This framework is built to be lightweight, efficient, and…
 orange-cyberdefense/bof
BOF (Boiboite Opener Framework) is a testing framework for industrial protocols implementations and devices.
 threat9/routersploit
Exploitation Framework for Embedded Devices
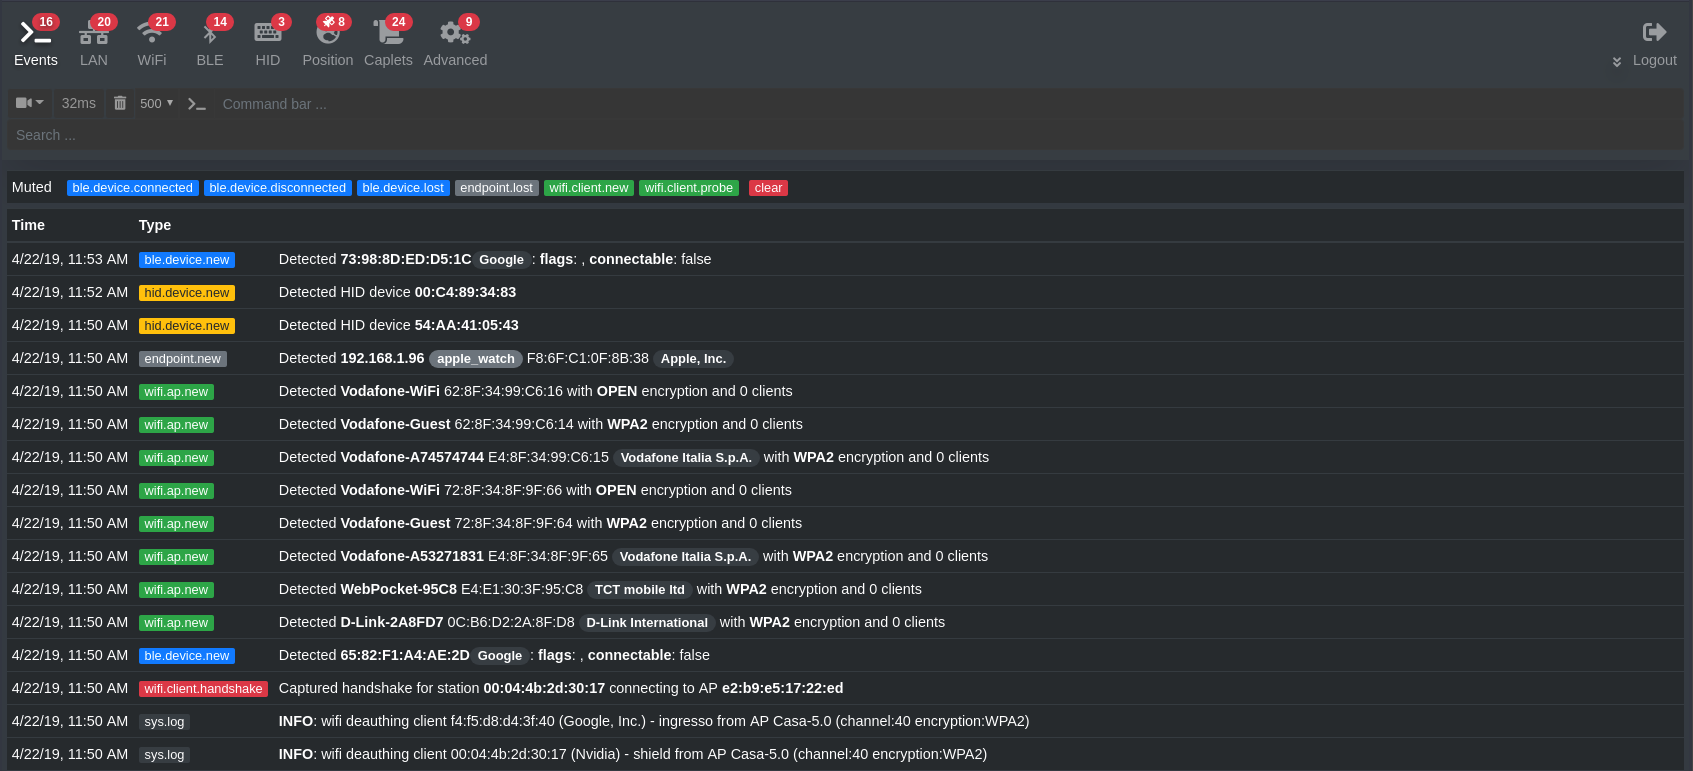 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
 renode/renode
Open-source simulation framework for developing, testing, and debugging unmodified software for multi-node embedded and IoT systems, supporting ARM,…

 expliot_framework/expliot
EXPLIoT - Internet of Things Security Testing and Exploitation framework
 riverloopsec/killerbee
IEEE 802.15.4/ZigBee Security Research Toolkit
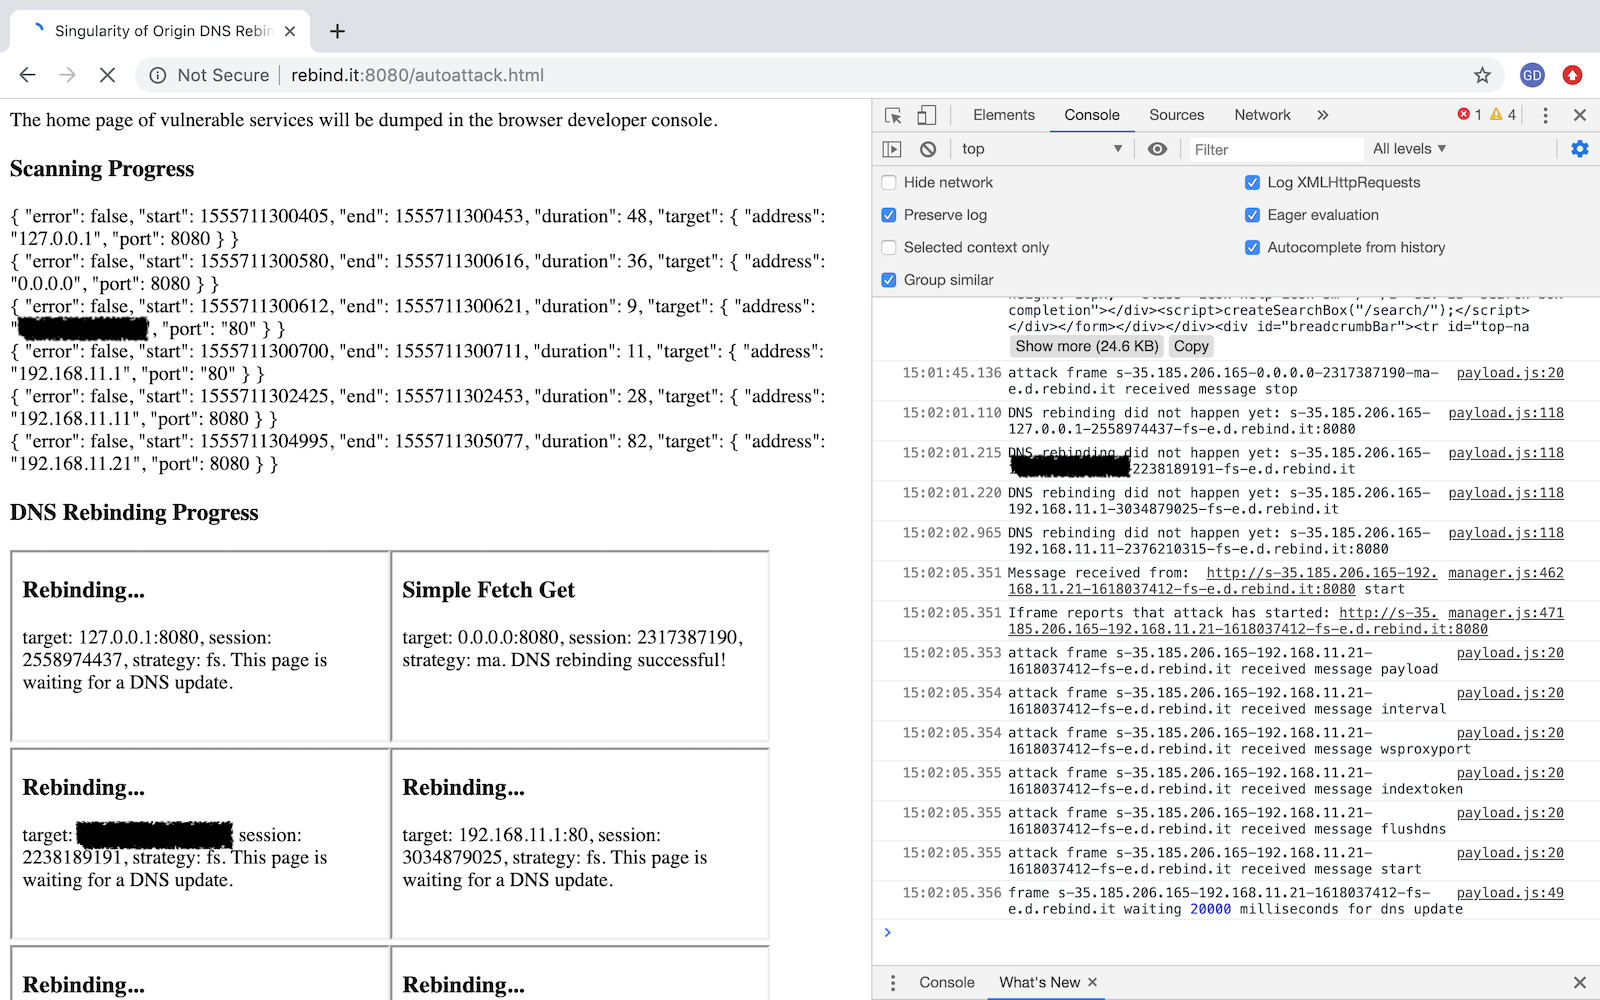 nccgroup/singularity
A DNS rebinding attack framework.
 ioactive/laf
This project intends to provide a series of tools to craft, parse, send, analyze and crack a set of LoRaWAN packets in order to audit or pentest the…
 cisc0-gif/kitt-lite
Python-Based Pentesting CLI Tool
 cisc0-gif/kitt
Python-Based Pentesting Framework
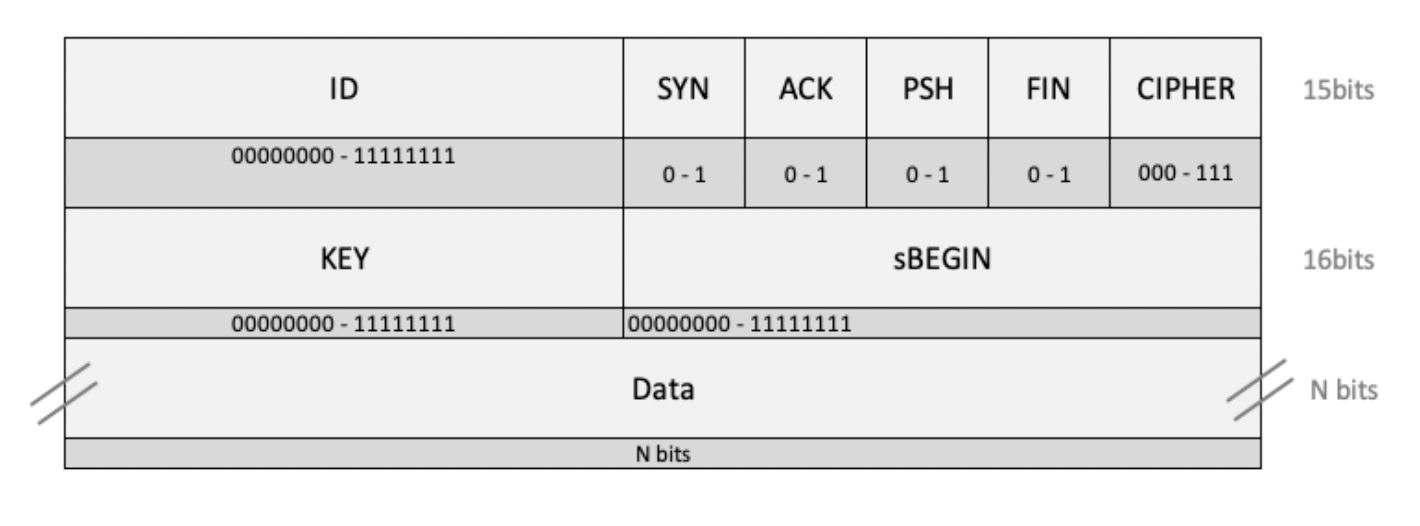 telefonica/sdk-sms-stack
Framework providing TCP/IP-like characteristics over GSM SMS with AES+CTR encryption, enabling secure, ordered message streams for device-to-device…