usb-ninja-detection-poc

Detects USB Ninja keystroke injection attacks by logging keystrokes and application events, providing a proof-of-concept for defensive monitoring.

Detects USB Ninja keystroke injection attacks by logging keystrokes and application events, providing a proof-of-concept for defensive monitoring.

A collection of exploits for various vulnerabilities targeting Inteno IOPSYS devices

ZoneMinder is a free, open source Closed-circuit television software application developed for Linux which supports IP, USB and Analog cameras.

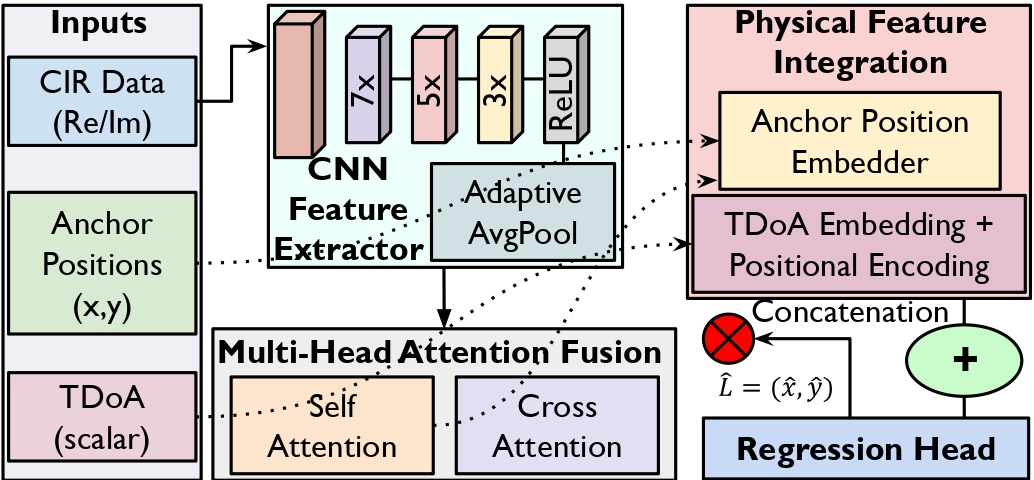
Adversary-resilient deep learning architecture for secure 5G indoor localization, combining CNN and multi-head attention to defend against signal…

CVE-2025-63587

Disclosure of client-side authentication bypass in AVer camera web interface exposing unencrypted credentials via network traffic monitoring.

Auerswald VoIP System Secret Backdoors -PoC

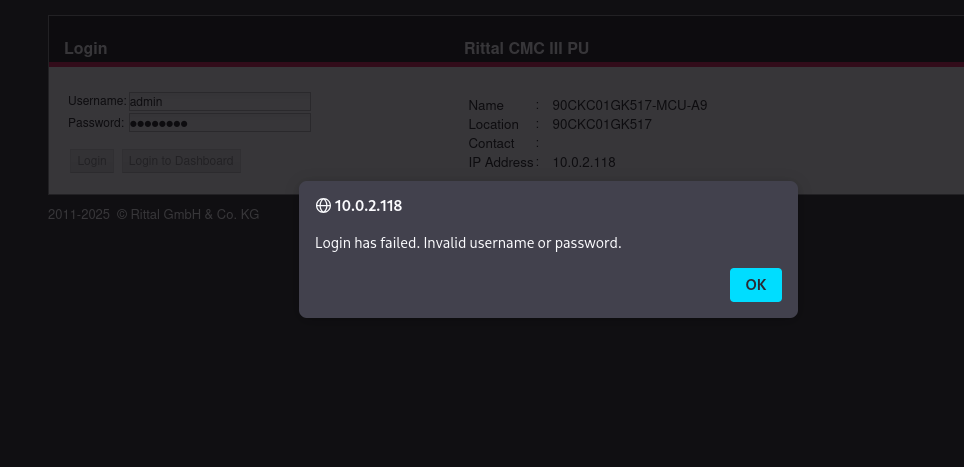
Proof-of-concept for stored XSS vulnerability in Rittal CMC PU III web management interface, enabling persistent client-side script injection before…

exploit camera with vuln cve-2018-9995 ( Novo, CeNova, QSee, Pulnix, XVR 5 in 1 (title: "XVR Login"), Securus, - Security. Never Compromise !! - …

Primary Git Repository for the Zephyr Project. Zephyr is a new generation, scalable, optimized, secure RTOS for multiple hardware architectures.

Anviz M3 RFID CVE-2019-11523 PoC

Norton Core Secure WiFi PoC (CVE-2018-5234) on Rust.

A vulnerability in fiberhome GPON ONU HG6145F1 RP4423 allows the device's factory default Wi-Fi password (WPA/WPA2 pre-shared key) to be predicted…

Proof-of-concept exploit demonstrating command injection via BLE service in Norton Core Secure WiFi Router (CVE-2018-5234). Includes SSH access setup…

Go-based PoC exploit for unauthenticated remote code execution on Shenzhen Aitemi M300 Wi-Fi repeaters. Includes a scanner and does not reboot the…

Proof-of-concept exploit for CVE-2024-31964, a temporary authentication bypass in Mitel 6900w Series SIP phones allowing unauthenticated POST…

IC Realtime ICIP-P2012T is vulnerable to Incorrect Access Control via an open port

IC Realtime ICIP-P2012T 2.420 is vulnerable to Incorrect Access Control