

FirmAE
 pr0v3rbs/firmae
Towards Large-Scale Emulation of IoT Firmware for Dynamic Analysis
dynamic-analysis-sandboxingembedded-systems-securityfirmware-analysis+3
9584 months ago
pr0v3rbs/firmaeTowards Large-Scale Emulation of IoT Firmware for Dynamic Analysis
 hunt-benito/go-without-bounds-cve-2026-67822-stack-overflow-in-tenda-w6-s-wifissidset
PoC for CVE-2026-67822 stack overflow in Tenda W6-S /goform/wifiSSIDset: DoS reproducer, QEMU MIPS shim, and conceptual RCE payload skeleton.
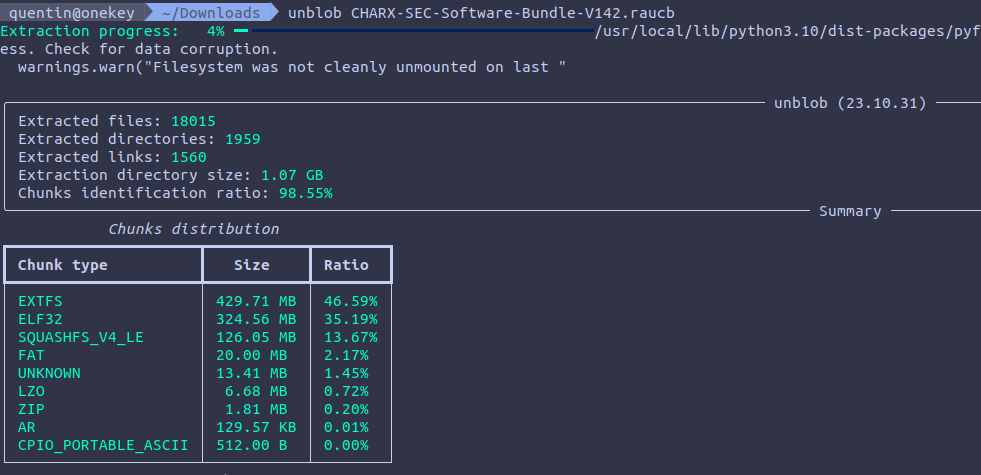 onekey-sec/firmware-workshop
In this workshop session, we will extract firmware from an EV charger, dig into the firmware, and eventually emulate it so we can interact with the…
 bishopfox/sparkplugfuzzer
Fuzzer for the Sparkplug B IIoT protocol
 moxie25/nanomq-memory-leak-research
Public advisory and technical analysis for CVE-2026-36590, a NanoMQ v0.24.9 denial-of-service vulnerability.
 firmadyne/firmadyne
Platform for emulation and dynamic analysis of Linux-based firmware
 fkie-cad/fact_core
Firmware Analysis and Comparison Tool
 e-m-b-a/emba
EMBA - The firmware security analyzer