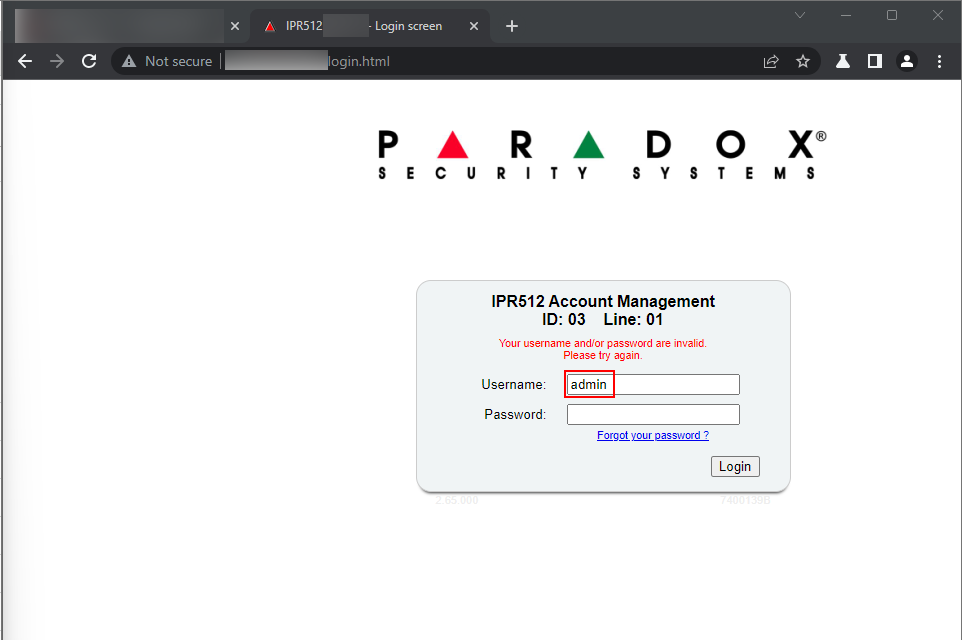
Injection-vulnerability-in-Paradox-Security-Systems-IPR512-CVE-2023-24709-PoC

In Paradox Security System IPR512 Web console login form page, attacker can input JavaScript string, such as "</script>" that will overwrite…

In Paradox Security System IPR512 Web console login form page, attacker can input JavaScript string, such as "</script>" that will overwrite…

Python script to generate neo4j Cypher representation of a collection of IoT devices for visualisation and query.

CVE-2025-9983 POC Exploit

CVE-2023-43261 - Credential Leakage Through Unprotected System Logs and Weak Password Encryption

Proof-of-concept exploit for CVE-2024-10914, a command injection vulnerability in D-Link NAS devices via the account_mgr.cgi script. Includes…

Python3 script to scan for Linksys smart wifi devices that are vulnerable to CVE-2014-8244

Proof-of-concept exploit for CVE-2024-34463 targeting insufficient Bluetooth security in BPL Smart Weighing Scale PWS-01-BT. Includes BLE scanner and…

Proof-of-concept exploit for CVE-2022-30114, a heap-based buffer overflow in Fastweb FastGate routers. Sends a crafted HTTP Authorization header to…

Authenticated command injection exploit for Tenda HG9 routers. Provides interactive remote shell access via Python script for penetration testing and…

Cross Site Scripting (XSS) in Digisol DG-HR3400 Router

Proof-of-concept for stored XSS vulnerability in Rittal CMC PU III web management interface, enabling persistent client-side script injection before…

CVE-2018-14714 PoC RCE

CVE-2017-7921 exploit. Allows admin password retrieval and automatic snapshot download.

Vulnerability checker for Callstranger (CVE-2020-12695)

M1 Band Smart Watch Bluetooth Low Energy Exploit python script (CVE-2018-11631)

it is script designed to exploit certain vulnerabilities in routers by sending payloads through SNMP (Simple Network Management Protocol). The script…

This script exploits a remote command execution vulnerability in the TPLink WR840N router, using the configure function IPv6 protocol.

This script exploits a vulnerability (IoF) in the TPLink WR840N router, using a field for injecting code in the module DNS.