metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…

HikPwn, a simple scanner for Hikvision devices with basic vulnerability scanning capabilities written in Python 3.8.

Chrome extension that uses vulnerabilities CVE-2021-33044 and CVE-2021-33045 to log in to Dahua cameras without authentication.

CVE-2026-43499 (GhostLock) — Linux kernel futex PI rt_mutex UAF ARM32 privilege escalation research targeting Huawei Watch 4 Pro (kernel 5.4.210)

PoC for DoS vulnerability CVE-2021-37740 in firmware v3.0.3 of SCN-IP100.03 and SCN-IP000.03 by MDT. The bug has been fixed in firmware v3.0.4.

Software-only proof of concept for CVE-2025-52464 in Meshtastic Direct Messages

Proof-of-concept exploit for CVE-2024-7120 command injection vulnerability in RAISECOM gateway devices. Provides exploitation details, affected…

网络摄像头漏洞扫描工具 | Webcam vulnerability scanning tool

Android NFC package patched for CVE-2020-0453, addressing a security vulnerability in the NFC component.

TOTOLINK-A702R-V1.0.0-B20161227.1023 Directory Indexing Vulnerability

A technical case study and exploitation analysis of the Authentication Bypass vulnerability in TP-Link TL-WR840N firmware (CVE-2018-12633).

Dahua IPC/VTH/VTO devices auth bypass exploit

Advisory and technical analysis of CVE-2026-15469, a hard-coded RSA-512 mesh group private key in TP-Link Deco routers, including root cause, impact,…

Towards Large-Scale Emulation of IoT Firmware for Dynamic Analysis

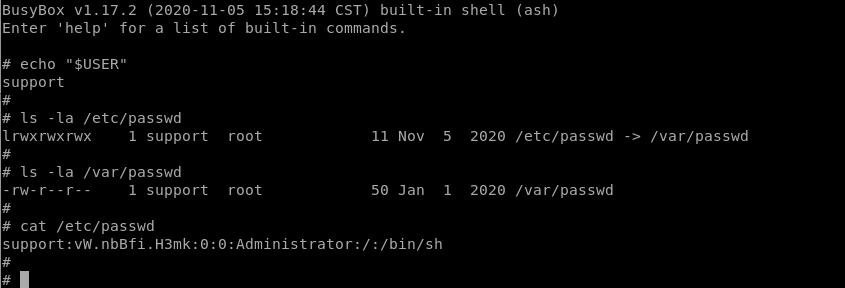
Privilege escalation vulnerability on MitraStar routers

PoC for CVE-2026-94095, a traceroute command injection in Netcore NBR200V2 firmware via ubus JSON-RPC, enabling root RCE for authorized testing.

Simulated BLE peripheral exposing an unauthenticated GATT firmware-update characteristic; demonstrates critical CVE-2026-22017 device-takeover…