JXL_Infotainment_CVE-2025-69515

Proof-of-concept exploit for CVE-2025-69515 demonstrating static GPS spoofing on JXL 9-inch Android infotainment units via SDR-based signal…

Proof-of-concept exploit for CVE-2025-69515 demonstrating static GPS spoofing on JXL 9-inch Android infotainment units via SDR-based signal…

Linux kernel module implementing a zero-configuration, OTP-based firewall for IoT devices. Transparently authenticates network traffic using a…

Practical labs, notes, and reports for CEH v13 modules — covering web hacking, network pentesting, malware analysis, social engineering, and security…

PoC tools for CVE-2026-58457: Unauthenticated OS Command Injection leading to remote root on Shenzhen Aitemi M300 Wi-Fi Repeater (MT02). Includes…

Firmware for getting a power trace of the behavior of the bluetooth module on the ESP32 when the ESP32 is sent the undocumented hci bluetooth…

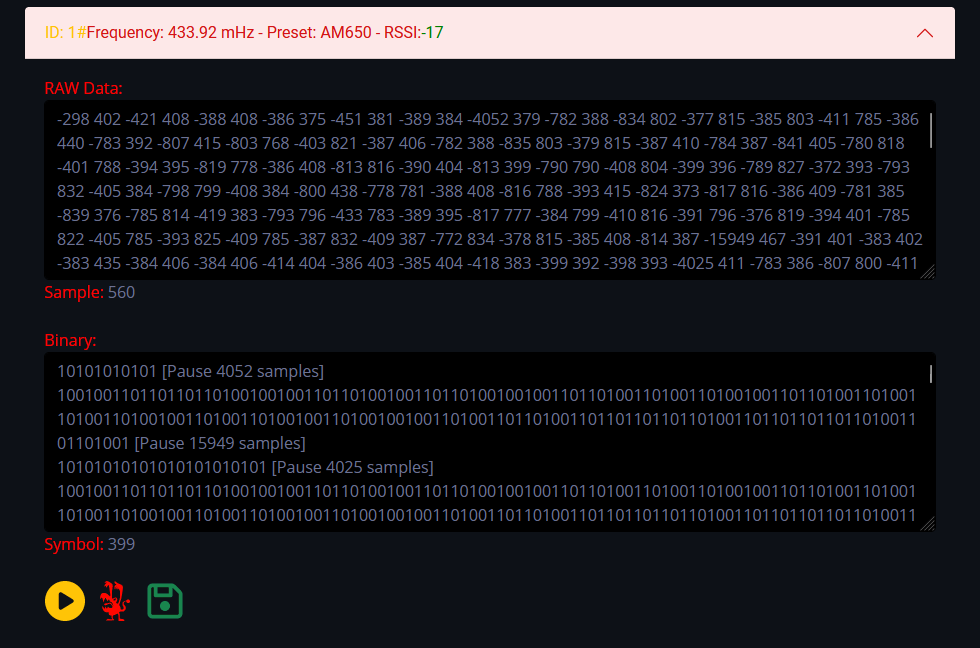
This firmware is an alternative to the EvilCrowRF default firmware. Module: CC1101 - Compatible Flipper Zero file.

Bitcoin Cryptanalysis: CVE-2025-27840 Vulnerability in ESP32 Microcontrollers Puts Billions of IoT Devices at Risk via Wi-Fi & Bluetooth

Sinilink XY-WFTX Wifi Remote Thermostat Module Temperature Controller

This script exploits a vulnerability (IoF) in the TPLink WR840N router, using a field for injecting code in the module DNS.

Metasploit module exploiting unauthenticated command injection in multiple Netgear router models to achieve remote code execution with root…